App · Tool:
OpenAllegroParserC2
OpenAllegroParser is a C++17 library and CLI for investigating Cadence Allegro binary design files.
- App
Reviewed Werni2A/OpenAllegroParser@d9d9d68
App · Tool:
OpenAllegroParser is a C++17 library and CLI for investigating Cadence Allegro binary design files.
Reviewed Werni2A/OpenAllegroParser@d9d9d68
App · Tool:
LogicX Analyzer inspects Logic Pro .logicx project bundles and studies their undocumented ProjectData binary format.
Reviewed geoffmyers/logicx-analyzer@a1c4078
Binary · Tool:
FunctionParser identifies function ranges in IDA Pro HTML, reads switch-case error addresses from a XenonRecomp log and writes function entries for a XenonRecomp TOML configuration.
Firmware · Tool:
hyperscan-emulator loads a HyperScan firmware image into emulated memory and exposes CPU execution through an interactive debugger.
Reviewed LiraNuna/hyperscan-emulator@be1bfdd
Binary · Tool:
AppleWin emulates Apple II computers on Windows and includes a symbolic debugger for inspecting running software.
Reviewed AppleWin/AppleWin@4a43bcd
App · Tool:
PyFLP parses FL Studio project and preset files in Python.
Reviewed demberto/PyFLP@f937126
Binary · Case study:
An official educational challenge investigation connects binary checks to equations and records an original-program validation.
Reviewed morluto/rea@808339f
Binary · Case study:
An unofficial field study that reads REA's source and then drives the running server through 1,012 recorded calls across 27 artifact classes, measuring its content-addressed Evidence records, revision-chained unknown ledger, typed refusals, cold starts and response limits.
Reviewed no-flag.com/2026/10/18/REA-paper
Binary · Case study:
Fedele Mantuano reports using Codex with REA in an offline Docker lab to statically analyze a public Windows malware sample without executing it.
Reviewed codegeeksai.github.io/en/blog/static-malware-analysis-rea-c…
Binary · Case study:
A REA/Ghidra report studies the Ubuntu netcat-openbsd 1.234-1 ELF binary and publishes evidence envelopes, decompiled functions and a function inventory.
Binary · Case study:
The authors describe Woxi as a Rust interpreter for a subset of the Wolfram Language, focused on CLI scripting and Jupyter notebooks.
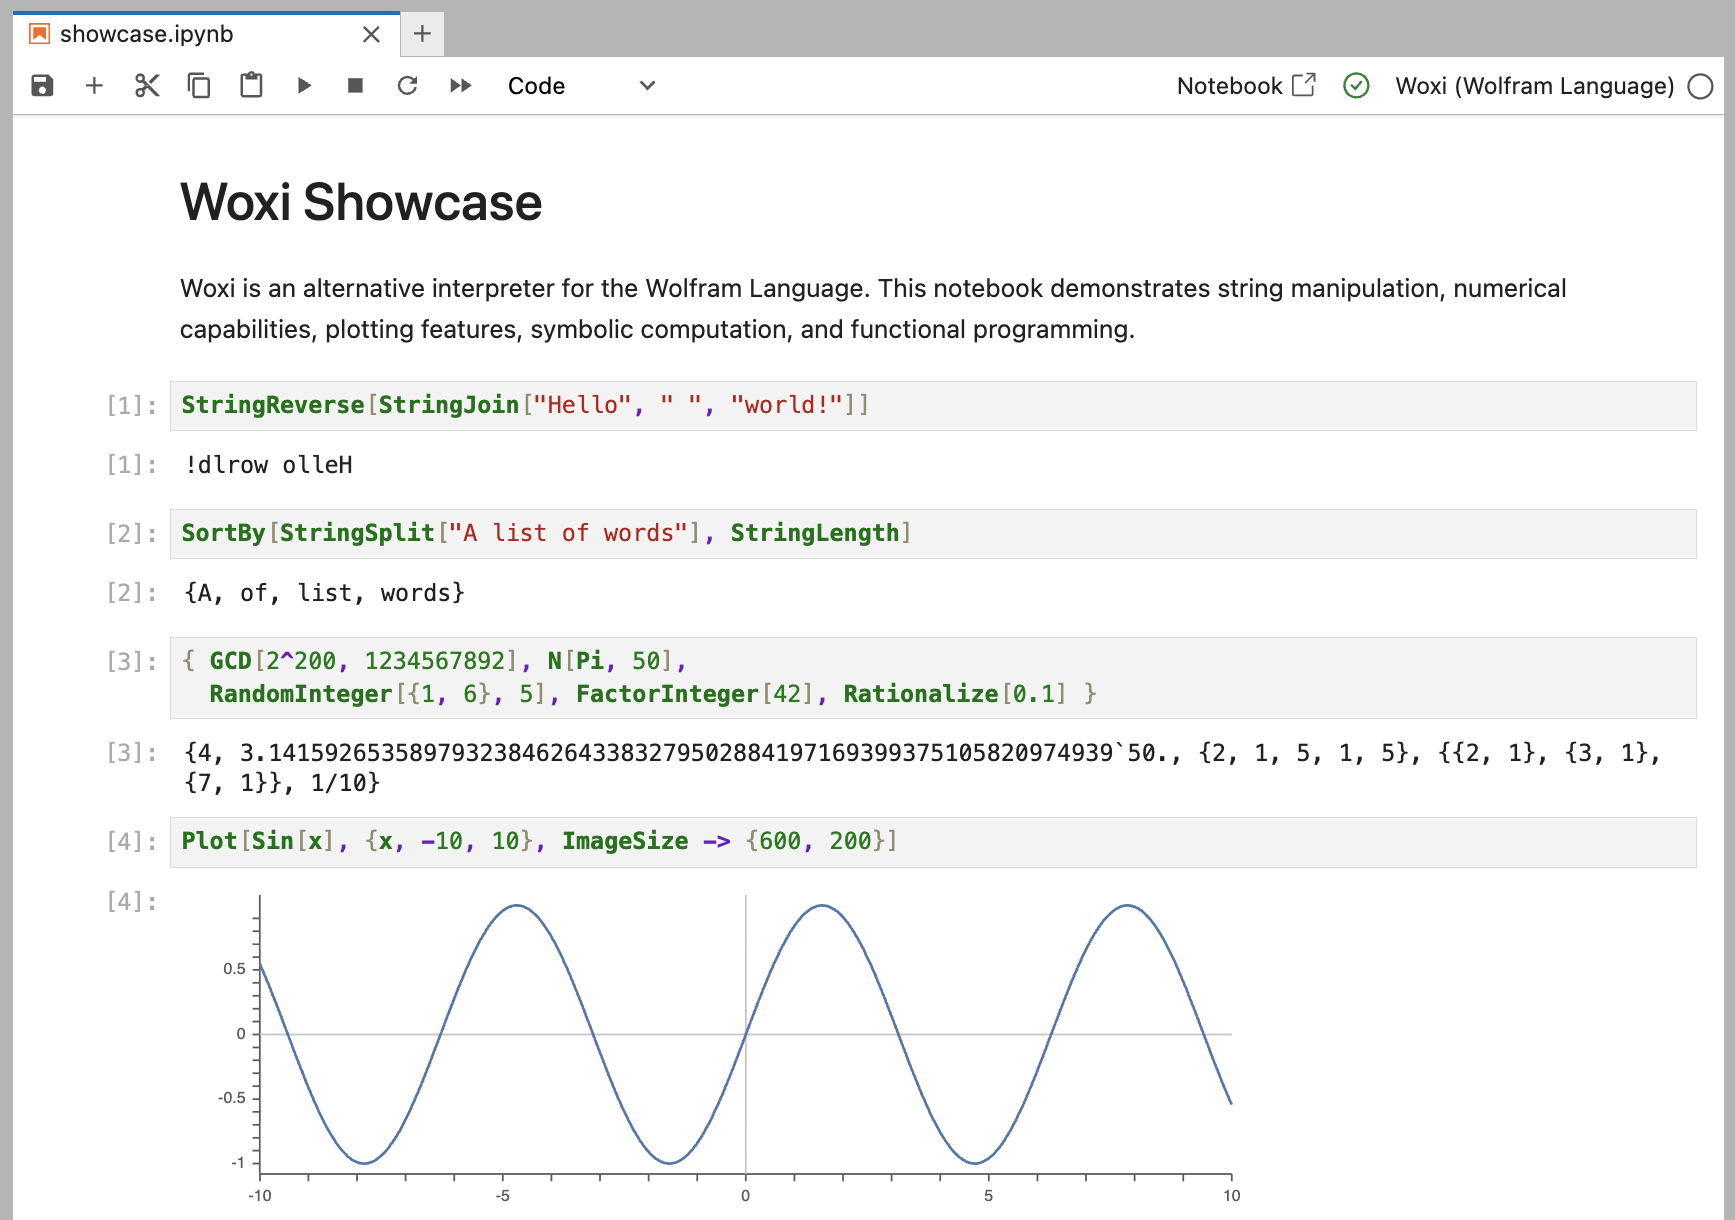
Reviewed ad-si/Woxi@09b106c
Binary · Case study:
uniswap-v2-reborn reconstructs Uniswap v2 factory, pair and Router02 behavior from deployed EVM runtime bytecode using REA interface inspection, storage probing and written specifications.
Binary · Case study:
Ports Eidolon, Poo-Brain’s winning PC 64k intro from Revision 2017, from its packed 60,928-byte Windows executable to Rust, with chapters on how the original binary works and a separate size-optimized build.
Binary · Case study:
The m0rph investigation examines an obfuscated x86-64 ELF CTF flag checker with readelf, strings, Cutter and Radare2.
Reviewed UmbertoDellaMonica/m0rph-CTF-CyberChallenge.IT@064dbf1
Binary · Case study:
CPQ IO Scheduler reconstructs Xiaomi's proprietary cpq.ko Linux block scheduler from a stripped ARM64 kernel module.
Reviewed Rasenkai/CPQ_IOSched@ed59893
Binary · Case study:
A malware investigation examines njRAT and a UPX-packed Casdet executable with PEStudio static triage and ANY.RUN sandbox telemetry, alongside a malicious PDF and benign comparison files.
Reviewed phour44/Malware-Analysis@c30cab3
Binary · Case study:
An FSR 4.1.1 INT8 investigation reconstructs the upscaler’s GPU passes in HLSL and compares their outputs with AMD’s compiled kernels through a D3D12 harness.
Binary · Case study:
bcwc_pcie audits the community FaceTime HD Linux driver against Apple's AppleCameraInterface.kext for Broadcom PCI 14e4:1570 cameras.
Reviewed unfallenwill/bcwc_pcie@8ed2655
Binary · Case study:
XexTool-RE reimplements the closed XexTool utility from analysis of its binary and processes Xbox 360 .xex executables.
Reviewed mrtitanic777/XexTool-RE@c421d37
Binary · Case study:
slopgs reconstructs the behavior of the Windows XP SP3 Microsoft GS Wavetable Synth driver in a portable C synthesizer.
Reviewed sloptainment/slopgs@9eb9433
Binary · Case study:
SP11X1e-audio reconstructs Surface Pro 11 speaker and internal microphone behavior on Linux from Windows runtime observations and binary analysis.
Reviewed geocausa/SP11X1e-audio@3232e1d
Binary · Case study:
uniq-reconstruction rebuilds GNU coreutils 9.7 uniq in C from black-box observations of a stripped ELF executable.
Reviewed daedalus/uniq-reconstruction@a1f1c18
Binary · Case study:
Watcom C 6.5 run-time library restoration rebuilds damaged CLIBS.LIB and CLIBC.LIB from surviving archive modules.
Binary · Case study:
IOReport decompile investigates Apple’s IOReport dylib, which provides calls for reading system reports and counters.
Binary · Case study:
dargh reconstructs the Dynamic Animation Replacer DLL for Skyrim Special Edition in C++ from analysis of versions 1.1.2 and 1.1.3.
Reviewed noxsidereum/dargh@cb91016
Binary · Case study:
ndec-re investigates an old MS-DOS COM encryption program through debugger-assisted assembly analysis and implements its encryption behavior in Go.
Reviewed bereal/ndec-re@12ae44a
Binary · Case study:
re-sysinternals-suite records an educational rebuild of the Sysinternals strings.exe executable.
Binary · Case study:
ExCrypt reconstructs Xbox 360 XeCrypt functions as a C and C++ replacement for use with existing console code and data.
Reviewed emoose/ExCrypt@0880945
Binary · Case study:
L1J-Encode-CLI reconstructs the Lineage 1 launcher's ServerData encoding as a Python encoder and decoder for IP addresses, ports, and feature flags.
Reviewed Lan-0v0/L1J-Encode-CLI@997e255
Binary · Case study:
Wirenet Reverse Engineering investigates the Wirenet Linux trojan through recovered source code and an Italian analysis report.
Reviewed shxdow/wirenet-analysis@862fce0
Binary · Case study:
SNES Station Decompilation reconstructs the PlayStation 2 SNES Station v0.23 WIP executable through source recovery, historical toolchain matching and image comparison.
Reviewed ReyFxck/SNESstation-Decomp@74403ac
Binary · Case study:
RFL reconstructs the Wii library responsible for handling Miis from an original game image.
Reviewed koopthekoopa/RFL@db7c33a
Binary · Case study:
cod4map reconstructs the BSP compiler shipped with the 2007 Call of Duty 4 mod tools from its executable.
Reviewed prd0nja/cod4map@fc4226b
Binary · Case study:
The project reconstructs AGS Aging Cartridge 7.0 from a user-supplied Game Boy Advance ROM as assembly and C source.
Reviewed Normmatt/ags_aging@e4b2edf
Binary · Case study:
OtterSec researchers describe an agent pipeline that reconstructed Rust source for the closed-source GoonFi V2 Solana program until a rebuild with the original toolchain reproduced the deployed ELF.
Reviewed osec.io/blog/goonfi-decompilation
Binary · Case study:
Statically recompiles HyperCard 1.2.2, a classic Mac application.
Reviewed sp00nznet/macrecomp@708adac
Binary · Case study:
A from-scratch C reimplementation of the Berkeley Speech Technologies formant synthesizer sold as BeSTspeech and shipped in HumanWare Keynote GOLD.
Reviewed Mudb0y/openbst@a151e78
Binary · Case study:
Rebuilds Centigram TruVoice, the 1997 text-to-speech engine, as portable C.
Reviewed RetroBunn/tv-decomp@8488e51
Binary · Case study:
Rebuilds Lernout & Hauspie TruVoice 6.00 build 10, the SAPI 4 American English engine in tv_enua.dll, as C99.
Binary · Case study:
Rebuilds Microsoft Anna, the Windows Vista and Windows 7 TTS20 voice, as C99 that reads the original voice data files.
Reviewed KamiKitsune420/ms-ana-decomp@a8da046
Binary · Case study:
Rebuilds the Windows OneCore text-to-speech engine MSTTSEngine_OneCore.dll 10.3, the David, Zira, and Mark voices, as C99 that reads the original voice files.
Binary · Case study:
Rebuilds the Windows XP SAPI 5 engine spttseng.dll for Microsoft Sam, Mike, and Mary as C99 that reads the original voice files.
Binary · Case study:
Rebuilds ETI Eloquence 6.1.0.2, the US English ECI.DLL plus ENU.SYN, as C with a drop-in ECI.DLL for x86 and x64.
Binary · Case study:
Decompiles the Speech Plus and Telesensory Systems Prose 2000 text-to-speech firmware, an 8086 host plus an NEC uPD7720 DSP, into C.
Reviewed rommix0/prose2000_reborn@26c36db
Binary · Case study:
Reorganized cc65 source for GEOS 2.0 on the Commodore 64 and 128.
Reviewed mist64/geos@617efdc
Binary · Case study:
Reverse-engineered cc65 source for geoWrite 2.1, the GEOS word processor, in English and German.
Reviewed mist64/geowrite@640f1ab
Binary · Case study:
A C99 library of the E-mu SP-1200 and SP-12 sampler audio path: pitch playback, filters, and the dynamic filter.
Reviewed Mudb0y/libmd12@427c8e3
Binary · Case study:
A drop-in dsound.dll that reimplements Creative ALchemy and DirectSound behavior, including DirectMusic pieces the README names.
Reviewed PlayNeth/reAL@b68e4d1
Binary · Case study:
Konami's Game Master reconstructs the Japanese RC-735 MSX utility cartridge as annotated assembly.
Reviewed ricbit/game-master@b1ca2ef
Binary · Case study:
dolnetbp reconstructs the GameCube Dolphin Network Base Package eth, mdm and netcfg libraries in C.
Reviewed Cuyler36/dolnetbp@ba3846a
Binary · Case study:
Dolphin SDK 2004 Libraries reconstructs the built code libraries of the April 20, 2004 Dolphin SDK as C and assembly sources.
Reviewed doldecomp/dolsdk2004@2328b41
Binary · Case study:
dolsocketlibrary reconstructs the Dolphin Network Base Package ip and dvdeth libraries in C.
Reviewed Cuyler36/dolsocketlibrary@e023566
Binary · Case study:
open_rvl reconstructs the Wii SDK version found in Wii Sports as C source for reuse in game decompilations.
Reviewed kiwi515/open_rvl@af505ae
Binary · Case study:
NW Eft decompiles the NintendoWare for Cafe Eft library found in the Wii U game New Super Mario Bros. U. Its C++ source and headers cover emitters, rendering and related library components.
Reviewed open-ead/NW4F-Eft@8ea1127
Binary · Case study:
libgpu2 reconstructs Sony's 1998 PlayStation 2 Graphics Synthesizer software model from 23 ELF32/i386 objects as buildable C++.
Reviewed aap/libgpu2@89c9c4d
Binary · Case study:
re_nfpii reimplements the Wii U nn_nfp.rpl library for amiibo emulation and research.
Reviewed GaryOderNichts/re_nfpii@cbb6136
Binary · Case study:
MWCC reconstructs six Windows x86 versions of the GameCube CodeWarrior compiler mwcceppc.exe.
Reviewed rayanht/mwcc@92f893f
Binary · Case study:
GA330-libretro reconstructs the Gemei A330 runtime as a libretro core using Unicorn to execute ARM application binaries.
Reviewed minexew/GA330-libretro@e69dd92
Binary · Case study:
linker_pc reconstructs the fastfile linker distributed with the Call of Duty 4 mod tools from its shipped 2008 executable.
Reviewed prd0nja/linker_pc@5e295a8
Binary · Case study:
EGG Library is a work-in-progress decompilation of a Wii software library, aiming to share one source set across multiple games and applications.
Reviewed vabold/EGG@9b80879
Binary · Case study:
NitroSDK Decompilation reconstructs Nintendo DS SDK library source from code extracted from supported game ROMs.
Reviewed nitro-decomp/nitro@10e447b
Binary · Case study:
Hagi decompiles the GameCube and Wii emulator executable included with Super Mario Sunshine in Super Mario 3D All-Stars version 1.0.0.
Reviewed GRAnimated/Hagi@a1d1740
Binary · Case study:
Character Pipeline April 2001 Libraries reconstructs C source for the component's built code libraries.
Reviewed doldecomp/dolcp-apr2001@0d3aed5
Binary · Case study:
This repository disassembles BIOS images from 8088 machines: the Tandy 1000, Tandy 1000A, Tandy 1000 HX, IBM PCjr, and IBM PC 5150.
Reviewed ricardoquesada/bios-8088@6dc405d
Binary · Case study:
lv0pen rebuilds PlayStation 3 boot-chain programs and isolated SPU modules with the original compilers.
Reviewed sagemono/lv0pen@14584b7
Binary · Case study:
This decompiles the Wii Forecast Channel, version HAFE v7, USA/NTSC.
Reviewed doldecomp/forecast@92a5782
Binary · Case study:
This is a work-in-progress decompilation of the Xbox 360 kernel, file set 21256.18_D, kernel version 17489.0.
Reviewed AleBello7276/xkrnl-decomp@cfe7a00
Binary · Case study:
PICOLOVE implements the PICO-8 API in LÖVE so PICO-8 carts can run as LÖVE programs.
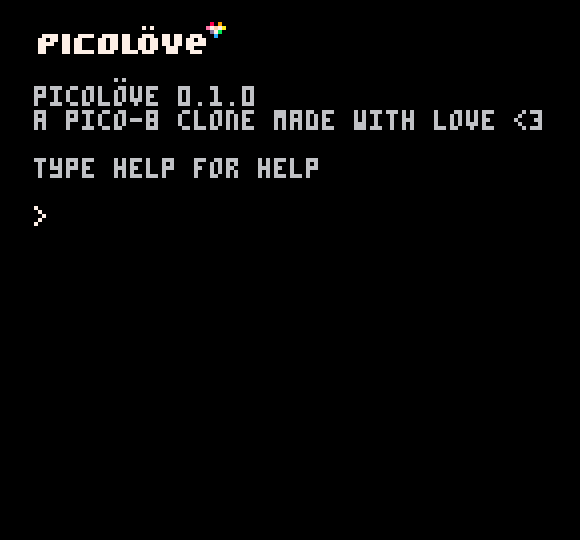
Reviewed picolove/picolove@97075db
Binary · Case study:
DLSS 5 Neural Rendering reconstructs parts of NVIDIA's model from static analysis of nvngx_dlssnr.dll 310.8.0.0 shipped with NBA 2K27.
Reviewed huggingface.co/inarikami/dlss5-nr-reverse-engineerin…
Binary · Case study:
linux-apfs-rw reconstructs support for Apple's APFS filesystem in a Linux kernel module using reverse-engineered format knowledge and an incomplete official specification.
Reviewed linux-apfs/linux-apfs-rw@cb9c0a0
Binary · Project:
A dataset of binary-source function pairs published for the LLM4Decompile project.
Reviewed huggingface.co/datasets/LLM4Binary/decompile-bench/b…
Binary · Project:
This repository holds Ghidra Function ID datasets generated with ghidra-fid-generator from a manual selection of libraries.
Reviewed threatrack/ghidra-fidb-repo@aaa36e3
Binary · Project:
BinaryAudit is a benchmark of AI agents looking for backdoors in compiled binaries of open-source software.
Reviewed QuesmaOrg/BinaryAudit@175b7ec
Game · Project:
Zakuro is a high-level Nintendo 3DS emulator written in Rust.
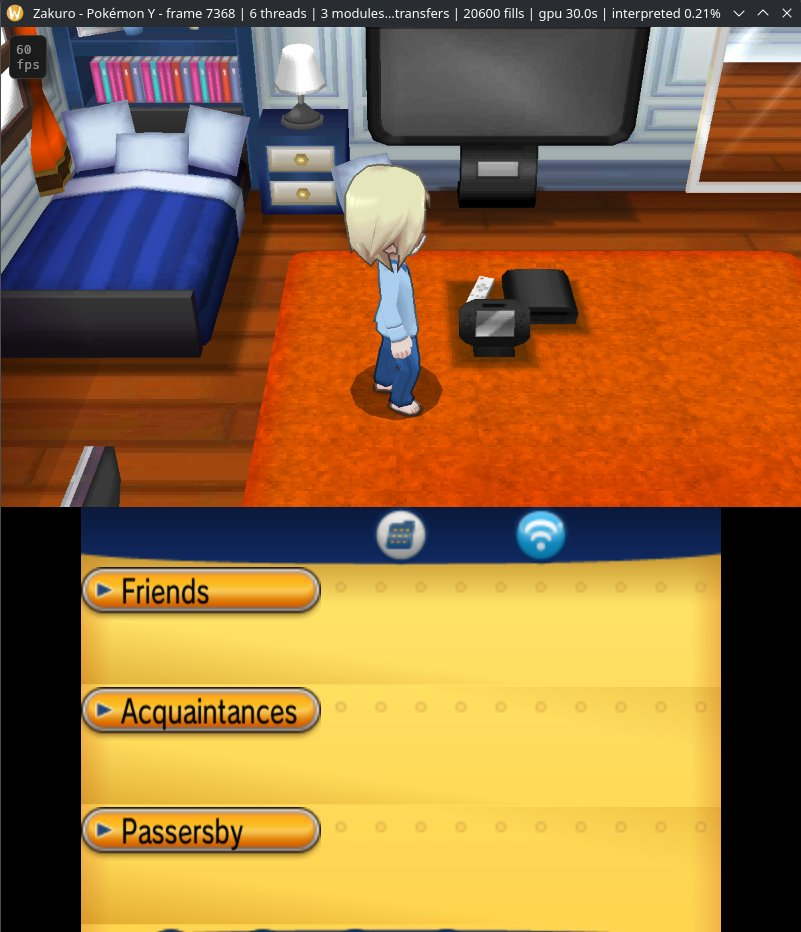
Reviewed fearkov/zakuro@c856685
Protocol · Project:
Luxon Server is a clean-room implementation of the Photon Realtime server.
Reviewed niansa/LuxonServer@e70722a
Game · Project:
FreeVGUI reimplements the Half-Life 1 VGUI library.
Reviewed FWGS/freevgui@410c35c
Firmware · Tool:
Identifies embedded formats and optionally extracts their contents, with entropy analysis for firmware triage.
Reviewed ReFirmLabs/binwalk@e0a4434
Firmware · Tool:
Recursively extracts archives and filesystems from binary blobs while reporting chunk boundaries and unknown regions.

Reviewed onekey-sec/unblob@3b470cd
Firmware · Tool:
Ghidra loaders and helpers for PCI option ROMs, UEFI firmware volumes, Intel flash descriptors and coreboot images.
Firmware · Tool:
Extract firmware, combine static checks with emulation-based analysis, inventory software components, and generate web reports and SBOMs for further investigation.
Reviewed e-m-b-a/emba
Firmware · Tool:
Unpack and analyze firmware through an extensible platform whose web interface and HTTP API make component contents and analysis results searchable and comparable across samples.
Reviewed fkie-cad/FACT_core@dc594e8
Firmware · Tool:
Recursively identify, unpack, analyze, modify, and repack firmware and binary formats using a resource-tree GUI and Python API, with optional disassembler backends.

Reviewed redballoonsecurity/ofrak@1e1ef75
Firmware · Tool:
Emulate router and IP-camera firmware to inspect network services and runtime behavior, with automated emulation checks and separate analysis, run, and debugging modes.
Reviewed pr0v3rbs/FirmAE@653565b
Firmware · Tool:
Examine captured logic and analog waveforms with sigrok's graphical frontend.
Reviewed sigrokproject/pulseview@af02198
Firmware · Tool:
Parse UEFI firmware images into an inspectable tree and check their structure.
Reviewed LongSoft/UEFITool@dac91b2
Firmware · Tool:
Use FPGA-based open hardware and Python applets to read and write SPI flash, I2C EEPROM and parallel memory chips, determine JTAG pinouts, debug supported processors and analyze UART, SPI and QSPI transactions on physical devices.
Reviewed GlasgowEmbedded/glasgow@d51713b
Firmware · Tool:
Rehost embedded Linux firmware from an extracted root filesystem using a generated, editable configuration of emulation transformations, then refine it through a guest root shell, forwarded network services and recorded dynamic-analysis output.
Reviewed rehosting/penguin@b645cd2
Firmware · Tool:
Command-line toolkit for Apple firmware research and reverse engineering.
Reviewed blacktop/ipsw@a9eae76
Firmware · Tool:
Python framework from EURECOM's S3 group that orchestrates emulators, debuggers and physical devices for dynamic analysis of embedded firmware.
Reviewed avatartwo/avatar2@56a90cf
Firmware · Tool:
IDA Pro plugin and loader that automate static analysis of UEFI firmware.
Reviewed REhints/efiXplorer@9e3b40a
Firmware · Tool:
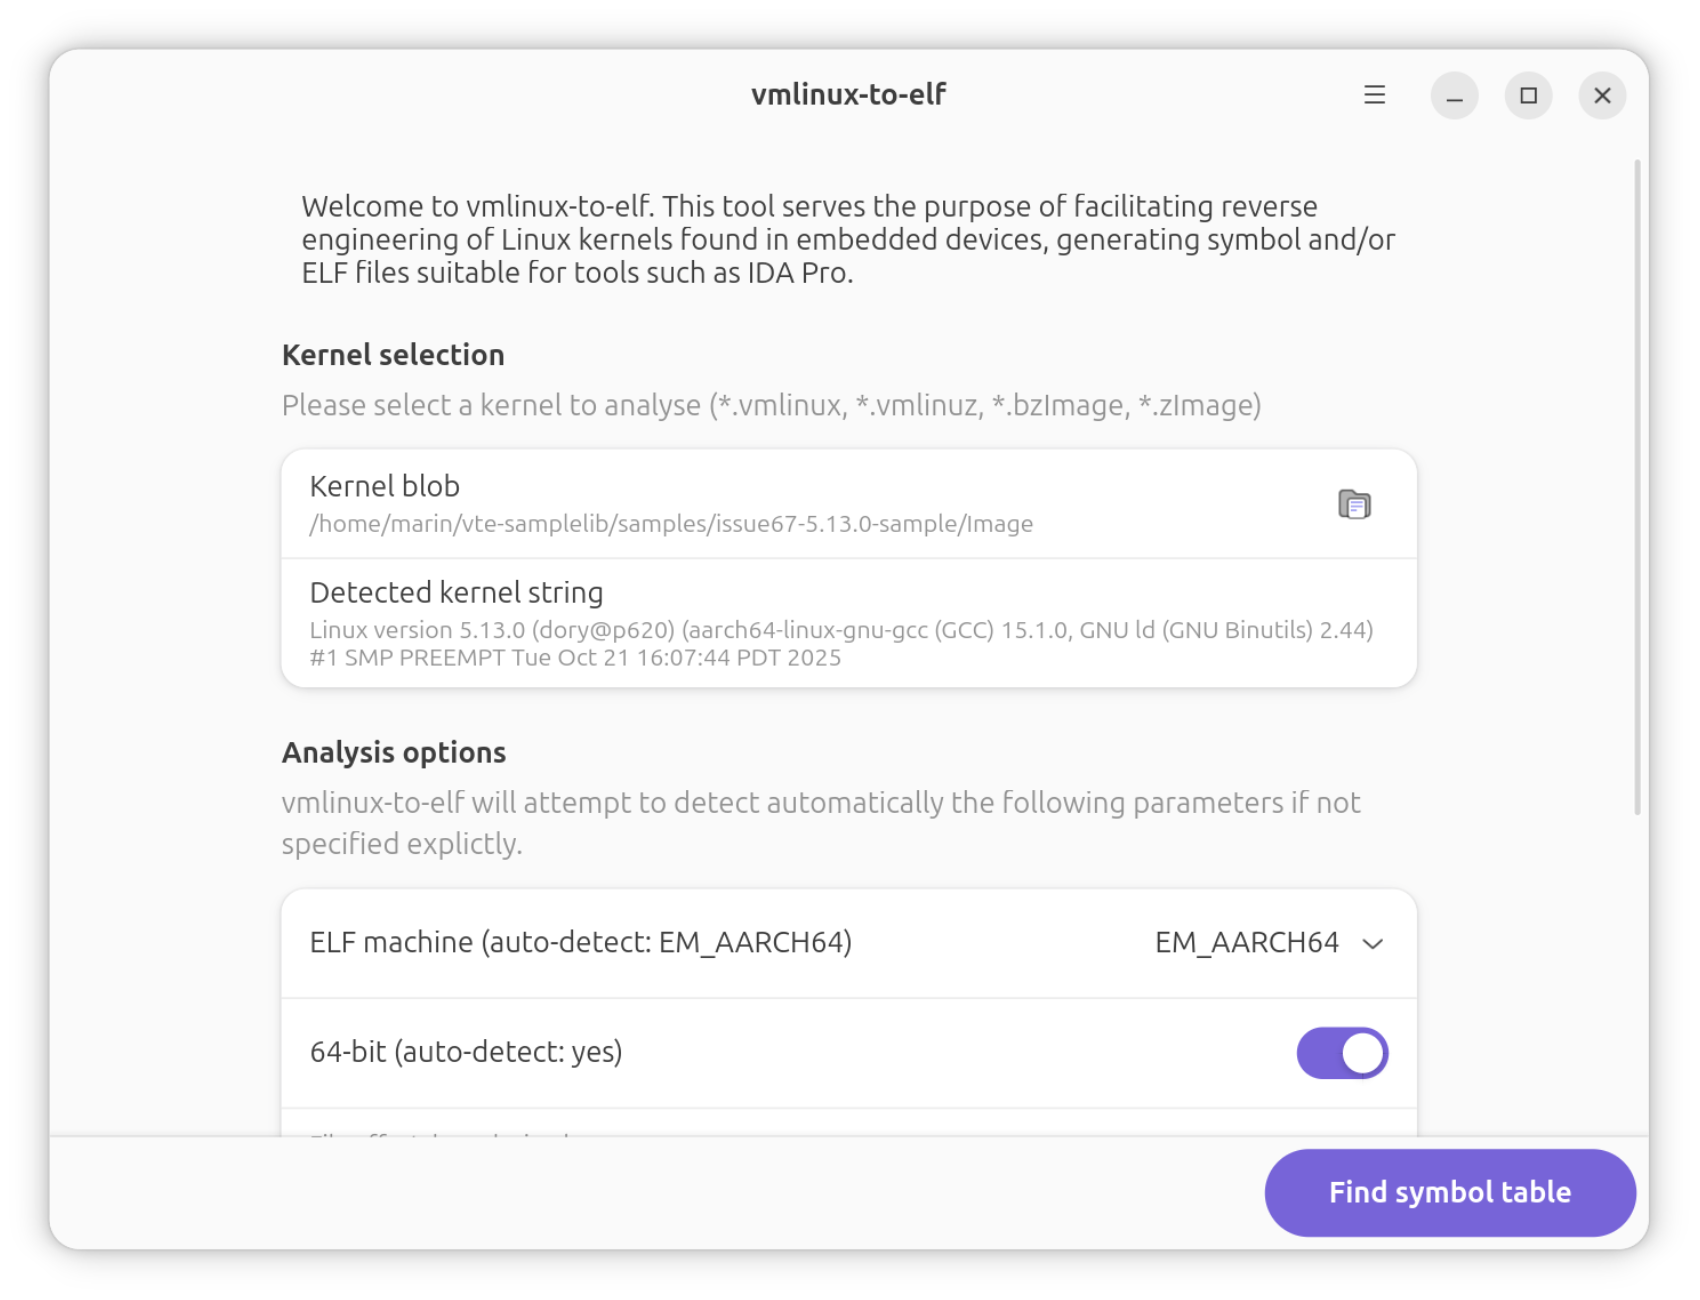
Rebuild an analyzable ELF with function and variable symbols from a Linux kernel image, whether a raw or compressed vmlinux, vmlinuz, zImage or bzImage blob, certain Android boot.img files or a stripped kernel ELF, by locating and decoding the embedded kallsyms symbol table.
Reviewed marin-m/vmlinux-to-elf@2d094bc
Firmware · Tool:
USB tool built from reverse engineering Sony digital cameras.
Reviewed ma1co/Sony-PMCA-RE@a82f5ba
Firmware · Tool:
Statistically recognize the CPU instruction set in an arbitrary binary file, such as an unknown firmware image, by comparing Markov-chain byte statistics with a default corpus covering dozens of architectures, from 6502 and 8051 to ARM, MIPS, PowerPC, RISC-V, x86-64 and WebAssembly.
Reviewed airbus-seclab/cpu_rec@6b19239
Firmware · Tool:
Parse Intel Management Engine (CS)ME, TXE and SPS firmware, Graphics System Controller firmware and their independent PMC, PCHC, PHY and option-ROM images to report family, version, release, SKU, platform, size and health status.
Reviewed platomav/MEAnalyzer@d27ccdb
Firmware · Tool:
Platform security assessment framework, with Intel Corporation copyright notices, for analyzing PC hardware configuration, BIOS/UEFI system firmware and platform components from Windows, Linux or the UEFI shell.
Reviewed chipsec/chipsec@c117563
Firmware · Tool:
Quarkslab command-line tool that infers basic properties of a headerless raw firmware image from simple statistics on its content, which is why the README says it works with any architecture.
Reviewed quarkslab/binbloom@95cfaac
Firmware · Tool:
Asahi Linux's bootloader and hardware-research environment for Apple Silicon Macs.
Reviewed AsahiLinux/m1n1@7cde7d1
Firmware · Tool:
Ghidra script from leveldown security that reads a CMSIS-SVD file, the XML format describing a microcontroller's memory-mapped peripherals and their registers, and applies it to firmware already loaded in Ghidra.
Firmware · Tool:
Python library and uefi-firmware-parser command for identifying, parsing and extracting PC firmware images: UEFI firmware volumes, capsules, firmware file systems, files and sections, Intel PCH flash descriptors, Intel ME modules and Dell PFS update packages.
Firmware · Tool:
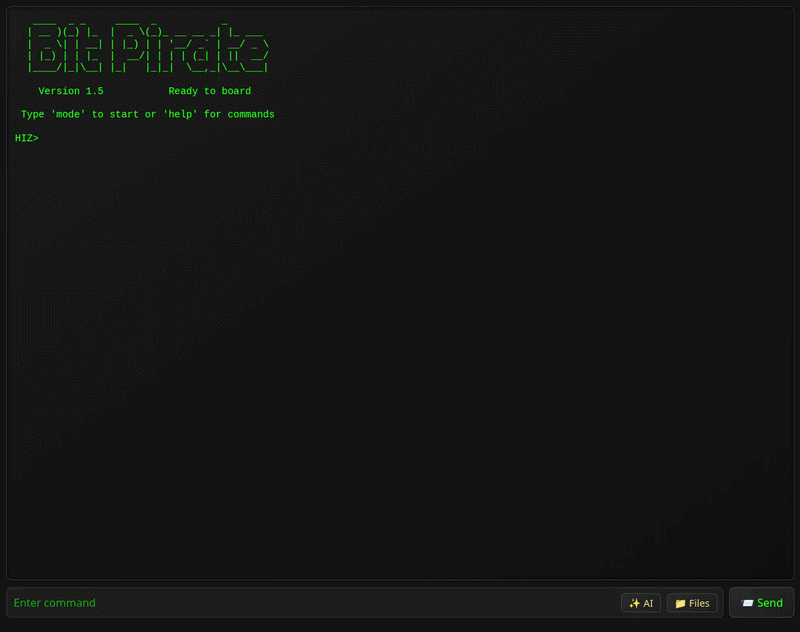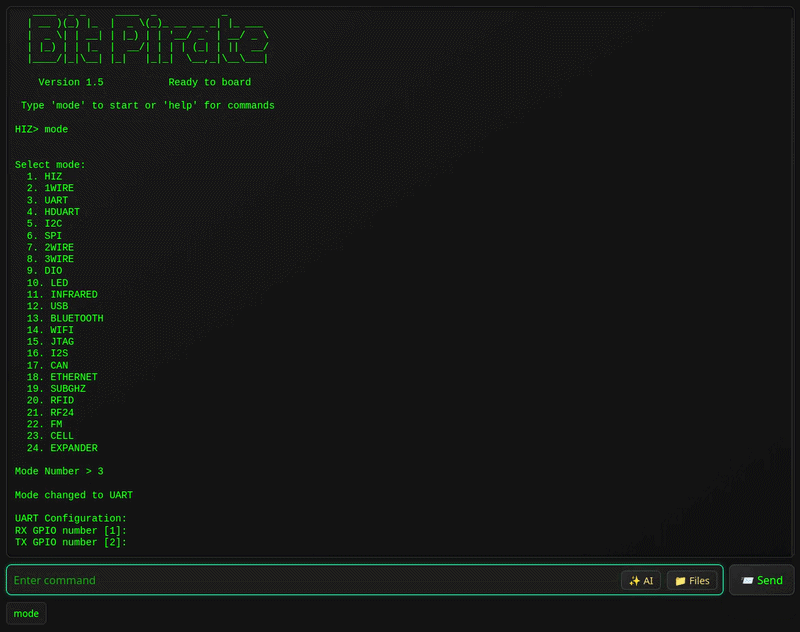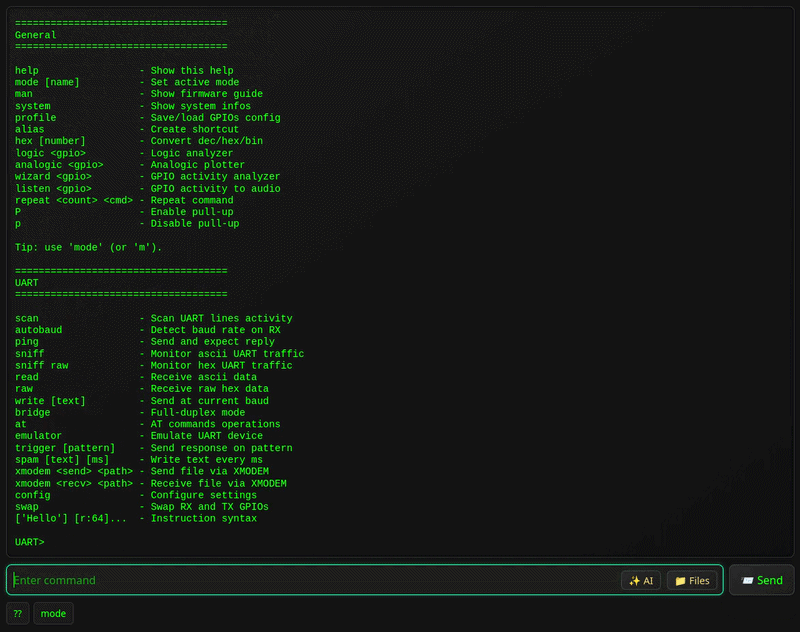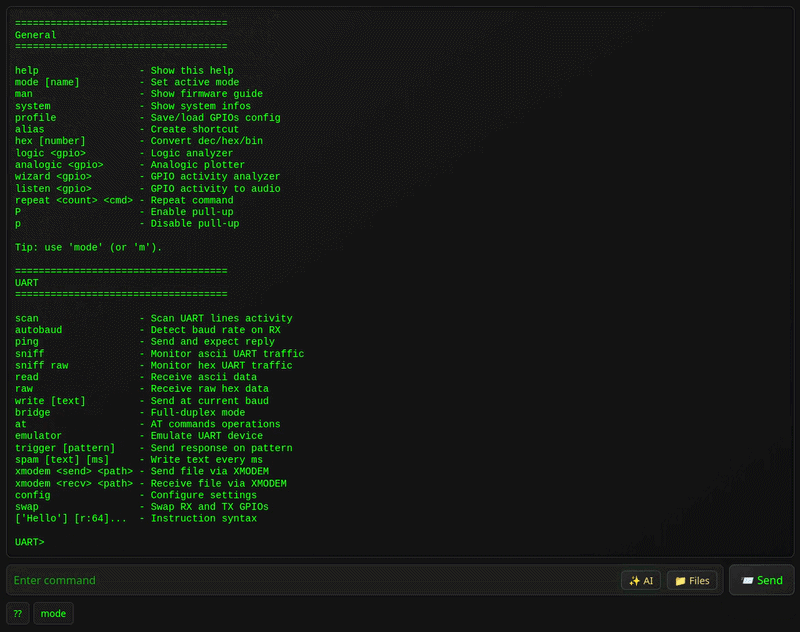
Open-source firmware that turns ESP32-S3 boards into a Bus Pirate-inspired multi-protocol hardware tool, operated from a USB serial terminal, a Wi-Fi web CLI or the M5 Cardputer's own keyboard and screen.
Reviewed geo-tp/ESP32-Bit-Pirate@8a91778