Firmware · Case study:
Nuked MD: reconstructing the Sega Mega Drive chipsetC1
Nuked MD reconstructs Sega Mega Drive chipset behavior in C using decapped chip photographs.
- Firmware
Reviewed nukeykt/Nuked-MD@594ca2a
Firmware · Case study:
Nuked MD reconstructs Sega Mega Drive chipset behavior in C using decapped chip photographs.
Reviewed nukeykt/Nuked-MD@594ca2a
Firmware · Case study:
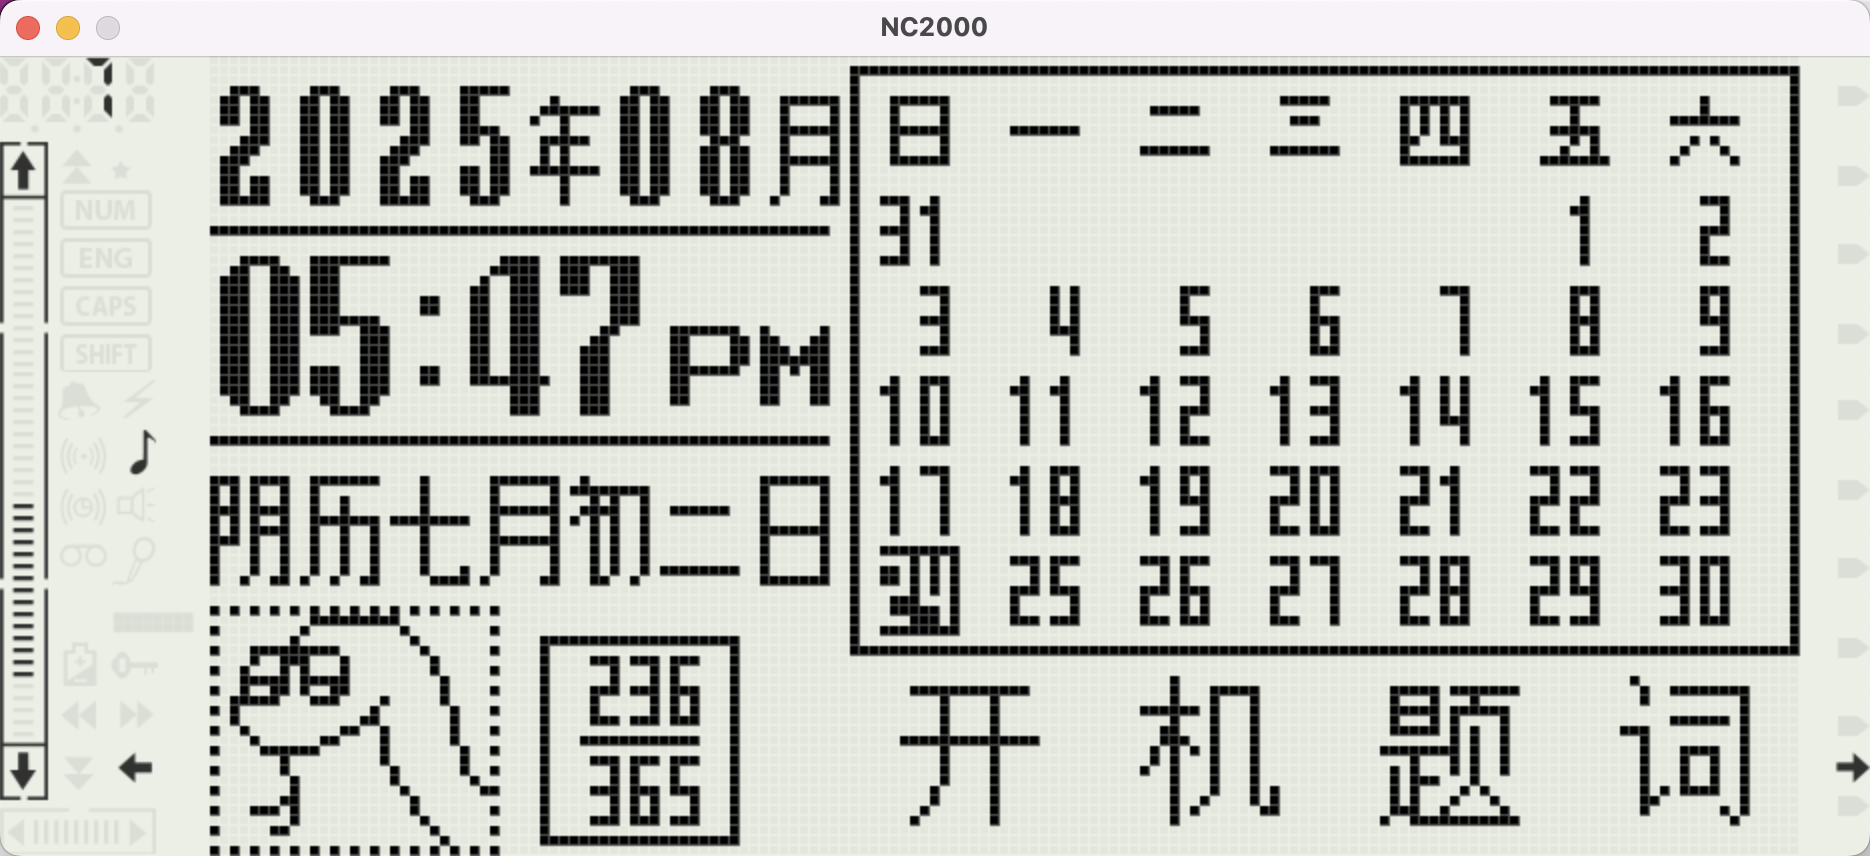
NC2000/1020Emu reconstructs the hardware environment needed to run firmware dumped from Wenquxing NC2000, NC2600 and NC1020 portable computers.
Reviewed wangyu-/NC2000@b281c13
Firmware · Case study:
m-bootloader reconstructs the boot and flash interfaces of the M-VAVE FM-1 and SMK-37 Pro/Elite synthesizers built around the JieLi AC791N chip.
Reviewed jvitkauskas/m-bootloader@724ae41
Firmware · Case study:
CEN64 emulates Nintendo 64 hardware and aims to model it down to register-transfer level.
Reviewed n64dev/cen64@e0641c8
Firmware · Case study:
Orbital reconstructs PlayStation 4 hardware in a virtualization-based emulator intended to boot decrypted console kernels.
Reviewed AlexAltea/orbital@cc40836
Firmware · Case study:
TamaLIB emulates first-generation Tamagotchi devices built around Epson E0C6S46 and E0C6S48 microcontrollers, allowing their program ROMs to run on other hardware.
Reviewed jcrona/tamalib@ce304d5
Firmware · Case study:
The Quansheng UV-K5 Hardware Reverse Engineering Project reconstructs the radio's V1.4 PCB as KiCad schematic and board files.
Reviewed mentalDetector/Quansheng_UV-K5_PCB_R51-V1.4_PCB_Reversing_Rev._0.9@9fc1953
Firmware · Case study:
orsala_hack reconstructs the control behavior of the IKEA ORSALA lamp in replacement STM8 firmware.
Reviewed j-zero/orsala_hack@38984da
Firmware · Case study:
stf-sharc reconstructs and annotates the two ADSP-21062 microcode images used by Sega Model 2 hardware.
Reviewed biggestsonicfan/stf-sharc@474c90d
Firmware · Case study:
F3DEX2 is a set of matching disassemblies of the Nintendo 64 F3DEX2 and F3DZEX2 RSP microcode family.
Reviewed Mr-Wiseguy/f3dex2@bd31393
Firmware · Case study:
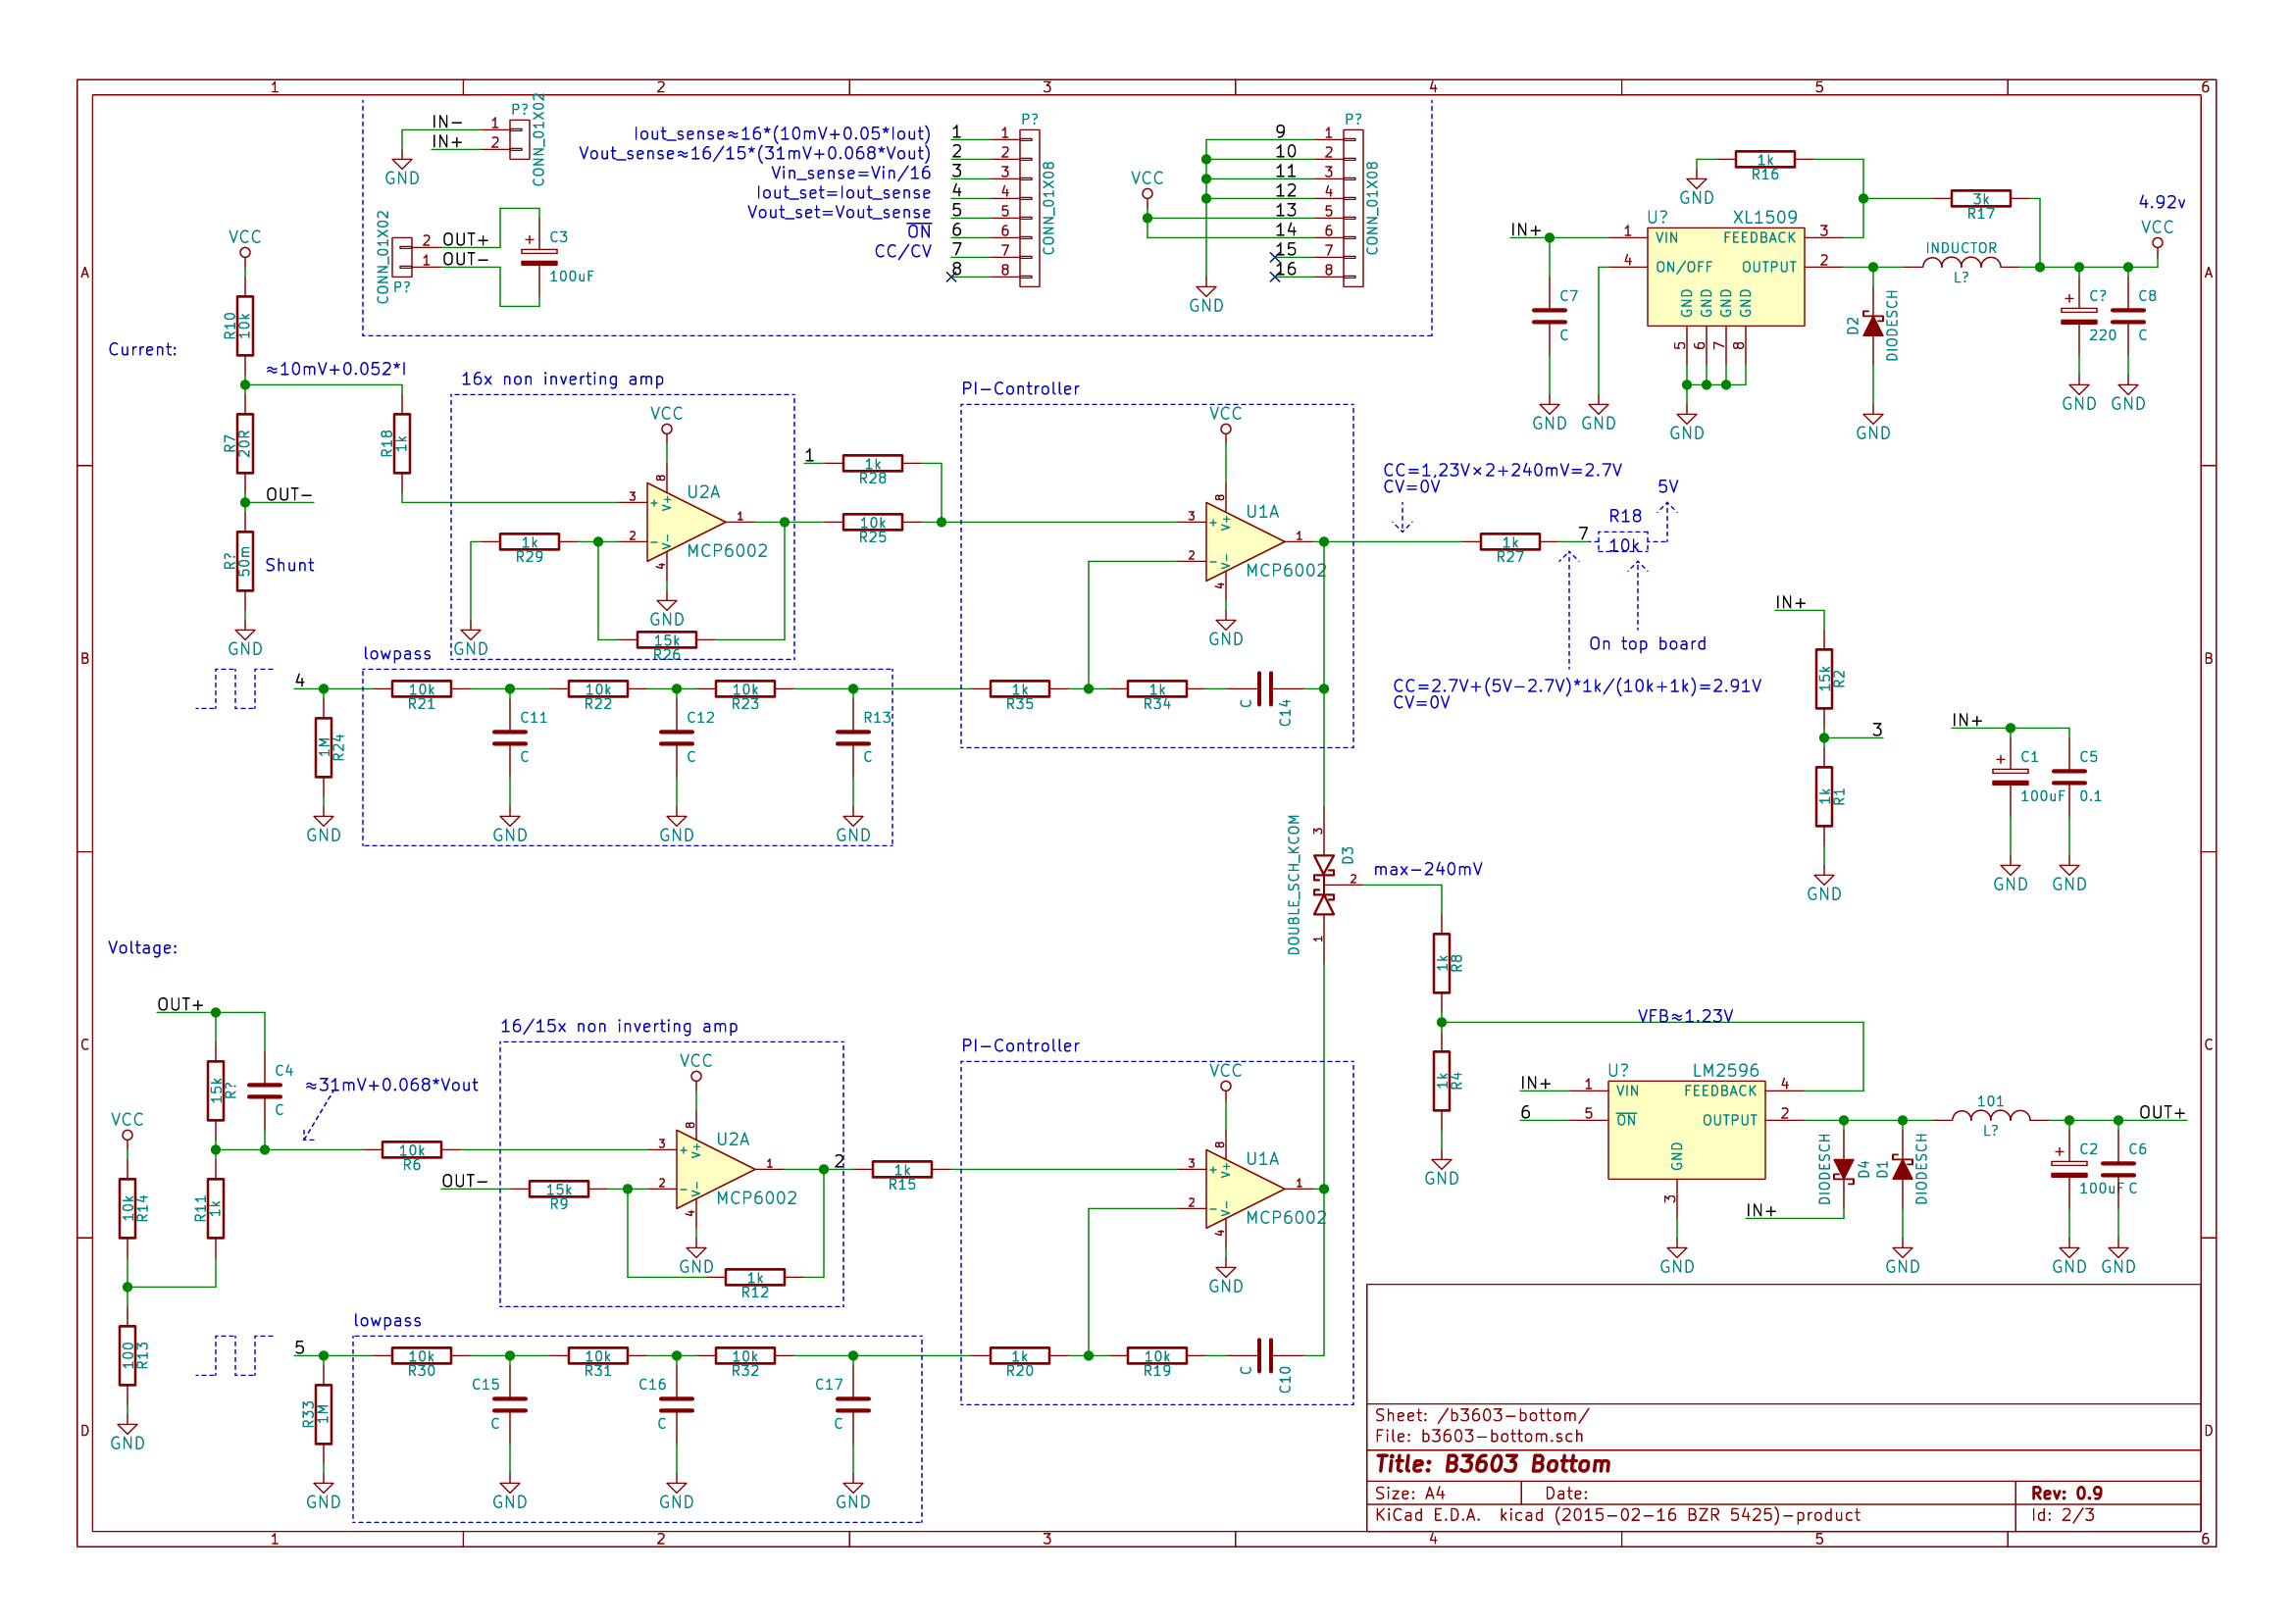
B3603 investigates the buck converter's control board to support replacement STM8 firmware.
Reviewed baruch/b3603@1244057
Firmware · Case study:
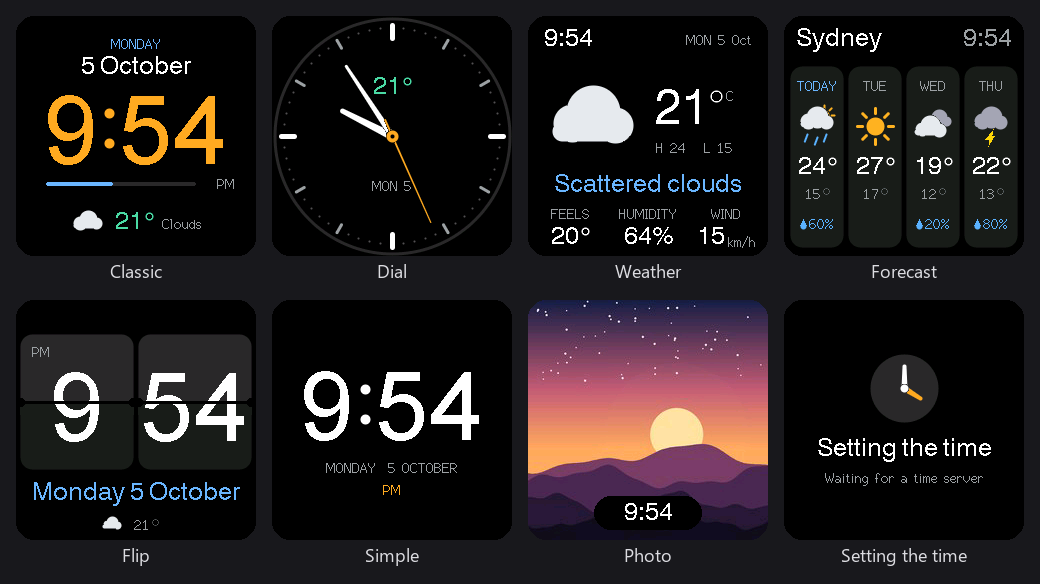
SmartClock-OSS rebuilds firmware for the SD Pro Smart Weather Clock after analysis of its stock image and flash layout.
Reviewed michaeldale/smartclock-oss@b214f30
Firmware · Case study:
The Radtel RT-890 project reimplements version 1.34 of the radio's firmware as C source to study device behavior.
Firmware · Case study:
Macrosilicon Custom Firmware studies the 8051 mask ROM and EEPROM loading behavior of MS2107, MS2109 and MS9123 USB video chips, then builds replacement EEPROM images.
Reviewed kraln/macrosilicon_firmware@caa3d27
Firmware · Case study:
Obliteration reconstructs the PlayStation 4 kernel in Rust for a custom virtualization stack intended to run dumped PS4 system software on Windows, Linux, and macOS.
Reviewed obhq/obliteration@2a53d5c
Firmware · Case study:
libElysianVMU reconstructs the Sega Dreamcast Visual Memory Unit as a C17 emulator core.
Reviewed gyrovorbis/libevmu@2b15502
Firmware · Case study:
Digimon V-Pet investigates the 1997 Digital Monster firmware, focusing on Ver.
Firmware · Case study:
BCM5719 Firmware Reimplementation rebuilds firmware for the Broadcom BCM5719 network controller from the Ortega specification.
Reviewed meklort/bcm5719-fw@3bc3260
Firmware · Case study:
The X-40 laser rangefinder study reconstructs the tape measure's circuit and replaces its firmware for DIY distance measurement.
Firmware · Case study:
CatCard implements Rust replacement firmware for Coldcard mk3, mk4, mk5 and Q1 hardware.
Reviewed TibaneLabs/catcard@038c37c
Firmware · Case study:
LaiNES reconstructs NES console behavior in a cycle-level emulator.
Reviewed AndreaOrru/LaiNES@1f3d126
Firmware · Case study:
EP4CE6 Bitstream Reverse Engineering maps the proprietary .rbf configuration format of the Cyclone IV EP4CE6F17C8 FPGA.
Reviewed 14sea/Cyclone_CRAM_Mapper@221f790
Firmware · Case study:
Powar emulates the Pokéwalker using a user-supplied ROM and EEPROM image.
Reviewed UnrealPowerz/powar@df3ca7e
Firmware · Case study:
GameCube IPL investigates the USA retail GameCube BootROM and develops replacement IPL code.
Reviewed ogamespec/gc-ipl@0d8ec09
Firmware · Case study:
GoPro Metadata Format Parser maps the GPMD telemetry stream embedded in GoPro Hero 5 MP4 recordings and provides Go readers and conversion commands.
Reviewed stilldavid/gopro-utils@f0186d2
Firmware · Case study:
uOFW reconstructs PSP kernel and hardware behavior to produce technical documentation and open source firmware.
Reviewed uofw/uofw@28306bb
Firmware · Case study:
canon_cr3 maps Canon camera image files, especially the CR3 container and its CRX image structures.
Reviewed lclevy/canon_cr3@151c1a9
Firmware · Case study:
qemu-esp32-wireless reconstructs ESP32 Wi-Fi and Bluetooth LE hardware behavior in QEMU to run stock ESP-IDF firmware and its wireless blobs.
Reviewed codeberg.org/oHn017ss3ad1/qemu-esp32-wireless/src/…
Firmware · Case study:
rpi-open-firmware implements a replacement for the Raspberry Pi's stock VPU bootcode.bin and documents the device's boot stages.
Reviewed librerpi/rpi-open-firmware@2725d94
Firmware · Case study:
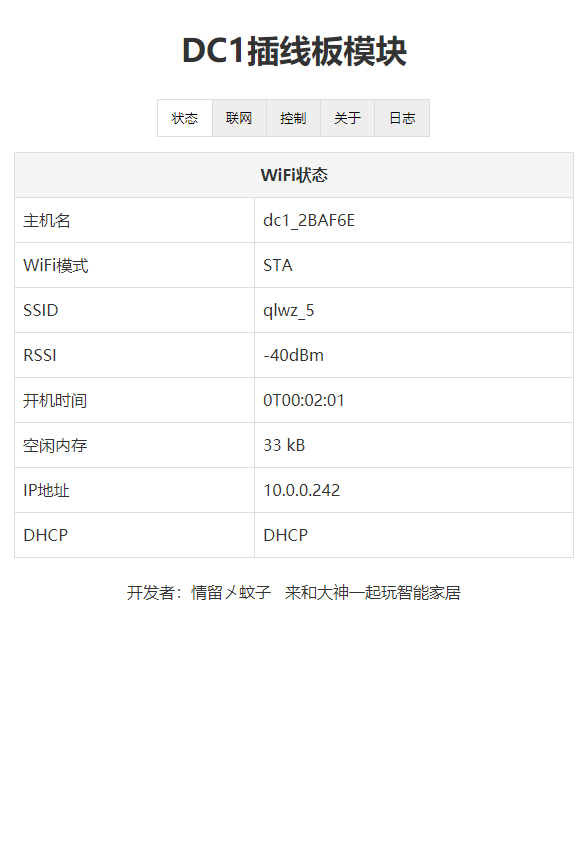
ESP DC1 provides replacement firmware for the Phicomm DC1 power strip after its original app service became unavailable.
Reviewed qlwz/esp_dc1@eefd75a
Firmware · Case study:
fdsboot is a 6502 disassembly of the Famicom Disk System boot ROM, split into disk I/O, PPU, joypad, timer, sound, interrupt and random-number routines with include files for the console and FDS registers.
Reviewed segaloco/fdsboot@6170758
Firmware · Case study:
gyx-decomp is a decompilation of the Casio ES PLUS GYX scientific calculator firmware, which runs on ROHM nX-U8/100 microcontrollers.
Reviewed codeberg.org/gwetm/gyx-decomp/src/commit/c8a8e72fa…
Firmware · Case study:
vmiv emulates the View-Master Interactive Video system by decoding a captured tape video with FFmpeg, extracting the UART-style data bytes and auxiliary audio carried in the scanlines, and feeding them to an 8051 core that runs the VMI8802 ROM alongside a TMS9128 video chip model rendered with SDL2.
Reviewed codeberg.org/Sprite_tm/vmiv/src/commit/f5d69864772…
Firmware · Project:
qemu-rtd2841 adds a Realtek RTD2841/RTK284x TV machine model to QEMU for bare-metal diagnostics and local firmware experiments.
Firmware · Project:
premium5 emulates the Volkswagen Premium 5 car radio at the register and signal level so its original firmware can run without patches.
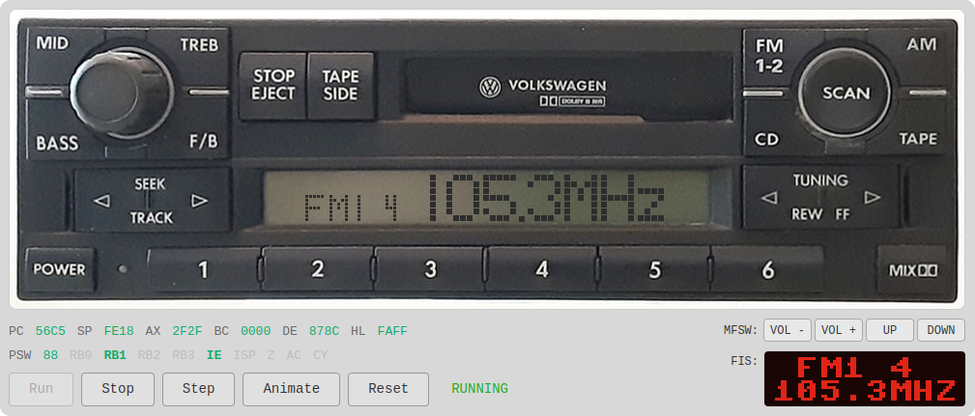
Reviewed mnaberez/premium5@f6713c5
Protocol · Case study:
Documents the Bluetooth Low Energy protocol between the Even app and Even Realities G2 smart glasses, worked out from captured traffic: GATT characteristic UUIDs, an 8-byte transport header with sequence, multi-packet and two-byte service-ID fields, a CRC-16/CCITT over the payload, and protobuf payloads with draft .proto definitions.
Reviewed i-soxi/even-g2-protocol@b227335
App · Tool:
Inspect captured application and device traffic as decoded protocol fields, with filtering and shared GUI/TShark dissection.
Reviewed wireshark/wireshark@e1087b1
Protocol · Tool:
Model communication protocols and infer message layouts from traces, with configured active learning for protocol state machines.
Reviewed netzob/netzob@088fe76
Protocol · Tool:
Script packet dissection, construction, request/reply matching and capture-file analysis in Python.
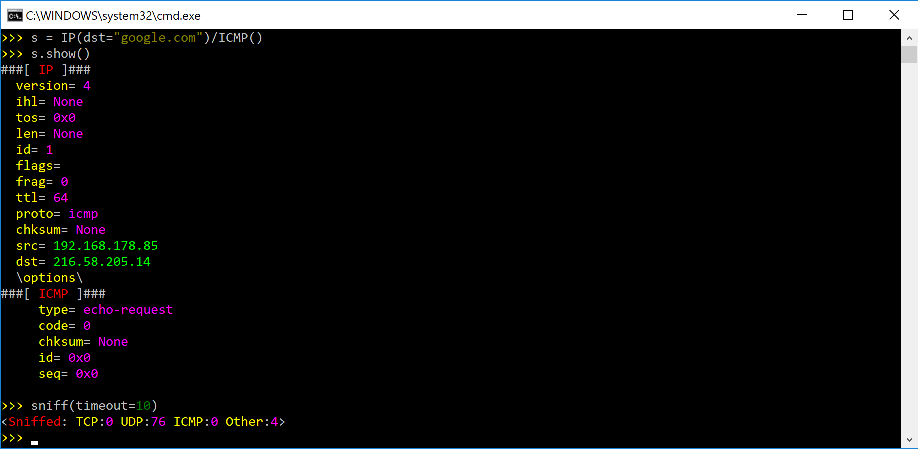
Reviewed secdev/scapy@e2e35c0
Protocol · Tool:
Demodulate and decode signals captured with software-defined radios, with automatic modulation-parameter detection and customizable decodings.
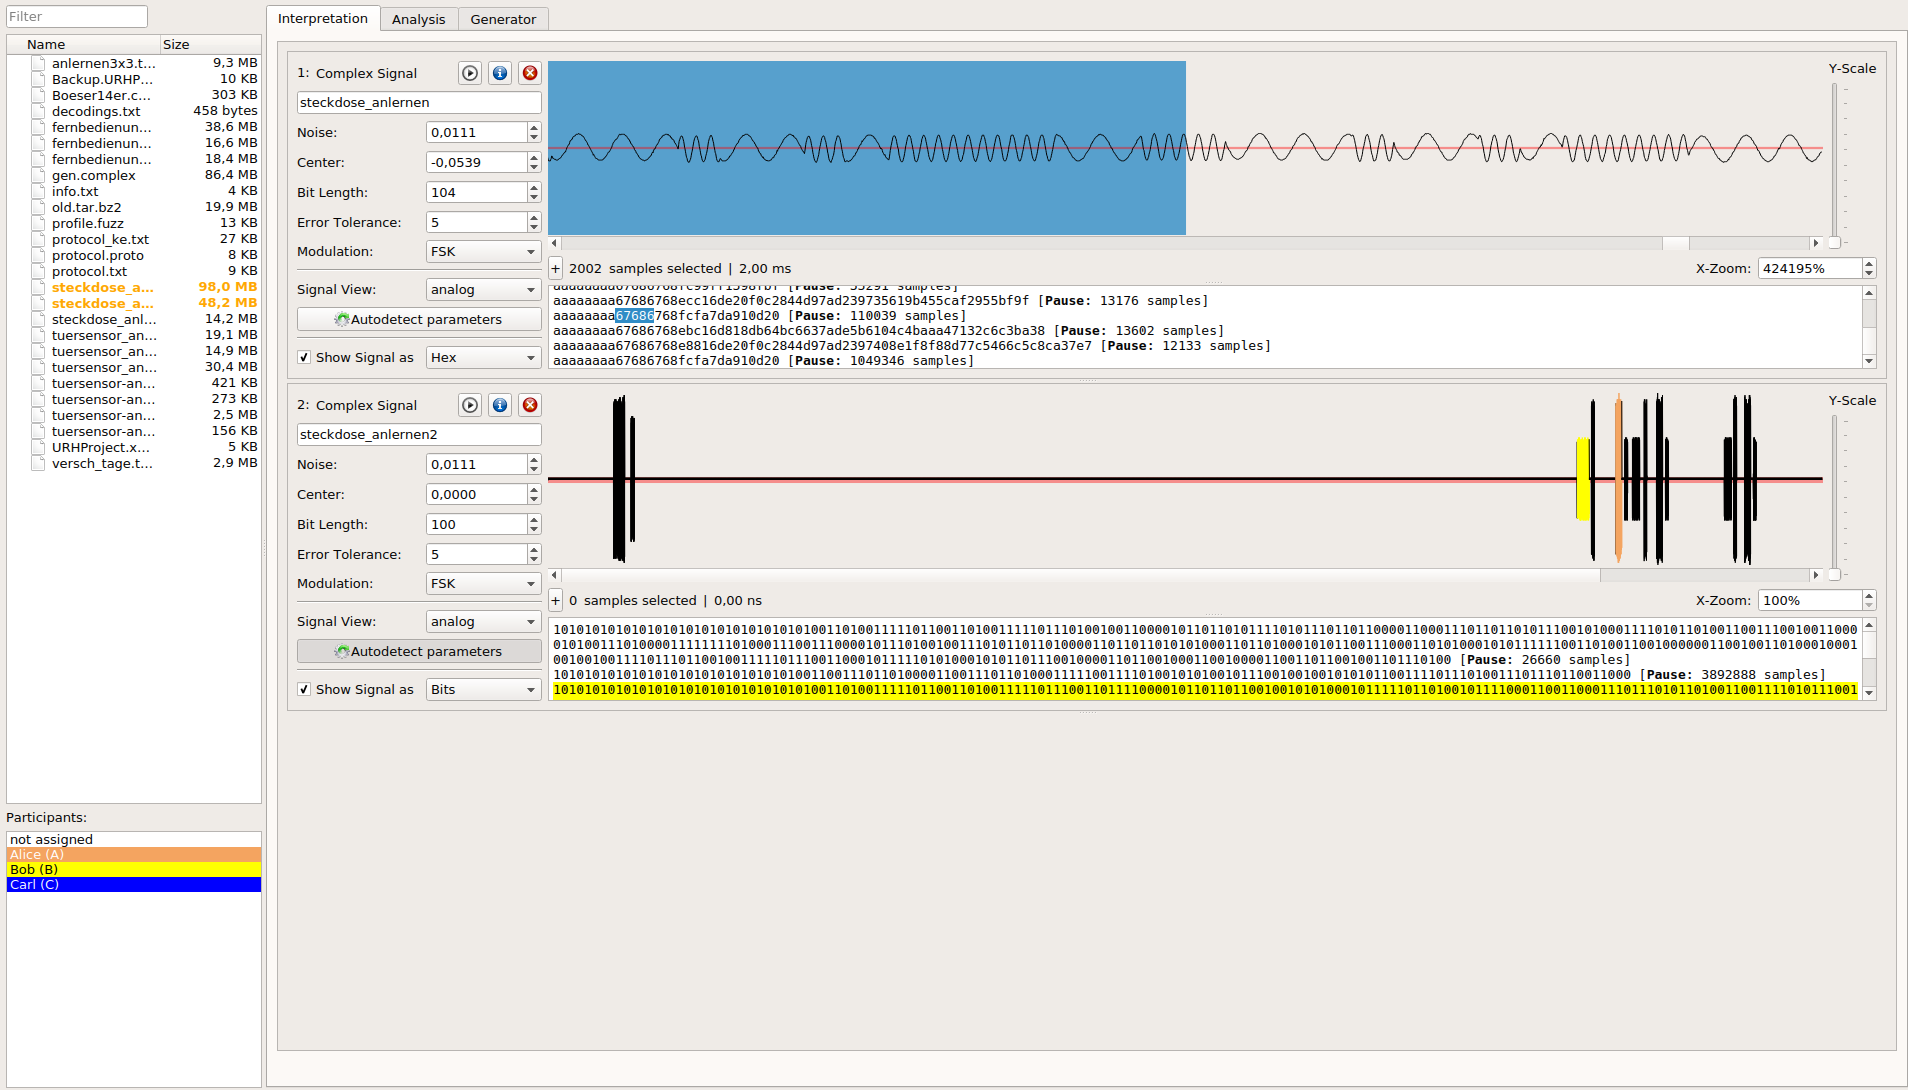
Reviewed jopohl/urh@1403d92
Protocol · Tool:
Capture or load CAN bus traffic and investigate frames with sniffer, graphing, file-comparison and ISO-TP/UDS decoding views; loaded or analyst-edited DBC files map raw bytes to named signals.
Reviewed collin80/SavvyCAN@3166d8c
Protocol · Tool:
General-purpose Python automata-learning library that infers deterministic, non-deterministic, stochastic and pushdown models of black-box systems from active queries or passive traces.
Reviewed DES-Lab/AALpy@335c50a
Protocol · Tool:
Receives and decodes transmissions from ISM-band devices such as weather sensors, remote controls, doorbells and alarm sensors, using RTL-SDR or SoapySDR receivers or recorded I/Q files, and emits decoded fields as JSON, CSV, MQTT and other outputs.
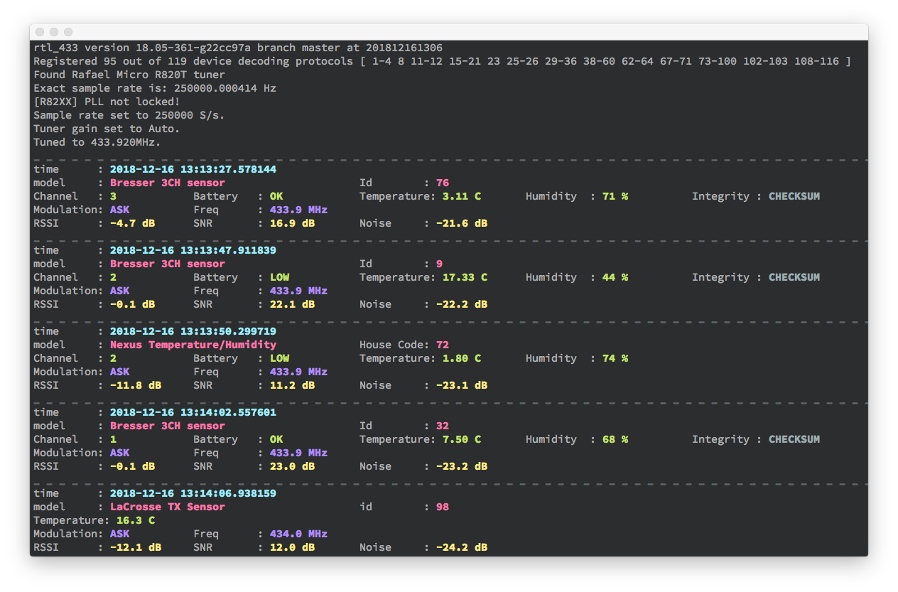
Reviewed merbanan/rtl_433@80f7bcc
Protocol · Tool:
NCC Group's tools for decoding and re-encoding Protocol Buffers messages without the matching .proto definition.
Reviewed nccgroup/blackboxprotobuf@b98861e
Protocol · Tool:
Reverse-engineering notes and a Wireshark dissector for Apple's proprietary Continuity Bluetooth LE advertisements, continuing the authors' PETS 2019 privacy study.
Reviewed furiousMAC/continuity@d9fa98b
Protocol · Tool:
comma.ai's repository of DBC files describing the CAN messages and signals of many car makes, with a Python library that parses and builds CAN messages from those definitions; its porting guide has contributors reverse engineer new messages from recorded drives in the cabana tool.
Reviewed commaai/opendbc@48c7f06
Protocol · Tool:
GNU Radio-based RF framework that carries a signal from survey and detection through IQ capture, inspection, conditioning, feature extraction and classification into a protocol discovery workflow.
Reviewed ainfosec/FISSURE@75abda1
Protocol · Tool:
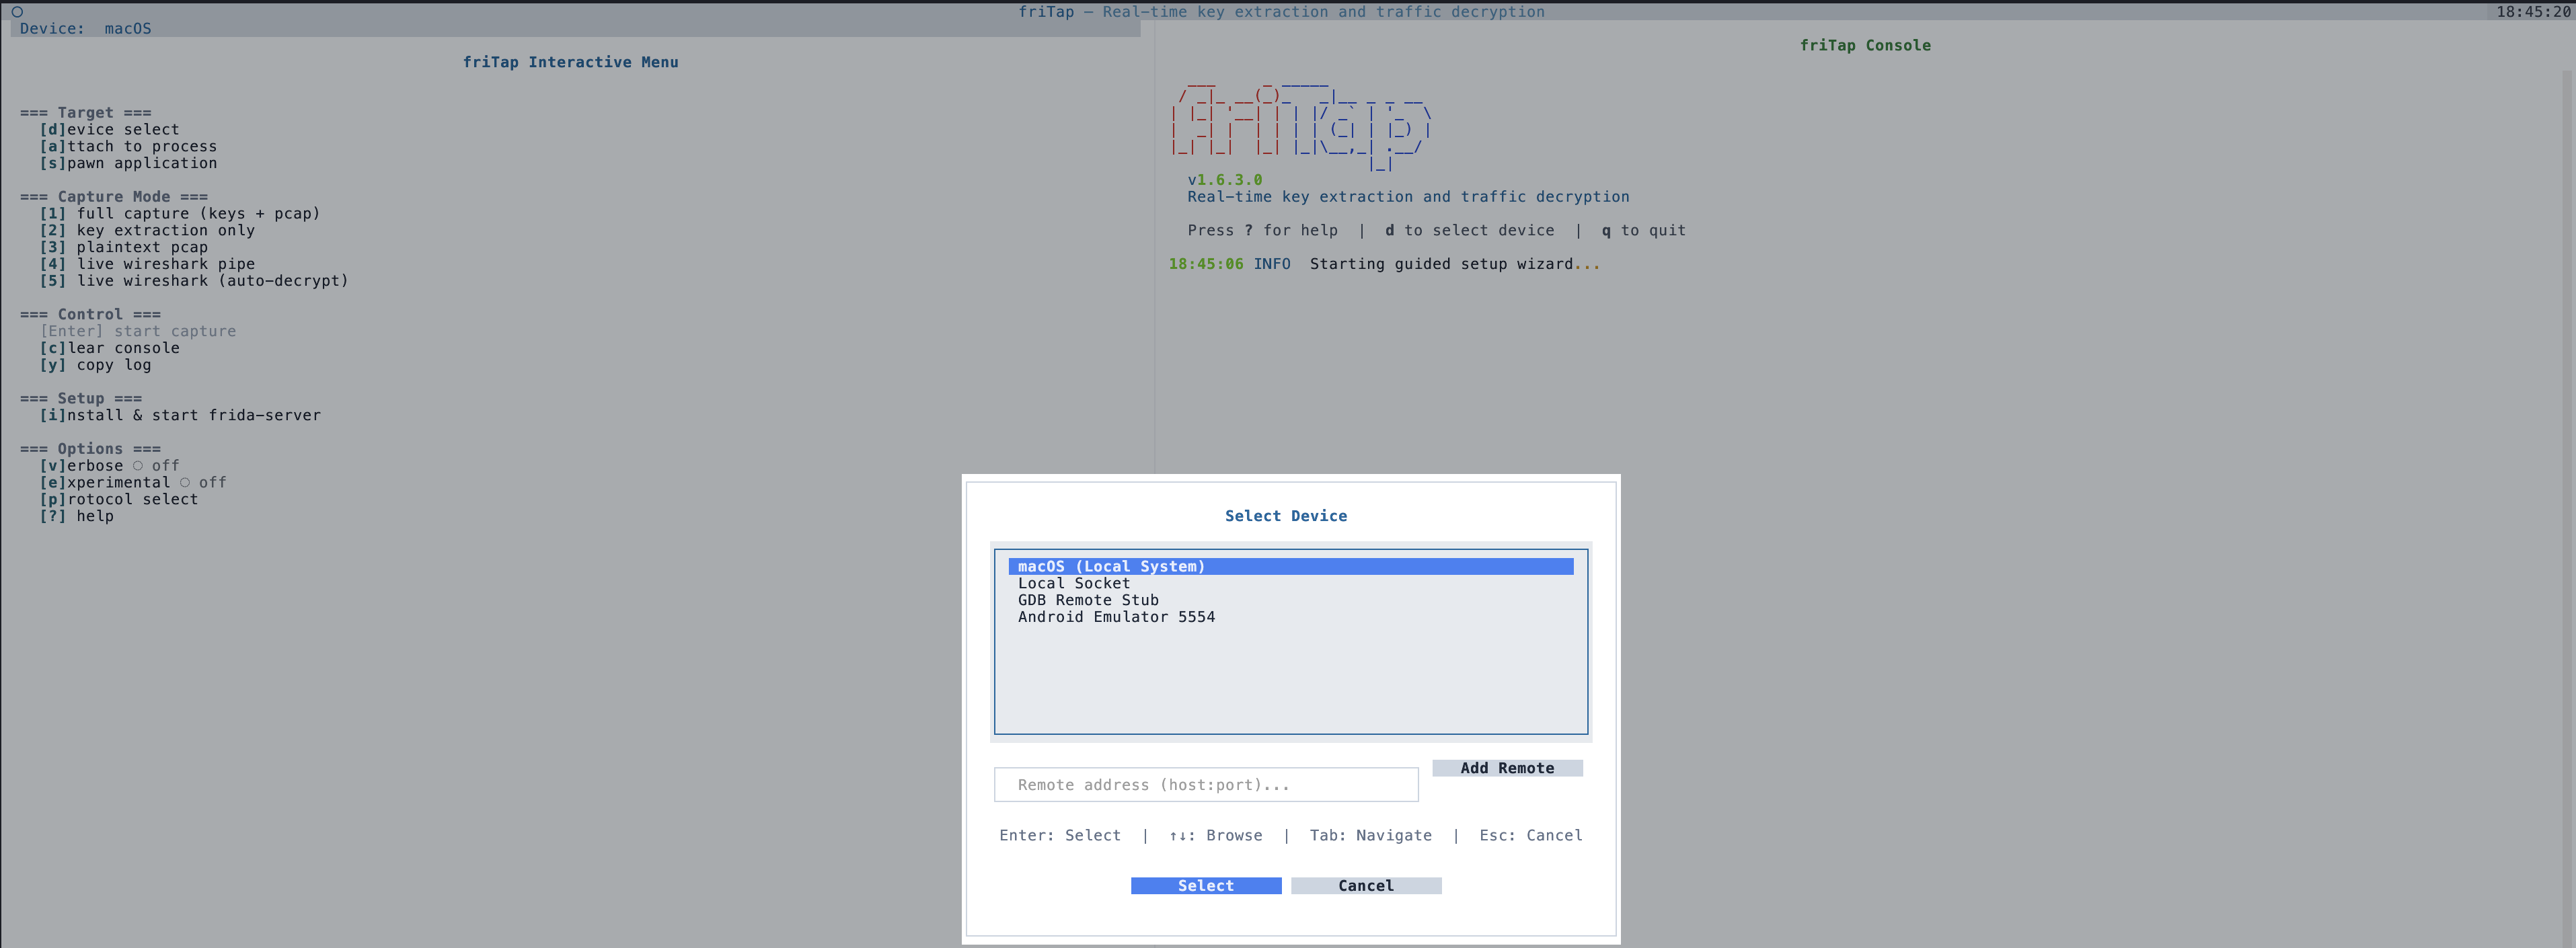
Frida-based tool that hooks TLS libraries such as OpenSSL, BoringSSL, NSS and GnuTLS inside a running process and writes NSS key logs and decrypted payloads as PCAP, so analysts can inspect an application's encrypted traffic in Wireshark.
Reviewed fkie-cad/friTap@d7398a1
Protocol · Tool:
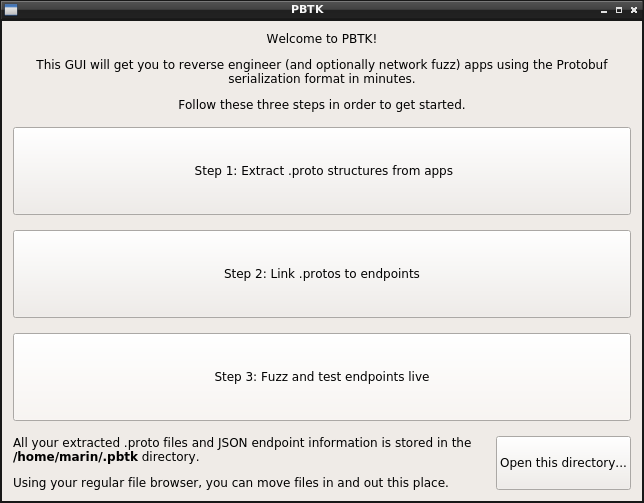
Recover Protobuf message definitions from compiled programs as readable .proto files.
Reviewed marin-m/pbtk@7c5fa2c
Protocol · Tool:
.NET library that implements the client side of Valve’s Steam network protocol: connection-manager sessions, authentication, friends, unified service and Game Coordinator messages, Web API calls and CDN depot downloads.
Reviewed SteamRE/SteamKit@49387ae
Protocol · Tool:
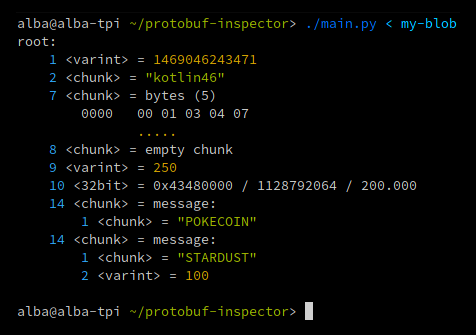
Parses Protocol Buffers blobs (proto2 or proto3) without their .proto definition and prints a colored view of the fields in wire order, trying each length-delimited chunk as a nested message, then a packed array, a string and finally a hexdump.
Protocol · Tool:
C library and command-line tools that speak iOS devices' native service protocols without Apple's proprietary libraries or a jailbreak.
Protocol · Tool:
NCC Group's sniffer for Bluetooth 5 and 4.x Low Energy, made of firmware for TI CC1352/CC26x2 radio boards and Python host tools.
Reviewed nccgroup/Sniffle@3a53f5a
Protocol · Tool:
Great Scott Gadgets' USB 2.0 protocol analysis application for live capture with the Cynthion analyzer or for exploring previously captured traffic, working from physical-layer packet data at High, Full and Low Speed.
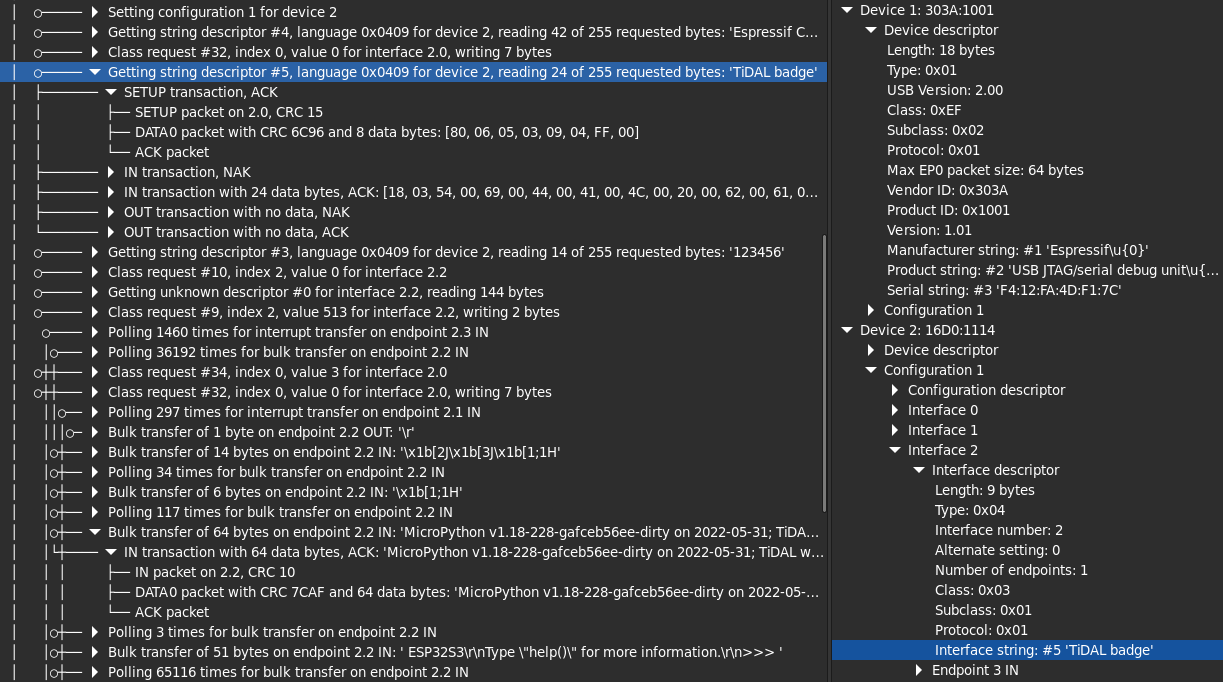
Reviewed greatscottgadgets/packetry@5a7f98b
Protocol · Tool:
Python automotive security exploration tool, begun in the HEAVENS research project, that the README describes as a zero-knowledge tool to drop onto a CAN network and collect information about the services present.
Reviewed CaringCaribou/caringcaribou@092eff3
Protocol · Tool:
Go command-line utility that recovers Protocol Buffers schemas from a compiled binary or any other file: it scans the raw bytes for serialized FileDescriptorProto records embedded by generated code, locating them through their .proto file names, and writes each one back out as a .proto source file under its original descriptor path.
Reviewed arkadiyt/protodump@d398fad
Protocol · Tool:
A Flipper Zero app and earlier Arduino sketches for reverse engineering CAN bus traffic, chiefly in vehicles.
Protocol · Tool:
Research Python and R scripts that automate reverse engineering of Controller Area Network (CAN) payloads recorded from passenger vehicles, implementing the pipeline from Brent Stone's AFIT dissertation.
App · Tool:
Frida-based interceptor for the traffic of proxy-unaware applications.
Reviewed Warxim/deluder@068bb06
Protocol · Tool:
Raspberry Pi Pico firmware and hardware designs for a low-cost CAN bus interface aimed at exploring and reverse engineering vehicle networks.

Reviewed Alia5/PiCCANTE@62ede82
Protocol · Tool:
Arduino library for ESP8266/ESP8285 and ESP32 boards that receives and transmits packets on the VAN (Vehicle Area Network) comfort bus that PSA fitted to Peugeot and Citroën models until about 2009.
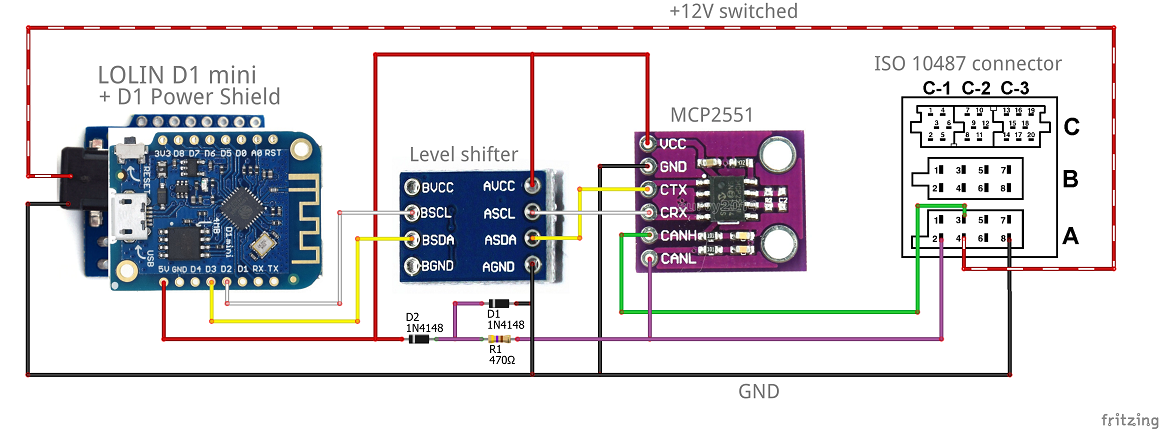
Reviewed 0xCAFEDECAF/VanBus@0c22517
Protocol · Tool:
Three macOS helpers from SEEMOO Lab that the Open Wireless Link project used to study Apple wireless services such as AirDrop, Wi-Fi Password Sharing, Handoff and Offline Finding from the host side.
Protocol · Tool:
Qt desktop CAN and CAN FD analyzer for decoding signals and reverse engineering unknown messages, split out of openpilot's cabana by Dean Lee, a frequent contributor to it, and now maintained on its own.
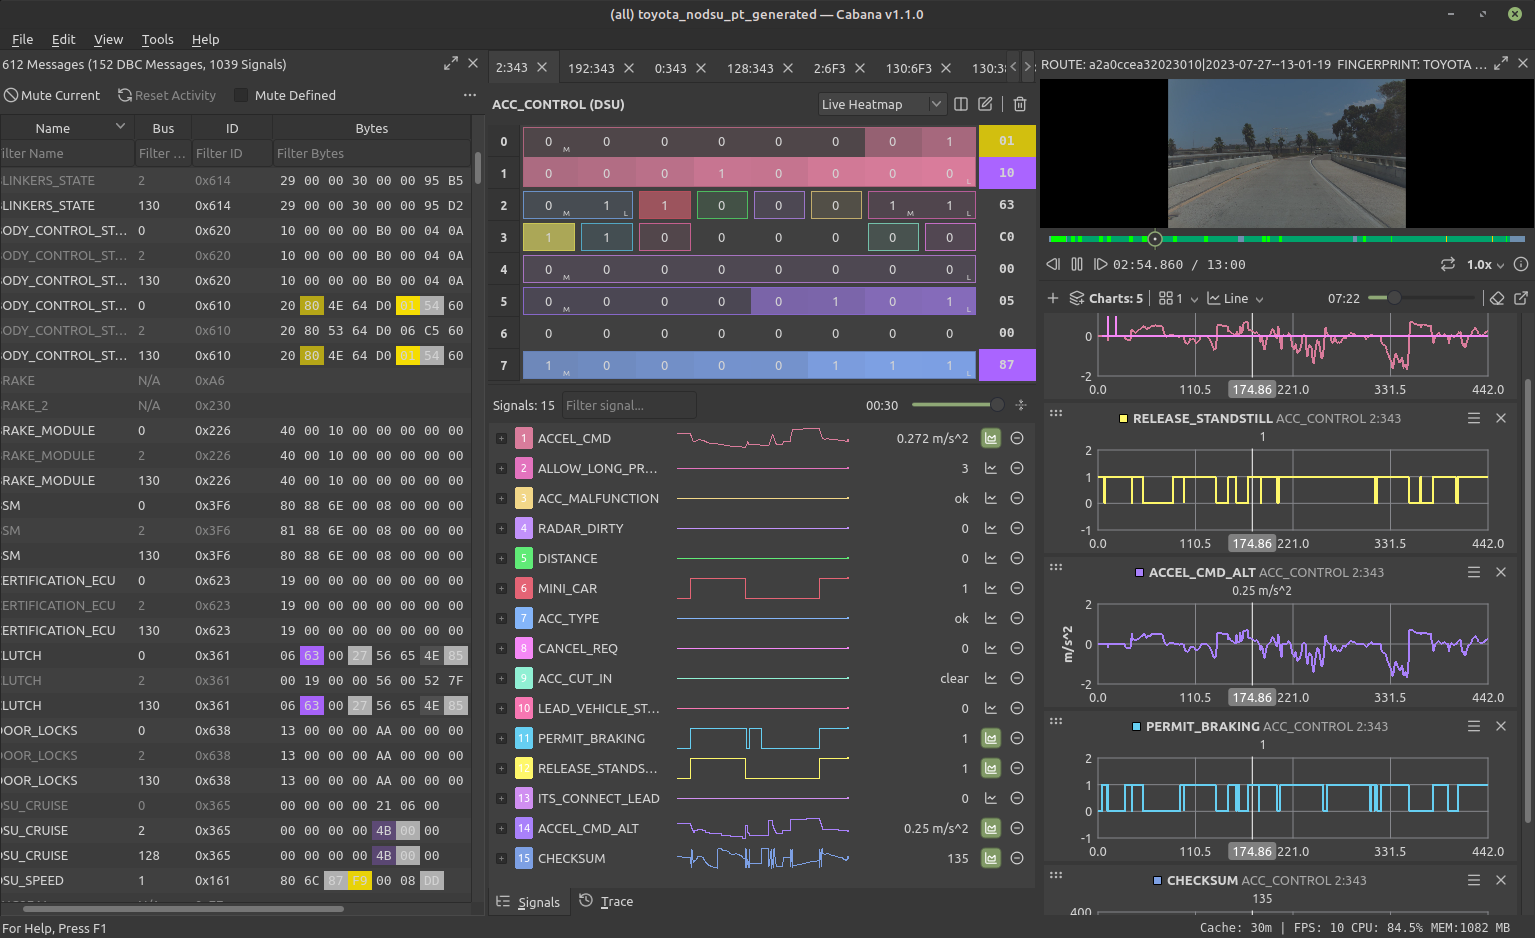
Reviewed deanlee/openpilot-cabana@0a4b189
Protocol · Tool:
eBPF-based Linux and Android tool that attaches uprobes to TLS libraries such as OpenSSL, BoringSSL, GnuTLS and NSS, and to Go's TLS stack, recording the plaintext a process sends and receives without a proxy or an installed CA certificate, so analysts can inspect an application's encrypted traffic on a host they control.
Reviewed gojue/ecapture@e834aa0
Protocol · Tool:
Tomasz Moń's open-source USB packet capture for Windows.
Reviewed desowin/usbpcap@477b6ed
Protocol · Tool:
Python 3 library and command-line tool for CAN bus databases that parses DBC, KCD, SYM, ARXML 3/4 and CDD files and encodes and decodes CAN messages, including simple and extended signal multiplexing and diagnostic DIDs.
Reviewed cantools/cantools@5d37340
Protocol · Tool:
Desktop analyzer for recorded radio signals, primarily captures from software-defined radio receivers, which the README says handles files of 100 GB and more.
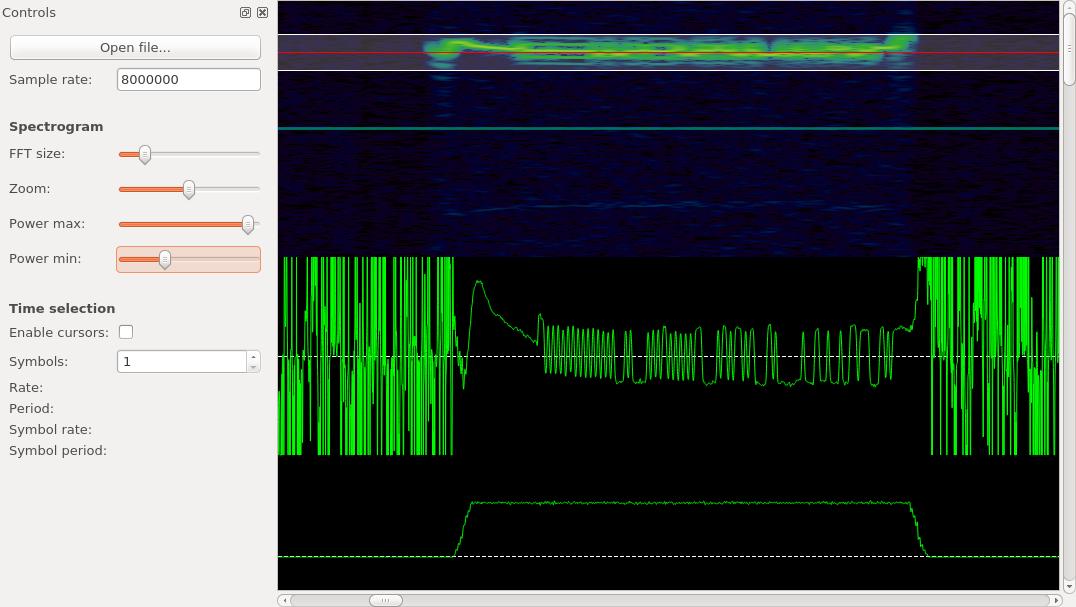
Reviewed miek/inspectrum@82f5779
Protocol · Tool:
Research prototype by Hugo Gascon and colleagues that learns a model of an unknown network protocol from recorded traffic.
Reviewed hgascon/pulsar@3c61178
Protocol · Tool:
PyQt6 desktop workstation and command-line tool for reverse-engineering CAN bus captures offline.
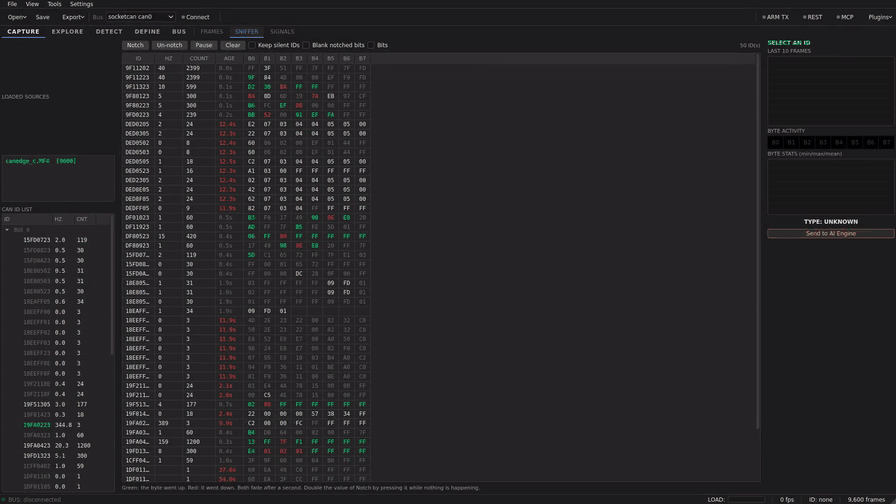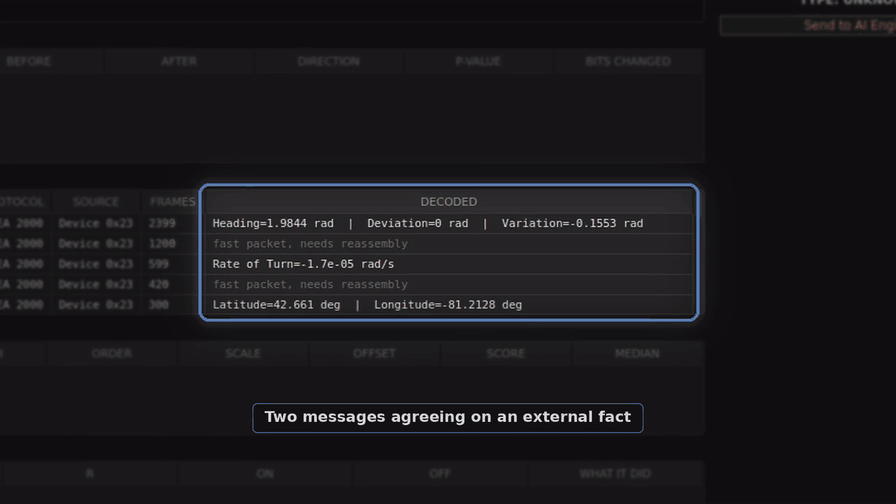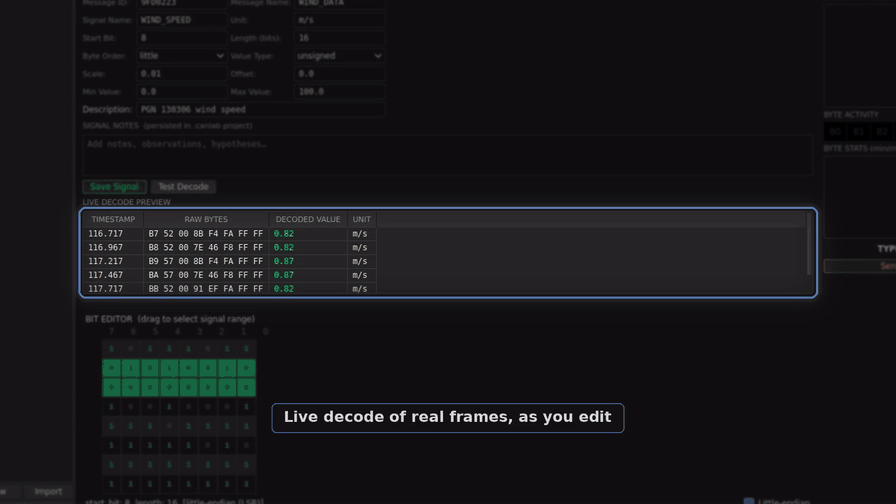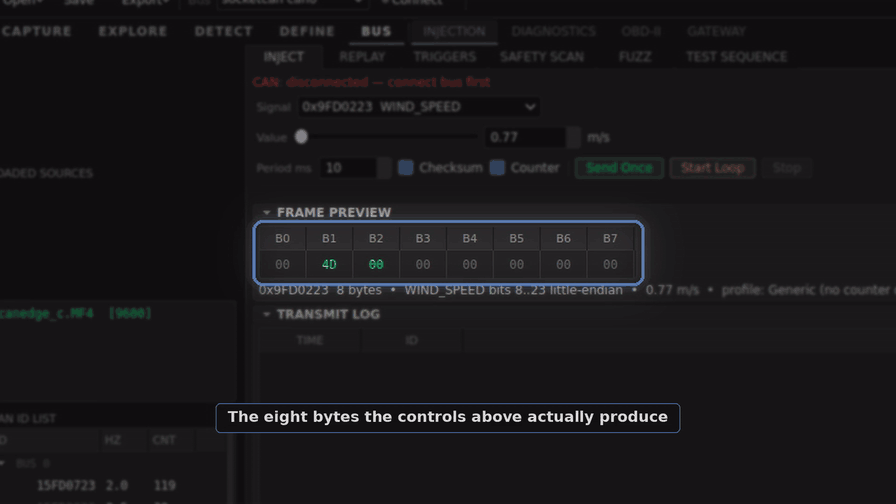
Reviewed Sherin-SEF-AI/CanLab@8aaa6ff
Protocol · Tool:
Python library for implementing USB devices in software, with a hardware peripheral such as Cynthion or GreatFET acting as a remote-controlled USB controller attached to the target host.
Reviewed greatscottgadgets/facedancer@9f12988
Protocol · Tool:
Python framework from IoT-security research at LAAS-CNRS for analysing wireless communications, with lightweight protocol stacks for Bluetooth Low Energy, Bluetooth, Enhanced ShockBurst, Mosart, Zigbee, Wi-Fi and infrared that a command-line interpreter drives through chainable modules.
Reviewed RCayre/mirage@b6cd39e
Protocol · Tool:
Pawit Pornkitprasan's React web application for decoding Protocol Buffers data without the original .proto files, offered as a hosted page or run locally, with all decoding done in the browser.
Reviewed pawitp/protobuf-decoder@7d0b5ed
Protocol · Tool:
GNU Radio out-of-tree module by Pieter Robyns and co-authors for receiving and decoding LoRa physical-layer frames with a software-defined radio, implementing the modulation features described in patents and blog posts.
Reviewed rpp0/gr-lora@90343d4
Protocol · Tool:
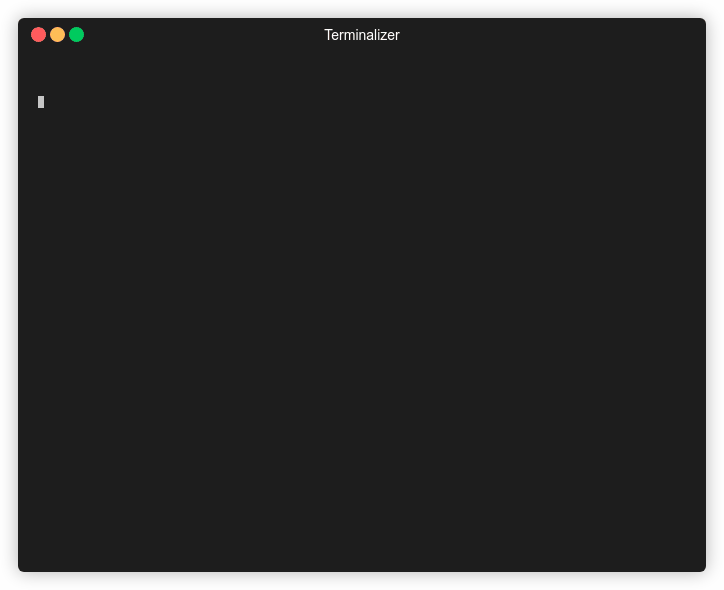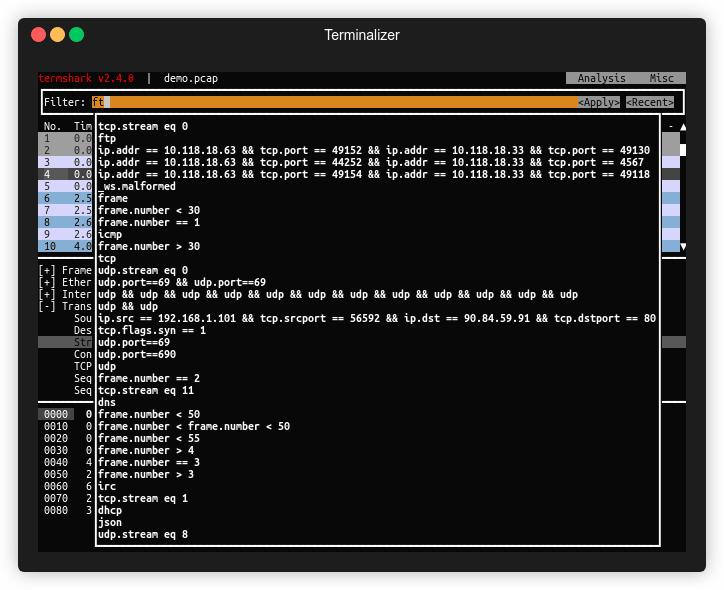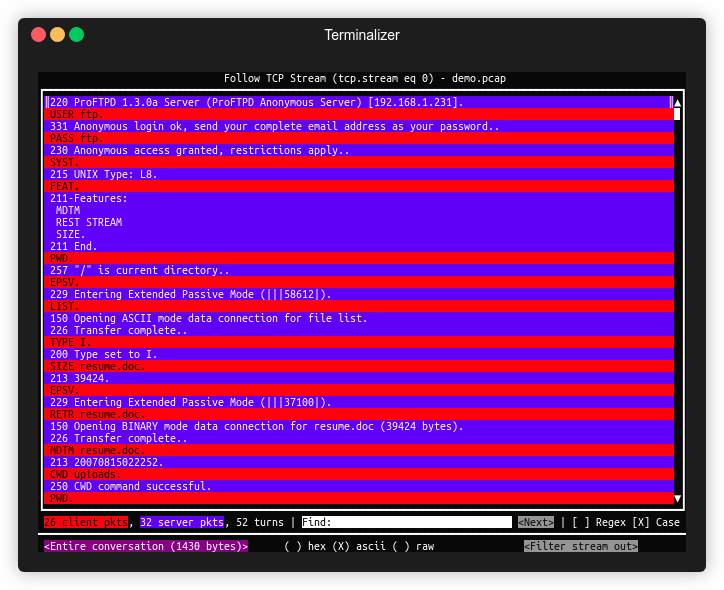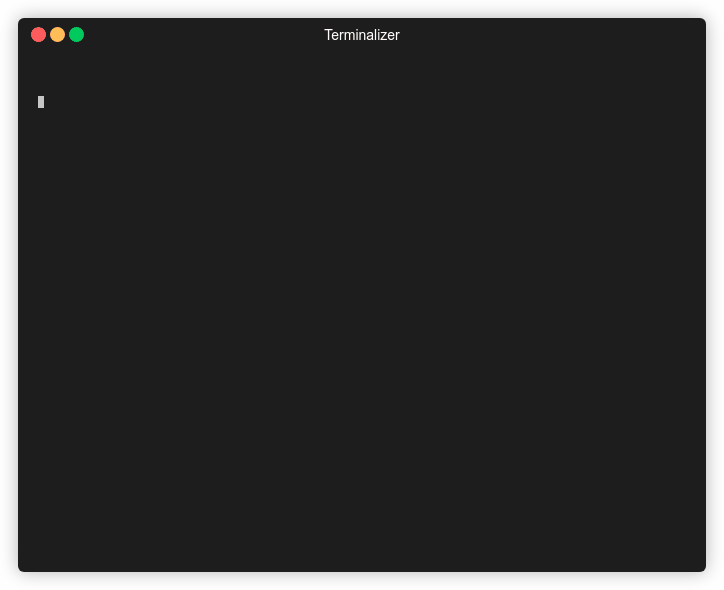
Graham Clark's terminal user interface for tshark, inspired by Wireshark and aimed at inspecting captures on a remote machine, for example over SSH, without copying them back to a desktop.
Reviewed gcla/termshark@e8a1ec6
Protocol · Tool:
Qt graphical digital signal analyzer by Gonzalo José Carracedo Carballal, built on his Suscan and Sigutils libraries; its user manual names reverse engineering of radio signals with unknown parameters as the main use.
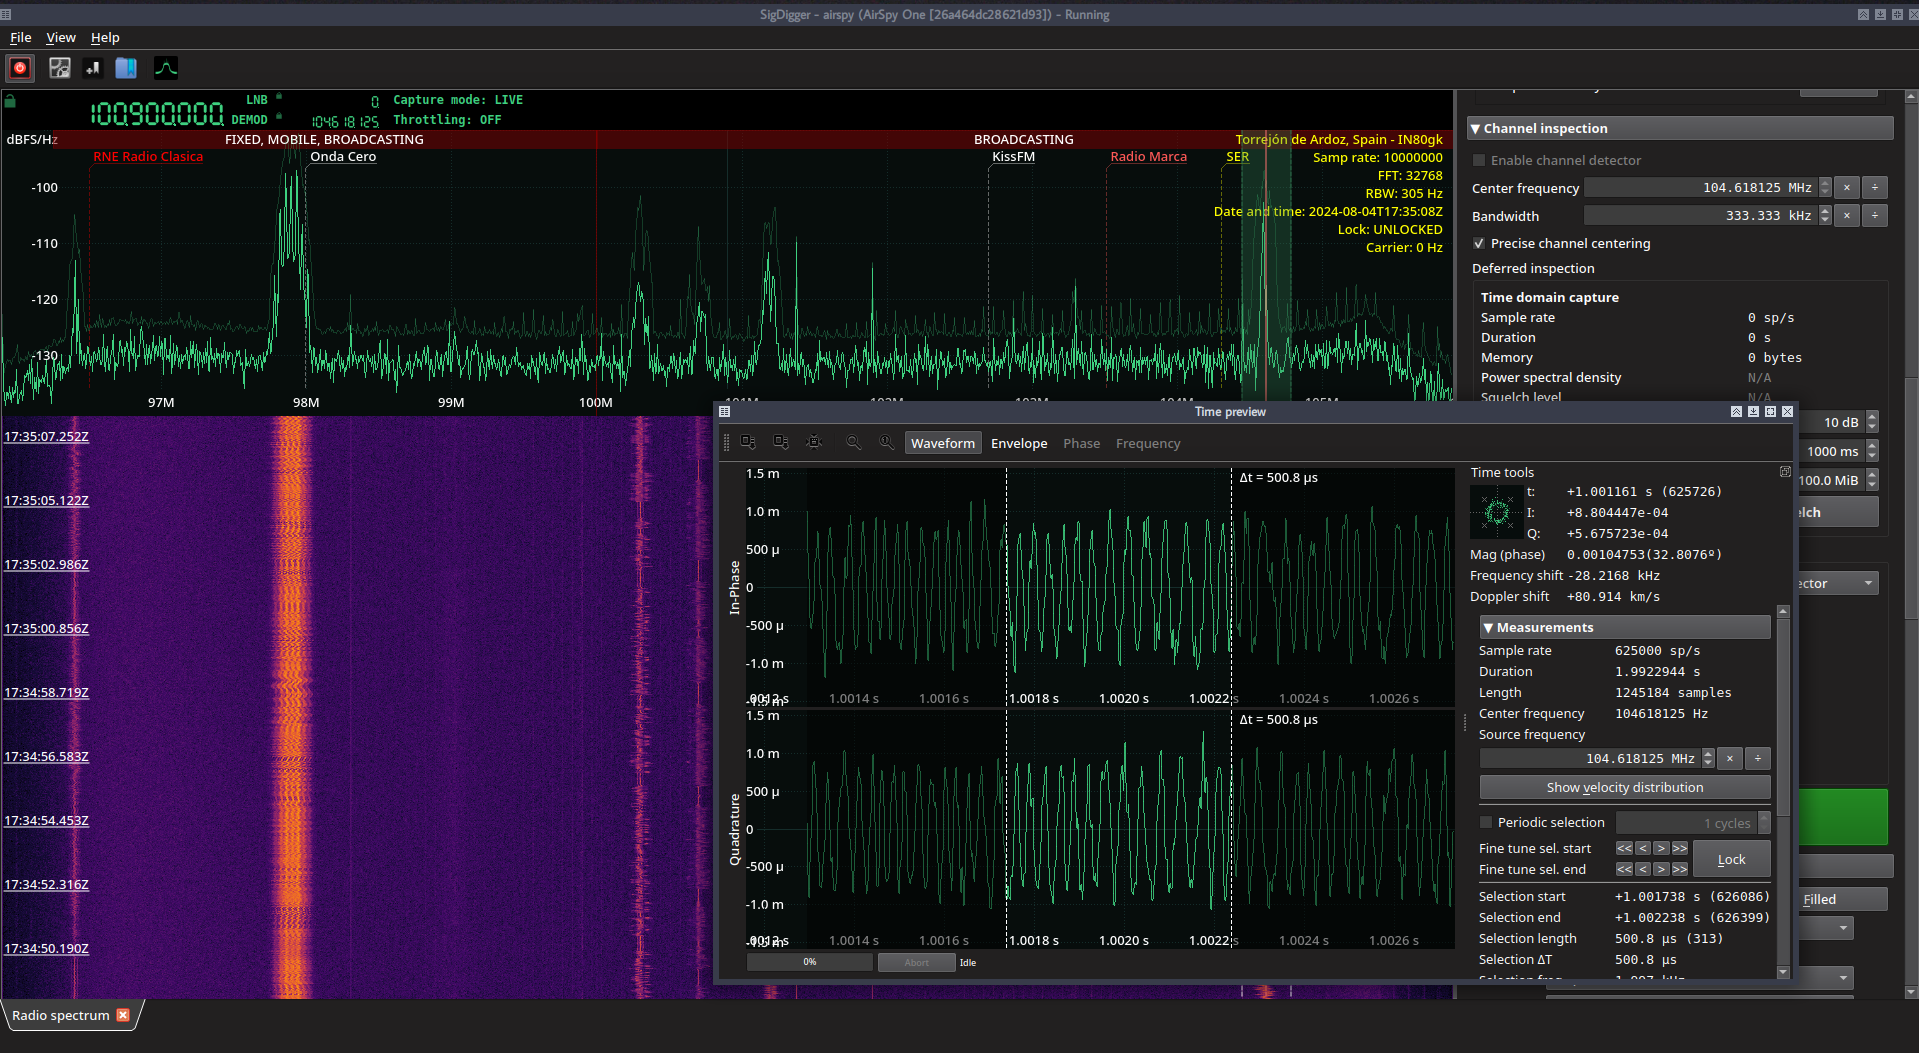
Reviewed BatchDrake/SigDigger@70f688b
Protocol · Tool:
Bradley Kemp's suite of gRPC debugging tools, described as Fiddler or Charles for gRPC.
Reviewed bradleyjkemp/grpc-tools@928b1b9
Protocol · Tool:
Holley EFI Parser decodes Holley DL and DLZ data logs and live ECU CAN messages.
Reviewed HackingLZ/holley-efi-parser@3403b04
Protocol · Tool:
CAN Bus Parser decodes VanMoof SA5 and later bicycle CAN captures from CSV or candump input.
Reviewed Knight1/vanmoof-canbus@9a74287
Protocol · Tool:
Hermes is a Flipper Zero app for identifying unknown UART settings and inspecting a device's serial console.
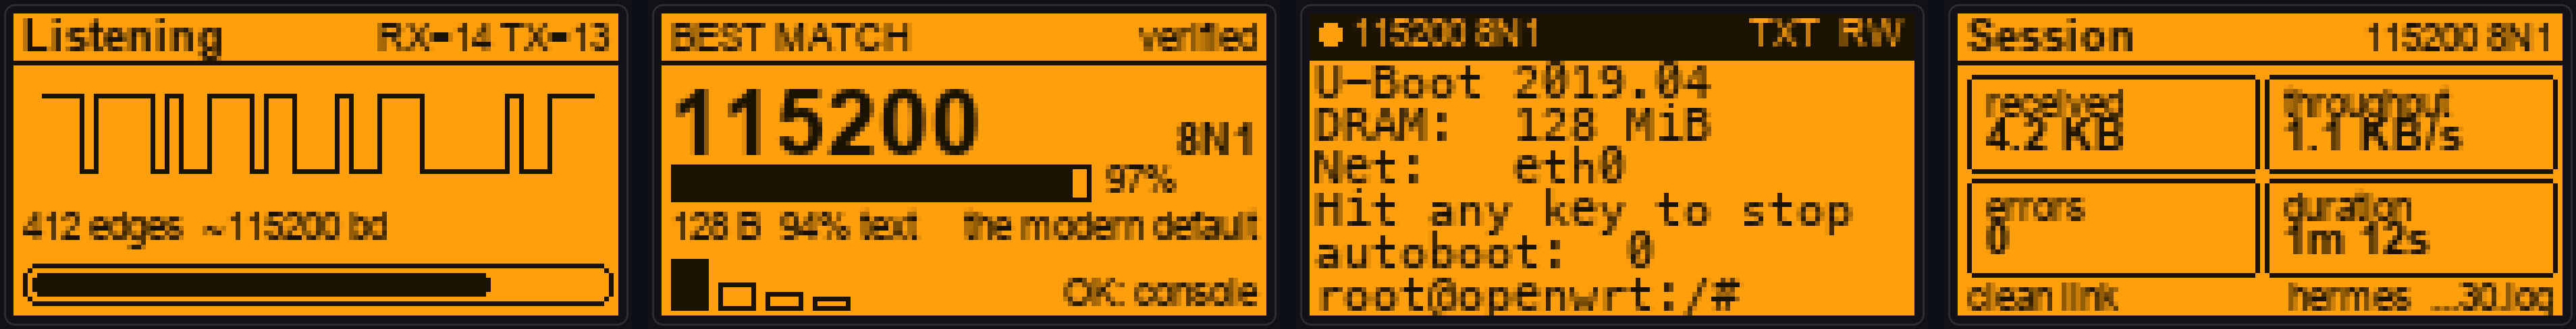
Reviewed at0m-b0mb/Hermes-FlipperZero@9c463e3
Game · Tool:
RoflLens is a Python library and CLI for analysing League of Legends ROFL v2 replay containers and network transport.
Reviewed ss26367098/rofllens@62a475a
Protocol · Tool:
LogicAnalyzer is a hardware and software tool for capturing digital signals and decoding communication protocols.
Reviewed gusmanb/logicanalyzer@4e88df7
Protocol · Tool:
BtleJuice is a framework for intercepting Bluetooth Low Energy GATT operations between devices.
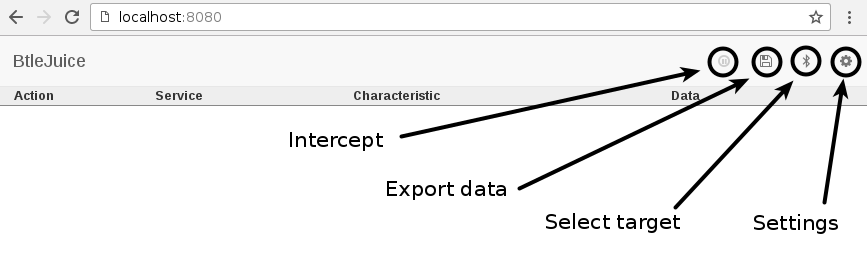
Reviewed DigitalSecurity/btlejuice@981b2e3
Protocol · Tool:
Impacket is a Python library for constructing and parsing network packets and working with protocol implementations.
Reviewed fortra/impacket@0b3ef2b
Protocol · Tool:
Capture Bluetooth Low Energy connections with compatible nRF51822-based boards and export packets for Wireshark analysis.
Reviewed virtualabs/btlejack@c487859
Protocol · Tool:
Record, filter, compare and replay SocketCAN traffic with tools for raw CAN, ISO-TP and J1939 analysis.
Reviewed linux-can/can-utils@834ceef
Protocol · Tool:
Run sigrok’s Python protocol decoders through a C library to interpret captured digital signals.
Protocol · Tool:
Capture Bluetooth radio traffic using the Ubertooth hardware platform and its host analysis tools.
Reviewed greatscottgadgets/ubertooth@c9dfdbd
Protocol · Tool:
Explore a USB host’s supported device classes and vendor-specific behavior through programmable device emulation.
Reviewed nccgroup/umap2@a428667
Protocol · Tool:
DSDcc decodes digital radio traffic in DMR, D-Star, dPMR and Yaesu System Fusion formats through a C++ library and command-line program.
Reviewed f4exb/dsdcc@f27b32d
Protocol · Tool:
winbox implements the Winbox protocol's M2 packet and message structures in Python.
Reviewed jabb3rd/winbox@fe8e620
Protocol · Tool:
wow_messages maintains World of Warcraft authentication and world-server message definitions in the wowm language.
Reviewed gtker/wow_messages@e1bde21
Protocol · Tool:
Vifterpreter is a Rust crate for inspecting PlayStation 2 DMA packet structures and VIF commands.
Reviewed 0x5abe/vifterpreter@68f33f3
Protocol · Tool:
meteor_decoder processes captured Meteor-M LRPT weather-satellite signals into BMP images or decoded dumps.
Reviewed artlav/meteor_decoder@8021339
Protocol · Tool:
RF-Bridge-OB38S003 provides replacement firmware for 433 MHz radio-to-Wi-Fi bridges that decodes radio packets and sniffs unknown codes.
Reviewed mightymos/RF-Bridge-OB38S003@bfddbd1
Protocol · Tool:
RFLink ESP is ESP32 and ESP8266 firmware that receives and decodes 433 MHz OOK device messages.
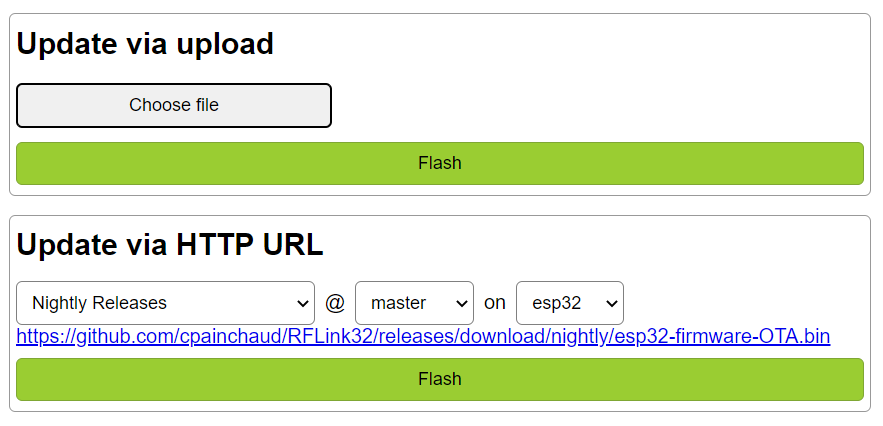
Reviewed cpainchaud/RFLink32@dbf78f8
Protocol · Tool:
bedrock-protocol parses and serializes Minecraft Bedrock Edition packets as JavaScript objects and provides client, server and proxy connections.
Protocol · Tool:
Twonkie is a USB-PD sniffer, injector and sink built around a four-layer board derived from the open-source Twinkie design.
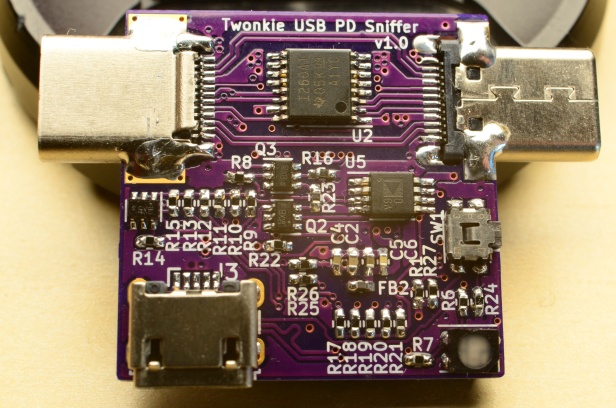
Reviewed dojoe/Twonkie@64a9e85
Protocol · Tool:
BresserWeatherSensorReceiver is an Arduino library for receiving and decoding 868 MHz transmissions from Bresser weather sensors.
Protocol · Tool:
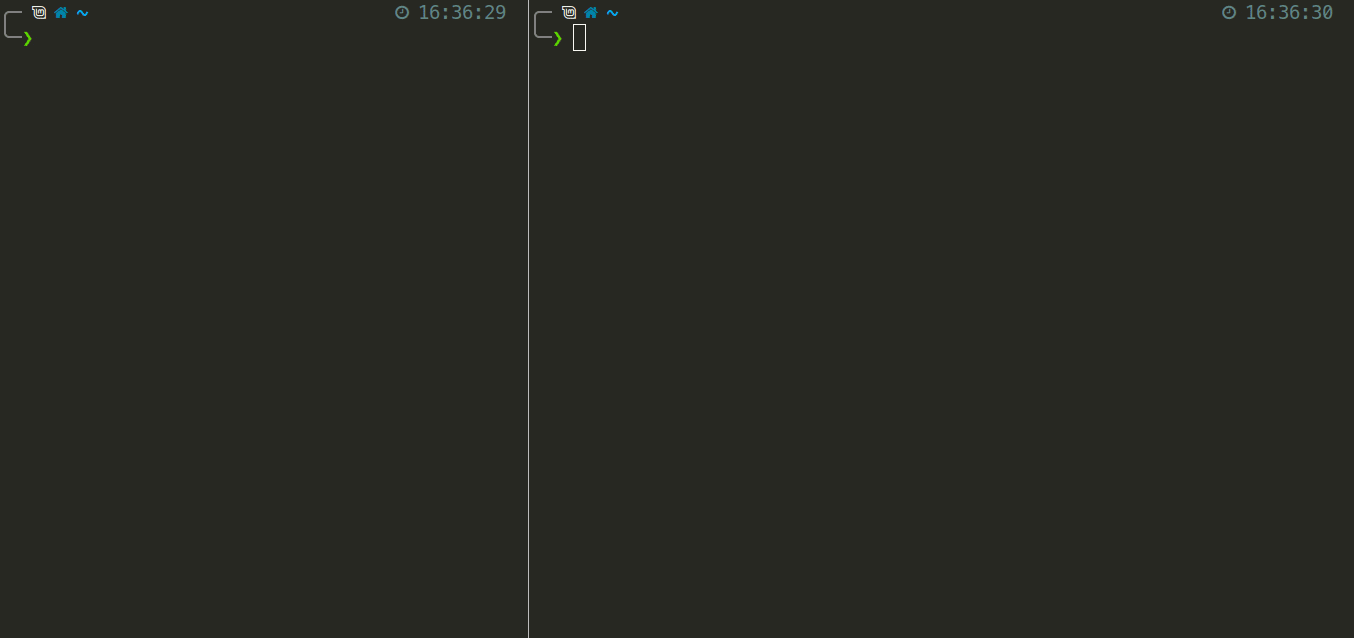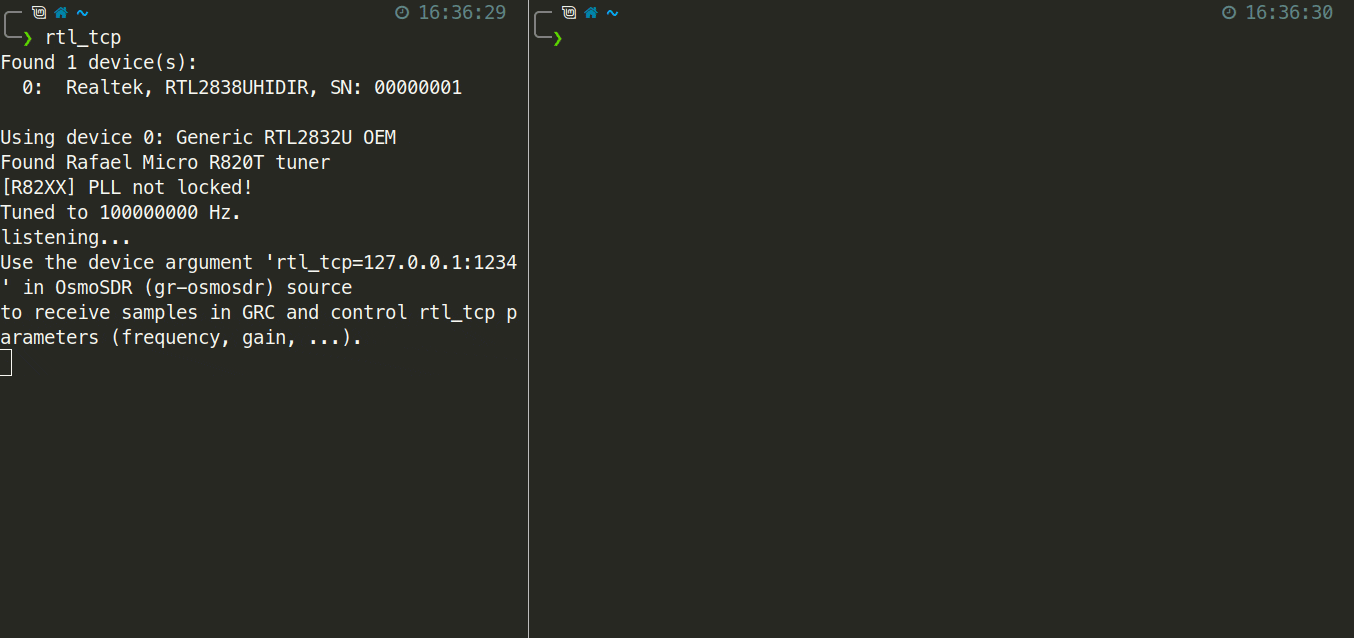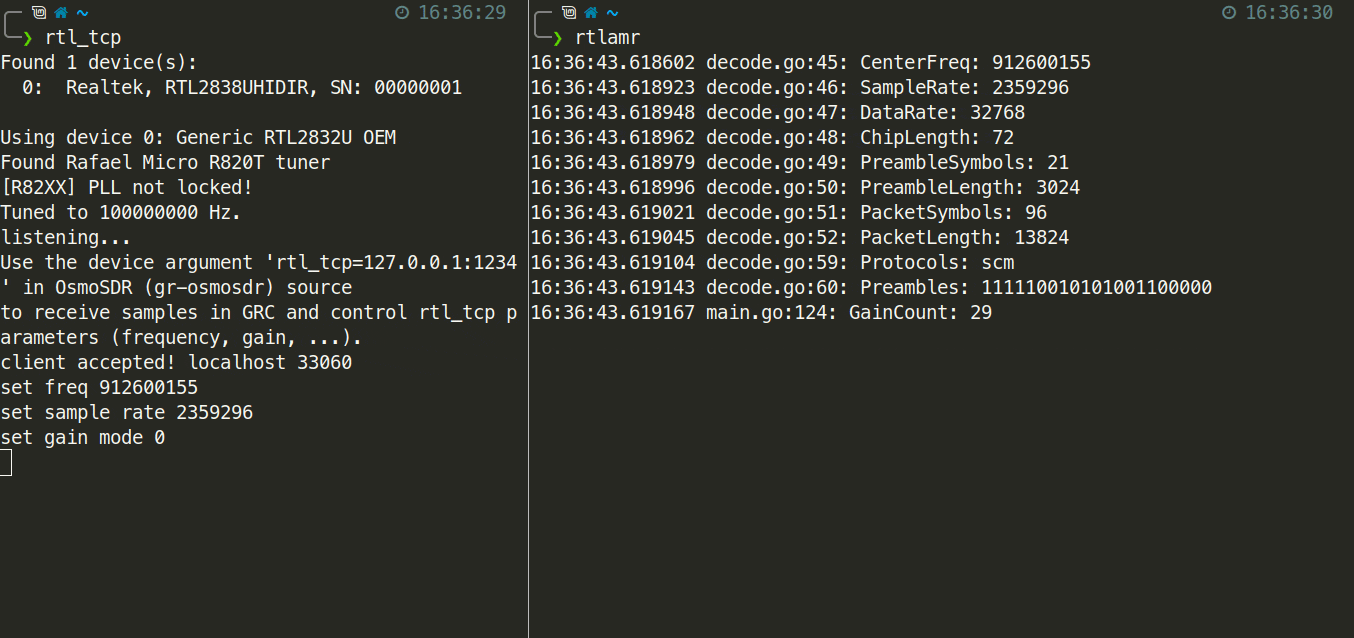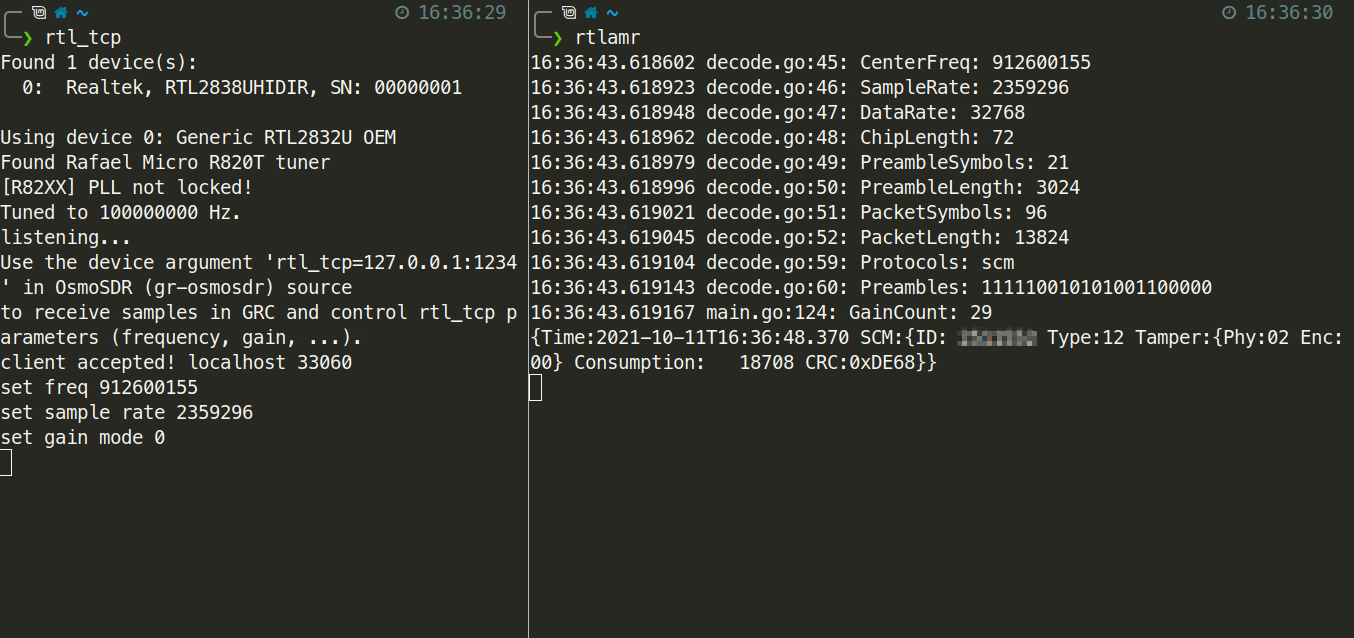
rtlamr receives and decodes Itron ERT-compatible smart-meter transmissions in the 900 MHz ISM band through rtl-sdr and rtl_tcp.
Reviewed bemasher/rtlamr@92cca2f