Binary · Tool:
PbdViewerC1
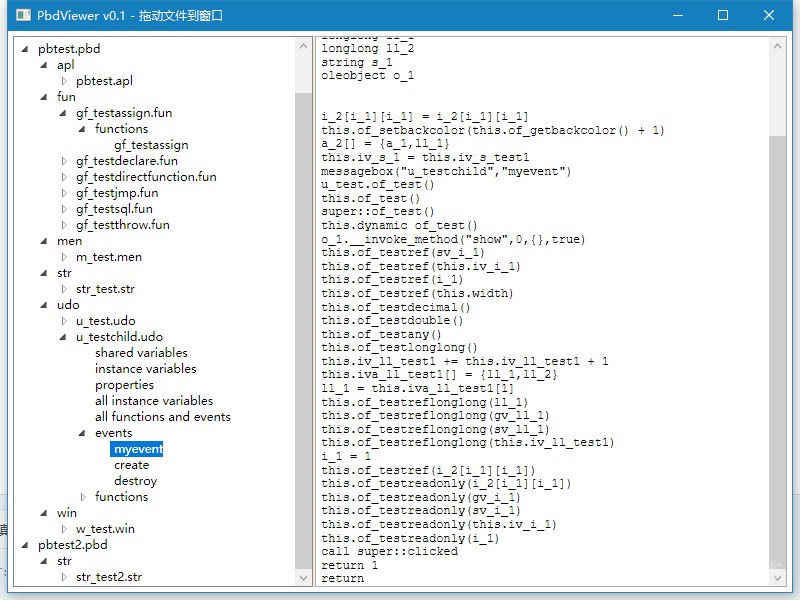
PbdViewer is a PowerBuilder decompiler. The README points to a Kanxue thread, bbs.kanxue.com/thread-247372.htm.
- Binary
Reviewed Hucxy/PbdViewer@b46fd3e
Binary · Tool:
PbdViewer is a PowerBuilder decompiler. The README points to a Kanxue thread, bbs.kanxue.com/thread-247372.htm.
Reviewed Hucxy/PbdViewer@b46fd3e
Binary · Tool:
Copy as YARA is a Binary Ninja plugin that copies selected disassembly as text usable in a YARA rule.
Reviewed ald3ns/copy-as-yara@539b28a
Binary · Tool:
pytest-idapro is a pytest plugin for IDA and IDAPython.
Reviewed nirizr/pytest-idapro@12f9aab
Game · Tool:
360tools is a toolkit and playbook for statically recompiling Xbox 360 games to native x86-64 executables with the ReXGlue SDK.
Reviewed sp00nznet/360tools@1b53928
Game · Tool:
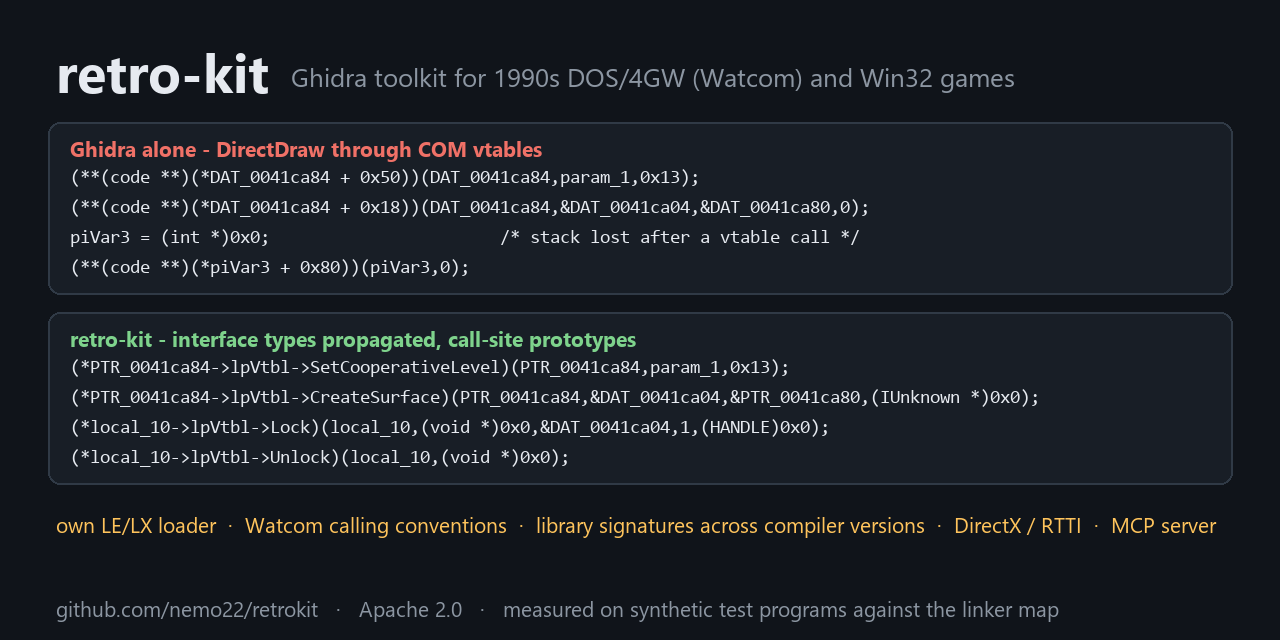
retrokit decompiles 32-bit games from about 1993 to 2010 with headless Ghidra.
Reviewed nautilusbits/retrokit@7625c6b
Game · Tool:
Source 2 Decompiler, s2dc, decompiles Source 2 resource files.
Reviewed Dingf/Source-2-Decompiler@0526b7a
Binary · Tool:
parascope scans source code and binaries with weggli rulesets.
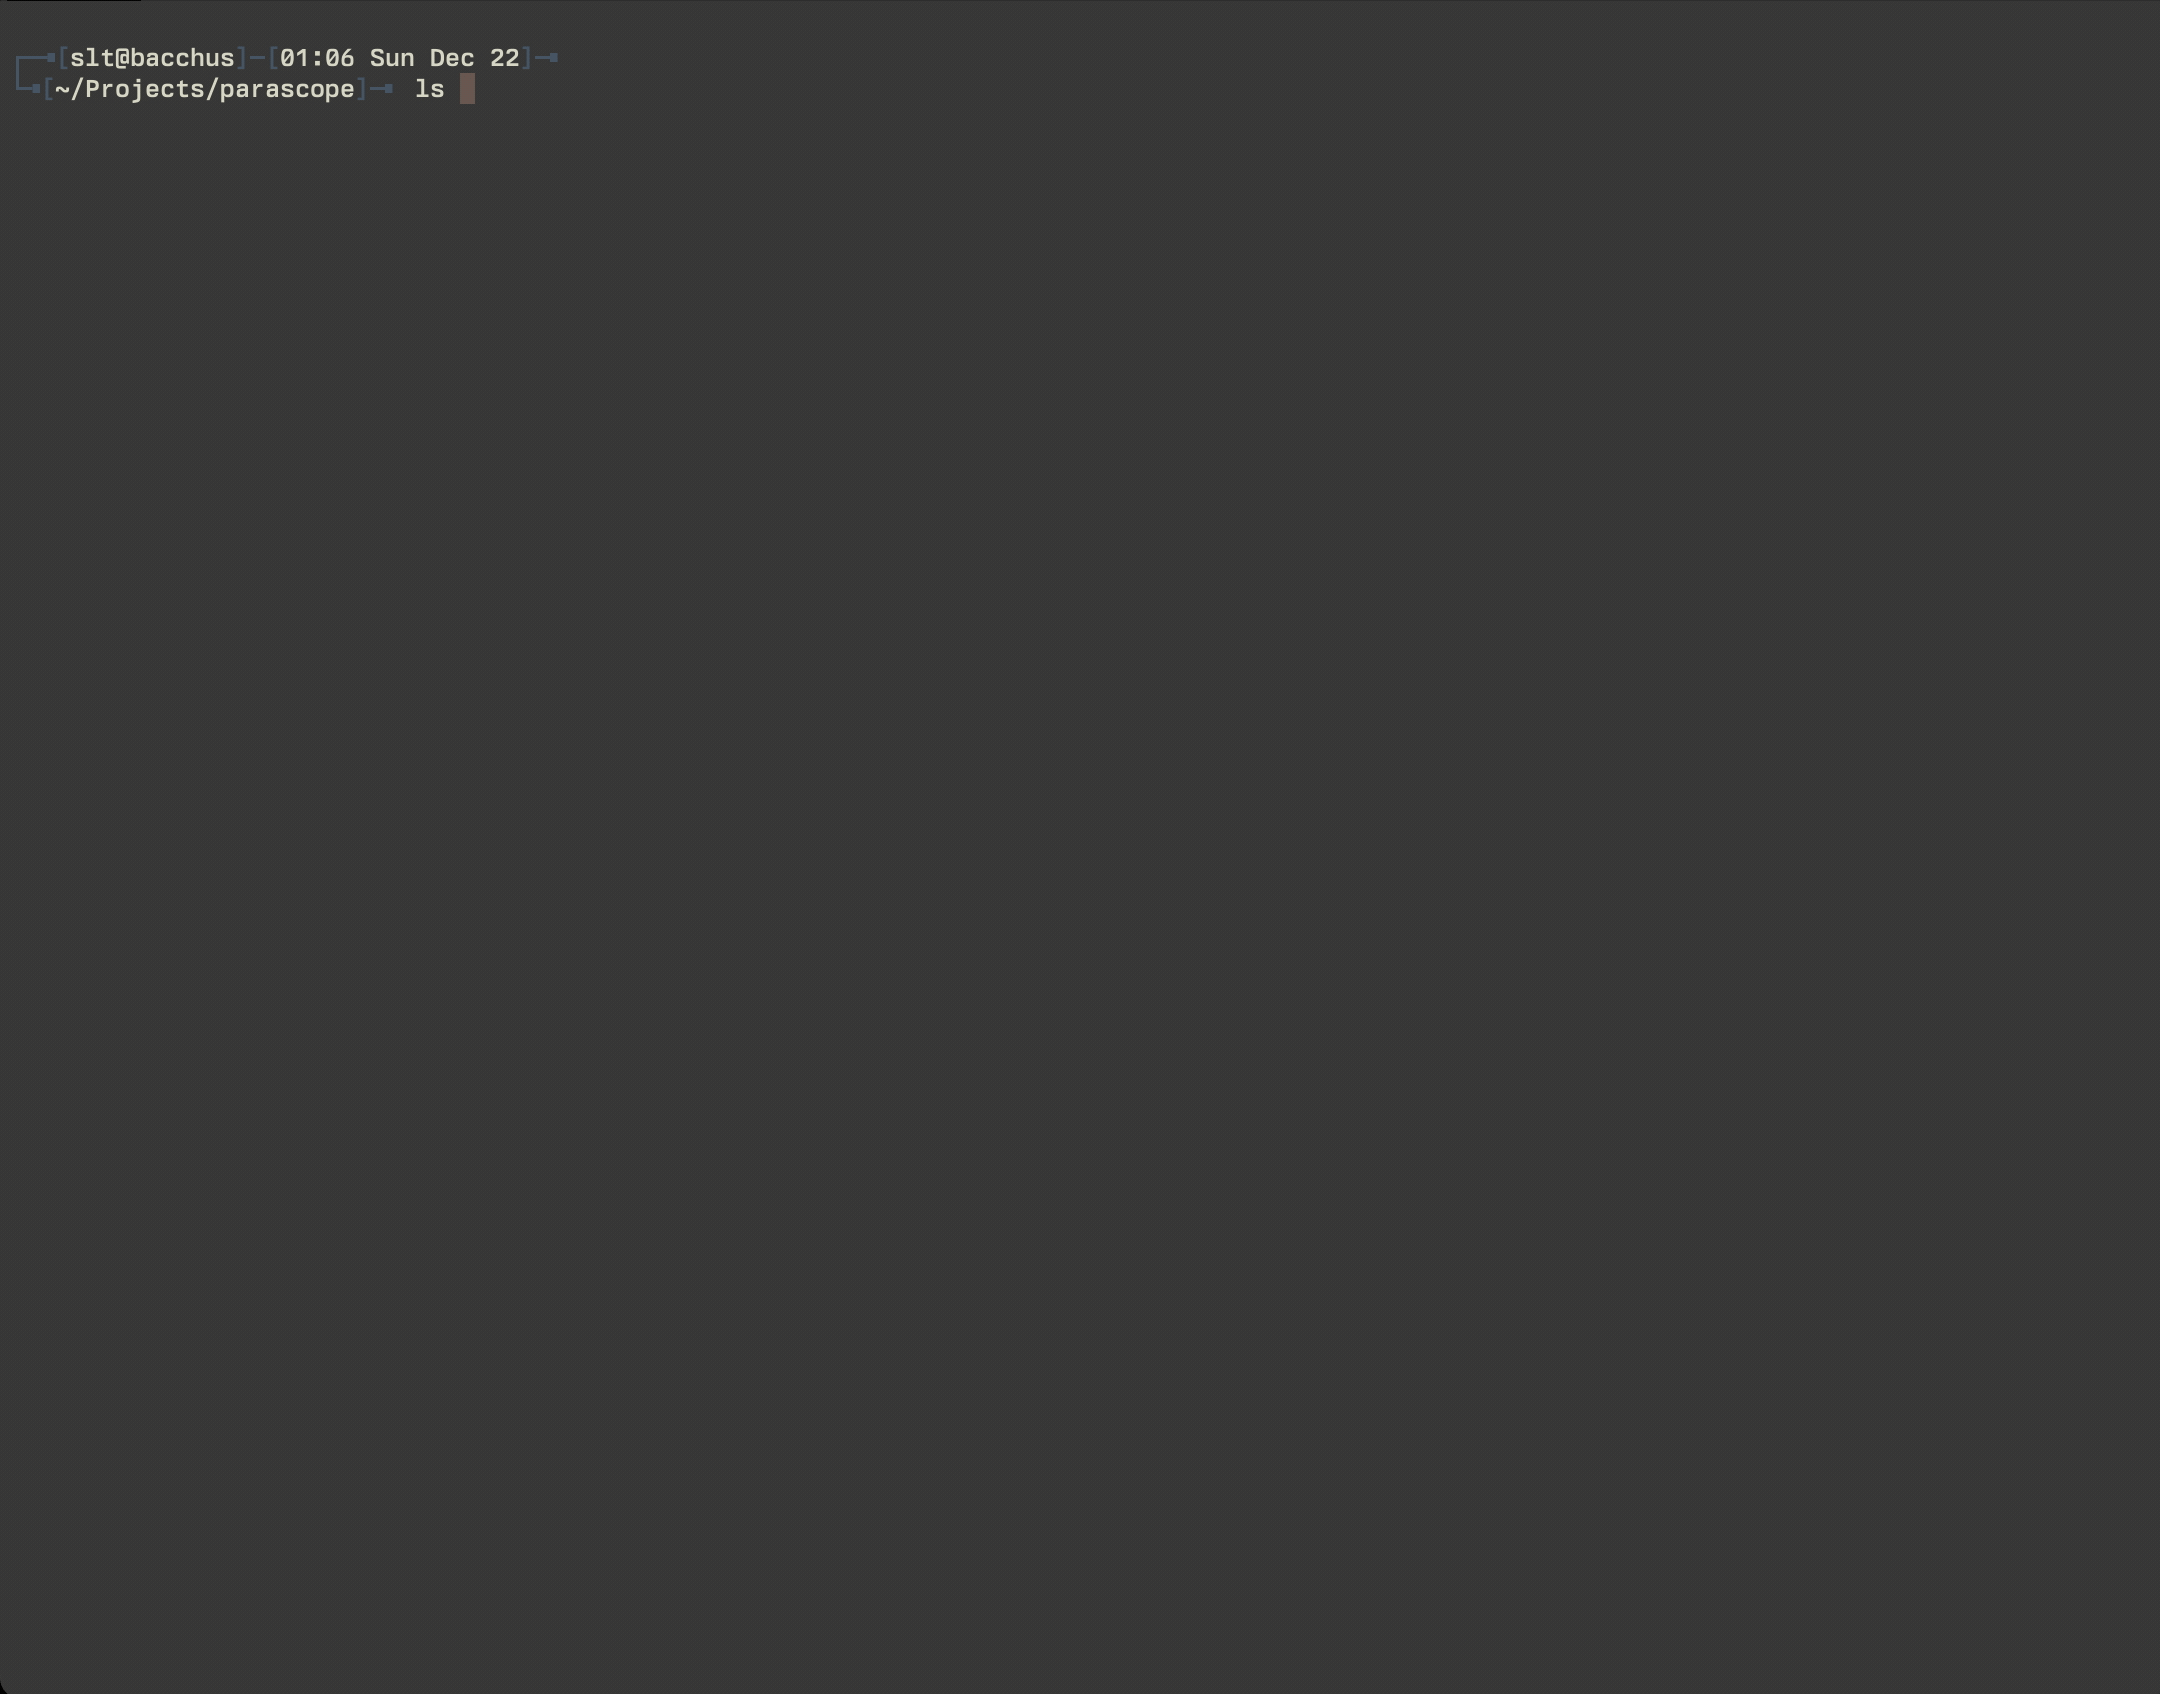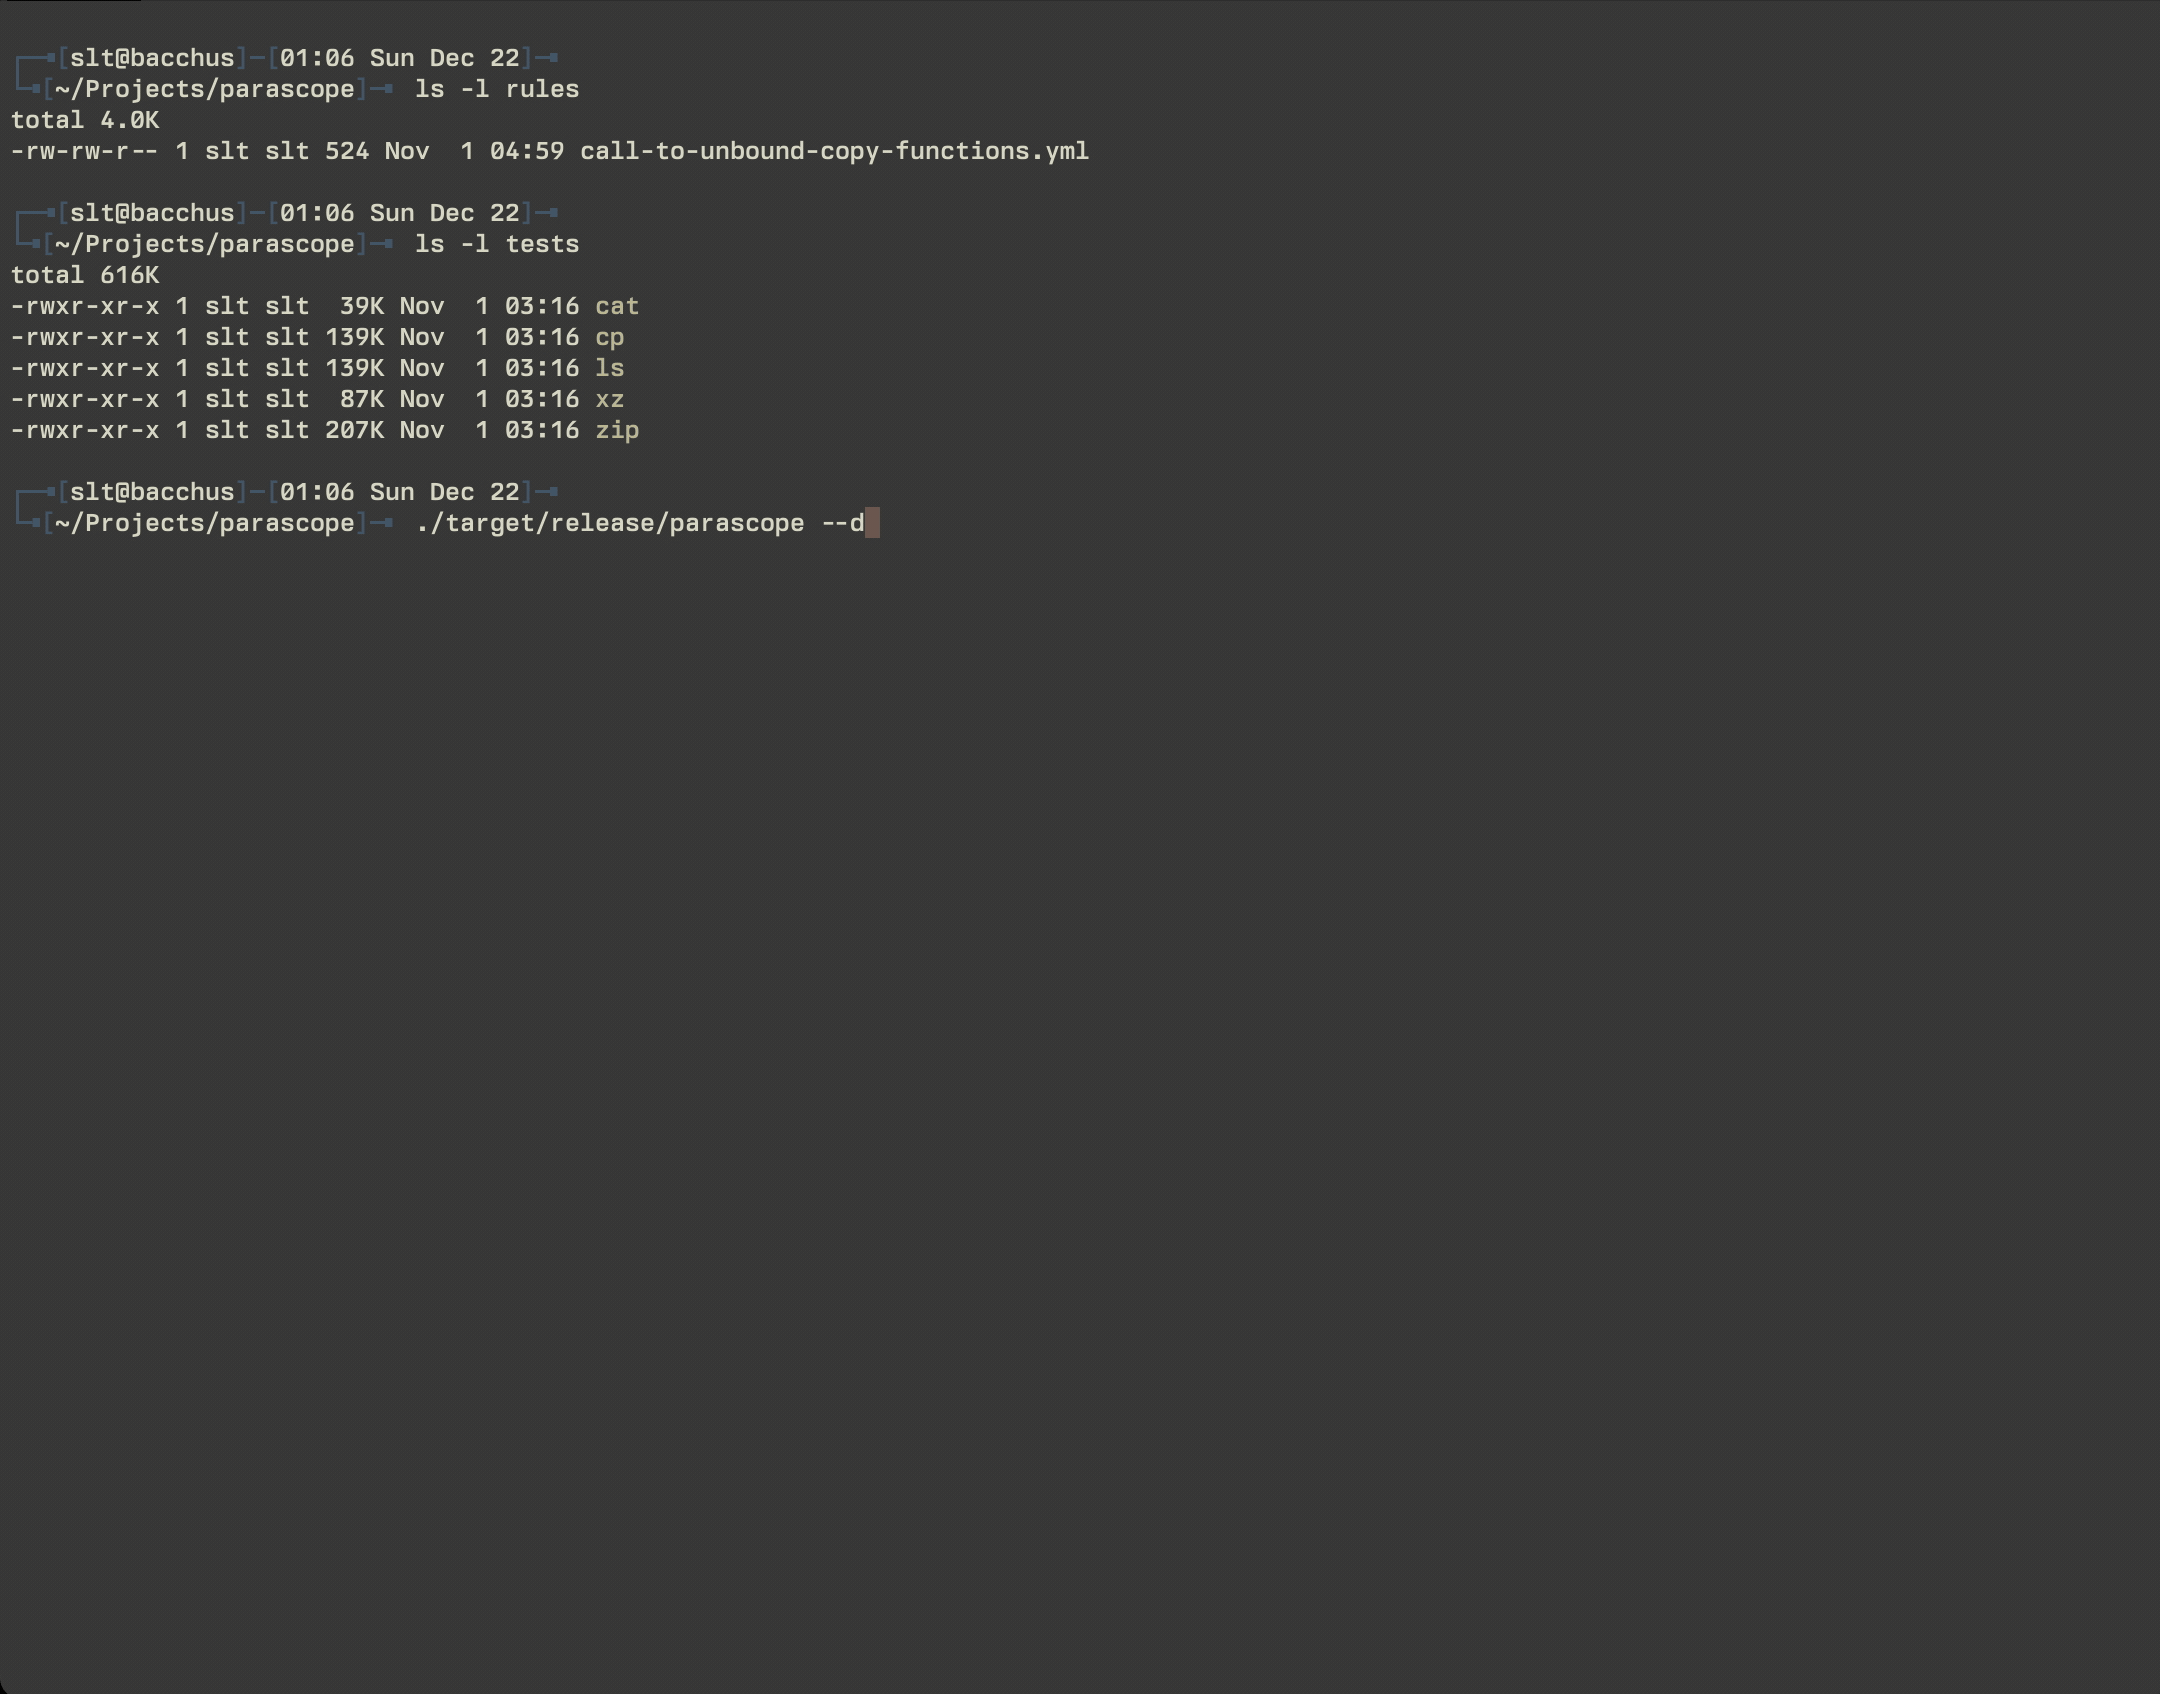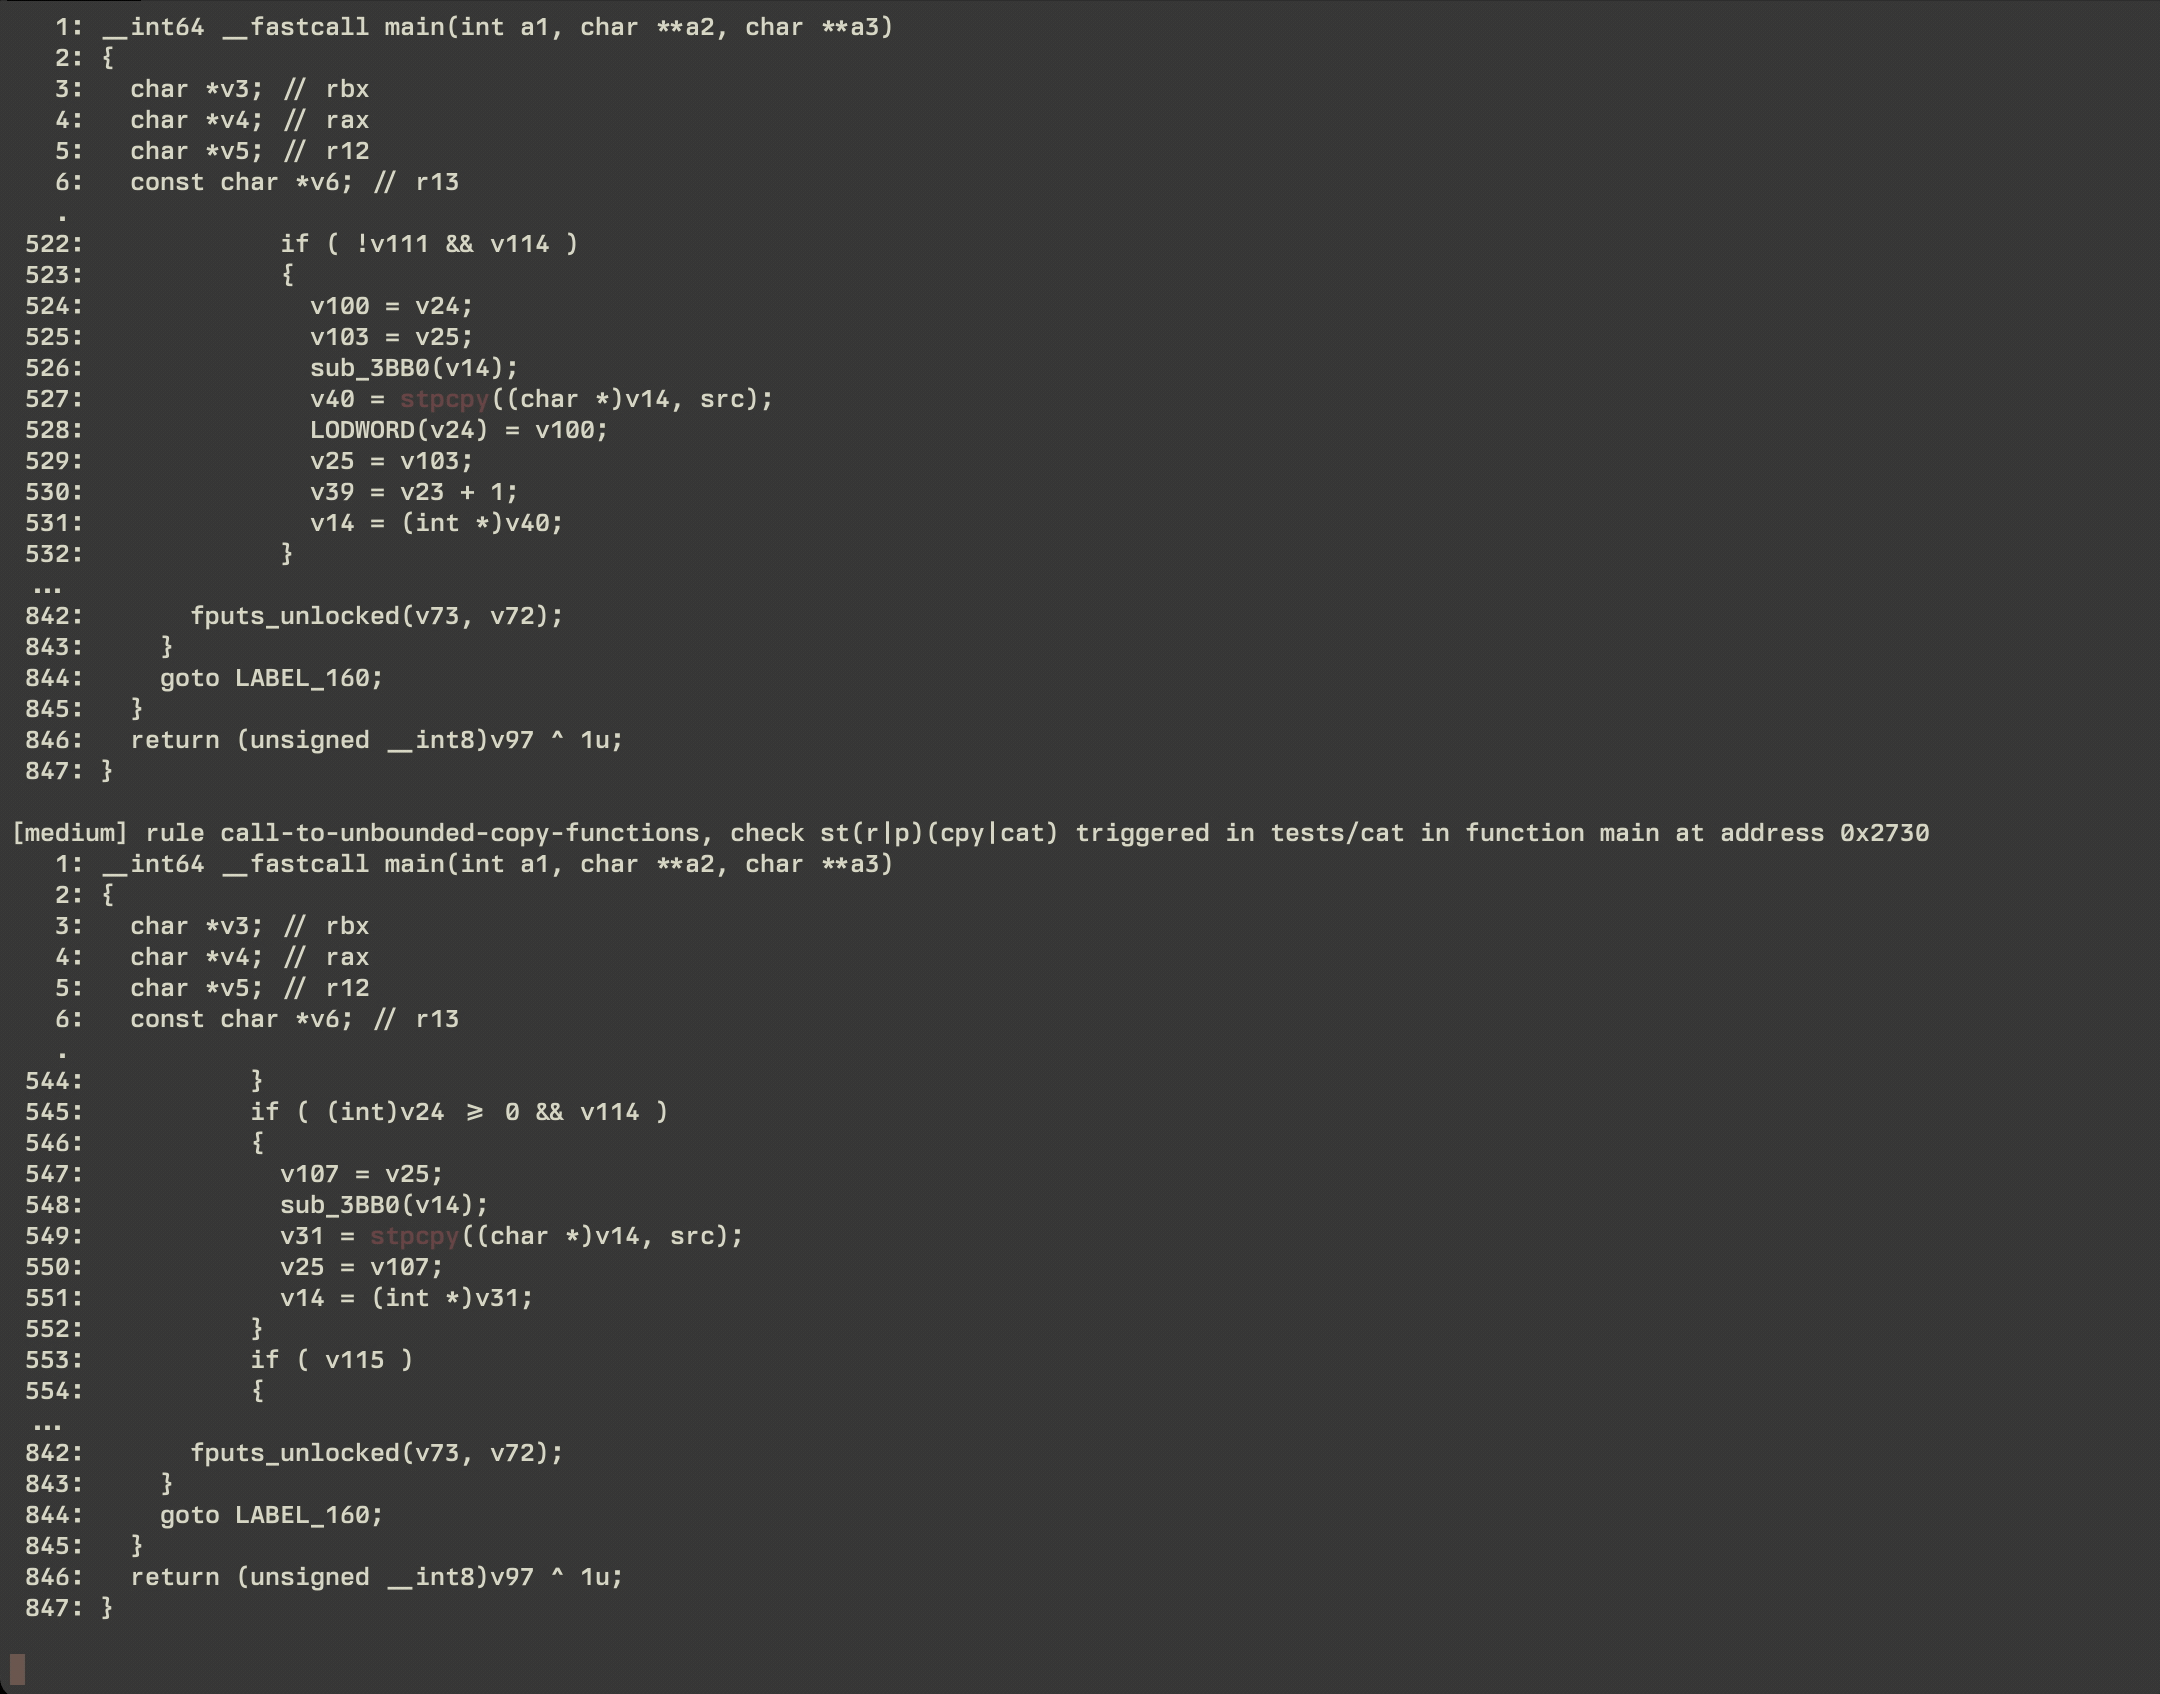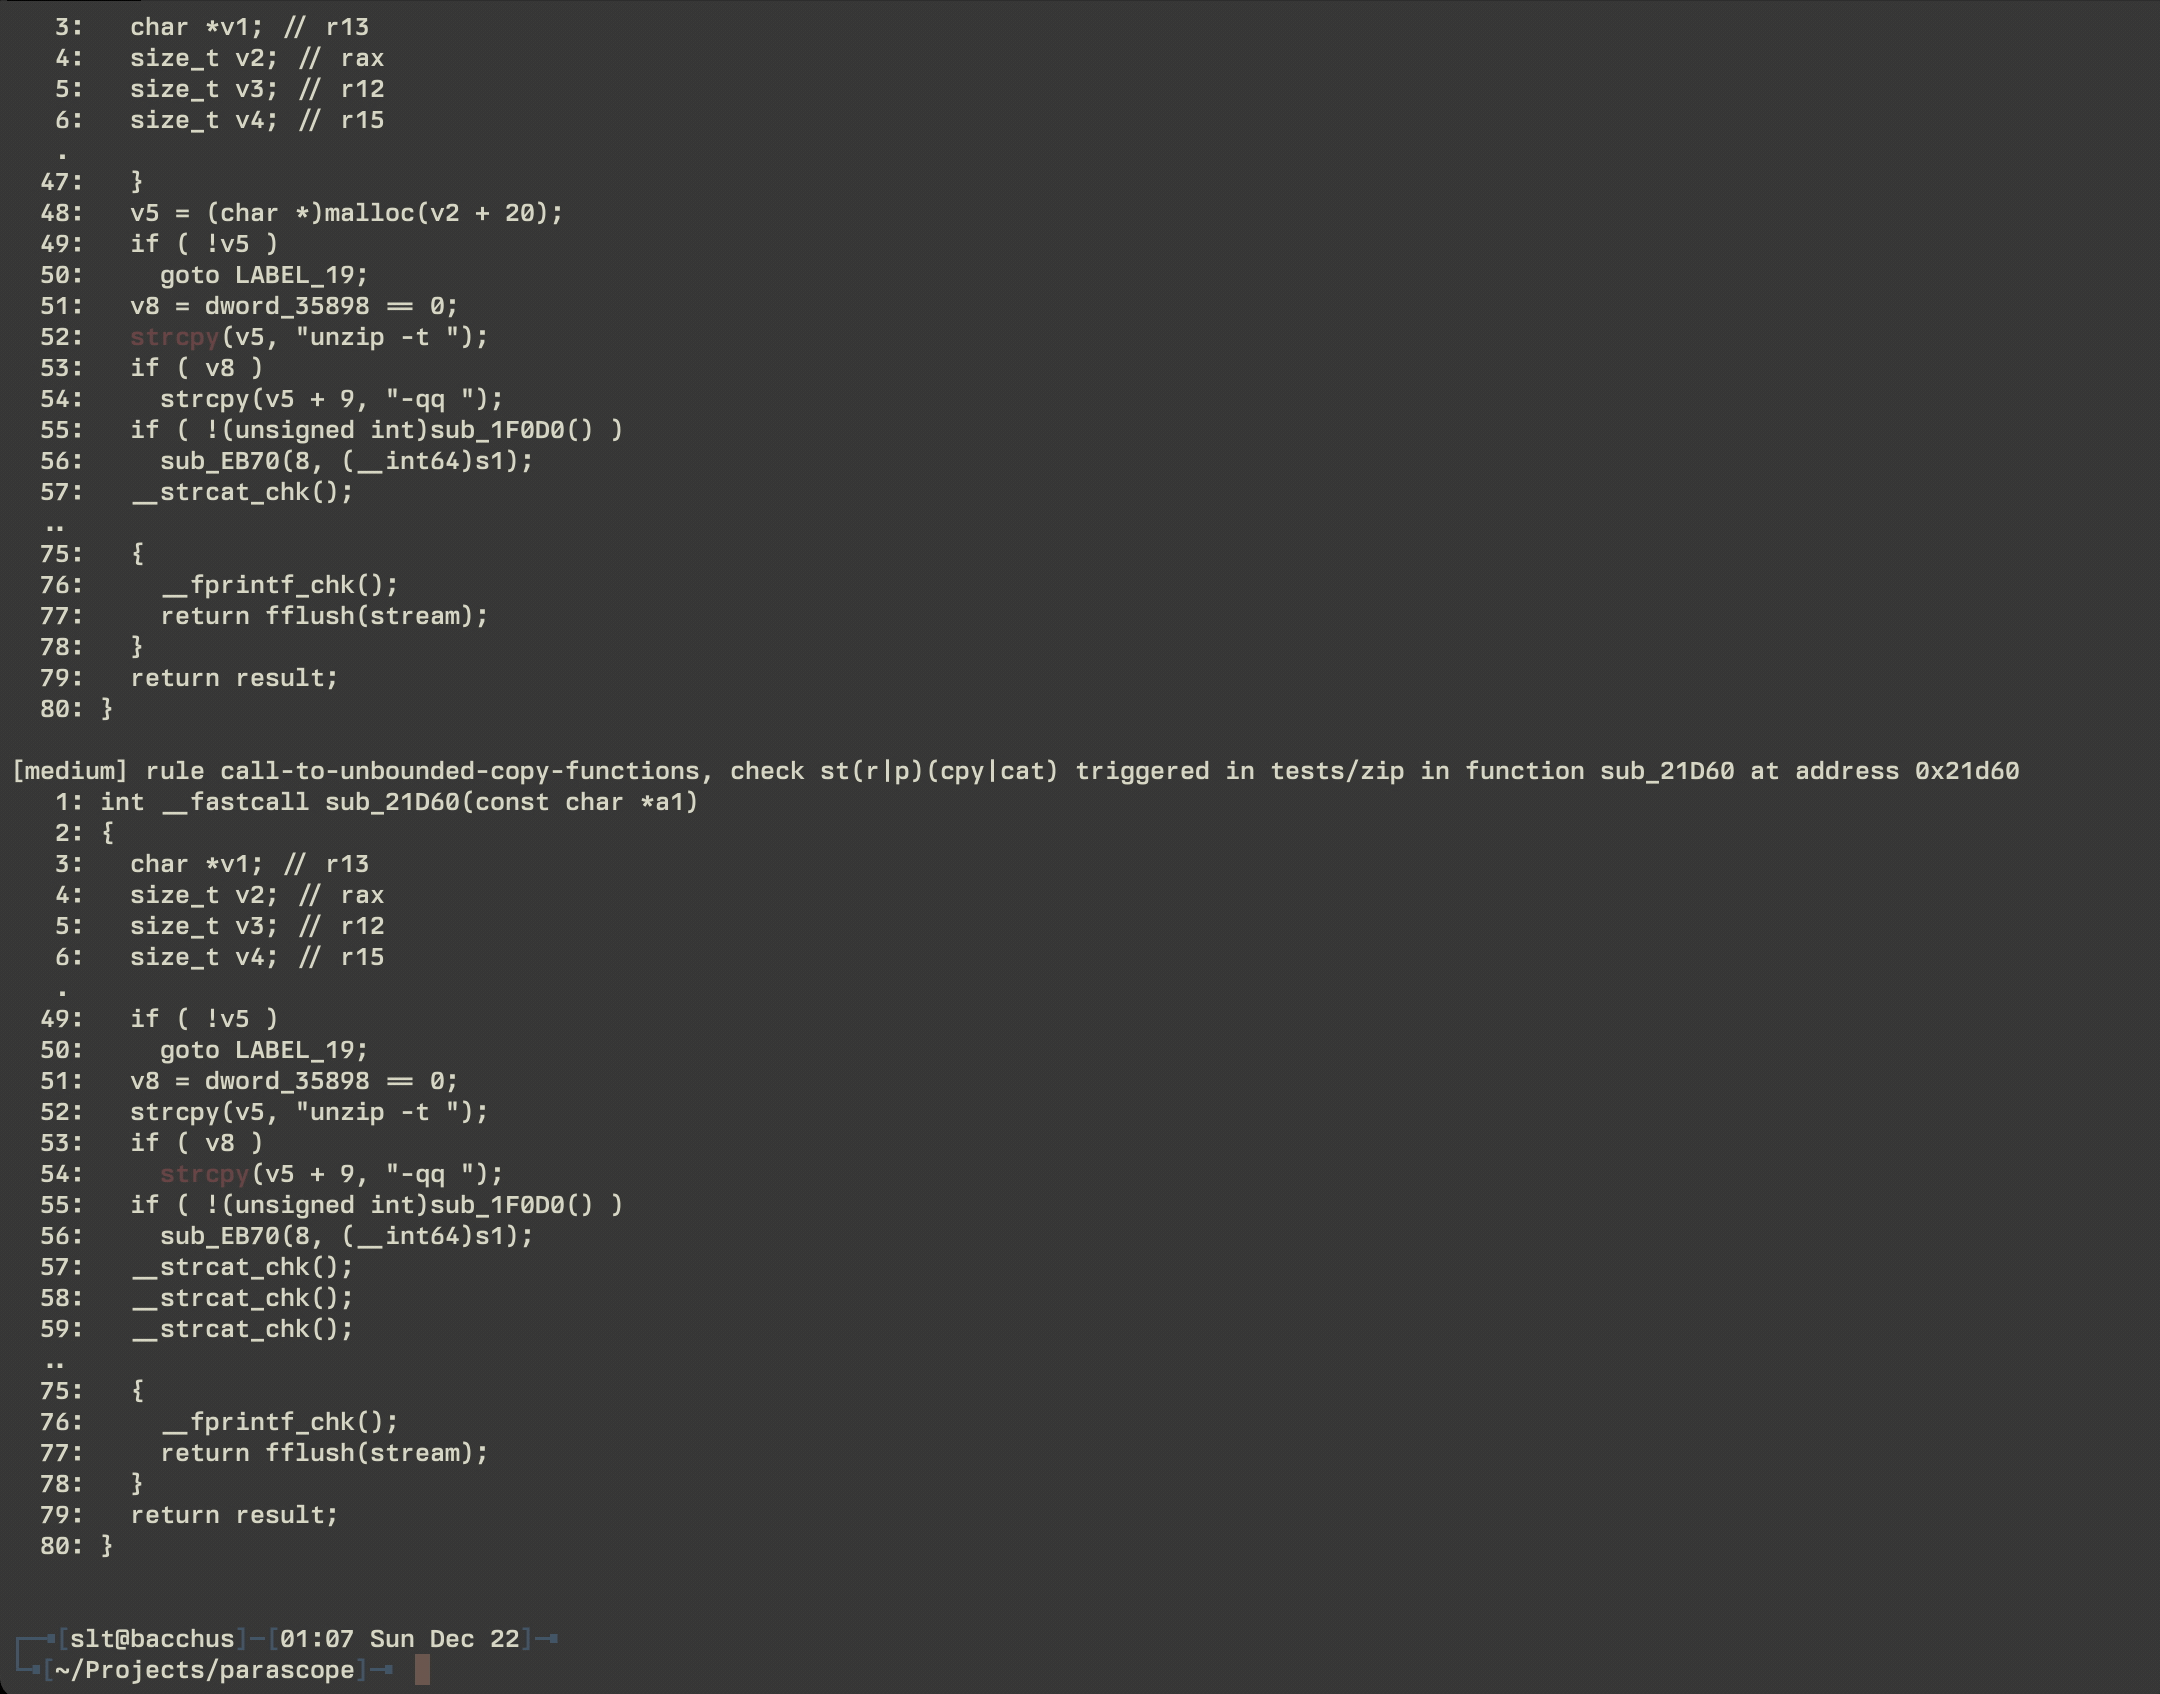
Reviewed xorpse/parascope@42e23e3
Binary · Tool:
MBASED is a Binary Ninja plugin that simplifies mixed Boolean-arithmetic expressions.
Reviewed bliutech/mbased@fb8315f
Binary · Tool:
r2garlic is a radare2 plugin for the Garlic DEX and Dalvik decompiler.
Reviewed radareorg/r2garlic@125c5fd
Binary · Tool:
Pocket Disasm is an MCP router that gives each binary its own headless IDALib worker.
Reviewed whoisqwerz/pocket_disasm@fdcdde8
Firmware · Tool:
Ghidra Hexagon SLEIGH is a Ghidra processor module for Qualcomm Hexagon QDSP6.
Reviewed CUB3D/ghidra-hexagon-sleigh@7ec35fc
Game · Tool:
sega2asm splits a Sega Genesis or Mega Drive ROM by segment.
Reviewed hansbonini/sega2asm@78f37b0
Binary · Tool:
CryptoKnight classifies compiled cryptographic primitives.
Binary · Tool:
cLuaDecompiler is a Free Pascal and Lazarus disassembler and decompiler for Lua bytecode.
Reviewed Coldzer0/LuaDecompiler@e75c48a
Binary · Tool:
HELPDECO dissects Windows Help files from Windows 3.0, 3.1, 3.11, and 95, and many MVB multimedia viewer titles, into the files needed to rebuild them with HC30, HC31, HCP, HCW, HCRTF, WMVC, MMVC, or MVC.
Reviewed pmachapman/helpdeco@7852737
Binary · Tool:
NWiiRecomp translates GameCube and Wii DOL and ELF executables into C++.
Binary · Tool:
Nehebn2 is a Python 3 command-line interface for Binary Ninja.
Reviewed ElykDeer/nehebn2@a92096d
Binary · Tool:
Fishbones is a Python library for implementing decompiled code.
Reviewed sledgeh4w/fishbones@ba22044
Binary · Tool:
JVM Inspector is an x64dbg plugin that reads a HotSpot JVM through VMStructs.
Reviewed kitsune-de/jvm-inspector@00340b3
Binary · Tool:
Binary Ninja PCode loads Ghidra SLEIGH architectures inside Binary Ninja and attempts to lift p-code into Low Level IL.
Reviewed pd0wm/binaryninja-pcode@4755b13
Binary · Tool:
mapfile_parser is a Python and Rust library that parses linker map files for decompilation projects.
Binary · Tool:
idaidle is an IDA Pro plugin that watches idle time.
Reviewed google/idaidle@d3206f1
Binary · Tool:
lumina-binja is a Binary Ninja plugin for IDA Lumina metadata.
Reviewed ubcctf/lumina-binja@e46a6e7
Binary · Tool:
gamedb is a Rust command-line tool that indexes a directory of decompiled C, C++, Java, or C# into SQLite.
Reviewed smileybaal/gamedb@7054201
Binary · Tool:
BNPyc is a Binary Ninja plugin that disassembles Python bytecode from version 3.0 through 3.10.
Reviewed Njord0/BNPyc@2bad86e
Binary · Tool:
bnpy is a Binary Ninja architecture plugin that disassembles raw Python bytecode.
Reviewed extremecoders-re/bnpy@58ba9fe
Binary · Tool:
HEXPYRION recovers Python source from Nuitka-compiled PE, ELF, and Mach-O binaries.
Reviewed DimaReverse/hexpyrion@4daa534
Binary · Tool:
This is an IDA loader and processor for YARA's compiled rule format.
Reviewed bnbdr/ida-yara-processor@d784e5b
Binary · Tool:
ida-headless embeds RPyC in IDA so a background thread serves IDA's API over TCP port 18812.
Reviewed hugsy/ida-headless@2f2d6ec
Binary · Tool:
UQBT is the University of Queensland binary translator.
Reviewed osfree-project/uqbt@1b33e29
Binary · Tool:
This IDA plugin disassembles x86-64 instructions, including inlined WOW64 code, inside a 32-bit IDA database.
Reviewed a1ext/ida-embed-arch-disasm@aa86249
Binary · Tool:
This Python module reads PowerBuilder PBD files.
Reviewed sijms/PowerBuilder-decompile@5a7b9b0
Binary · Tool:
x64dbg_ext adds three commands to x64dbg.
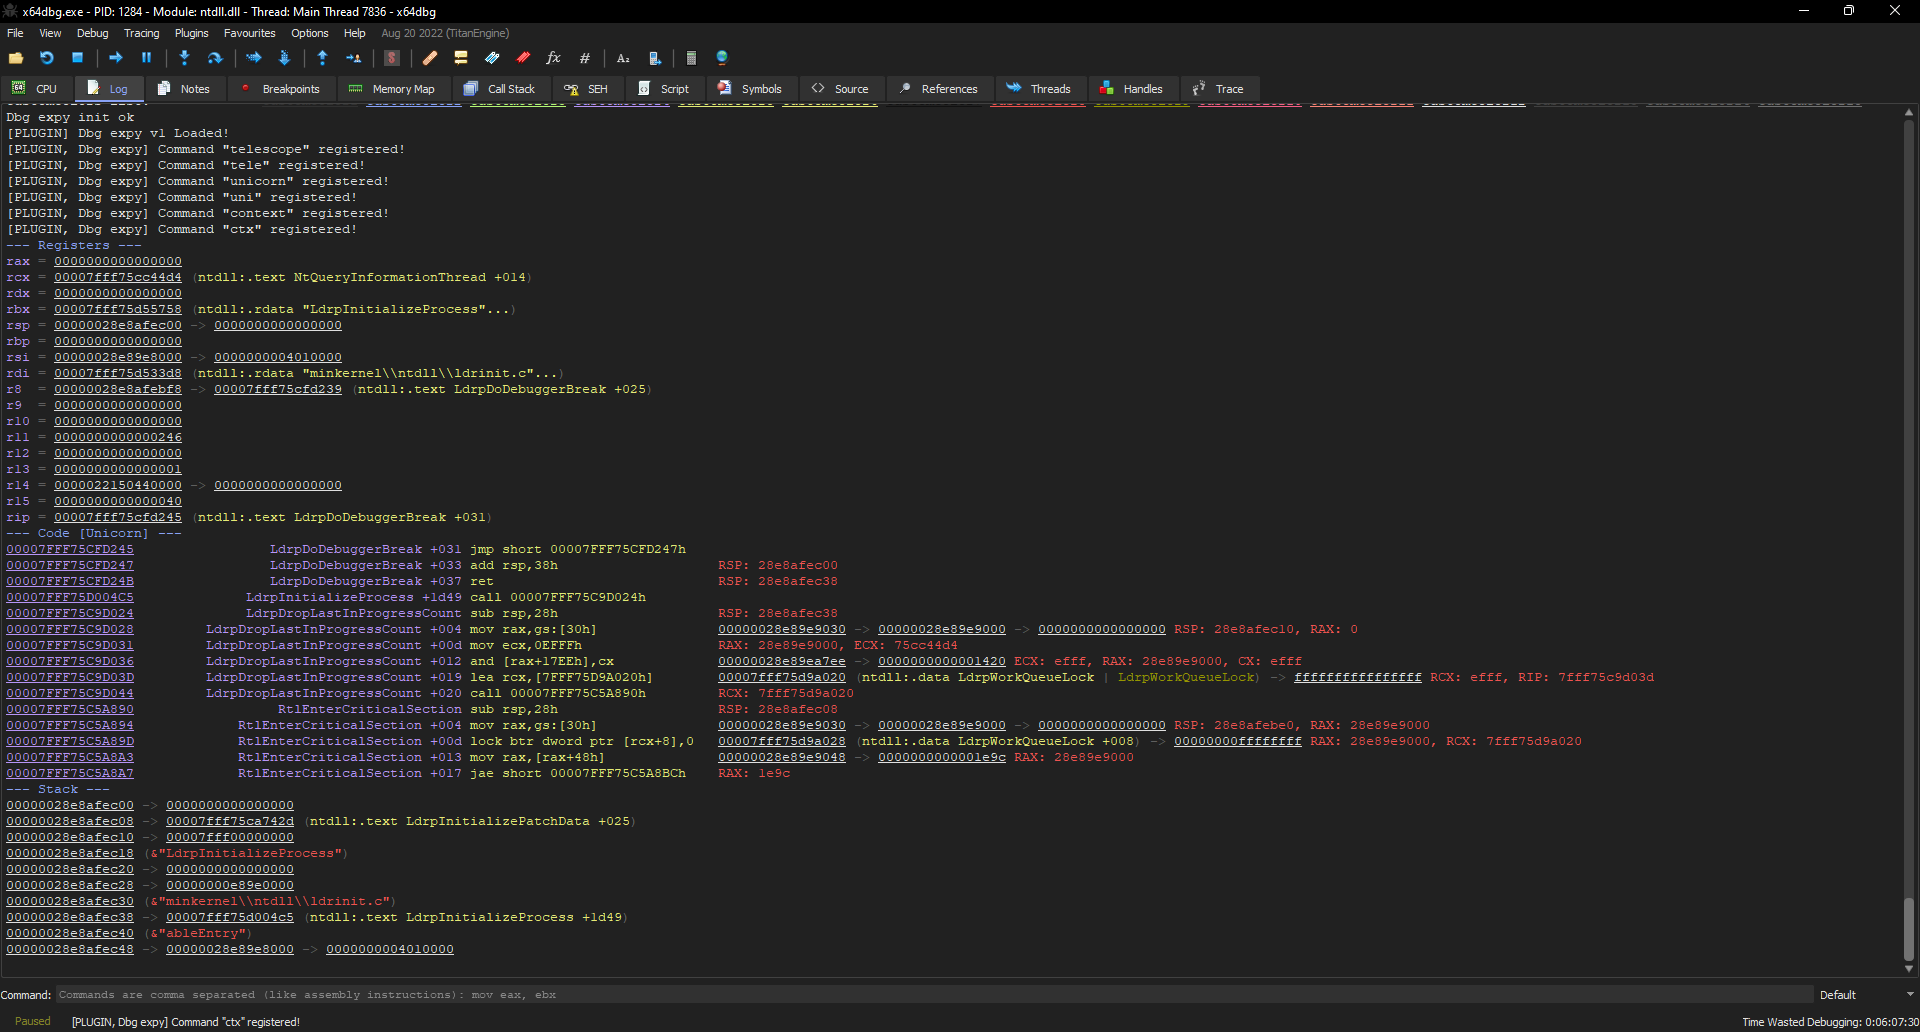
Reviewed expend20/x64dbg_ext@0e86748
Binary · Tool:
SemRay is an IDA Pro plugin that sends decompiler context to the Gemini API and applies reviewed names back to the IDB.
Reviewed 19h/ida-semray@3b4c01c
Game · Tool:
This splits the US Paper Mario ROM for the Nintendo 64.
Binary · Tool:
delink splits binaries for decompilation projects.
Reviewed HaydnTrigg/delink@fc10946
Binary · Tool:
AFL++ is a coverage-guided fuzzer forked from American Fuzzy Lop.
Reviewed AFLplusplus/AFLplusplus@d007072
Binary · Tool:
AsmDude2 is a Visual Studio 2022 extension and language server for assembly.
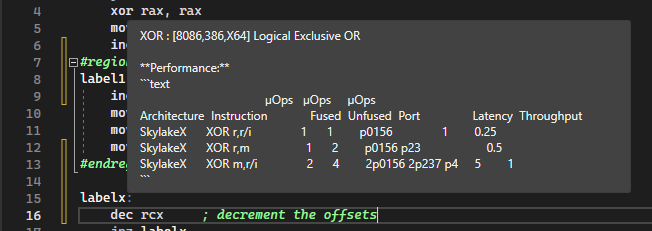
Reviewed HJLebbink/asm-dude@93b5669
Binary · Tool:
RePKG is a C# unpacker for Wallpaper Engine PKG files and a converter for TEX images.
Reviewed notscuffed/repkg@8005eb2
Binary · Tool:
Malimite decompiles iOS and macOS IPA files and application bundles on Mac, Windows, and Linux.
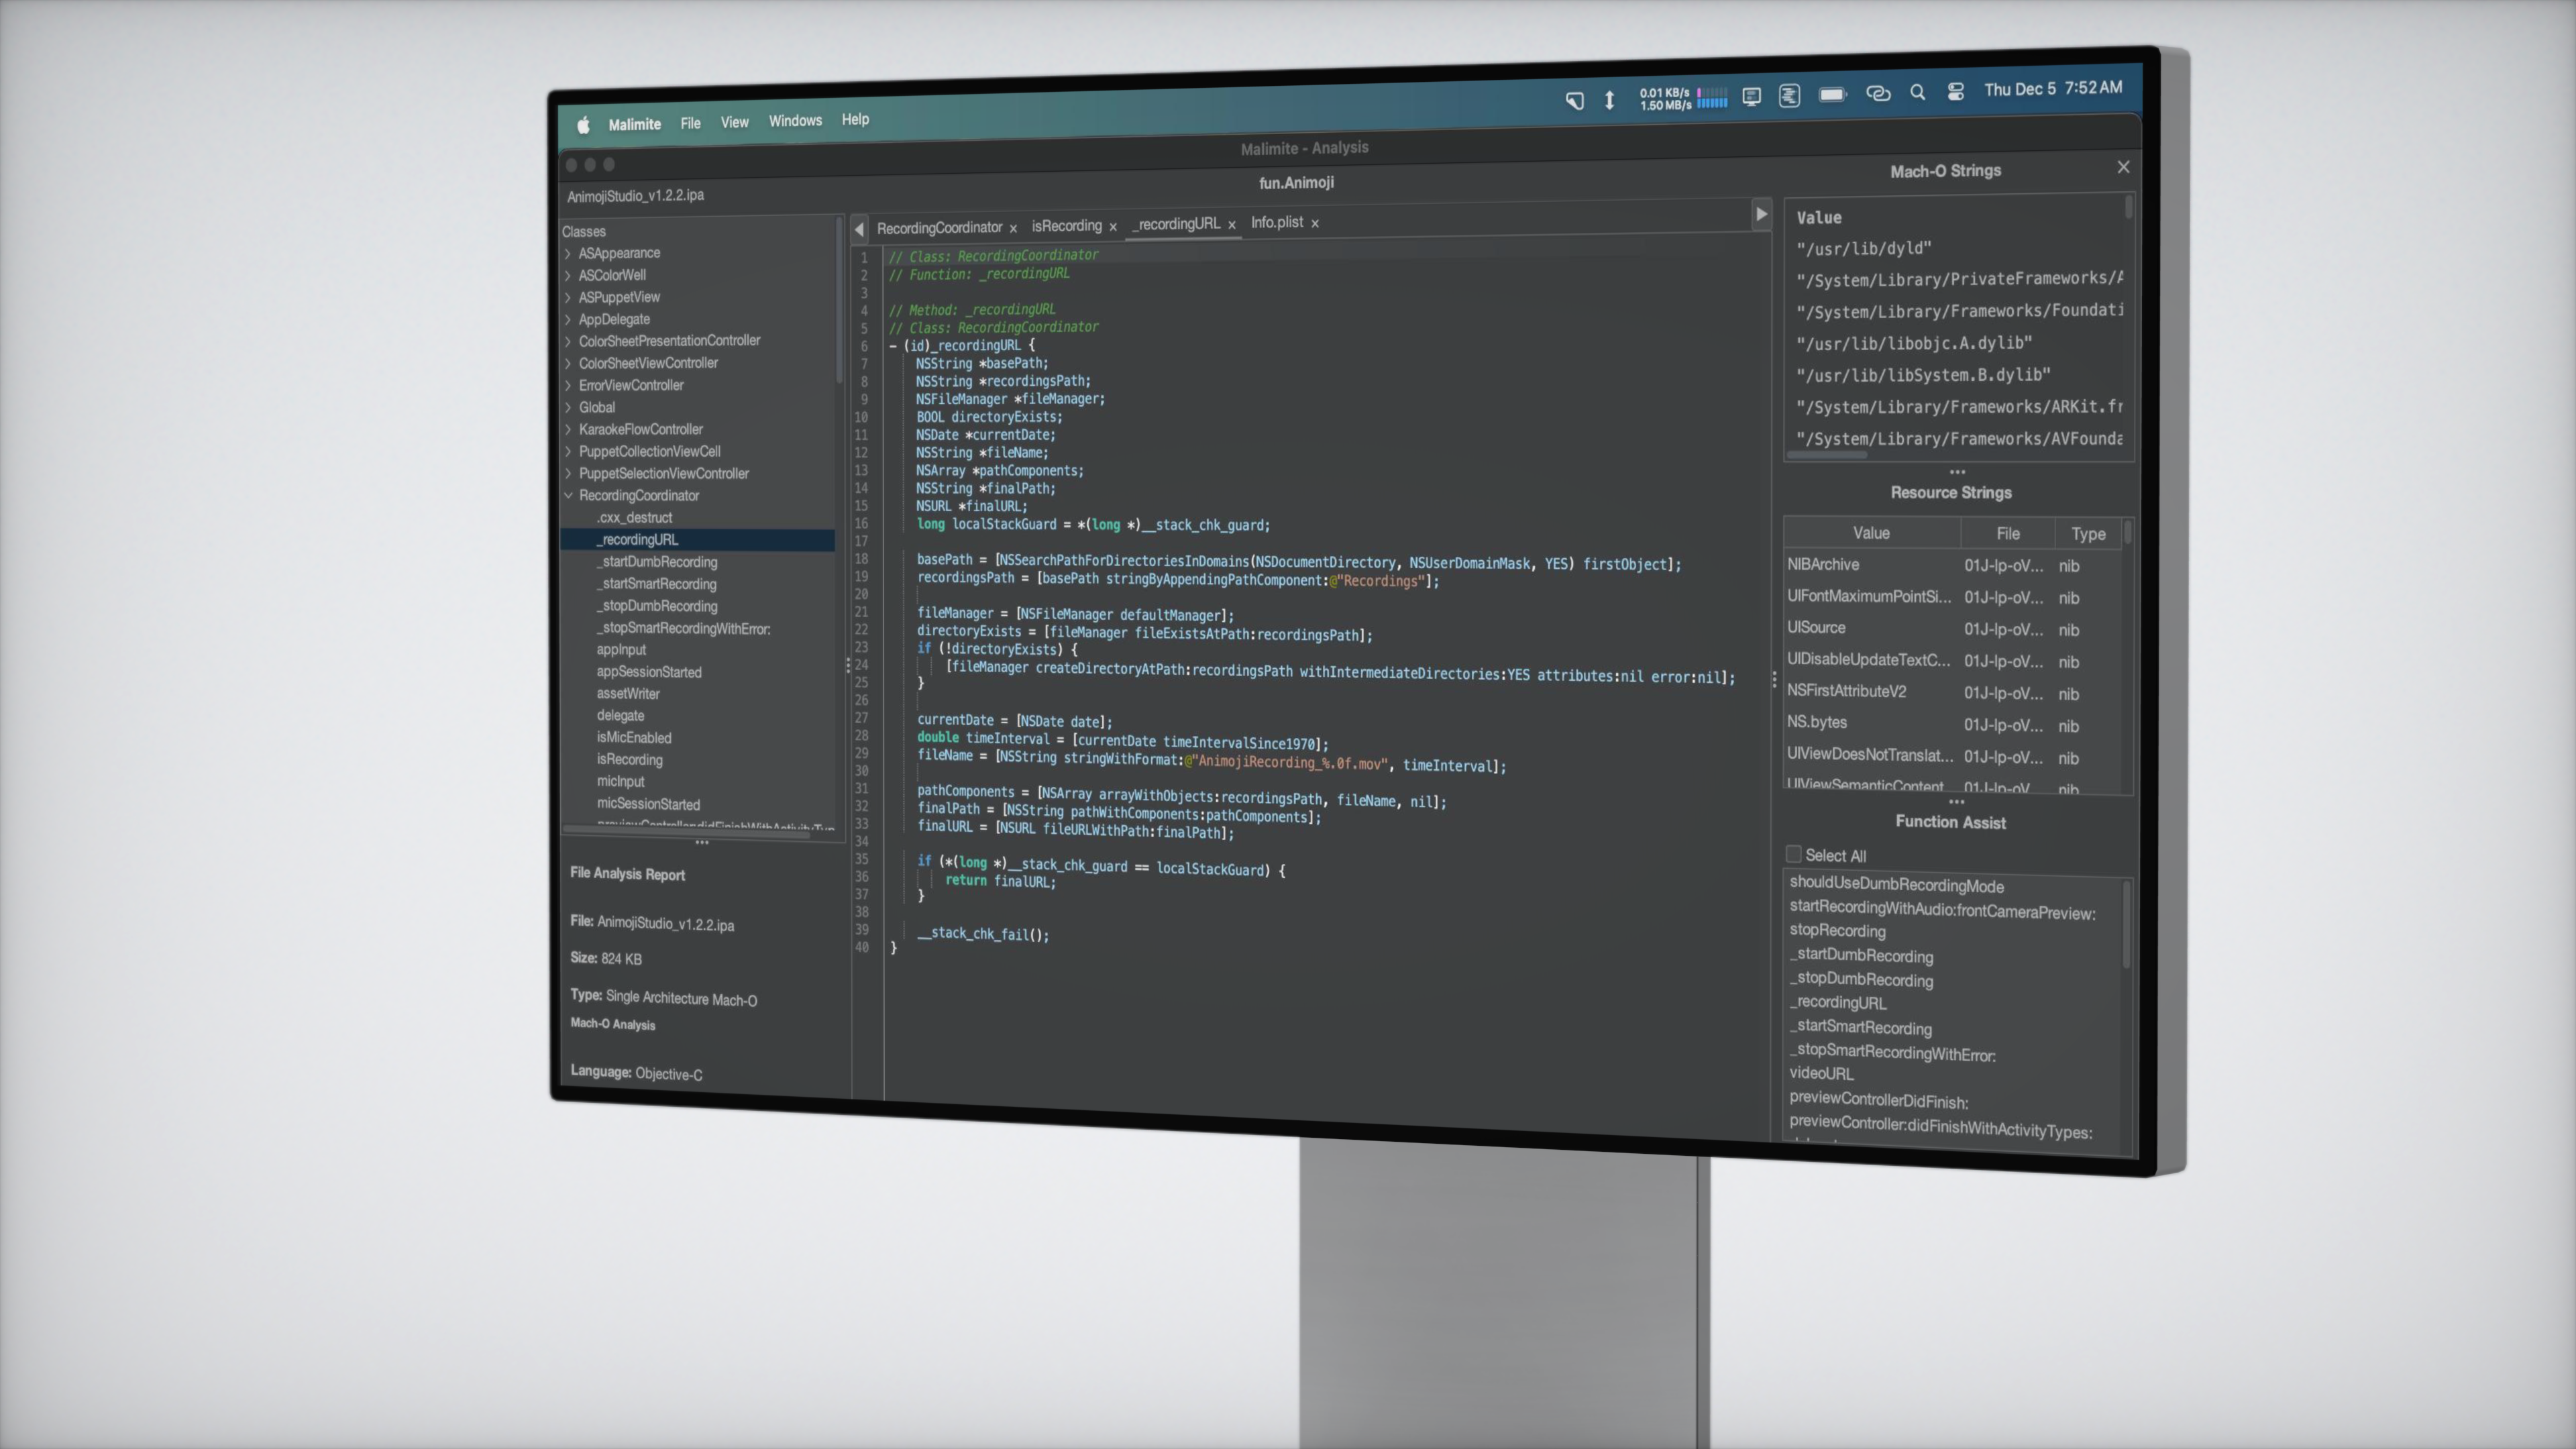
Reviewed LaurieWired/Malimite@f25b0a6
Binary · Tool:
SPIRV-Cross parses SPIR-V and converts it to GLSL, Metal Shading Language, HLSL, and a JSON reflection format.
Reviewed KhronosGroup/SPIRV-Cross@57e4efc
Binary · Tool:
PowerUp is a set of disassembly and decompilation utilities.
Reviewed badamczewski/PowerUp@cd197e3
Binary · Tool:
BiTE inspects executable content and debug information.
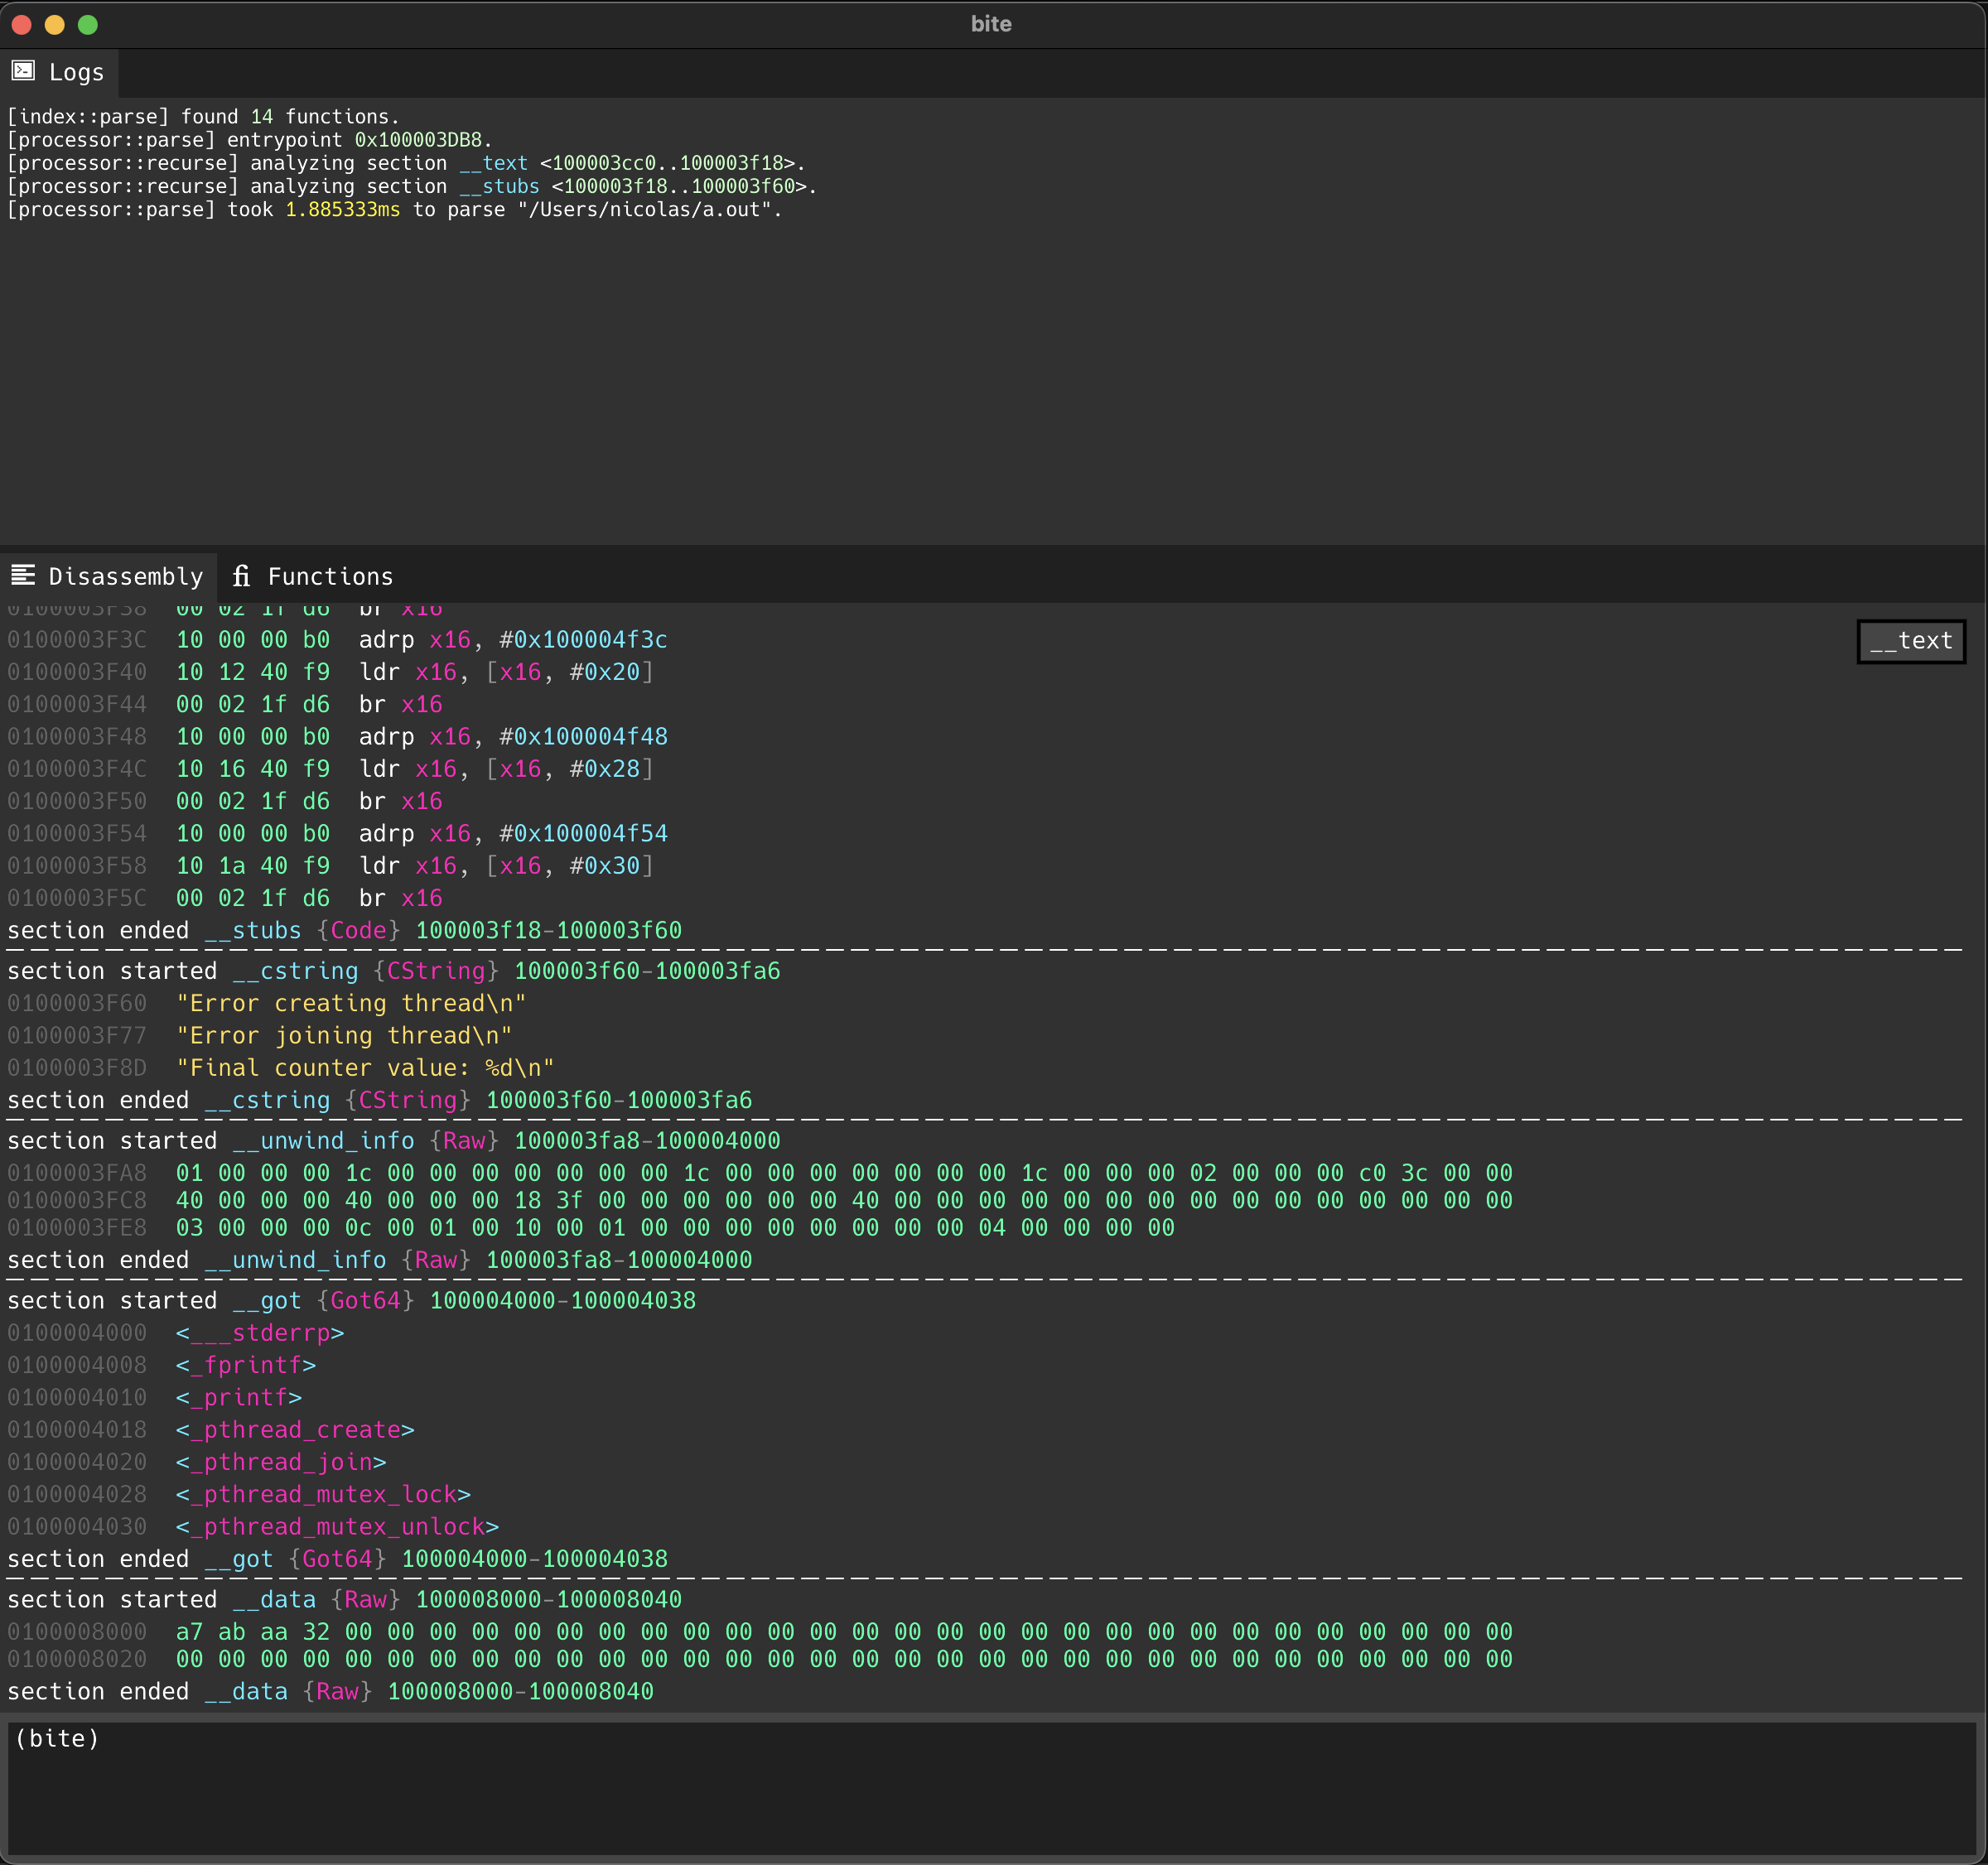
Reviewed WINSDK/bite@54c10e1
Binary · Tool:
gooMBA is a Hex-Rays Decompiler plugin that simplifies mixed Boolean-arithmetic expressions.
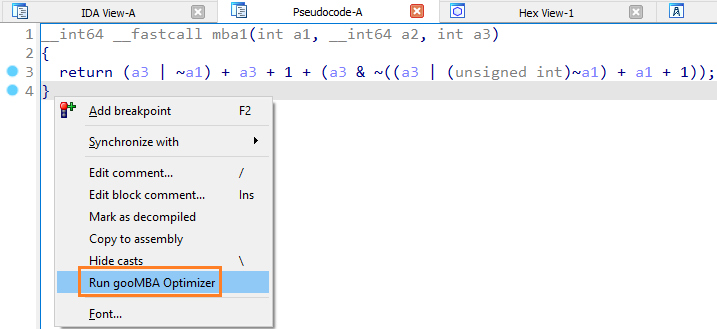
Reviewed HexRaysSA/goomba@8302f5b
Binary · Tool:
NtRays is a Hex-Rays microcode plugin that simplifies Windows kernel decompilation.
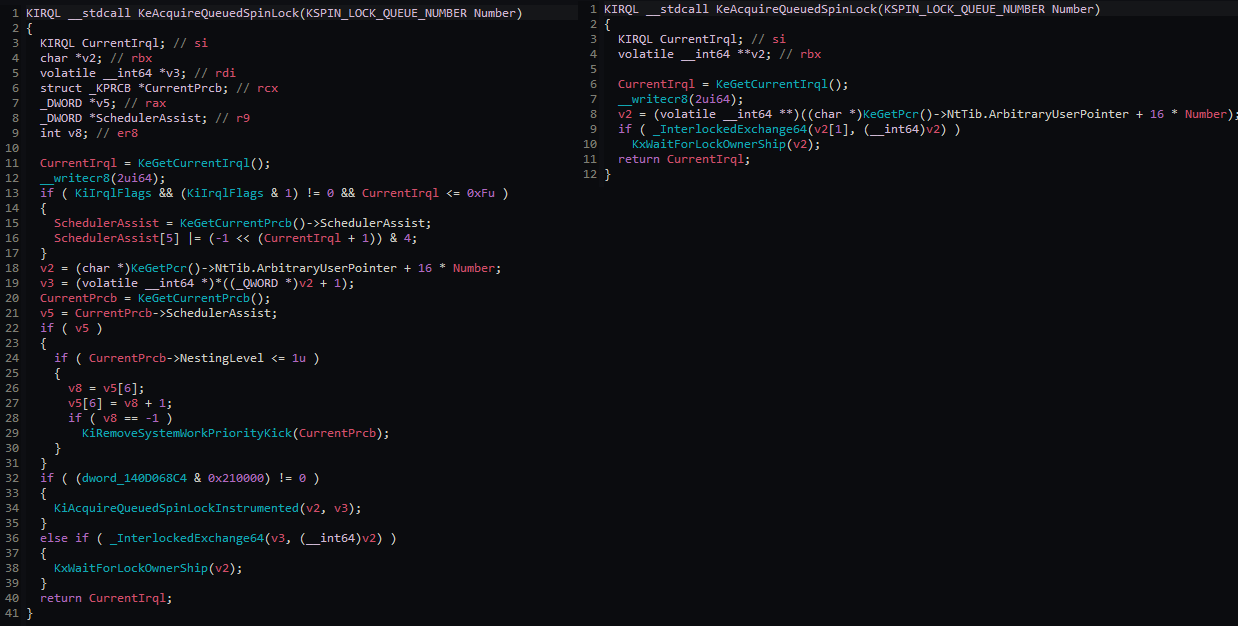
Reviewed can1357/NtRays@254eea6
Binary · Tool:
Fickling decompiles and statically analyzes Python pickle serializations, including PyTorch files.
Reviewed trailofbits/fickling@c098aeb
Binary · Tool:
r2ghidra integrates the Ghidra decompiler into radare2.
Reviewed radareorg/r2ghidra@edc6310
Binary · Tool:
Oxidizer is a Rust decompiler on angr. It identifies compiler versions from 1.39.0 through 1.93.0, recovers standard-library functions, and emits Rust pseudocode with enums, match, the ?
Reviewed sefcom/oxidizer@fc18d0a
Binary · Tool:
E-Decompiler is an IDA plugin for analyzing EPL programs.
Reviewed fjqisba/E-Decompiler@0d50f09
Binary · Tool:
Nyxstone assembles and disassembles code with the LLVM libraries already shipped by Linux distributions, Homebrew, and apt.llvm.org.
Reviewed emproof-com/nyxstone@14e894f
Binary · Tool:
Mikage Developer Edition is a Nintendo 3DS emulator.
Reviewed mikage-emu/mikage-dev@3e1952b
Binary · Tool:
STrace reimplements the Windows DTrace syscall and ETW probes.
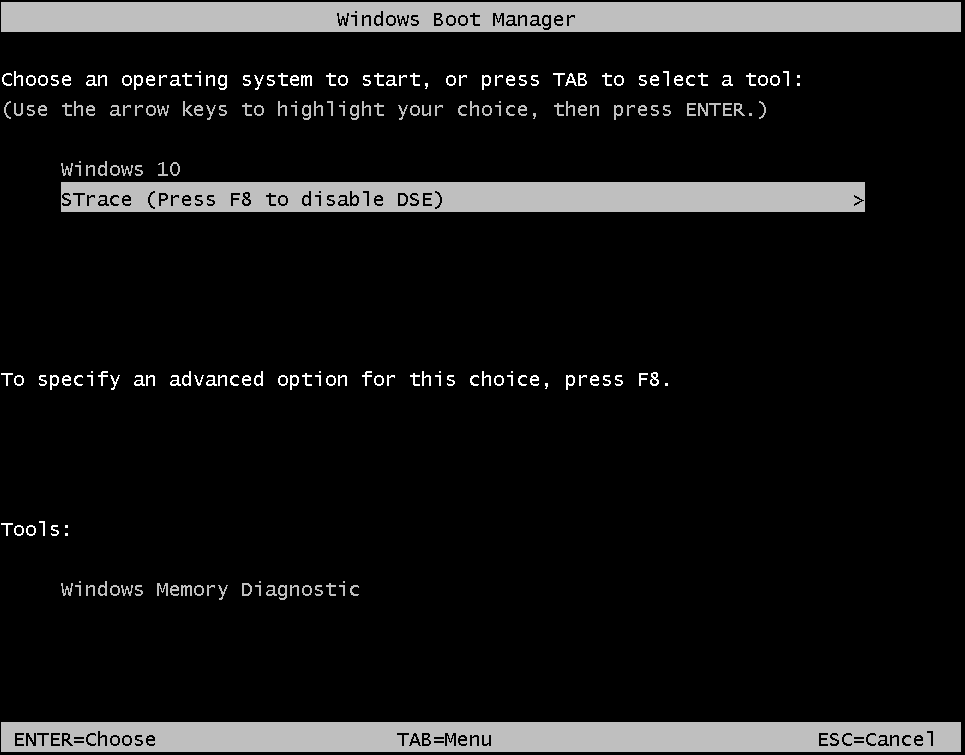
Reviewed mandiant/STrace@39d2cc4
Binary · Tool:
BinAIVulHunter is an IDA Pro plugin that sends Hex-Rays decompiled functions to OpenAI, Google Gemini, or a local Ollama model and reports possible vulnerabilities.
Reviewed ke0z/BinAIVulHunter@1b0b990
Binary · Tool:
pyasmtools has a Python bytecode disassembler and a tracer that prints each executed source line with the variables loaded and stored.
Reviewed MoserMichael/pyasmtool@f418cff
Game · Tool:
GameRoy is a Rust Game Boy emulator and debugger for the original DMG.
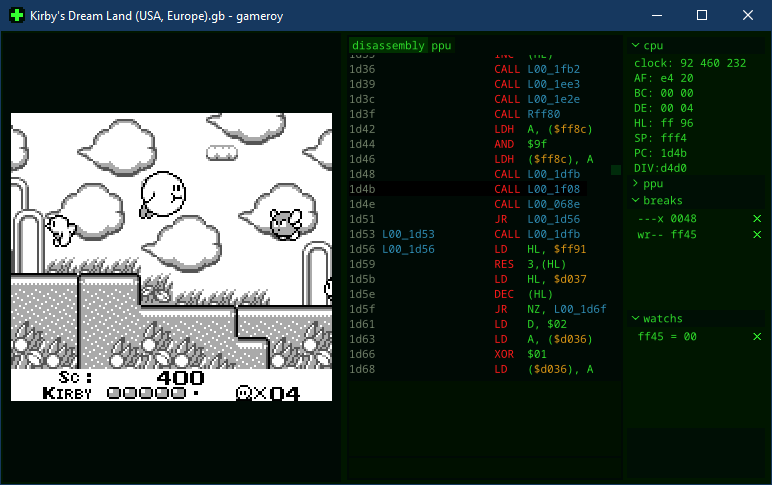
Reviewed Rodrigodd/gameroy@a5acdc9
Binary · Tool:
chernobog is a Hex-Rays decompiler plugin for Hikari LLVM obfuscation.
Reviewed 19h/chernobog@579c1c0
Binary · Tool:
ProjectorRays decompiles Adobe Director and Shockwave movies back to Lingo and editable project files.
Reviewed ProjectorRays/ProjectorRays@6f9bceb
Game · Tool:
Mupen64Plus-Next is a Nintendo 64 emulation library for the libretro API and the successor of the older Mupen64Plus libretro core.
Binary · Tool:
disasm.pro, formerly disasm.ninja, is a multi-architecture assembler and disassembler with line-to-line correlation.
Reviewed ret2jazzy/disasm.pro@f32009a
Binary · Tool:
ROPMEMU analyzes code-reuse attacks from a physical memory dump and reconstructs equivalent code for ordinary reverse-engineering tools.
Reviewed Cisco-Talos/ROPMEMU@d734228
Binary · Tool:
abi-decompiler recovers names and argument counts for functions in Ethereum bytecode.
Reviewed Decurity/abi-decompiler@ee042e7
Binary · Tool:
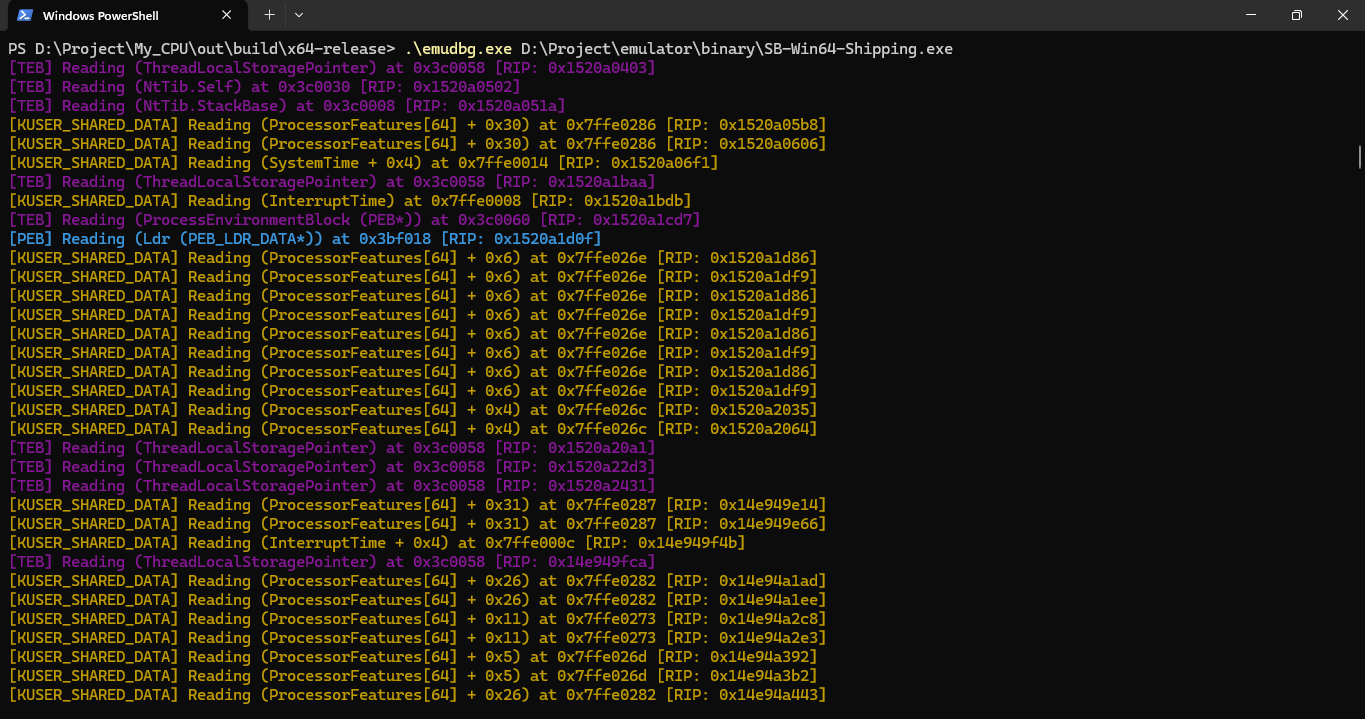
EmuDbg debugs a Windows executable by disassembling it with Zydis and emulating its instructions.
Reviewed mojtabafalleh/emudbg@4e095c3
Game · Tool:
DolRecomp statically recompiles GameCube and Wii PowerPC code, with an early Espresso path for Wii U RPX files.
Reviewed ExpansionPak/DolRecomp@02e27ac
Binary · Tool:
Py2ExeDecompiler recovers source from executables built with py2exe.
Reviewed endgameinc/Py2ExeDecompiler@e871e04
Binary · Tool:
dcc is Cristina Cifuentes and Mike Van Emmerik's decompiler for DOS executables, with later fixes for memory reallocation during decompilation.
Reviewed nemerle/dcc@e0585cc
Binary · Tool:
HRAST is an IDAPython proof of concept for matching and rewriting the Hex-Rays ctree.
Reviewed sibears/HRAST@5c64853
Binary · Tool:
Ouroboros is a Rust decompiler that recovers structure with symbolic execution and constraint tracking.
Reviewed Hexorg/Ouroboros@729c5b6
Binary · Tool:
genmc is an IDAPython script and plugin that displays Hex-Rays microcode.
Reviewed patois/genmc@f6f85d2
App · Tool:
serum-preset-packager reads and writes Serum 2 preset files using a format the author reverse engineered.
Binary · Tool:
OpenJOC decodes and inspects E-AC-3 JOC audio bitstreams in Rust.
Reviewed chyinan/OpenJOC@e3e330a
Binary · Tool:
Felix is an Atari Lynx emulator with facilities for analysing software running inside it.
Reviewed laoo/Felix@f5a9cda
App · Tool:
aftereffects-aep-parser is a Go library for inspecting Adobe After Effects AEP project files.
App · Tool:
OpenQBW reverse engineers the QuickBooks Desktop .qbw company-file format and provides a Rust reader, CLI, Python bindings and a format specification.
Reviewed Sigilweaver/OpenQBW@68f91eb
Binary · Tool:
WinTTD exposes recovered WinDBG virtual CPU structures and callback layouts for instruction instrumentation.
Reviewed Colton1skees/WinTTD@43e871e
App · Tool:
pyhwp parses HWP Document Format v5 files and extracts their internal streams.
Reviewed mete0r/pyhwp@83239f0
Binary · Tool:
apfs-fuse examines Apple File System volume structures with apfs-dump and apfs-dump-quick, and mounts APFS volumes through a read-only FUSE driver.
Reviewed sgan81/apfs-fuse@66b86bd
App · Tool:
Crate Digger parses rekordbox export databases and track-analysis files with Kaitai Struct definitions and generated Java classes.
Reviewed Deep-Symmetry/crate-digger@7c9d535
App · Tool:
MDB Tools reads Microsoft Access MDB files and documents the Jet3 and Jet4 file format.
Reviewed mdbtools/mdbtools@96d6880
App · Tool:
ExtractAltiumSTEPModels is a Python proof of concept for recovering STEP component models embedded in Altium .PcbDoc PCB project files.
Game · Tool:
Rustation embeds a GDB remote debugger in a Rust PlayStation emulator core for inspecting running game code.
Reviewed simias/rustation@5e650b9
App · Tool:
Unshield lists and extracts files from InstallShield cabinet files through a C tool and library.
Reviewed twogood/unshield@c602af6
Binary · Tool:
XBEpy is a Python library for inspecting Microsoft Xbox executable files.
Reviewed LoveMHz/XBEpy@87568a3
App · Tool:
libagdb analyzes the Windows SuperFetch database format and provides C library code and tools for accessing it.
Reviewed libyal/libagdb@2859755
Binary · Tool:
StringsX64DbgNext scans the main module of an x64dbg debuggee for printable ANSI and UTF-16LE strings.
Reviewed Orohal/stringsx64dbg-next@5b3b28d
App · Tool:
gho reads, extracts, creates and modifies Norton Ghost GHO disk images through a Go library and CLI.
Reviewed nyarime/gho@40af0e8
App · Tool:
tps-parse reads Clarion TPS database files using a Java parser built from reverse-engineered file structures.
Reviewed ctrl-alt-dev/tps-parse@9ebe03d
App · Tool:
OpenOrCadParser parses Cadence OrCAD Capture binary schematics and symbol libraries with a C++20 library and CLI.
Reviewed Werni2A/OpenOrCadParser@be0a83a
Game · Tool:
xvdtool is a C# command-line utility for inspecting Xbox One XVD and XVC packages.
Reviewed emoose/xvdtool@6fc2886
Binary · Tool:
MartyPC emulates early IBM PCs and provides disassembly, CPU and memory inspection, breakpoints, and instruction or cycle-based logging for 8088 programs.
Reviewed dbalsom/martypc@05c0d08
App · Tool:
ptformat decrypts and parses Pro Tools session files to extract audio sources, regions and tracks, plus MIDI chunks, regions, tracks and notes.
Reviewed zamaudio/ptformat@af15ee9
App · Tool:
LibreDWG reads and writes AutoCAD DWG documents through a C library and command-line tools.
Reviewed LibreDWG/libredwg@c184dd0
App · Tool:
libsai documents and implements access to PaintTool SAI .sai artwork files.
Reviewed Wunkolo/libsai@f07ee88
Binary · Tool:
Hiew edits files in text, hex and disassembler modes and supports x86-64 assembly and disassembly.
Reviewed hiew.ru
App · Tool:
OpenSKP parses, writes, and converts SketchUp SKP files using independently implemented Python, TypeScript, .NET, Dart, and C++ libraries.
Reviewed iamahsanmehmood/openskp@52980b7
App · Tool:
rekordcrate is a Rust parser and command-line inspector for Pioneer Rekordbox exports used by CDJ and XDJ players.
Reviewed Holzhaus/rekordcrate@68cd702
Binary · Tool:
Dislocker inspects and decrypts BitLocker encrypted volumes on Linux and macOS.
Reviewed Aorimn/dislocker@21ef6e5
App · Tool:
libflp is a C++ library for parsing FL Studio .flp project files.
Reviewed codecat/libflp@349d06b
Binary · Tool:
innodb_ruby parses InnoDB file formats to expose database storage structures for investigation and teaching.
Reviewed jeremycole/innodb_ruby@7ad09f9