Star on GitHubStar2.4k stars

Curated reverse engineering resources

5,191

Filters

Kind
Category
Show all 24

Showing 3,101–3,200 of 5,191

Evidence class
  • C0full software reconstruction
  • C1partial scope or analysis entry
  • C2code & docs, no demo or download
  • C3notes only
  • ?Source unavailable or unreadable at review time
How classes are assigned
  • Games

    2,976
  • Game · Integration:

    Cheat Engine MCP BridgeC2

    Connects MCP clients to Cheat Engine through a Lua bridge script and a Python MCP server, so an agent can inspect a process the user runs under Cheat Engine: memory reads and value scans, pointer-chain resolution, structure dissection, RTTI class names, disassembly, cross-references and hardware or DBVM breakpoints.

    • Game
    • Binary
    Reviewed miscusi-peek/cheatengine-mcp-bridge@6bd7ce9

  • Game · Project:

    PSP Web RecompC2

    Translate PSP MIPS executables into C++ and WebAssembly, backed by a PSP high-level emulation runtime and WebGL2 renderer.

    • Game
    • Website

    Reviewed snuri00/psp-web-recomp@37826ab

  • Game · Project:

    OpenRS2C2

    OpenRS2 develops a server compatible with RuneScape client build 550 and associated client-analysis tools.

    • Game

    Reviewed openrs2/openrs2@50175bc

  • Apps

    370
  • App · Tool:

    FridaC2

    Dynamic instrumentation toolkit for observing and scripting the behavior of live native and managed processes.

    • App
    • Game

    Reviewed frida/frida@e598d05

  • App · Tool:

    JADXC1

    Dex-to-Java decompiler with CLI/GUI navigation, resource decoding and cross-reference search for Android packages.

    Demo screenshot from the project's public documentation
    • App

    Reviewed skylot/jadx@c4c45fd

  • App · Tool:

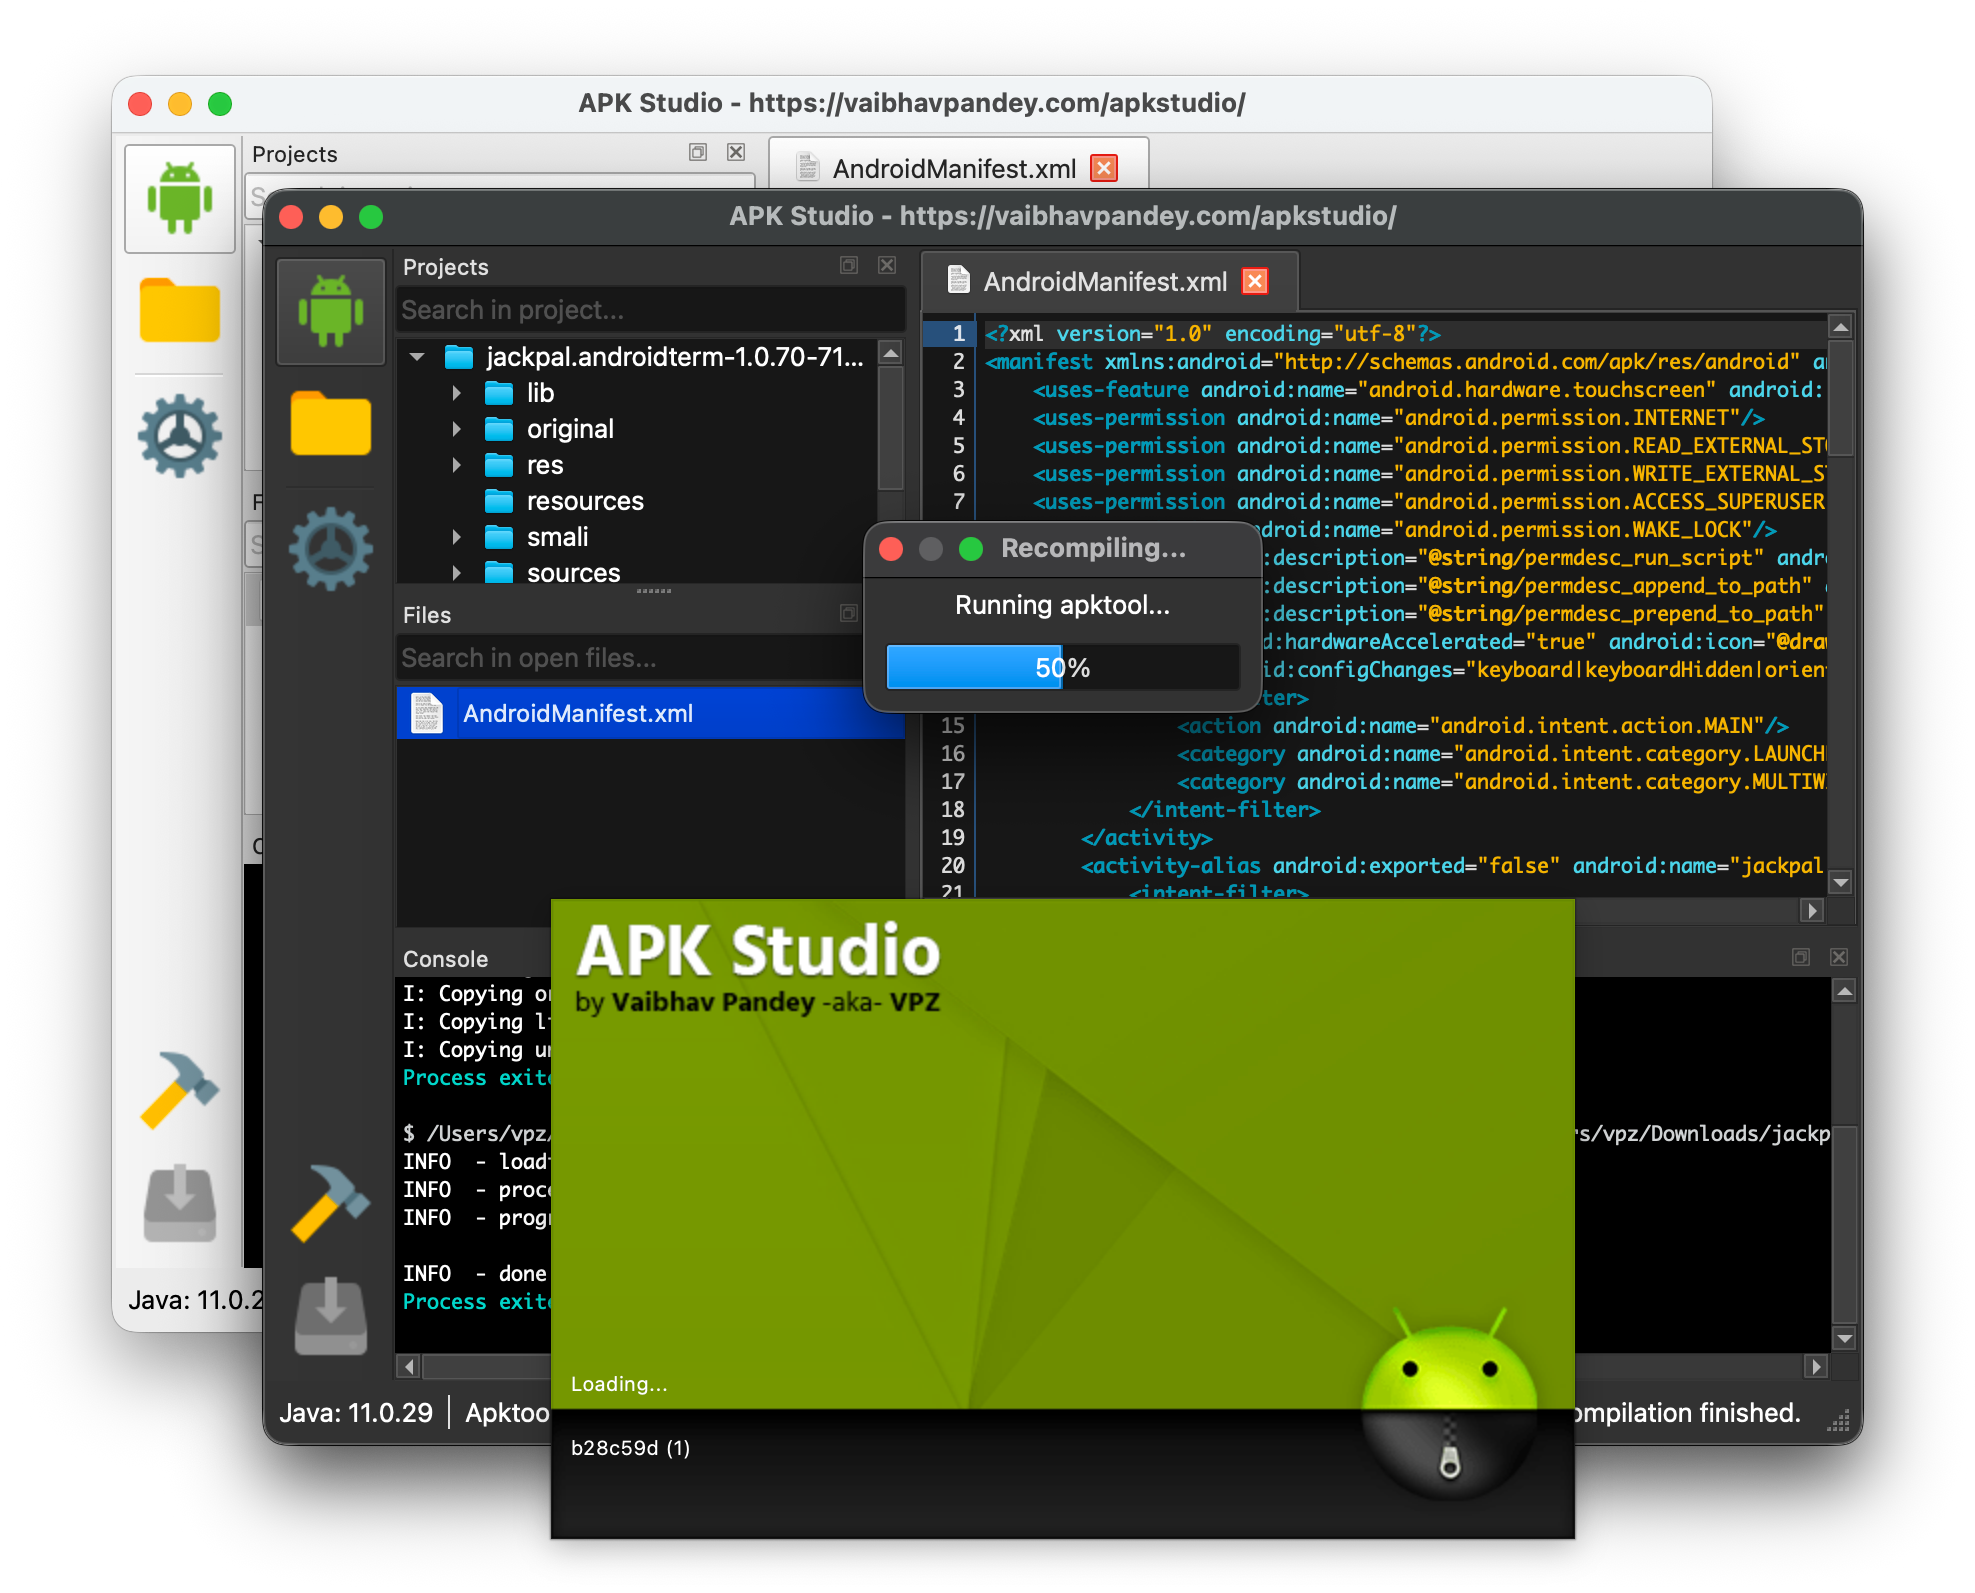
    ApktoolC2

    Decodes Android resources and smali into a project-like tree and can rebuild modified packages.

    • App

    Reviewed iBotPeaches/Apktool@0312d21

  • App · Tool:

    AndroguardC2

    Python toolkit for APK/DEX metadata, bytecode and reference analysis; the v5 source branch also documents agent skills and MCP.

    • App

    Reviewed androguard/androguard@90e7b42

  • App · Tool:

    ILSpyC2

    .NET assembly browser and C# decompiler with whole-project export, metadata inspection and a scriptable command-line frontend.

    • App

    Reviewed icsharpcode/ILSpy@729b5dc

  • App · Tool:

    dnSpyExC1

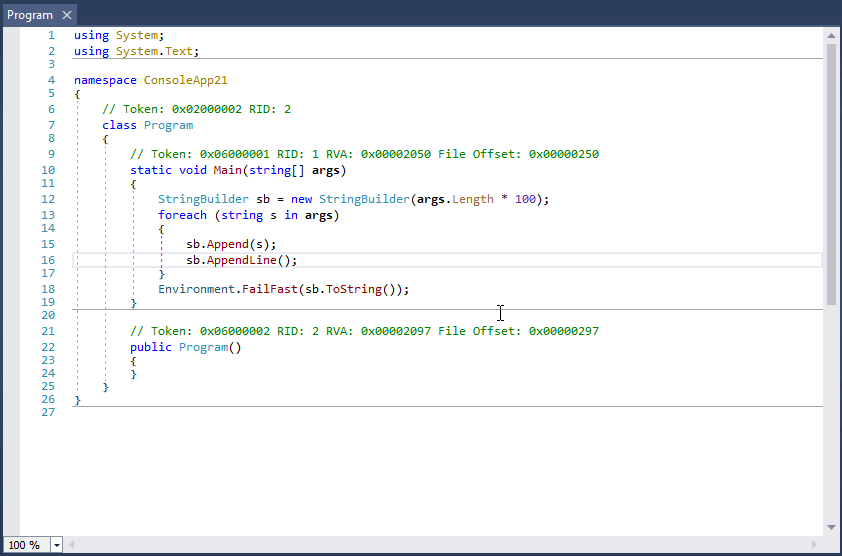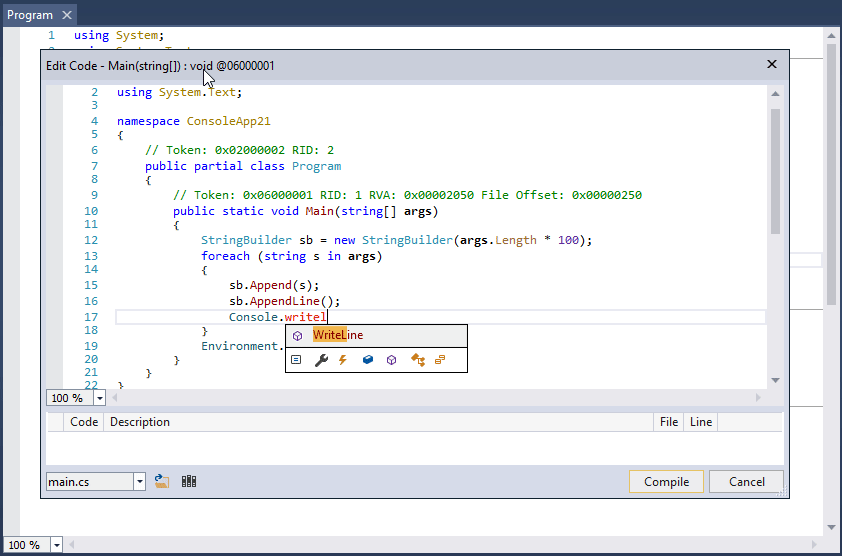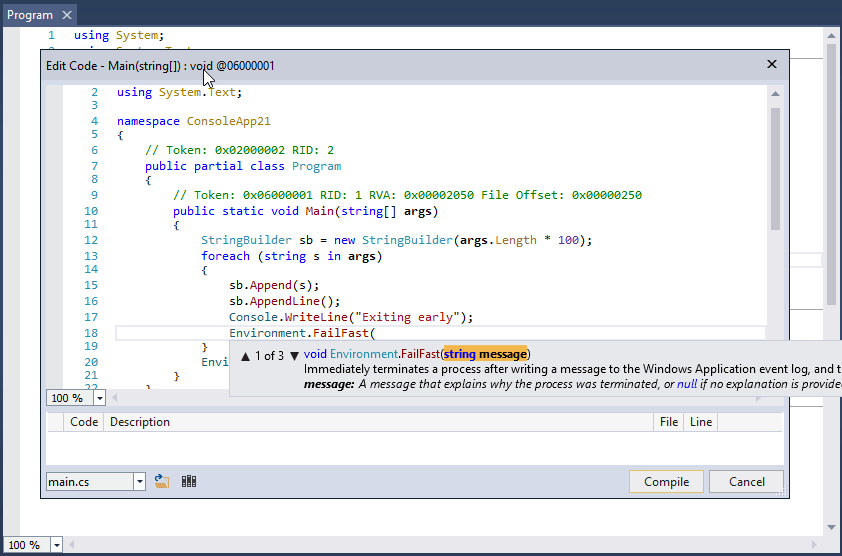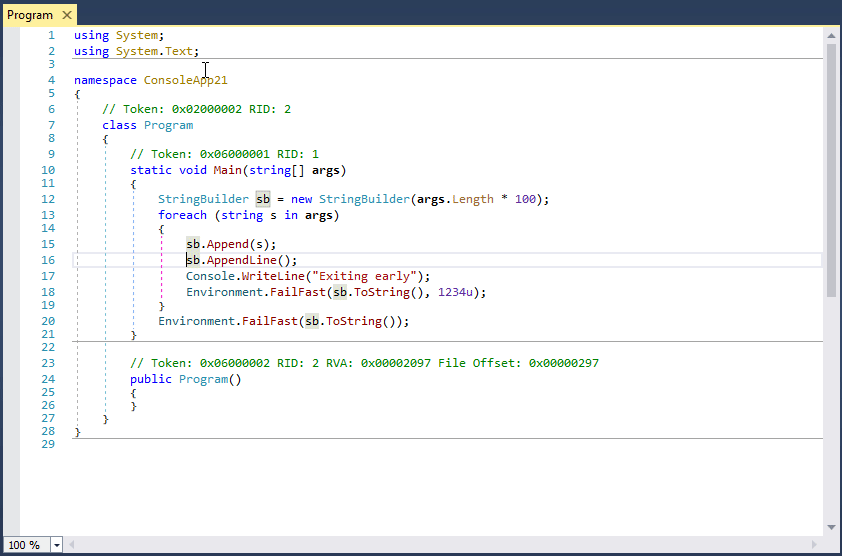
    Community continuation of dnSpy for debugging and editing .NET assemblies without the original source.

    Demo screenshot from the project's public documentation
    • App

    Reviewed dnSpyEx/dnSpy@de5a830

  • App · Tool:

    @electron/asarC2

    Electron's archive tool lists and extracts ASAR contents so packaged JavaScript and application assets can be inspected.

    • App
    • Website

    Reviewed electron/asar@01bc908

  • App · Tool:

    Mobile Security Framework (MobSF)C2

    Inspect mobile application packages with static analysis and supported-device dynamic testing, including runtime behavior and network traffic, through a web interface and APIs.

    • App

    Reviewed MobSF/docs@d3dc0f6

  • App · Tool:

    objectionC2

    Explore running Android and iOS apps with a Frida-backed command interface for inspecting app storage, memory, runtime objects, and instrumented behavior.

    • App

    Reviewed sensepost/objection@35c4e2c

  • App · Tool:

    GrapefruitC1

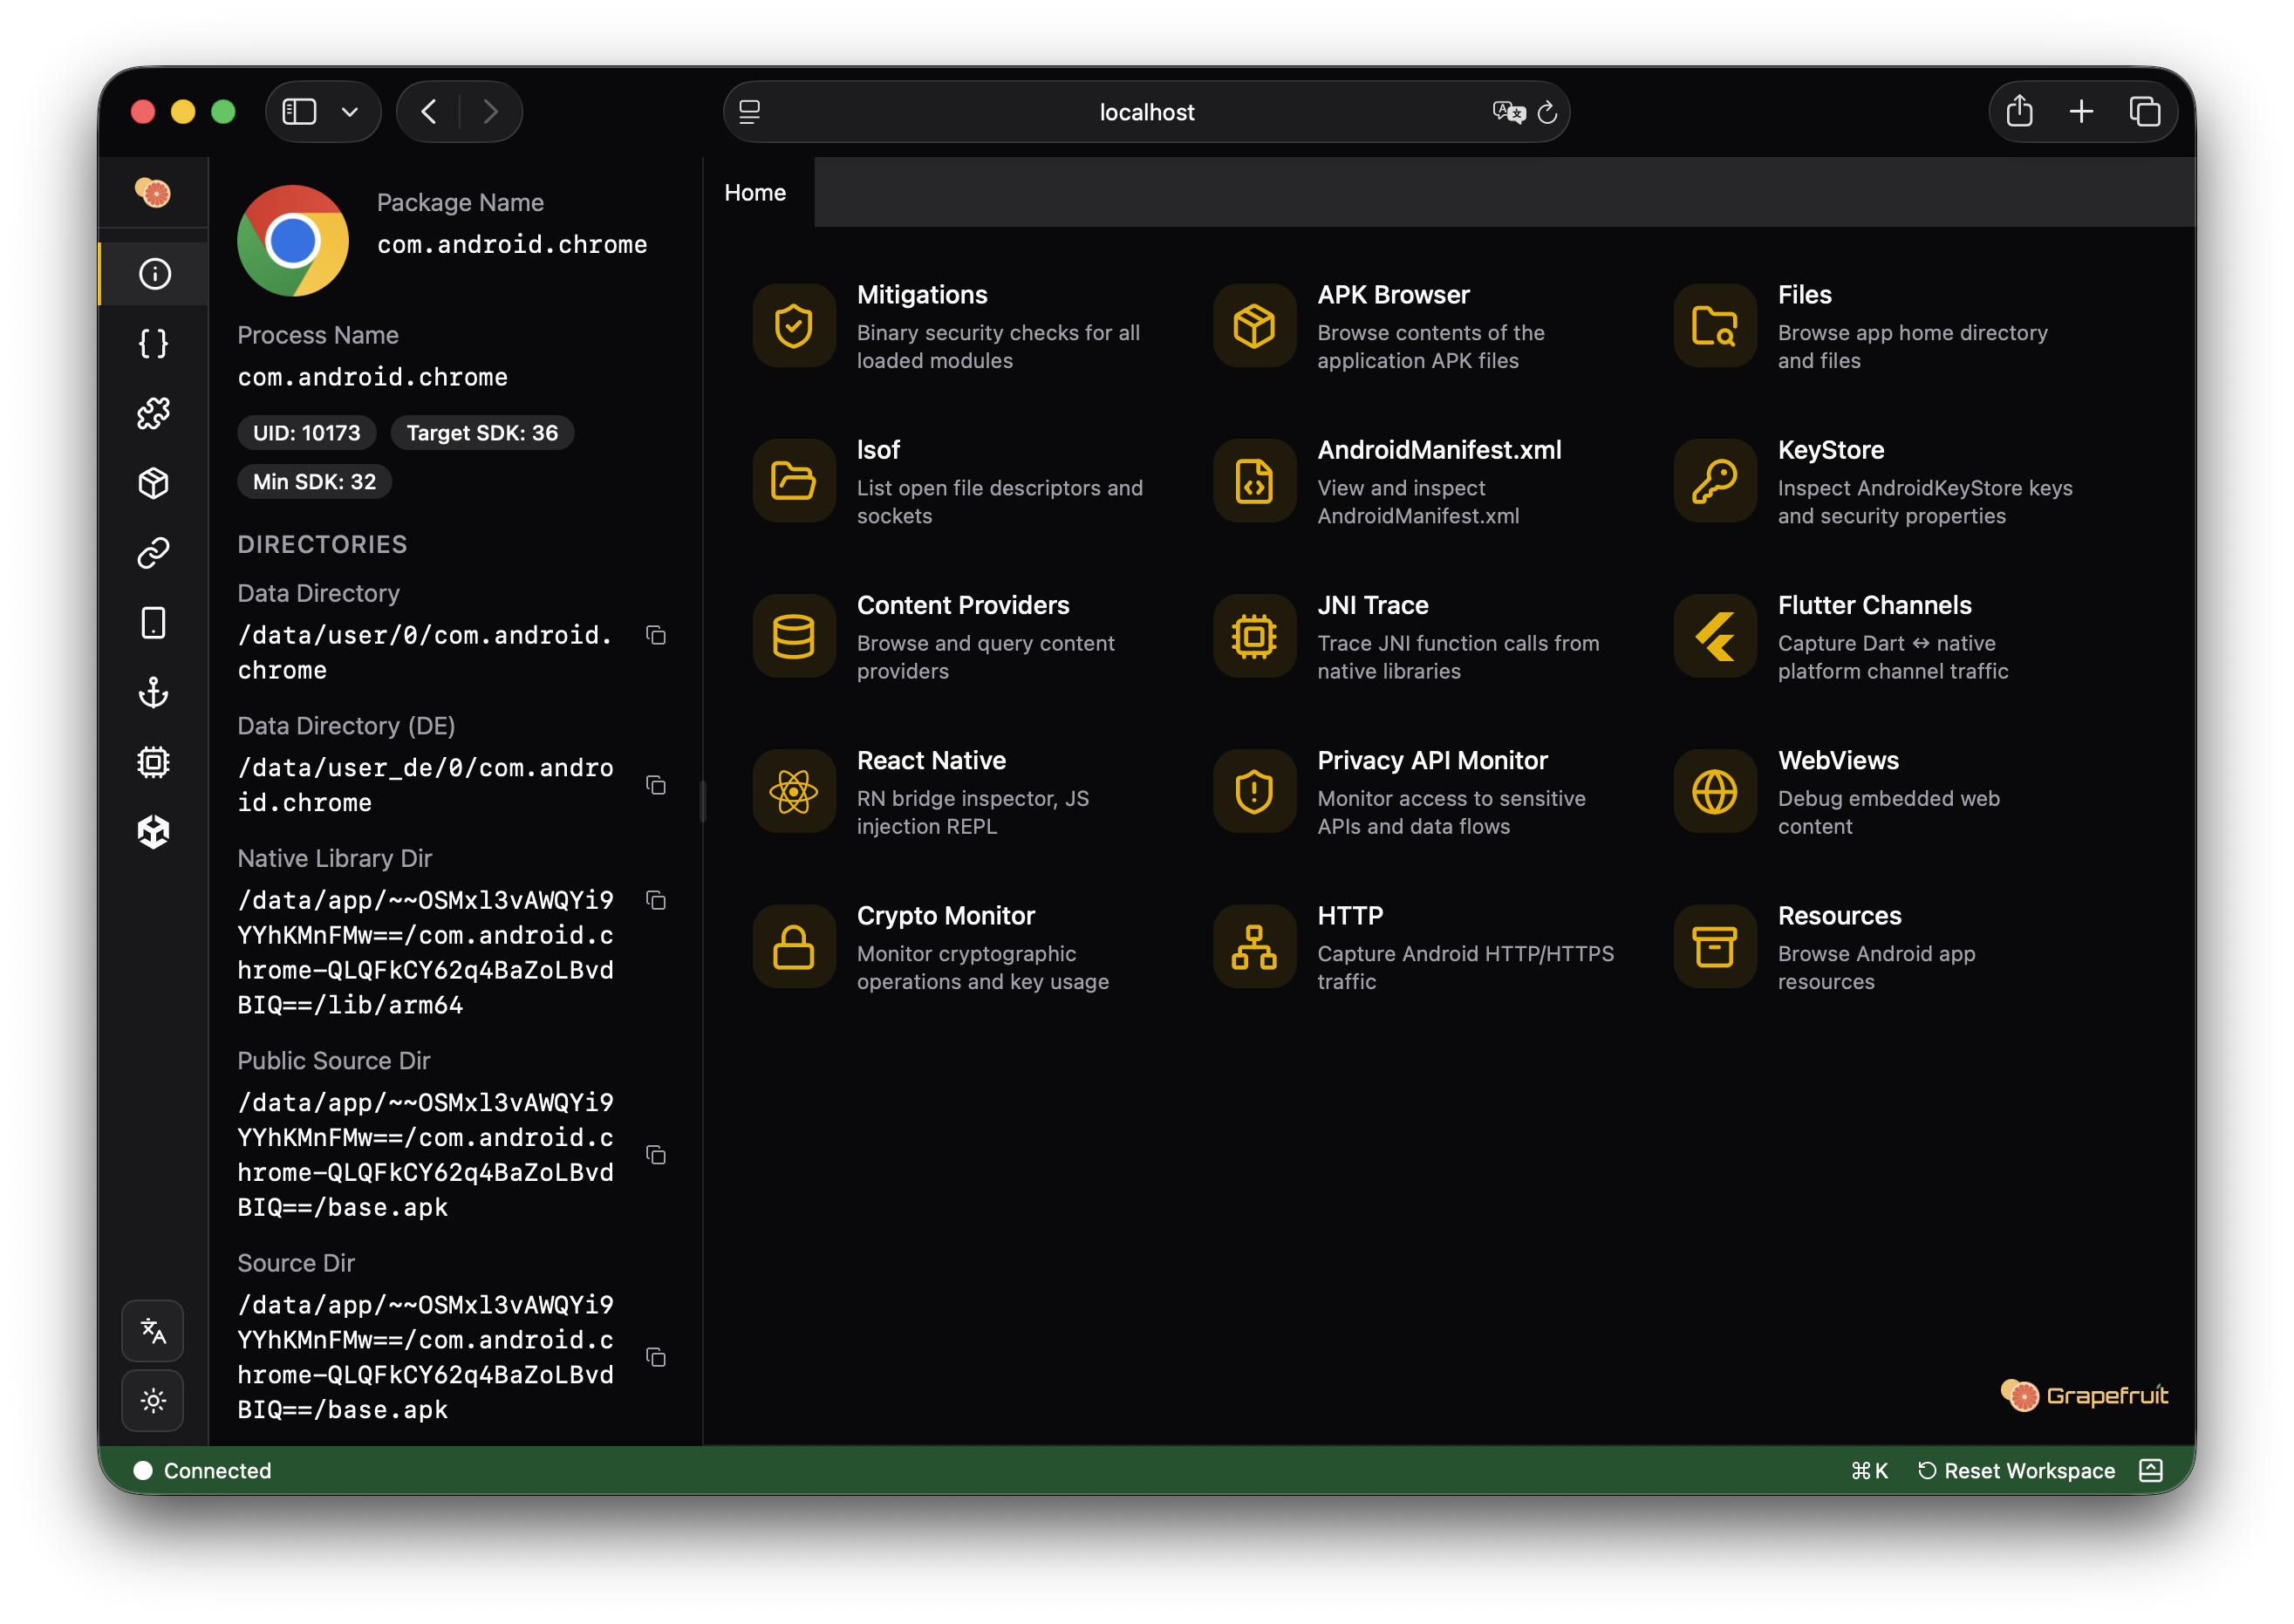
    Inspect and hook running iOS and Android apps from a Frida-based web interface, with method and crypto-API hooks, filesystem and SQLite browsers, iOS keychain and UI-hierarchy views, and HTTP capture from common networking libraries.

    Demo screenshot from the project's public documentation
    • App

    Reviewed ChiChou/grapefruit@b7176b4

  • App · Tool:

    BlutterC2

    Analyze Flutter Android ARM64 AOT binaries using the matching Dart runtime.

    • App
    • Binary
    Reviewed worawit/blutter@4a60ac6

  • App · Tool:

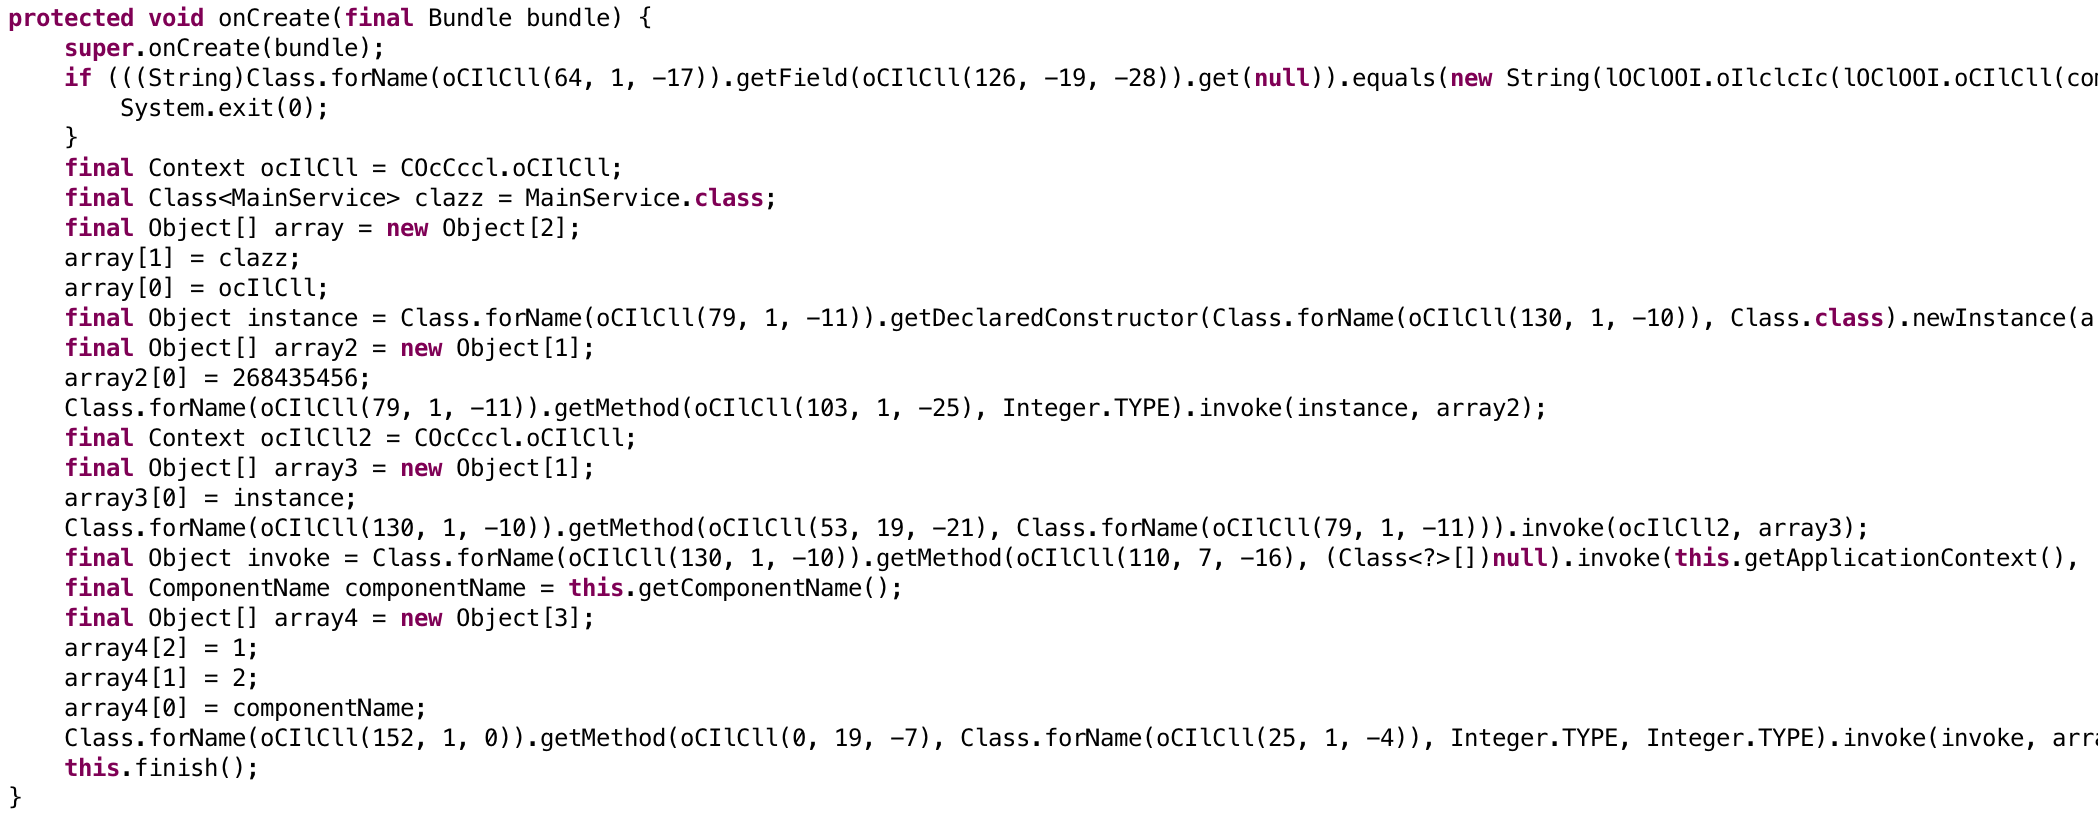
    RecafC1

    Inspect and modify compiled JVM applications with integrated decompilers, bytecode assembly, reference search, mappings and deobfuscation tools.

    Demo screenshot from the project's public documentation
    • App
    • Binary
    Reviewed Col-E/Recaf@7ce7b5d

  • App · Tool:

    nibkitC2

    Decode compiled iOS/macOS interface archives into object trees, Outlet/Action connections, custom classes and navigation relationships.

    • App

    Reviewed tokenbleed/nibkit@fcf4670

  • App · Tool:

    AOTopsyC1

    Statically inspect Flutter/Dart AOT libapp.so files to recover available metadata, class structures, call edges and pseudocode without embedding a Dart VM or compiling a matching SDK.

    Demo available · no screenshot
    • App
    • Binary
    Reviewed BroNils/aotopsy@01011df

  • App · Tool:

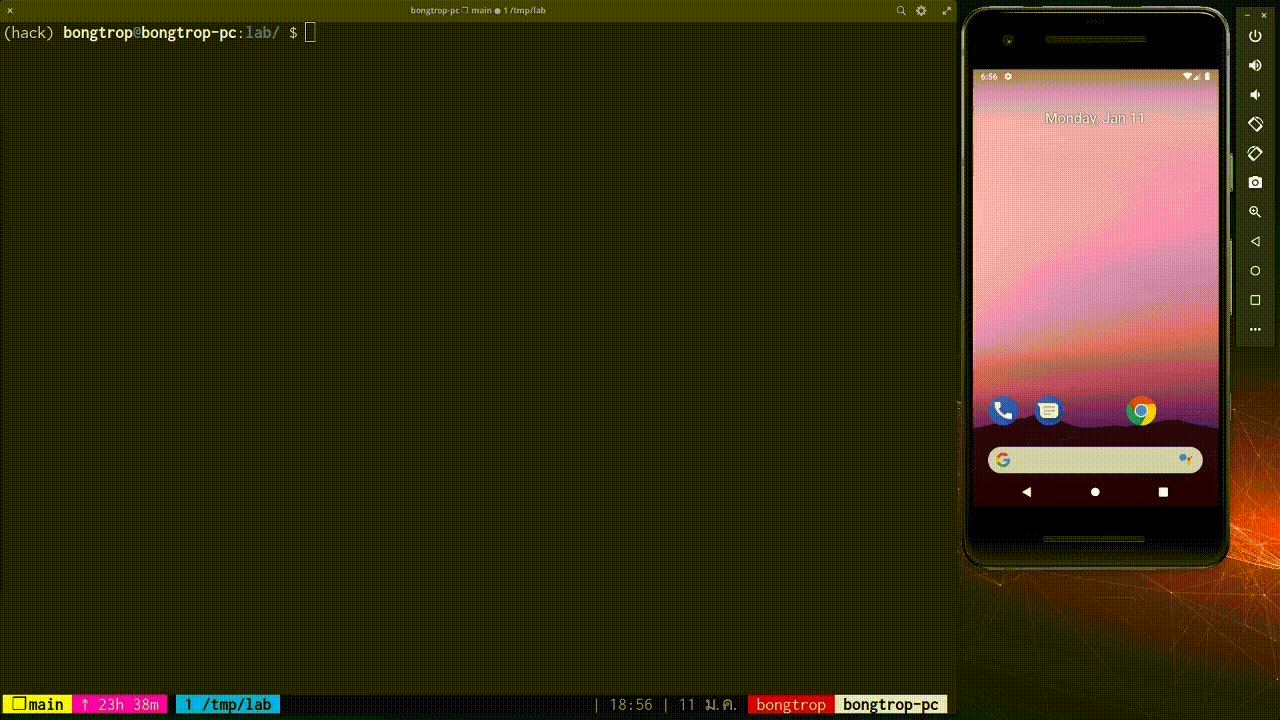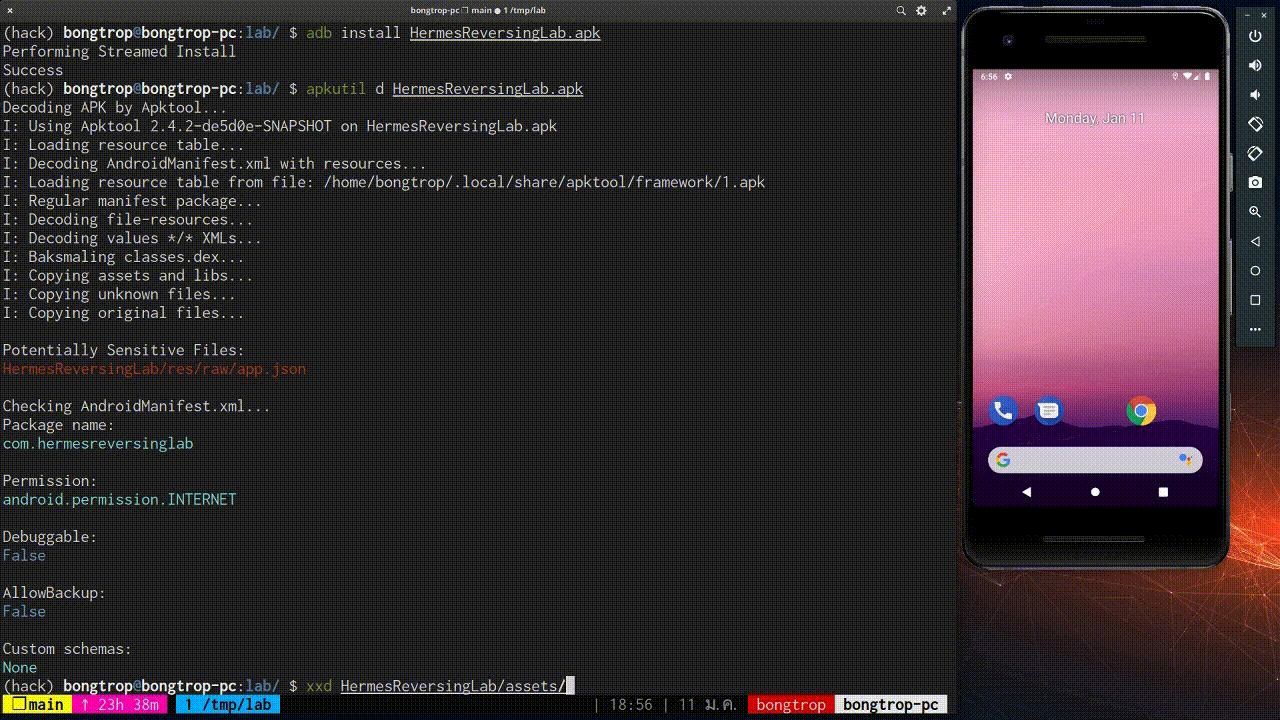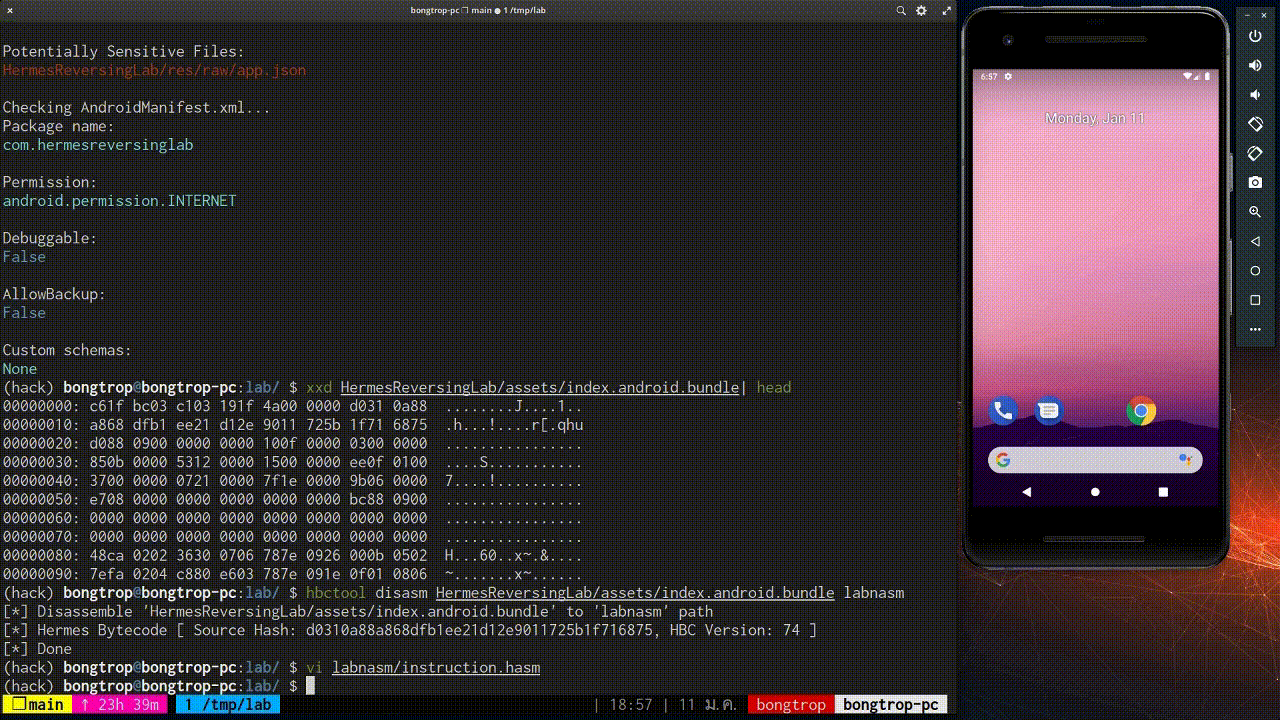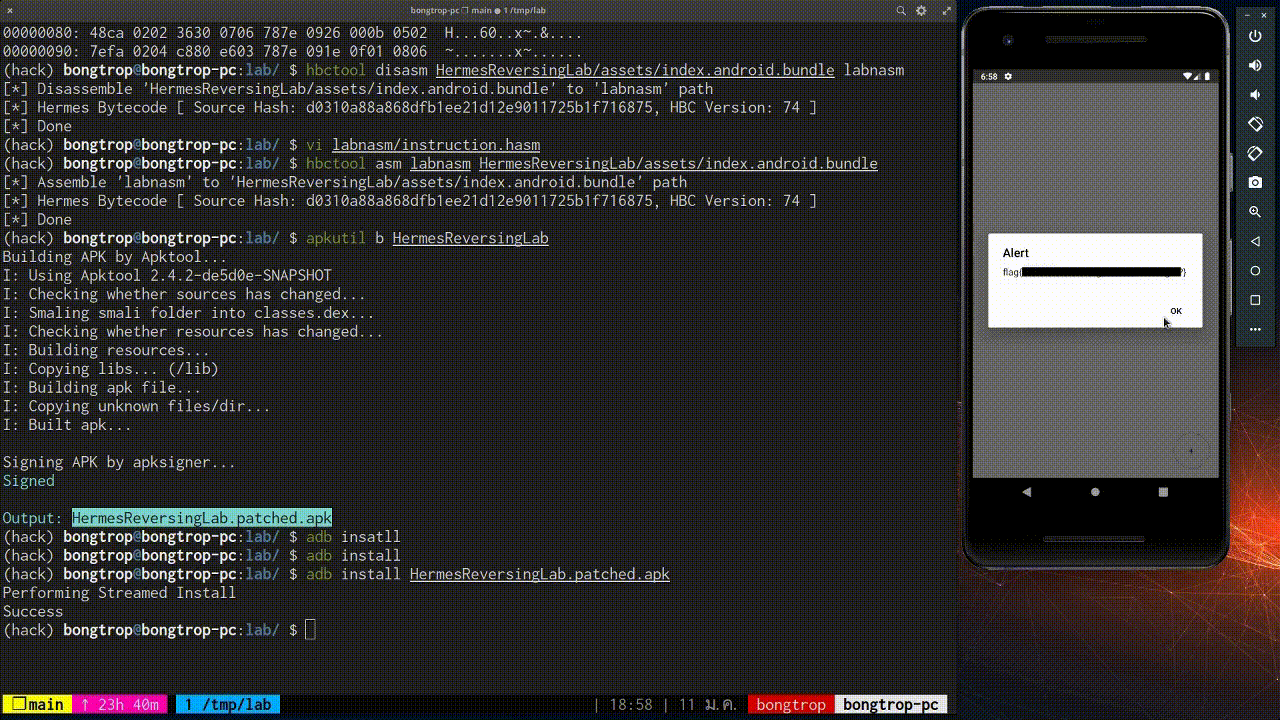
    hbctoolC1

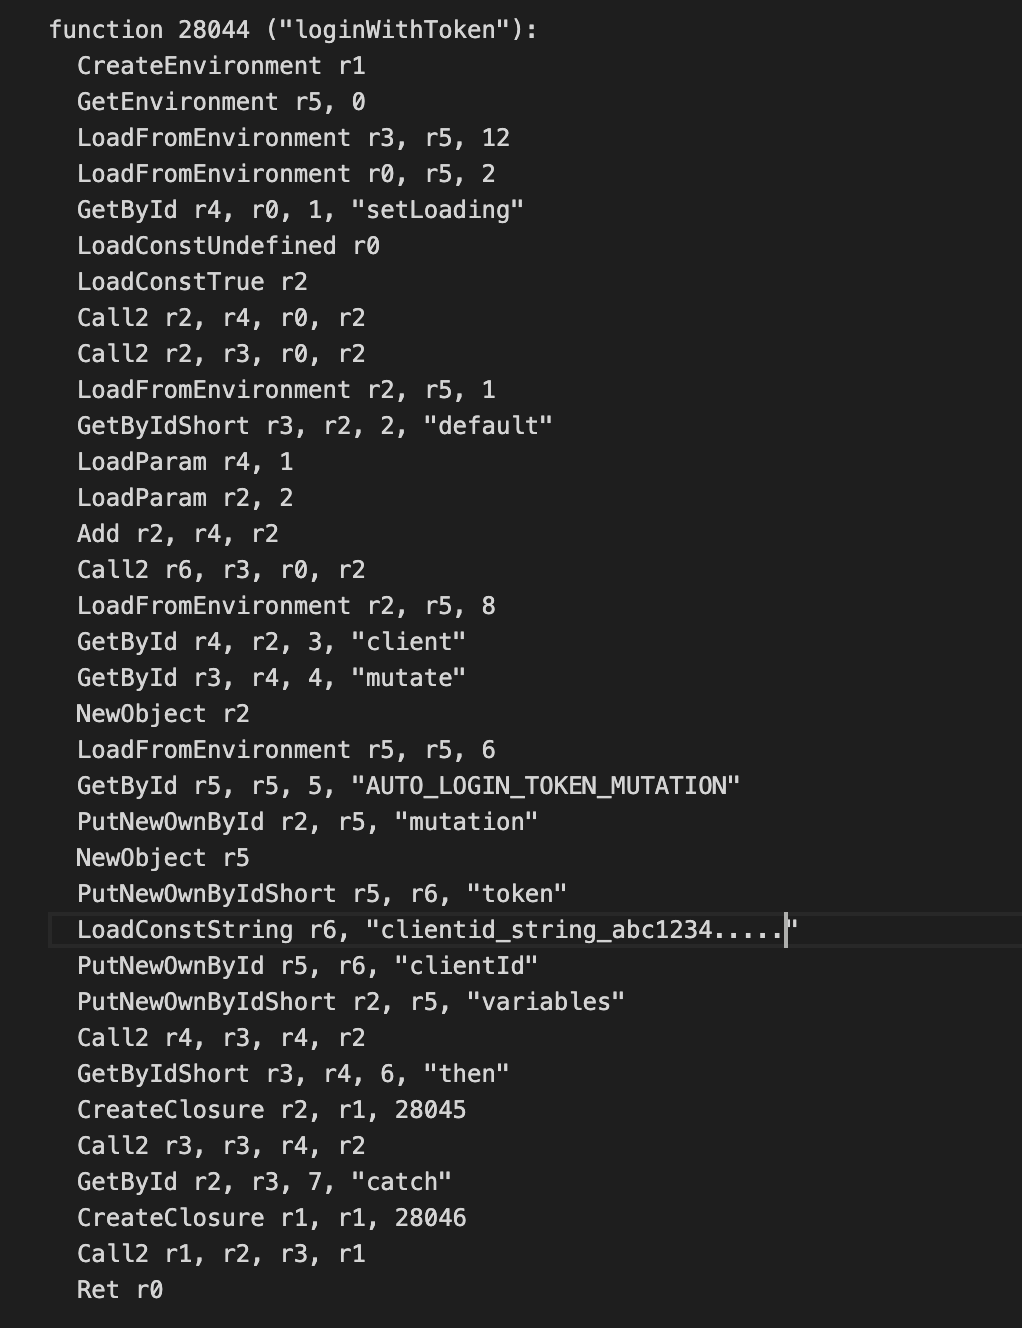
    Disassemble and reassemble supported React Native Hermes bytecode bundles through HASM files, enabling bytecode inspection and editing for the explicitly supported legacy HBC versions.

    Demo screenshot from the project's public documentation
    • App

    Reviewed bongtrop/hbctool@389b351

  • App · Tool:

    VineflowerC2

    Fernflower-derived decompiler for Java and other JVM languages that continues the ForgeFlower, Fabric and Quiltflower forks, focused on output quality and modern Java, including records, sealed classes, switch expressions and pattern matching through Java 21+.

    • App

    Reviewed Vineflower/vineflower@b827398

  • App · Tool:

    Droid ASCC2

    Python Android decompiler that answers queries directly against an APK instead of first unpacking and indexing it.

    • App

    Reviewed MG1937/ASC@60033d1

  • App · Tool:

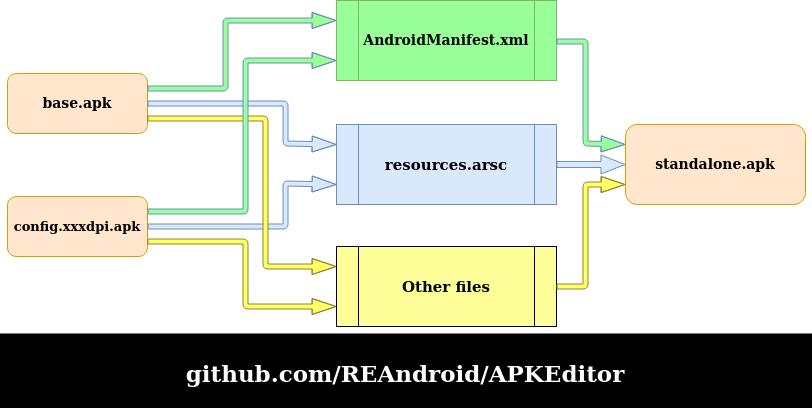
    APKEditorC1

    Command-line APK editor built on ARSCLib that decodes an APK's binary resources and DEX into editable JSON, XML or smali and rebuilds a package from them, independent of aapt and aapt2.

    Demo screenshot from the project's public documentation
    • App

    Reviewed REAndroid/APKEditor@5621fe6

  • App · Tool:

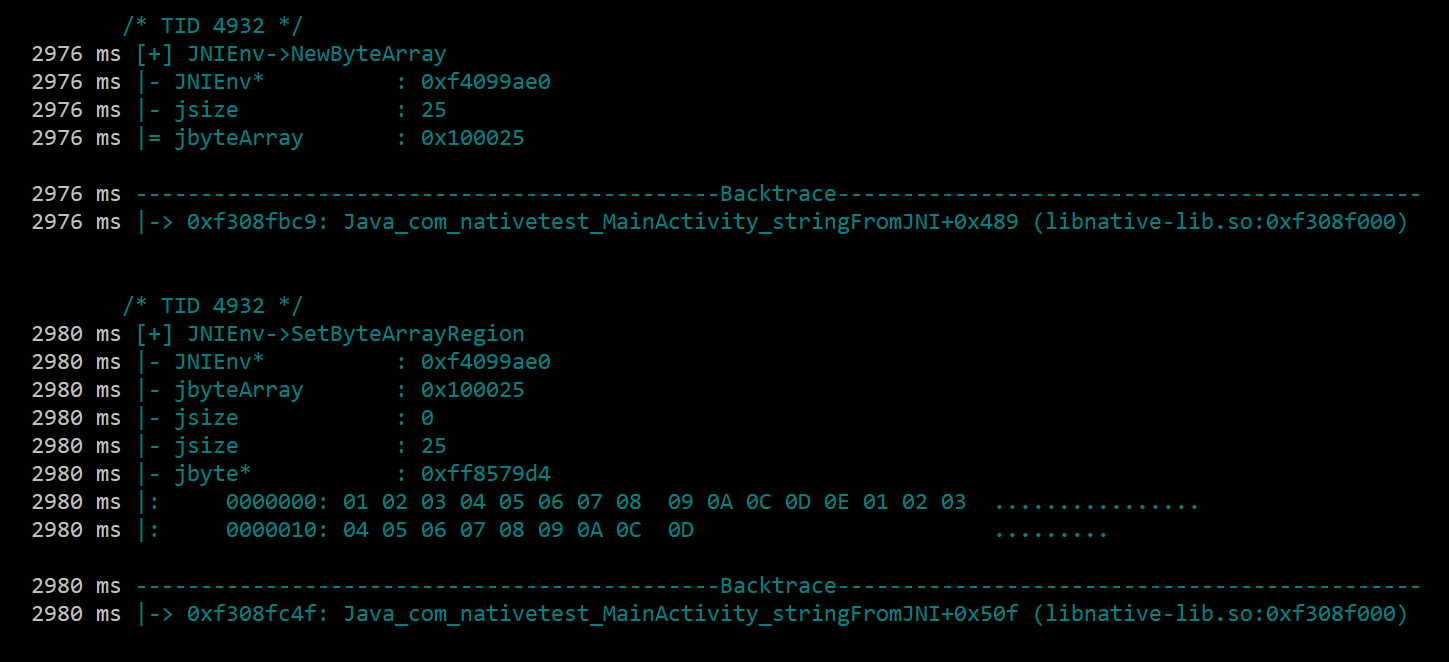
    jnitraceC1

    Frida-based dynamic-analysis tool that traces an Android app's use of the JNI API, similar to frida-trace or strace but for the Java Native Interface.

    Demo screenshot from the project's public documentation
    • App

    Reviewed chame1eon/jnitrace@5be47cb

  • App · Tool:

    AsmResolverC2

    C# library for reading, modifying and rebuilding Portable Executable files, covering both native Windows images and images with .NET metadata.

    • App
    • Binary

    Reviewed Washi1337/AsmResolver@0715000

  • App · Tool:

    CodemerxDecompileC2

    Cross-platform desktop .NET decompiler maintained by the original JustDecompile creators as a continuation of their JustDecompile Engine, built with Mono.Cecil and an Avalonia UI.

    • App

    Reviewed codemerx/CodemerxDecompile@9ada306

  • App · Tool:

    wxapkgC1

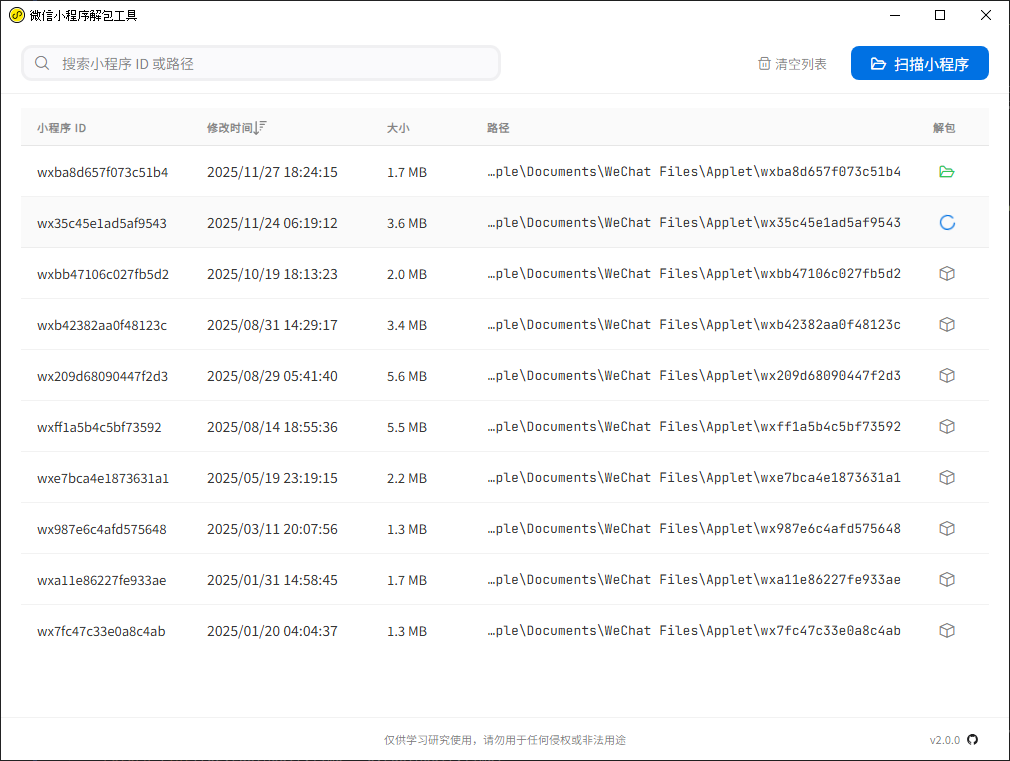
    Desktop GUI for Windows and macOS, built with Wails, that unpacks WeChat mini-program .wxapkg packages for study.

    Demo screenshot from the project's public documentation
    • App

    Reviewed wux1an/wxapkg@bae9b0f

  • App · Tool:

    React Native DecompilerC1

    Alpha-stage Node.js CLI that splits a React Native JavaScript bundle (index.android.bundle or main.jsbundle), an unbundled js-modules folder, or Webpack entrypoint and chunk bundles into one readable file per module.

    Demo available · no screenshot
    • App

    Reviewed numandev1/react-native-decompiler@77c7b94

  • App · Tool:

    hermes-decompC1

    Rust decompiler and analysis toolkit for Hermes bytecode (.hbc), the compiled form React Native apps ship for the Hermes engine; the README lists HBC versions 40 to 99.

    Demo screenshot from the project's public documentation
    • App

    Reviewed SymbioticSec/hermes-decomp@ad4c924

  • App · Tool:

    MEDUSAC2

    Modular Frida-based framework for runtime analysis of Android and iOS apps the analyst is authorized to test.

    • App

    Reviewed Ch0pin/medusa@a7bd929

  • App · Tool:

    apk-mitmC2

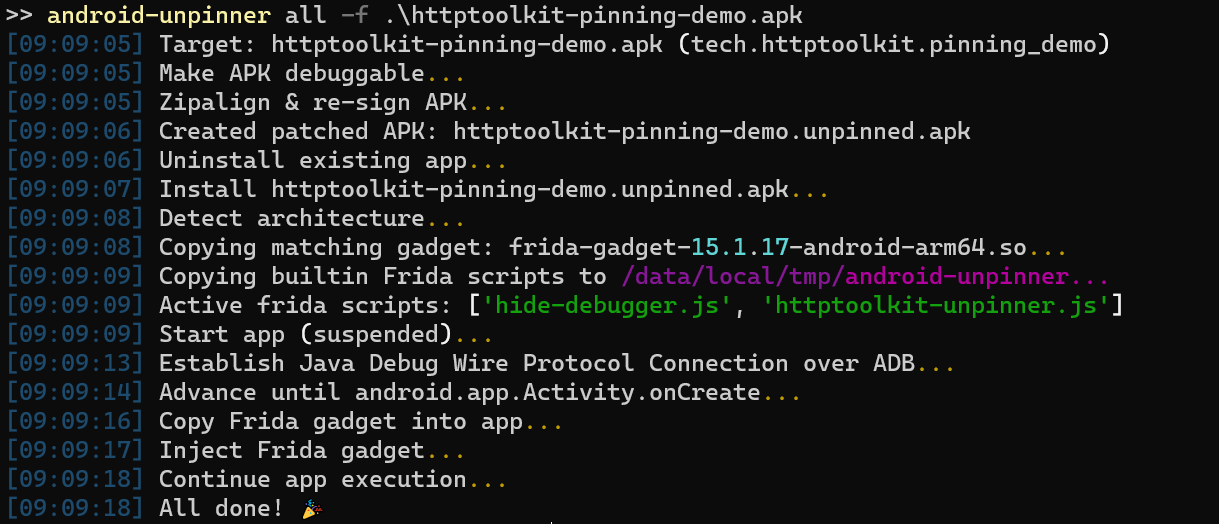
    Command-line tool that prepares an Android APK you own or are authorized to test for HTTPS traffic inspection.

    • App
    • Protocol

    Reviewed niklashigi/apk-mitm@5a96363

  • App · Tool:

    ddcC2

    Rust decompiler that turns Android DEX bytecode, versions 035 to 041, from APKs, multi-dex apps and XAPK/APKS/APKM containers into Java, folding lambdas and string concatenation back into Java syntax and giving locals jadx-style names.

    • App

    Reviewed ejfkdev/ddc@e240550

  • App · Tool:

    SimplifyC1

    Generic Android deobfuscator built on smalivm, a sandboxed Dalvik virtual machine that executes each method and records every possible register and class value along all execution paths, taking both branches when a value such as file or network input is unknown.

    Demo screenshot from the project's public documentation
    • App

    Reviewed CalebFenton/simplify@29fb25d

  • App · Tool:

    APKLabC2

    VS Code extension that turns the editor into an Android reverse-engineering workbench around Apktool, Jadx, smali-lsp and uber-apk-signer.

    • App

    Reviewed APKLab/APKLab@6ae69b1

  • App · Tool:

    FernflowerC2

    JetBrains' analytical decompiler that turns Java class files back into Java source; IntelliJ IDEA bundles it to show code when debugging or browsing class files.

    • App

    Reviewed JetBrains/fernflower@924b60f

  • App · Tool:

    Bytecode ViewerC1

    Desktop suite for inspecting compiled Java and Android programs: drop in a class, JAR, WAR, APK, DEX, XAPK or APKM file to browse its classes and resources, with up to three decompiler or disassembler views side by side.

    Demo screenshot from the project's public documentation
    • App

    Reviewed Konloch/bytecode-viewer@31430e0

  • App · Tool:

    Logic-LensC2

    Experimental JavaScript source-analysis toolkit that classifies AST-token sequences into configured formula families after local training, and produces heuristic structure, call-graph and intent reports.

    • App

    Reviewed Abdoulrazack1/Logic-Lens@bb15aab

  • App · Tool:

    abc-decompilerC1

    Decompiler for HarmonyOS Ark bytecode (.abc), the format HarmonyOS app packages carry in modules.abc, built by adapting the jadx decompiler and reading files through a patched copy of the abcde library.

    Demo screenshot from the project's public documentation
    • App

    Reviewed ohos-decompiler/abc-decompiler@427c4cd

  • App · Tool:

    slicerC2

    Browser-based Java reverse-engineering tool that loads class files and JAR/ZIP archives and disassembles or decompiles them with Vineflower (the default), CFR, Procyon or JASM, compiled to run in the browser, next to its own bytecode disassembler.

    • App

    Reviewed katana-project/slicer@1881aae

  • App · Tool:

    dex2jarC2

    Java toolkit that converts Android DEX bytecode, including DEX inside APKs, into JVM .class files packed as a jar for Java decompilers and bytecode tools.

    • App

    Reviewed pxb1988/dex2jar@b5bda4f

  • App · Tool:

    apk.shC2

    Bash script that automates repetitive Android app analysis chores around apktool: pulling an installed package from a device or emulator, decoding resources and disassembling dex code, and rebuilding the decoded directory into an APK.

    • App

    Reviewed ax/apk.sh@2a1ed25

  • App · Tool:

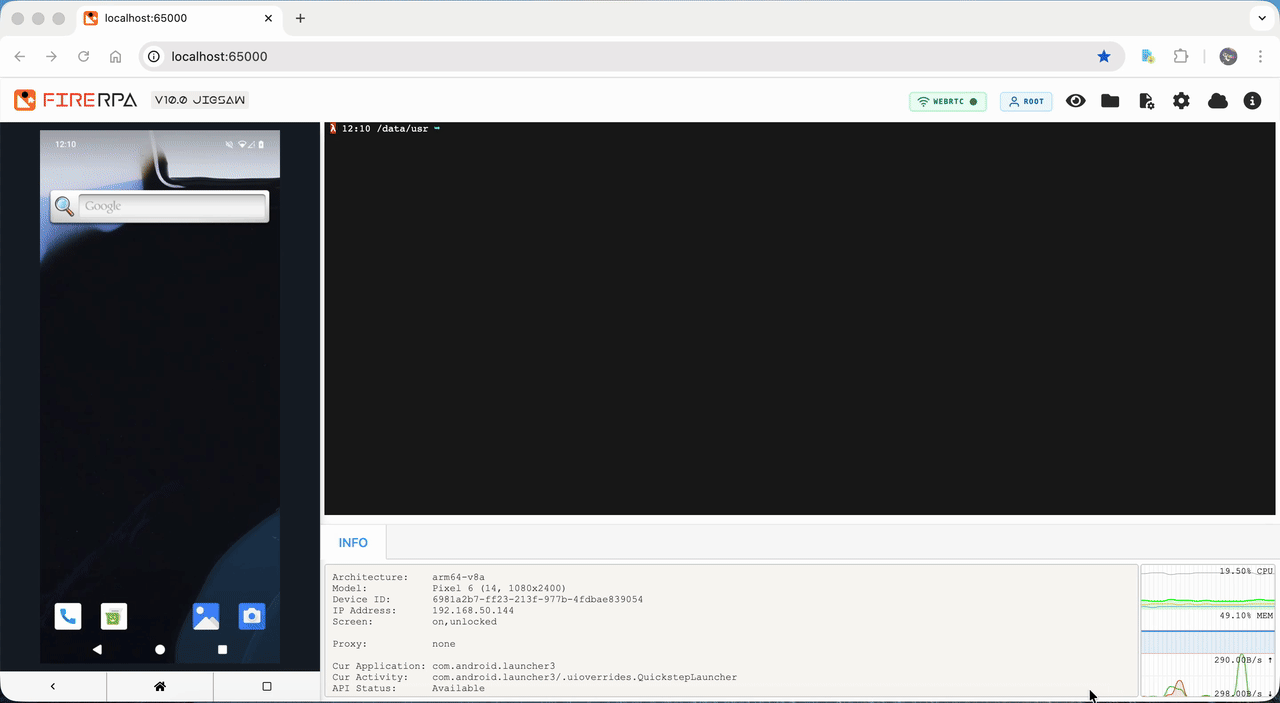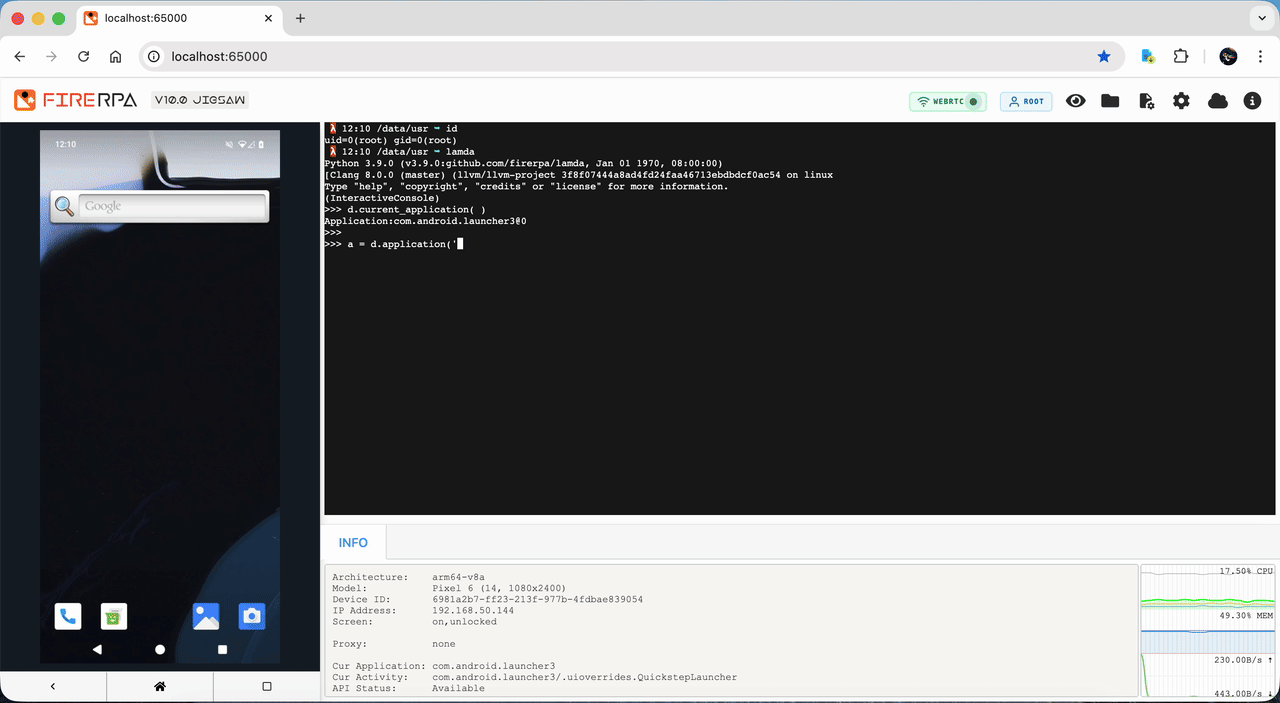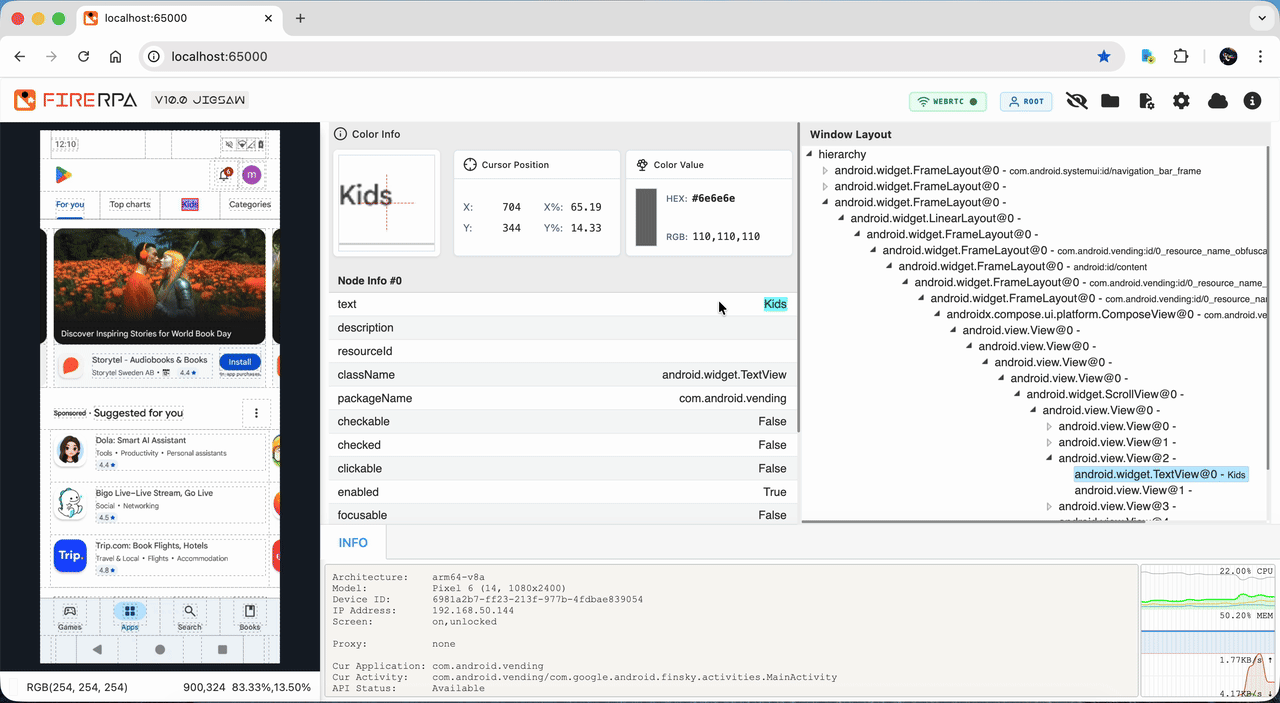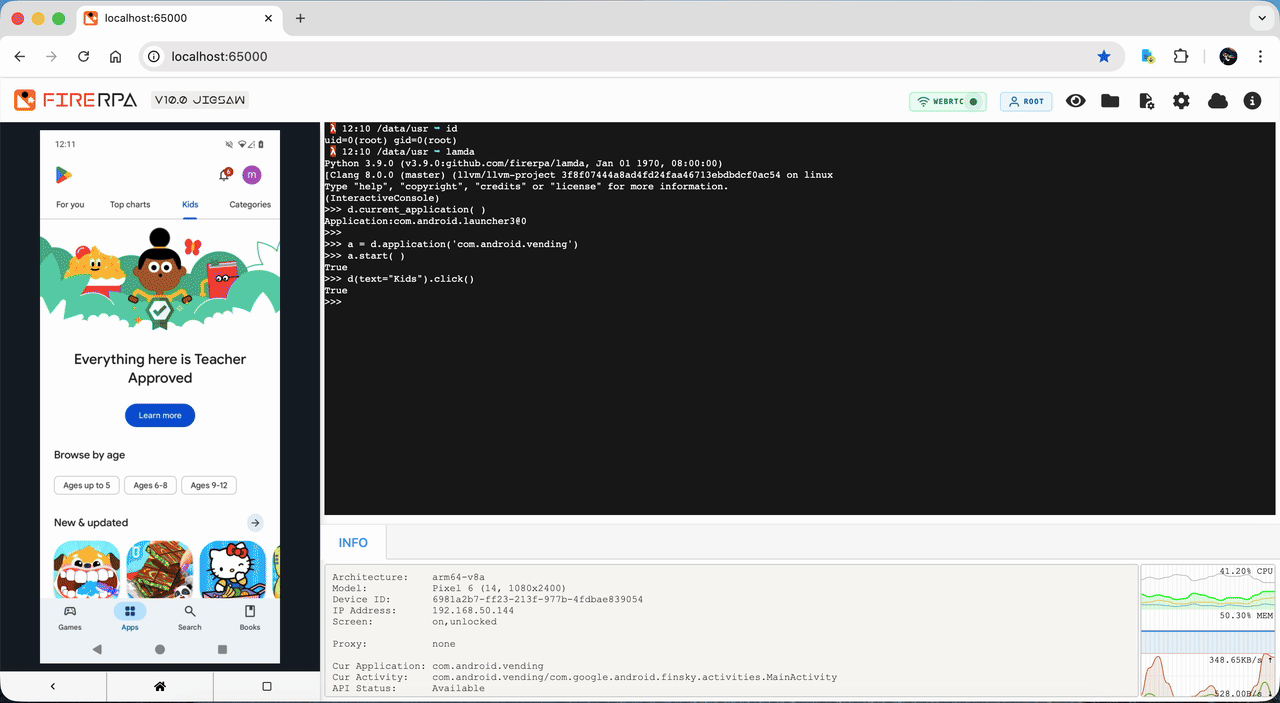
    FIRERPA (lamda)C1

    Client/server Android automation and dynamic-analysis platform for devices the analyst is authorized to test.

    Demo screenshot from the project's public documentation
    • App

    Reviewed firerpa/lamda@a980a38

  • App · Tool:

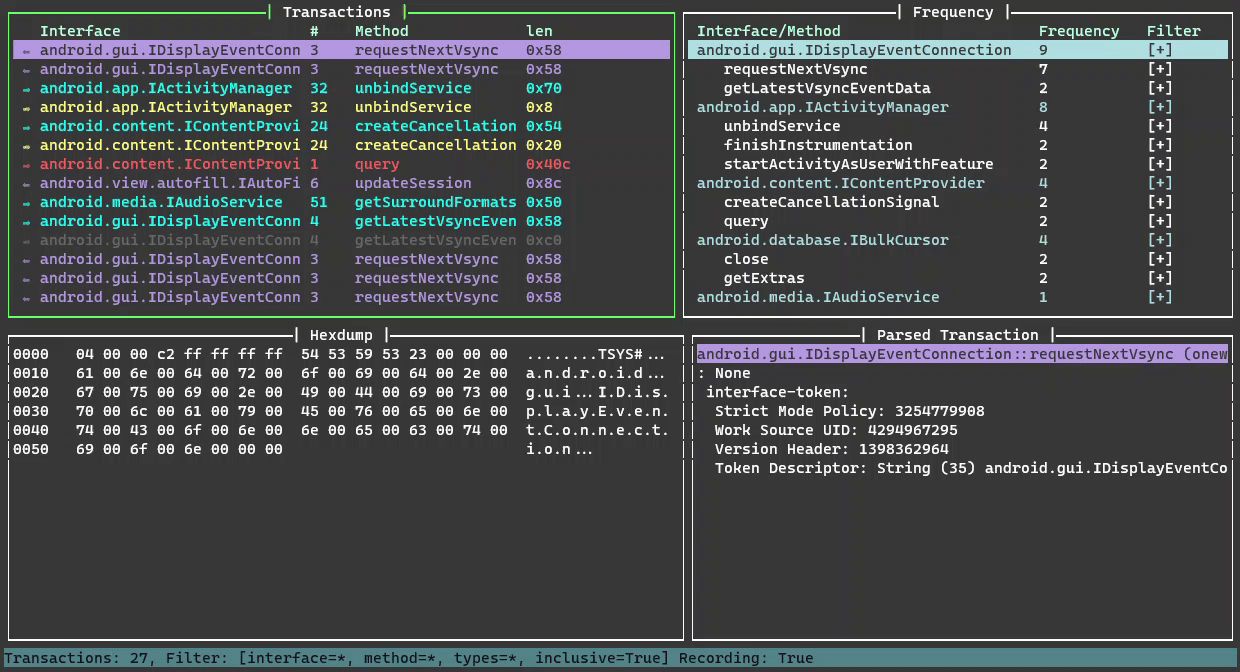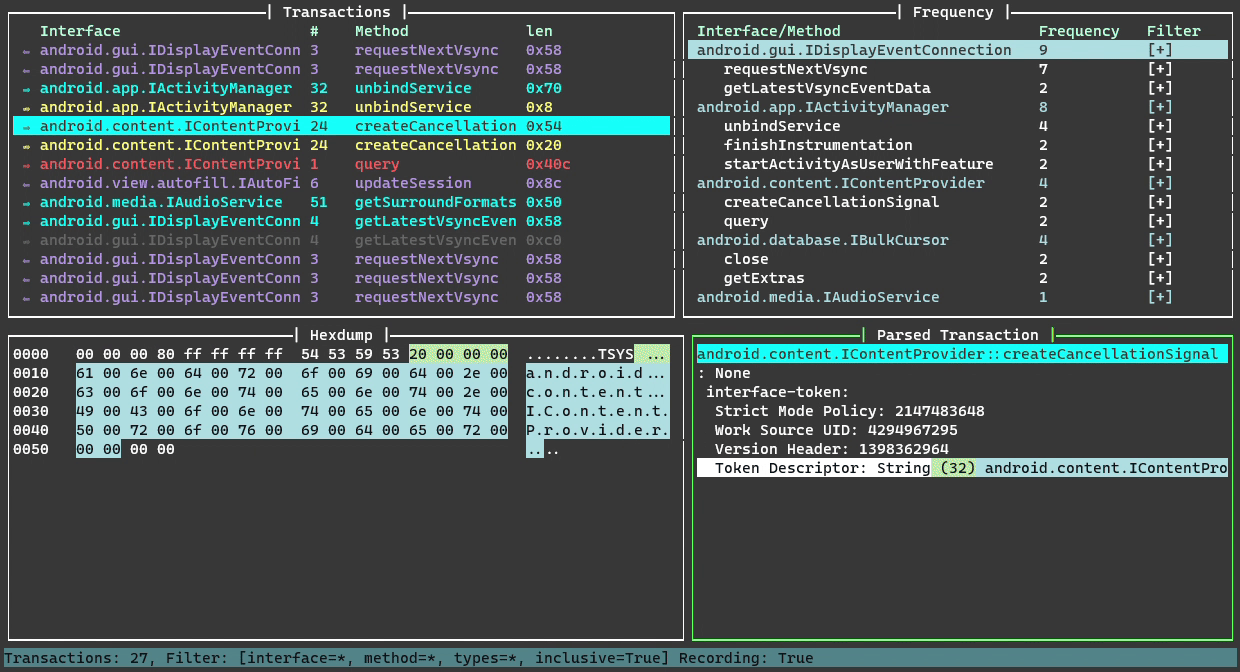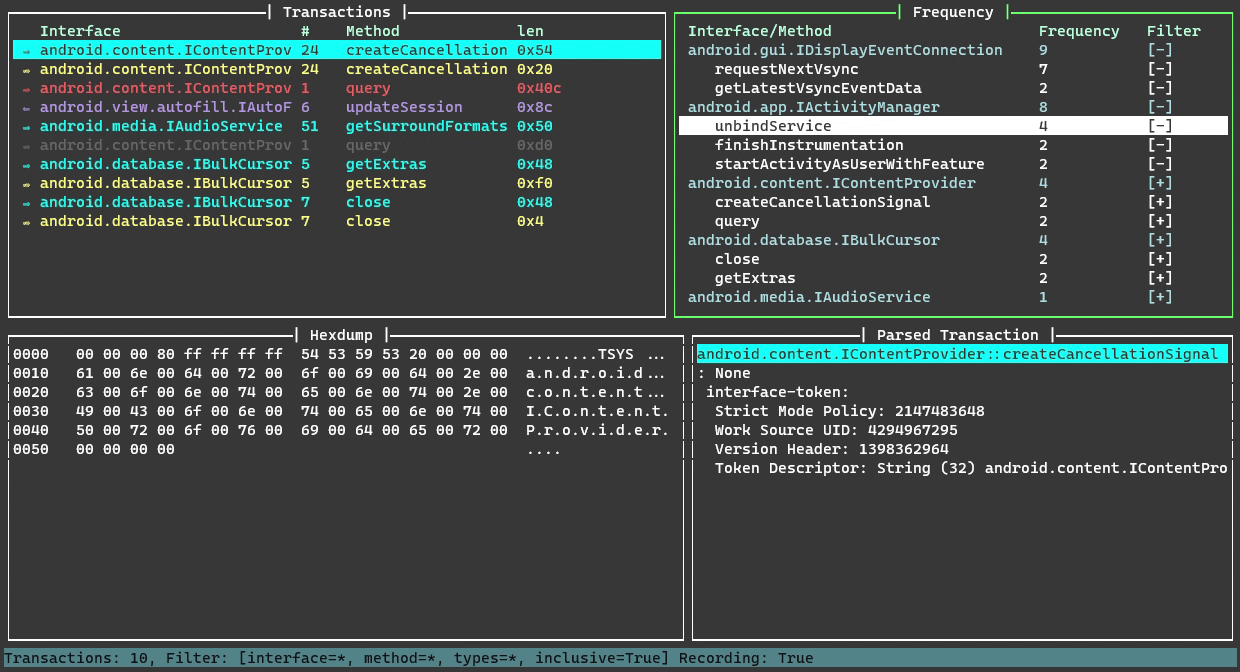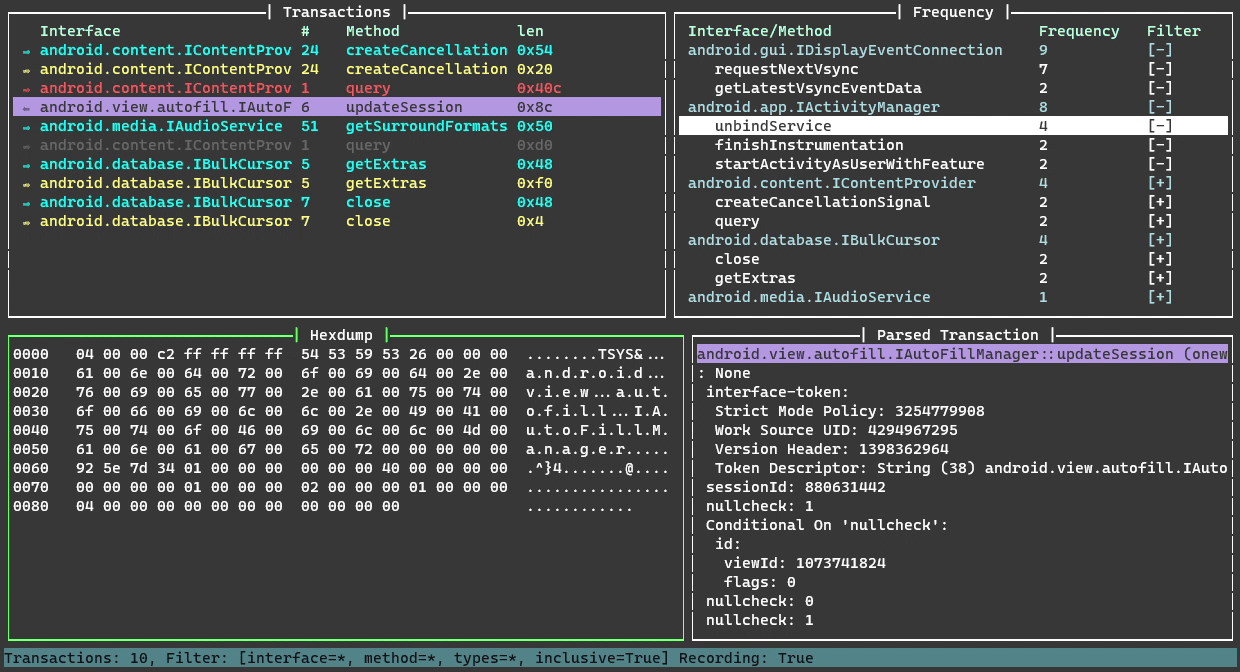
    Binder TraceC1

    Frida-based terminal tool, described by its authors as "Wireshark for Binder", that intercepts the Binder IPC transactions an Android process sends and parses each message and its reply.

    Demo screenshot from the project's public documentation
    • App
    • Protocol

    Reviewed foundryzero/binder-trace@a8a9a06

  • App · Tool:

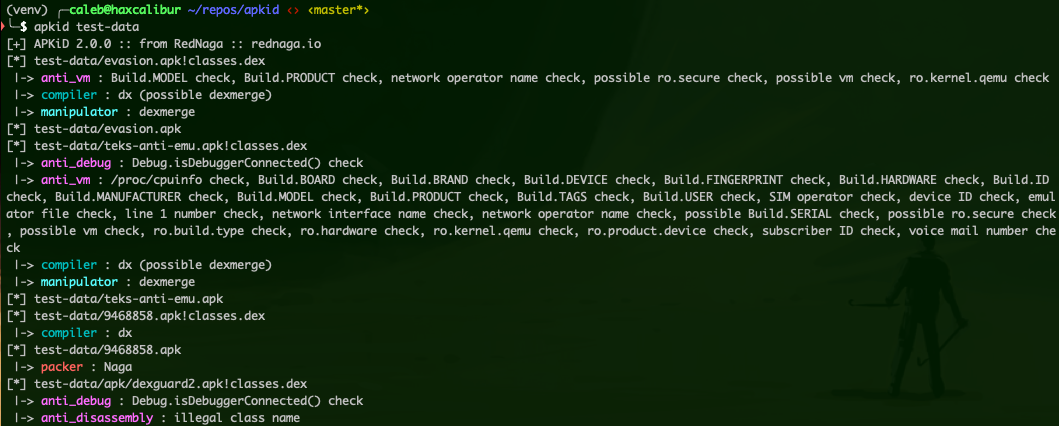
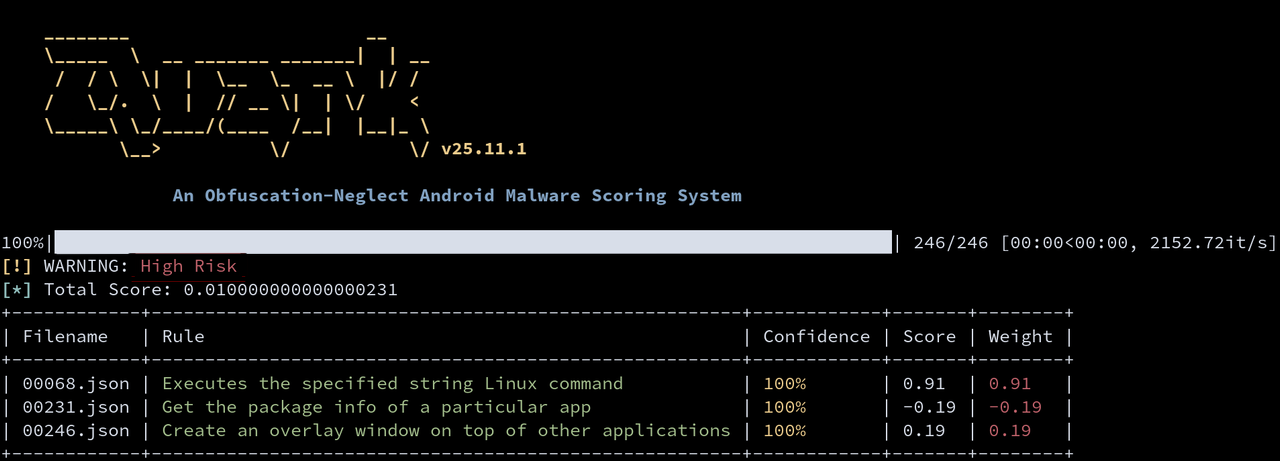
    Quark-EngineC1

    Rule-based engine for analysing suspicious Android apps: it loads an APK's Dalvik bytecode and checks JSON behaviour rules, each naming permissions and a pair of framework API calls, through five confidence stages, from the permission being requested and either API being called up to both calls appearing in order in one method and passing the same register.

    Demo screenshot from the project's public documentation
    • App

    Reviewed ev-flow/quark-engine@7accc95

  • App · Tool:

    Dexcalibur (Reversense)C2

    Android reverse-engineering platform that combines static analysis with Frida-based dynamic instrumentation; the master branch is Reversense (Dexcalibur 2.0), a rewrite that runs as a Node.js web server for collaborative projects.

    • App

    Reviewed reversenseorg/dexcalibur@2408f79

  • App · Tool:

    vdexExtractorC2

    Command-line C tool that extracts the Dex bytecode held in the Vdex containers that ART's dex2oat compiler writes beside Oat files since Android 8.0 (API 26), and by default reverts ART's dex-to-dex quickening so the output is ordinary Dex again.

    • App

    Reviewed anestisb/vdexExtractor@78f283b

  • App · Tool:

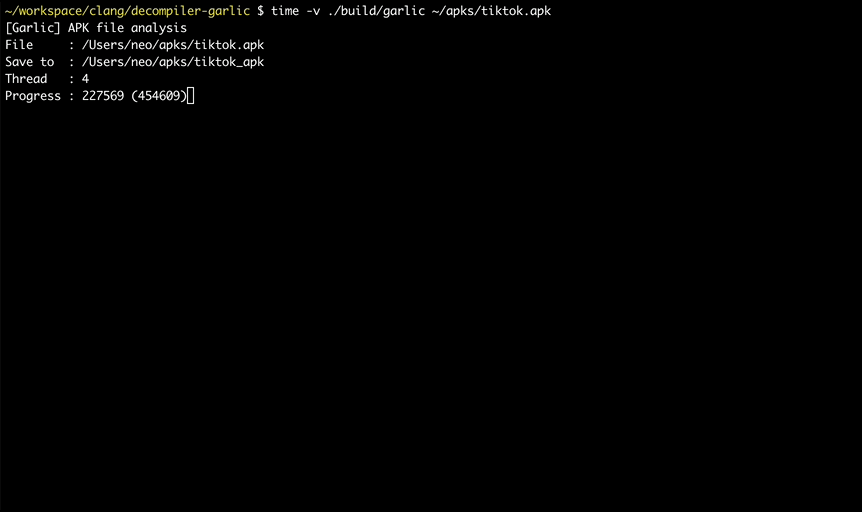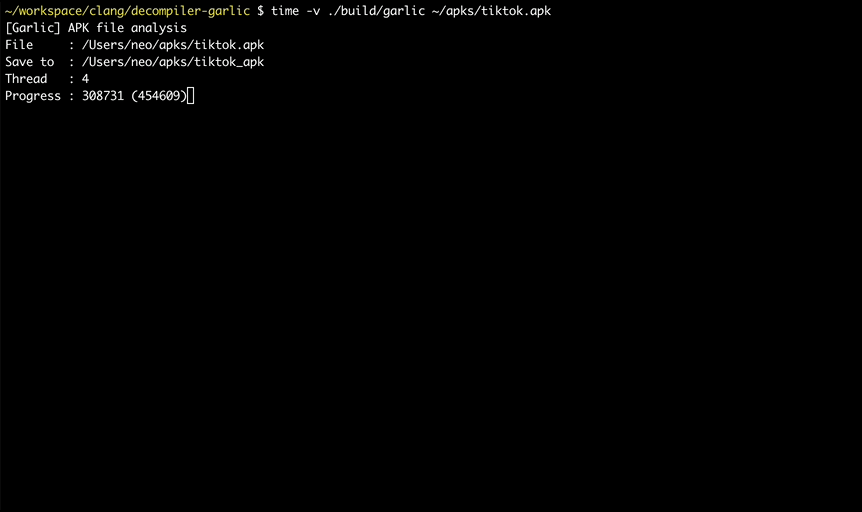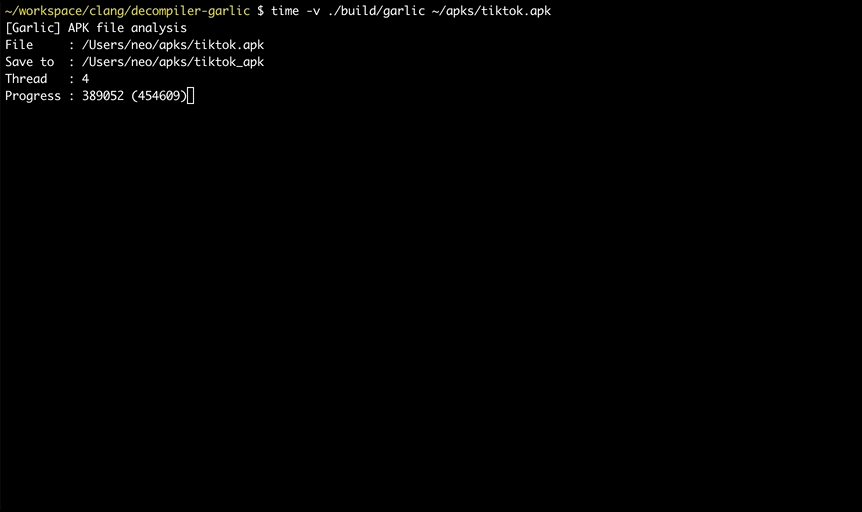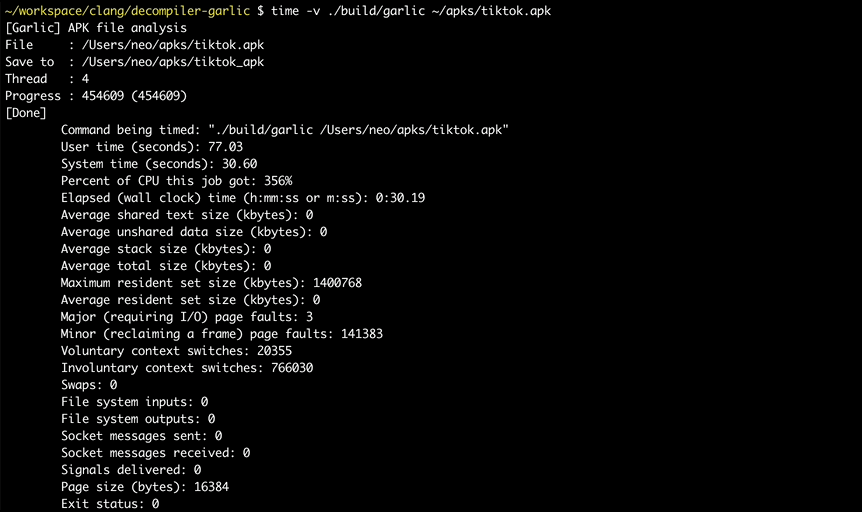
    GarlicC1

    Java and Android decompiler written in C that recovers Java source from class, JAR, WAR, DEX and APK files on multiple threads; it also prints javap- or dexdump-style class listings, converts APK and DEX files to smali, searches their strings with regular expressions and generates call graphs for DEX and APK files.

    Demo screenshot from the project's public documentation
    • App

    Reviewed neocanable/garlic@700a7f4

  • App · Tool:

    Android-DisassemblerC1

    On-device disassembler and binary viewer for Android, built on Capstone, that opens ELF shared libraries and executables, object files, Windows PE files, .NET assemblies, dex files and APKs chosen from storage or from installed apps.

    Demo screenshot from the project's public documentation
    • App
    • Binary

    Reviewed yhs0602/Android-Disassembler@dde36d9

  • App · Tool:

    XAPKDetectorC1

    APK and DEX detector from hors, the author of Detect-It-Easy, that reports the build tools, libraries and protections it identifies in Android packages, using scan engines and signature databases from the Detect-It-Easy family.

    Demo screenshot from the project's public documentation
    • App

    Reviewed horsicq/XAPKDetector@09ce272

  • App · Tool:

    JsxerC1

    C++ decompiler for JSXBIN, the binary format of Adobe's legacy ExtendScript, the ECMAScript 3 dialect used to script applications such as Photoshop, InDesign and After Effects.

    Demo video thumbnail from the project's public documentation
    • App

    Reviewed AngeloD2022/jsxer@0340bd3

  • App · Tool:

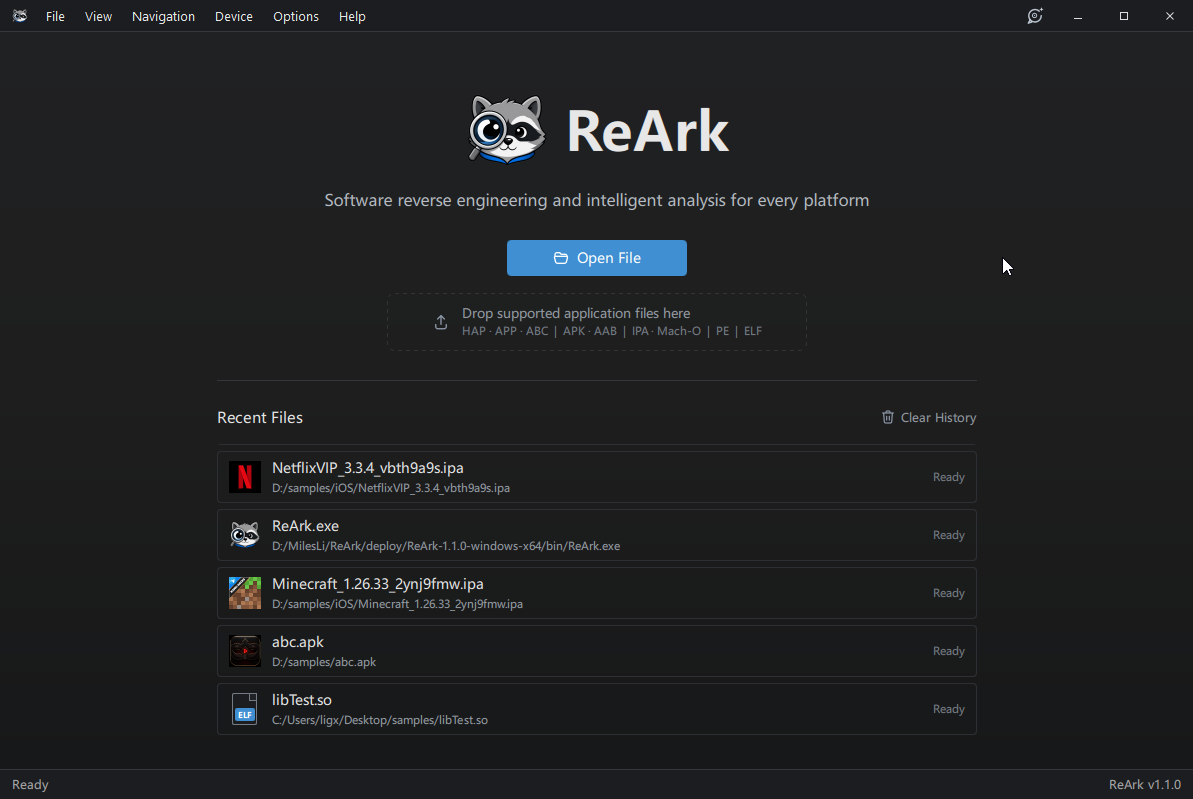
    ReArkC1

    Desktop reverse-engineering and AI-assisted analysis workbench for HarmonyOS NEXT packages (.hap, .app and .abc), whose binary releases add Android .apk/.aab, iOS .ipa and standalone PE, ELF and Mach-O analysis.

    Demo screenshot from the project's public documentation
    • App
    • Binary

    Reviewed lkimuk/ReArk@b4e8337

  • App · Tool:

    ARSCLibC2

    Java library, modeled on AOSP's androidfw ResourceTypes.h and meant to replace aapt/aapt2, that reads, writes, modifies and creates Android resource tables (resources.arsc) and binary XML files such as AndroidManifest.xml.

    • App

    Reviewed REAndroid/ARSCLib@bd7221b

  • App · Tool:

    Pithus (bazaar)C2

    Self-hostable Django platform behind the Pithus Android analysis service, which its README describes as built for activists, journalists, NGOs and researchers.

    • App

    Reviewed Pithus/bazaar@3217f72

  • App · Tool:

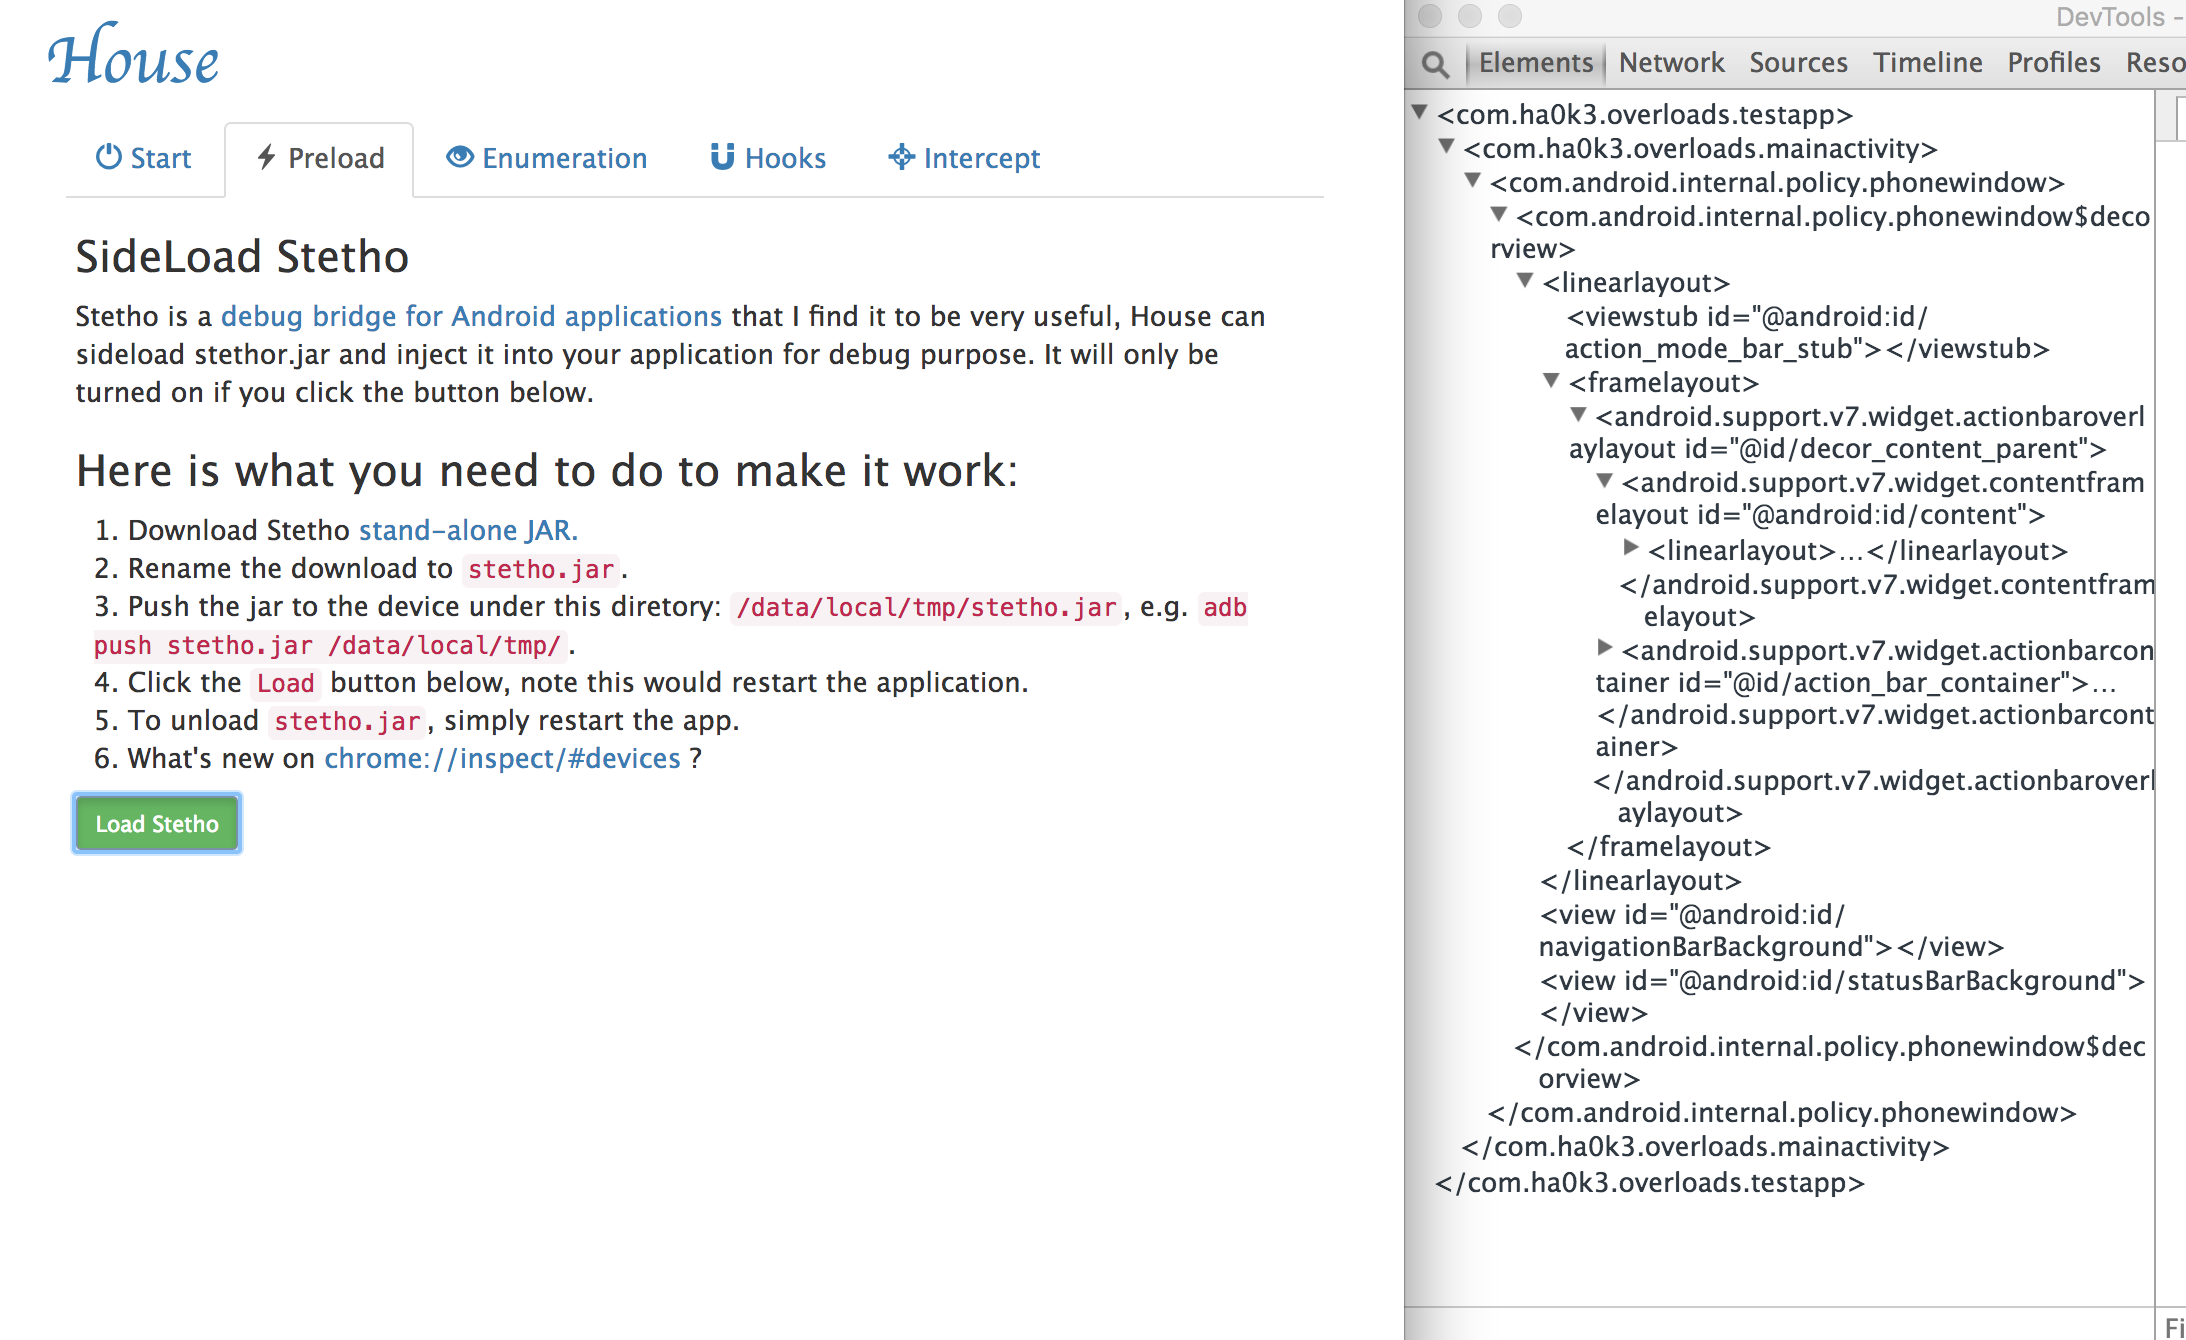
    HouseC1

    NCC Group’s Python and Flask web interface for Frida-based runtime analysis of Android apps, intended to make writing Frida scripts simpler.

    Demo screenshot from the project's public documentation
    • App

    Reviewed nccgroup/house@c3641e3

  • App · Tool:

    ABCDEC2

    Kotlin toolkit for OpenHarmony reverse engineering that parses Ark bytecode (.abc) files, the format HarmonyOS app packages carry in modules.abc, along with HAP packages and resource index (.index) files.

    • App

    Reviewed Yricky/abcde@62f7fc6

  • Website · Tool:

    de4jsC1

    Browser-based JavaScript deobfuscator and unpacker, built as a Jekyll site that also works offline as a progressive web app.

    Demo available · no screenshot
    • Website

    Reviewed lelinhtinh/de4js@b06fff9

  • App · Tool:

    DexKitC2

    C++ DEX parsing library with Kotlin and Java APIs that loads an APK, DEX bytes or an app’s class loader and finds classes, methods and fields by their characteristics rather than their obfuscated names.

    • App

    Reviewed LuckyPray/DexKit@f86a036

  • App · Tool:

    dex-oracleC1

    Pattern-based Dalvik deobfuscator that takes an APK, a DEX file or a Smali directory, disassembles it with baksmali and runs plugins that look for obfuscation patterns in the Smali code.

    Demo screenshot from the project's public documentation
    • App

    Reviewed CalebFenton/dex-oracle@d6be172

  • App · Tool:

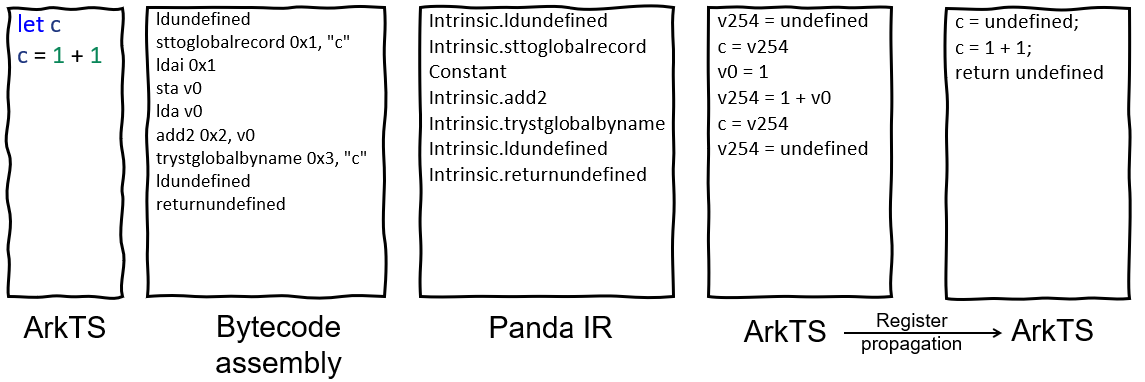
    arkdecompilerC1

    Decompiler for HarmonyOS NEXT apps, published under the jd-opensource GitHub organization, that turns Panda binary files (.abc Ark bytecode) back into ArkTS source.

    Demo screenshot from the project's public documentation
    • App

    Reviewed jd-opensource/arkdecompiler@8afb369

  • App · Tool:

    JNIAnalyzerC2

    A Ghidra extension by Terry Chia (Ayrx) with scripts for analyzing the native libraries of Android NDK apps.

    • App
    • Binary

    Reviewed Ayrx/JNIAnalyzer@7170ce6

  • App · Tool:

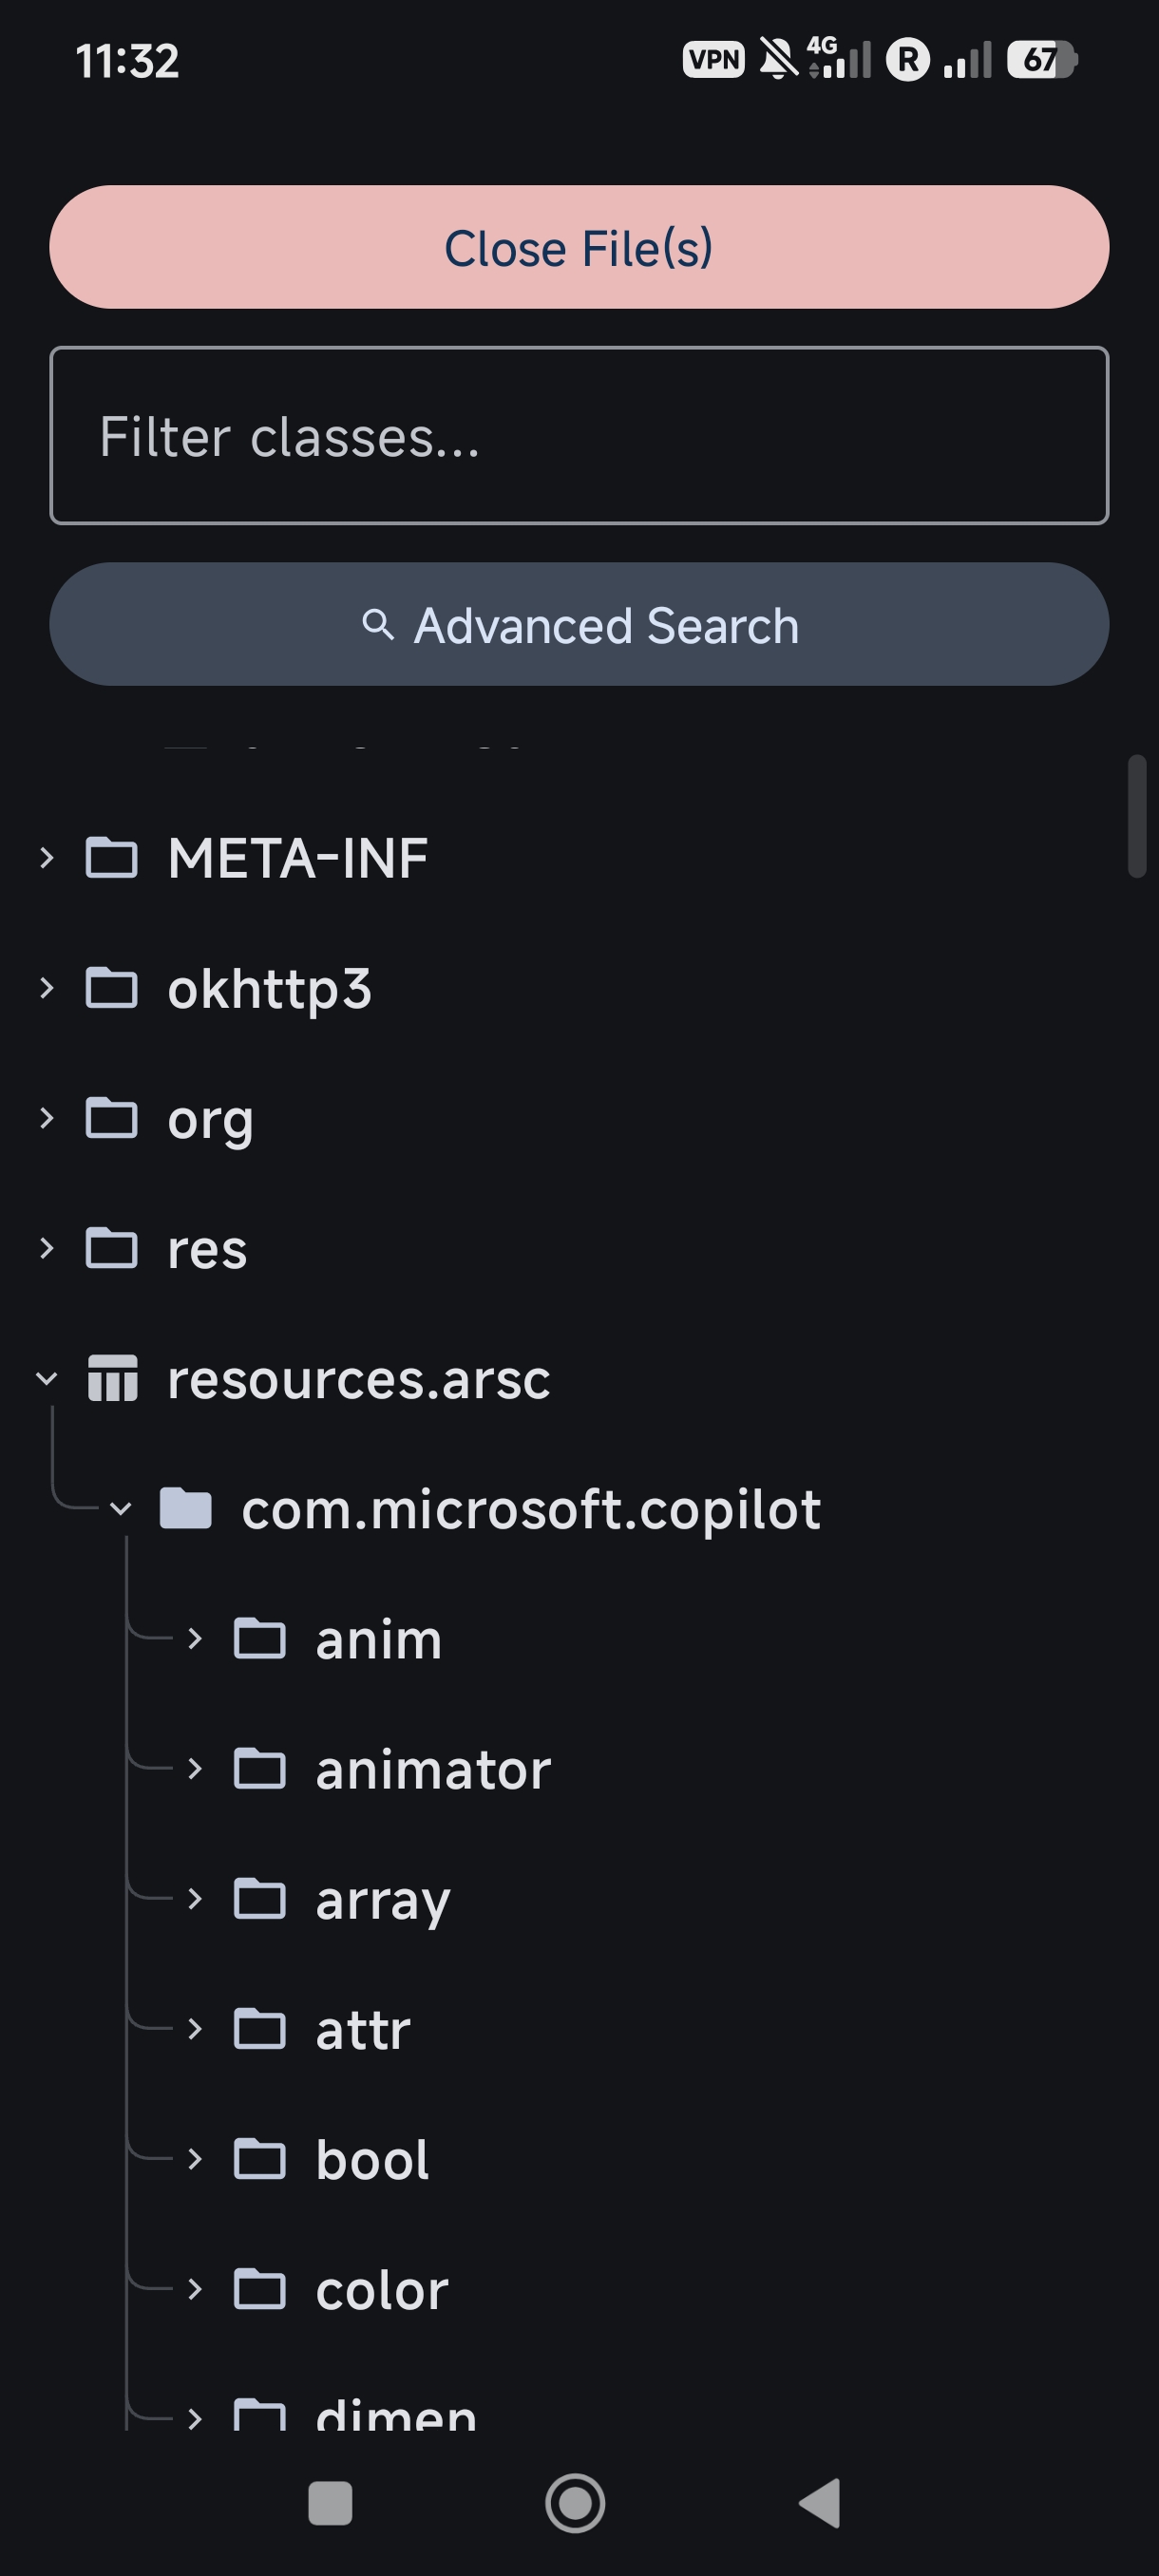
    Android ReverseC1

    Android app, published only as release APKs, that runs an APK reverse-engineering workflow entirely on the phone, from package extraction and Java decompilation to native analysis, editing and rebuilding.

    Demo screenshot from the project's public documentation
    • App

    Reviewed UltraSina/androidReverse@ad9dd7a

  • App · Tool:

    AndromedaC2

    Interactive command-line tool by Lasha Khasaia for first-pass reverse engineering of Android APKs, written in C/C++ for speed.

    • App

    Reviewed secrary/Andromeda@50fdaaf

  • App · Tool:

    smali/baksmaliC2

    Assembler and disassembler for the dex format used by Android's Dalvik VM: baksmali turns dex, APK, odex and oat files into smali text, and smali assembles that text back into a dex file.

    • App

    Reviewed JesusFreke/smali@2771eae

  • App · Tool:

    dalvikusC1

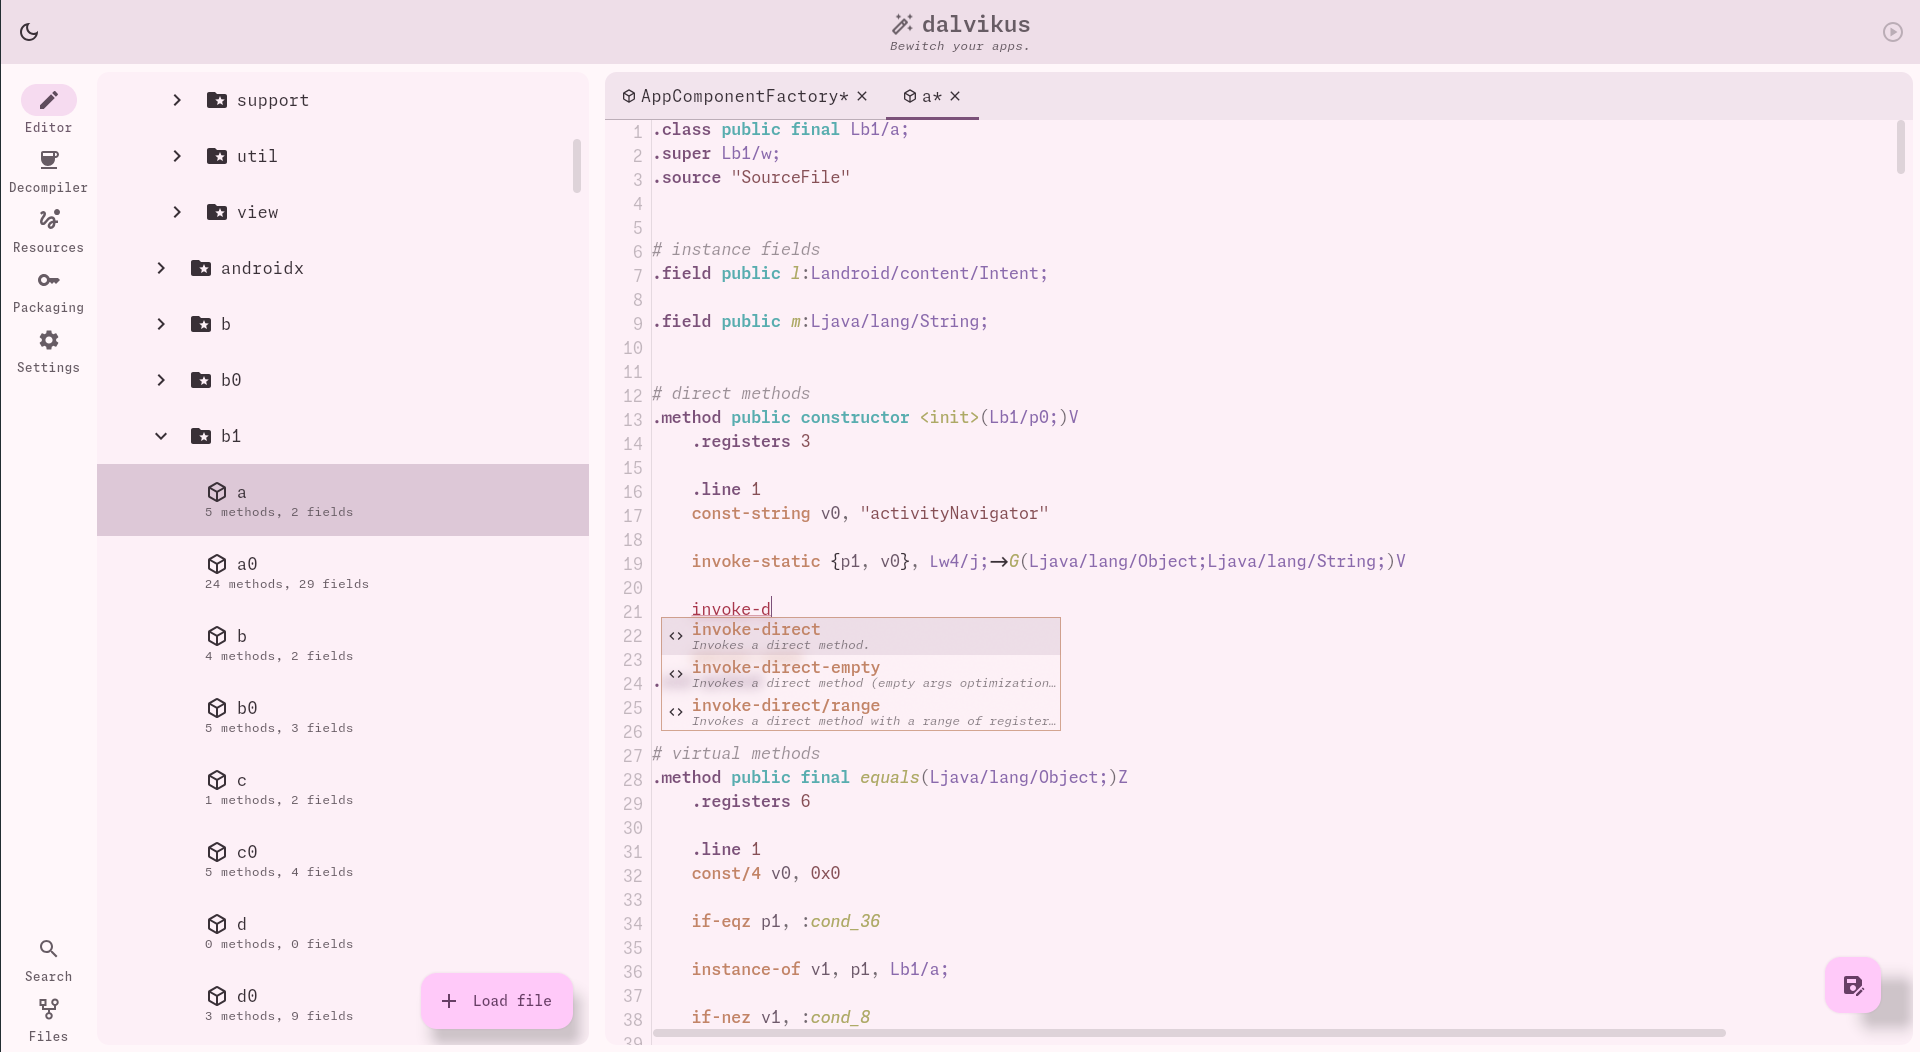
    Desktop Android reverse-engineering and modification workbench built with Kotlin Compose Multiplatform.

    Demo screenshot from the project's public documentation
    • App

    Reviewed loerting/dalvikus@931cbf3

  • App · Tool:

    KatalinaC2

    Python emulator for Dalvik bytecode that its README likens to Unicorn: it parses a DEX file and executes methods one instruction at a time, substituting Python mocks for common Java and Android APIs such as String, StringBuilder, Base64, ArrayList, AES Cipher and part of reflection.

    • App

    Reviewed huuck/Katalina@f8e27b9

  • App · Tool:

    DoldrumsC2

    Python parser for the Dart AOT snapshots inside libapp.so, the compiled Dart code of an Android Flutter app.

    • App
    • Binary

    Reviewed rscloura/Doldrums@7430196

  • App · Tool:

    Frida UIC1

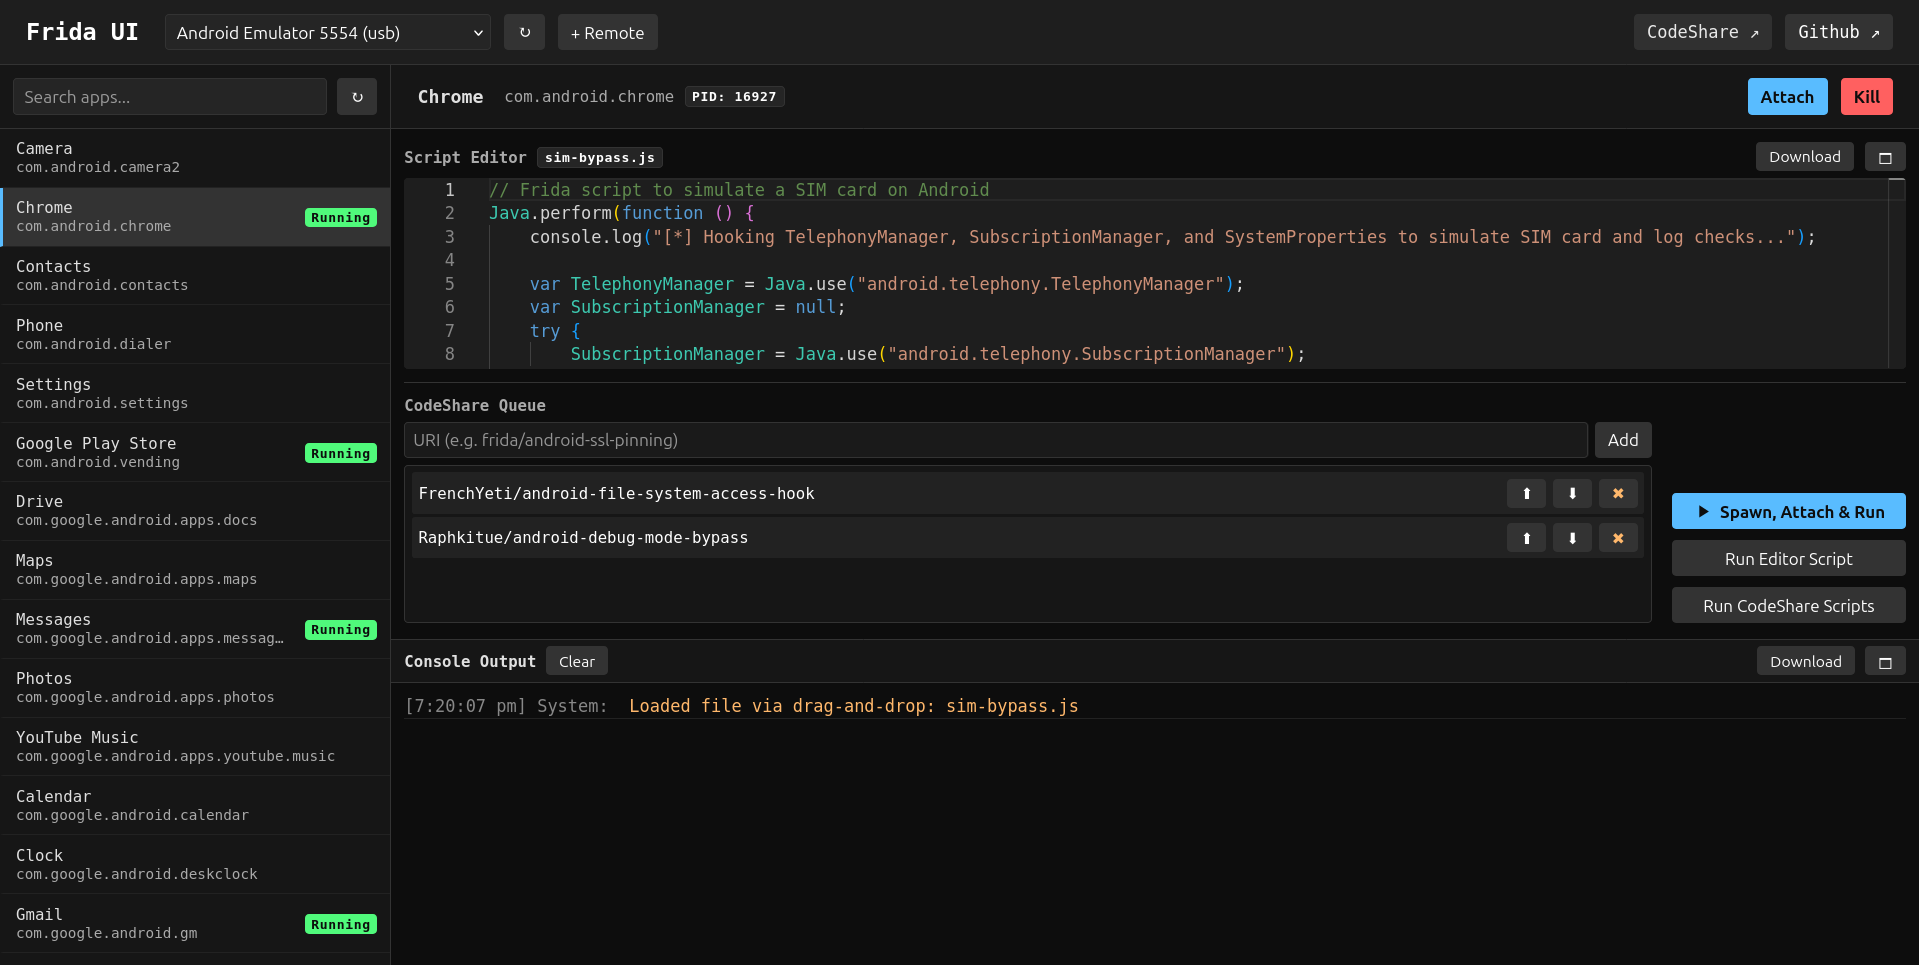
    Local browser interface for Frida aimed at Android app testing: a FastAPI server lists USB, local and remote frida-server devices with their installed apps and running processes, and lets the analyst attach to a process, spawn an app, spawn it with a script injected at launch, detach or kill it.

    Demo screenshot from the project's public documentation
    • App

    Reviewed adityatelange/frida-ui@4b25e28

  • App · Tool:

    darterC2

    Python module that parses binary Dart VM snapshots, such as the libapp.so of a release Flutter app, into a navigable graph of VM objects with back-references, including the memory structures the snapshot dumps.

    • App
    • Binary

    Reviewed mildsunrise/darter@a649878

  • App · Tool:

    AppsharkC1

    ByteDance's static taint-analysis engine for Android APKs, designed for very large apps, that scans an app against JSON rules naming entry methods, sources, sinks and sanitizers as Jimple signatures, for vulnerability and privacy-compliance review.

    Demo available · no screenshot
    • App

    Reviewed bytedance/appshark@487fa21

  • App · Tool:

    WallbreakerC2

    Frida-based explorer for the live Java heap of a running Android app, loaded as an objection plugin or used through its small Python package.

    • App

    Reviewed hluwa/Wallbreaker@f27f2da

  • App · Tool:

    axmlprinterC2

    Java library and command-line tool that parses Android binary XML, such as the compiled AndroidManifest.xml inside an APK, and prints it as readable XML.

    • App

    Reviewed rednaga/axmlprinter@5a8d3e5

  • App · Tool:

    EnjarifyC2

    Pure-Python 3 translator from Dalvik bytecode to equivalent Java bytecode, so Java analysis tools and decompilers can be applied to Android apps: given an APK, with every DEX file of a multidex APK combined into one jar, or a single DEX file, it writes a jar of class files.

    • App

    Reviewed google/enjarify@f2db056

  • App · Tool:

    MagiskFridaC2

    Magisk, KernelSU and APatch module that installs frida-server on a rooted Android device and starts it at boot, so Frida clients can attach for dynamic instrumentation without starting the server by hand.

    • App

    Reviewed ViRb3/magisk-frida@1f4003a

  • App · Tool:

    de4dotC2

    Open-source .NET deobfuscator and unpacker that tries to restore a packed and obfuscated assembly to almost its original form.

    • App

    Reviewed de4dot/de4dot@b7d5728

  • App · Tool:

    ClassySharkC1

    Google's standalone browser for Android executables and libraries that shows class interfaces and members, dex counts and dependencies.

    Demo screenshot from the project's public documentation
    • App

    Reviewed google/android-classyshark@78ddba7

  • App · Tool:

    JEB DecompilerC2

    PNF Software's commercial reverse-engineering platform for Android apps and native code, combining a Dalvik decompiler and Android debuggers with disassemblers and decompilers for x86, ARM, MIPS and RISC-V machine code.

    • App
    • Binary
    • Firmware

    Reviewed pnfsoftware.com/jeb

  • Binary · Tool:

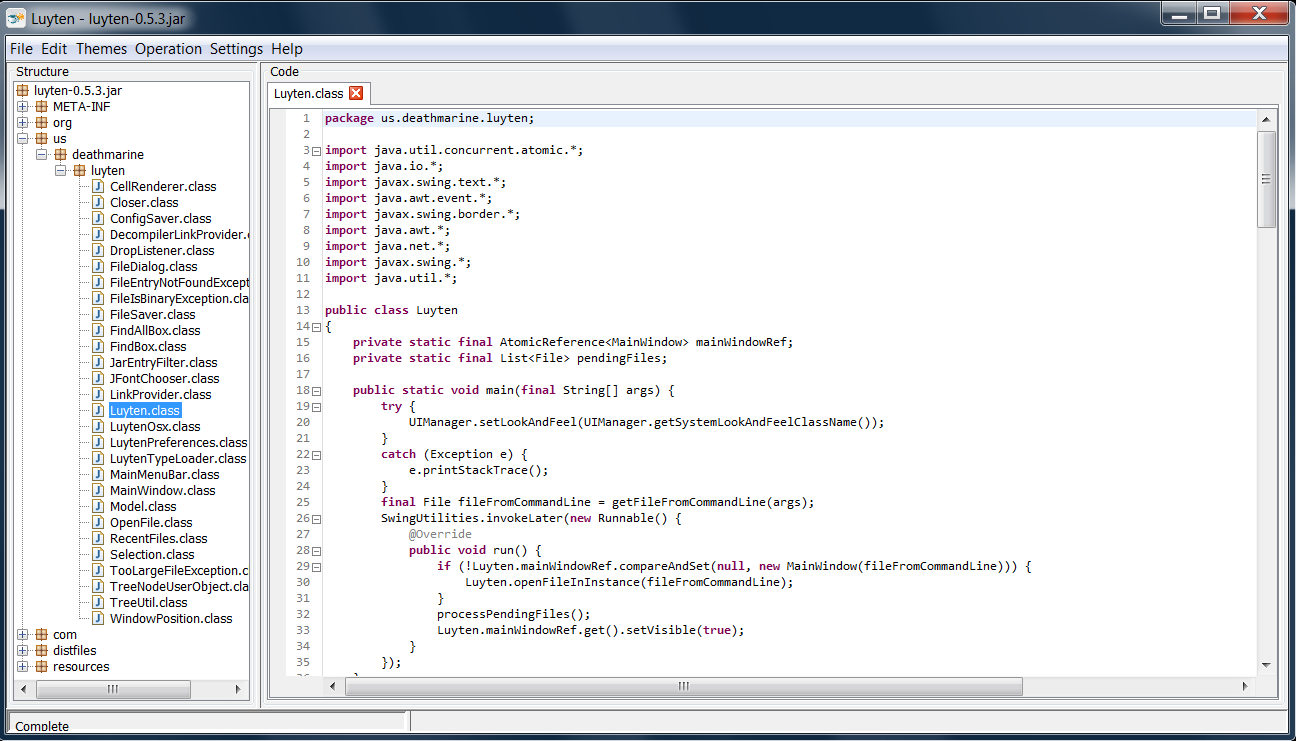
    LuytenC1

    Graphical Java decompiler front end for the Procyon decompiler, with its editor view powered by RSyntaxTextArea.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed deathmarine/Luyten@64af8d1

  • Binary · Tool:

    jd-cliC2

    Command-line wrapper around a jd-core fork that decompiles Java class and JAR files to the console, a directory or a ZIP file, with options for line numbers, file-matching patterns and parallel processing.

    • Binary

    Reviewed intoolswetrust/jd-cli@923d002

  • App · Tool:

    ReverseAPKC2

    Command-line tool that decompiles an APK to Java and Smali, lists the extracted files, and statically checks AndroidManifest.xml and the source for common vulnerabilities and behaviours such as intents, command execution, content providers, crypto references and hardcoded secrets.

    • App

    Reviewed 1N3/ReverseAPK@74b33e4

  • App · Tool:

    xHookC2

    PLT hook library for Android native ELF executables and shared libraries.

    • App

    Reviewed iqiyi/xHook@391d0c4

  • App · Tool:

    EpicC2

    Continuation of Dexposed on ART: a runtime method-hooking framework that loads into an app and can hook both the app's own code and Android framework code running in its process.

    • App

    Reviewed tiann/epic@c67d0d3

  • App · Tool:

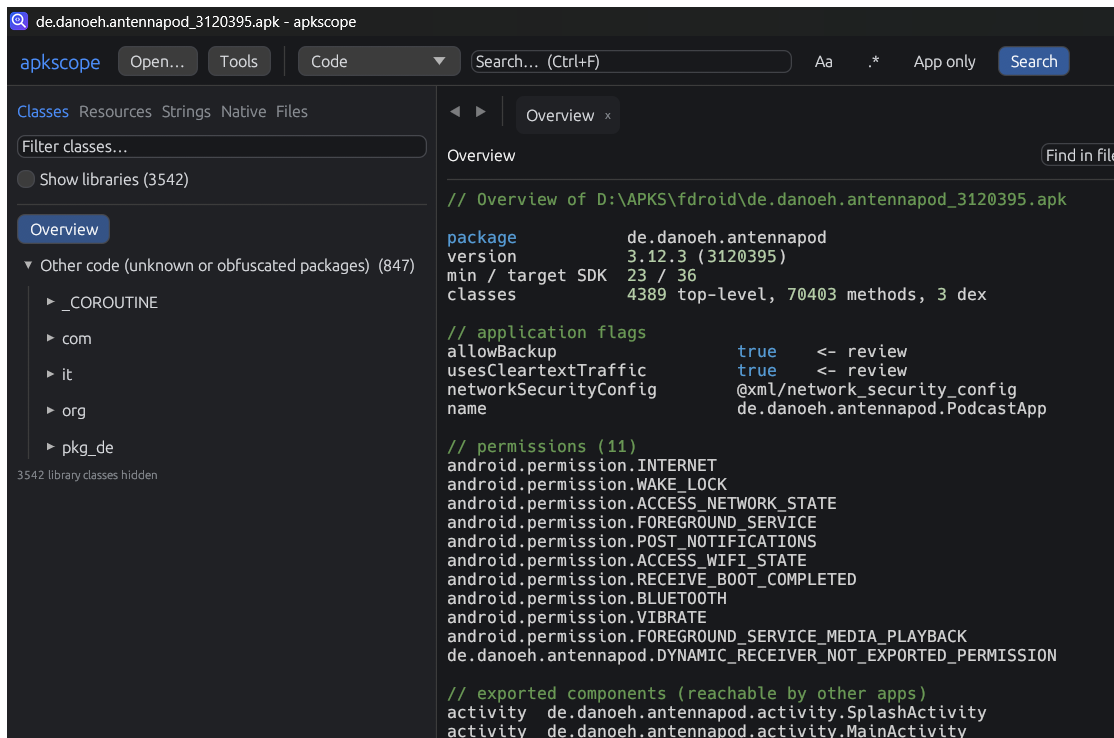
    apkscopeC1

    apkscope inspects Android application packages through a Rust viewer, CLI, and MCP server.

    Demo screenshot from the project's public documentation
    • App
    • Binary

    Reviewed suffixing/apkscope@e224d4f

  • Binary · Tool:

    derktC2

    derkt parses and disassembles Hermes Bytecode files in Racket.

    • Binary

    Reviewed rrandom/derkt@5a30bf9

↑↓ move↵ open⌘↵ new tab