Game · Integration:
Co-op AnythingC2
Agent playbook, skill set and stdio MCP server for adding online or split-screen co-op to single-player games the players already have installed.
- Game
Reviewed cranebeaker/coop-anything@bffd56f
Game · Integration:
Agent playbook, skill set and stdio MCP server for adding online or split-screen co-op to single-player games the players already have installed.
Reviewed cranebeaker/coop-anything@bffd56f
Binary · Integration:
IDA Pro 9.x plugin and PowerShell batch extractor that turn Windows PE files into material AI coding agents can read: a per-binary SQLite database of PE metadata, signatures, disassembly, Hex-Rays pseudocode, cross-references, strings, stack frames, loops and dangerous API calls, plus optional grouped C++ and assembly files with per-function caller, callee and string headers and JSON indexes.
Reviewed marcosd4h/DeepExtractIDA@af6b01d
Game · Integration:
Plugin pipeline for matching decompilation that loops over functions in an existing decomp project: m2c drafts C, decomp-permuter mutates it, Claude rewrites it through a compile-and-diff tool, and objdiff accepts a result only when the compiled object matches the target assembly.
Reviewed macabeus/mizuchi@25eaef4
Binary · Integration:
An open-source Python agent, published on PyPI as auto-re-agent, that drafts C/C++ implementations of functions in a compiled program from Ghidra evidence and has a separately configurable checker model review each draft in a bounded fix loop.
Reviewed Dryxio/reagent@d12cea3
Binary · Integration:
LLDB extension that adds an MCP bridge to a debugging session, adapted from ida-pro-mcp: the plugin's mcp start command serves 18 debugger functions over local JSON-RPC, and a FastMCP stdio server generated from those functions exposes them to MCP clients such as Claude Desktop.
Reviewed ant4g0nist/lisa.py@9dd61e9
Protocol · Integration:
Node.js MCP server that runs Wireshark's tshark for LLM clients, aimed in its README at threat hunting, network diagnostics and anomaly detection.
Reviewed 0xKoda/WireMCP@7f45f8b
Binary · Integration:
Binary Ninja plugin that suggests function names from HLIL decompiler output with a language model run locally through llama.cpp; the README says it operates entirely offline once the model is downloaded.
Reviewed mrphrazer/reverser_ai@1d572da
Binary · Integration:
IDA plugin, formerly WPeChatGPT and inspired by Gepetto, that sends the Hex-Rays pseudocode of a function to an OpenAI-compatible model (OpenAI, DeepSeek or another compatible endpoint) and writes the model's analysis back into IDA as comments.
Reviewed WPeace-HcH/WPeGPT@8a7802a
Binary · Integration:
IDA Pro plugin by Jason Tang, who also wrote GhidrAssist, that adds a dockable PySide6 panel for LLM-assisted analysis of the open database.
Reviewed symgraph/IDAssist@09dd910
Binary · Integration:
Ghidra extension that sends one function’s decompiled C to a hosted or local language model the user selects and streams the answer into a GhidraGPT console.
Reviewed weirdmachine64/GhidraGPT@364e3f5
Binary · Integration:
Ghidra extension by Jason Tang, who also wrote GhidrAssistMCP, that adds a tabbed GhidrAssist window to CodeBrowser for LLM-assisted analysis of the open program.
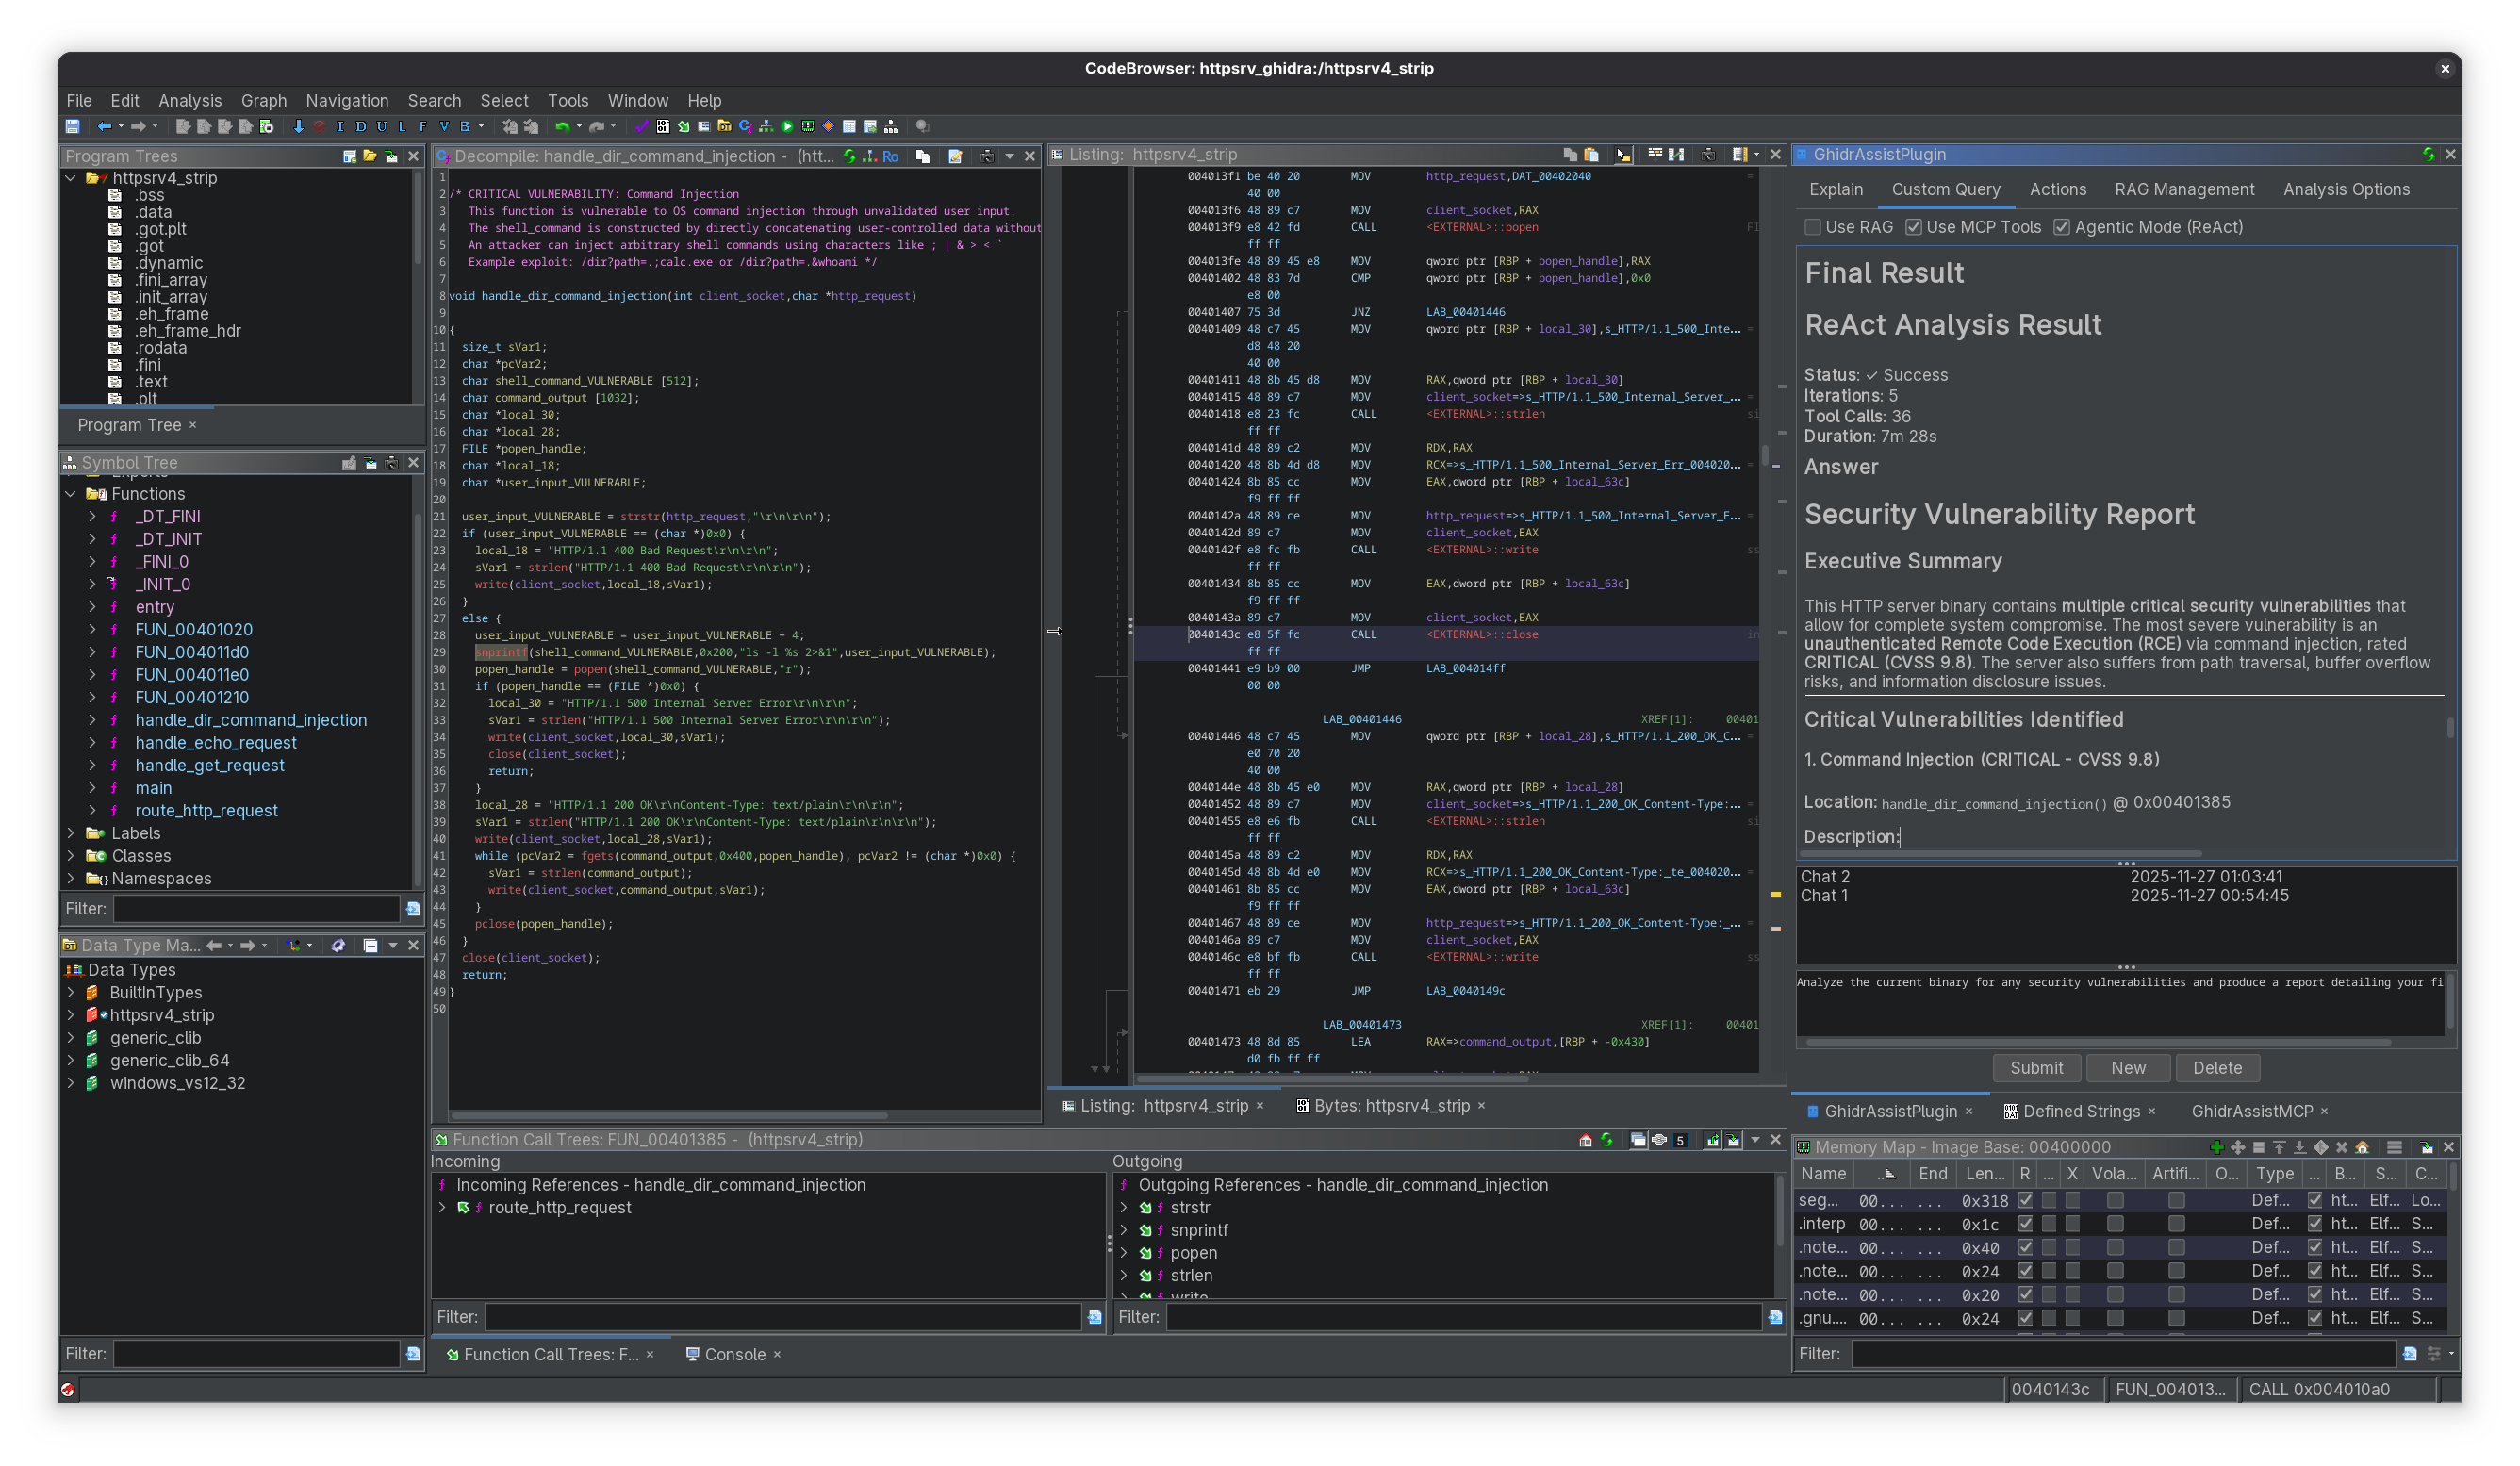
Reviewed symgraph/GhidrAssist@798a5d7
Binary · Integration:
IDA Pro and Binary Ninja plugin that runs its own agent loop inside the disassembler: a model the user chooses streams its answers and calls more than 60 in-process tools for navigation, decompilation, disassembly, cross-references, strings, types, annotations, scripting and host IL or microcode edits.
Reviewed buzzer-re/Rikugan@a2ba669
Binary · Integration:
Agent-oriented command-line interface for the Binary Ninja database already open in the GUI, reached through a companion plugin that listens on a local Unix-domain socket.
Reviewed banteg/bn@bd91032
Binary · Integration:
An IDA Pro plugin and a TypeScript MCP server by Florian Drechsler: the plugin starts an HTTP server inside IDA on 127.0.0.1:9045, and the stdio MCP server forwards agent requests to it.
Reviewed fdrechsler/mcp-server-idapro@6f96014
Binary · Integration:
Headless MCP server that drives Ghidra through PyGhidra and is meant to share a container with the agent.
Binary · Integration:
A third-party, headless-only MCP server by Ruben Marks (mrphrazer) that gives agents a large Binary Ninja tool surface the project counts as 181 tools across 36 feature groups, including disassembly, intermediate languages, cross-references, types, search, patching with undo/redo transactions, and arbitrary scripting through binja.eval and binja.call.
Binary · Integration:
Agent skill that has an AI agent triage malware samples statically in IDA Pro through headless idat.
Reviewed miunasu/IDA-Skill@4595864
Binary · Integration:
Binary Ninja plugin by Jason Tang, who also wrote GhidrAssist and IDAssist, that adds a BinAssist sidebar for LLM-assisted analysis of the open binary.
Reviewed symgraph/BinAssist@0f0b01a
Binary · Integration:
MCP server that puts radare2 with r2ghidra, LIEF, Capstone, YARA, CAPA, Detect It Easy, binwalk, angr, Volatility3, Scapy, Sleuth Kit and other engines behind 177 typed tools for AI clients such as Claude and Cursor.
Reviewed sjkim1127/Reversecore_MCP@c1c5767
Firmware · Integration:
Flying-probe control stack meant to let a coding agent or an operator take a circuit board on a GRBL 3018-style CNC from locating it on the plate, through XYZ-tagged USB-microscope frames and an annotated map of pads, pins and chips, to probing targets the operator has approved.
Reviewed GainSec/AutoProber@ff0e01f
Binary · Integration:
Python CLI that exports a binary, IDA database, Android APK, .NET assembly or whole application folder into a source-like project tree for coding agents: recovered C (Java for APKs, C# and IL for .NET) with matching assembly and function summaries, recovered headers and types, section dumps, JSON indexes of functions, strings, imports, exports, reachability and call-graph clusters, and generated AGENTS.md and CLAUDE.md files.
Reviewed buzzer-re/ToCode@216f1f9
Website · Integration:
Python CLI that turns the HTTP traffic a website actually produces into a typed API client.
Protocol · Integration:
Rust MCP server and Codex plugin that gives coding agents audited access to local serial devices, from identifying ports by USB metadata and sending framed requests to recording every received and transmitted byte in lossless .obcap captures.
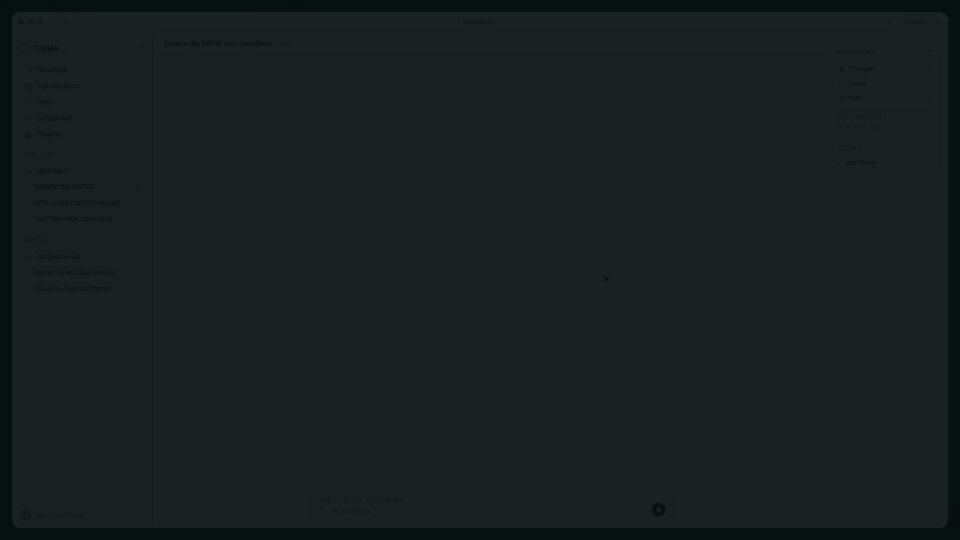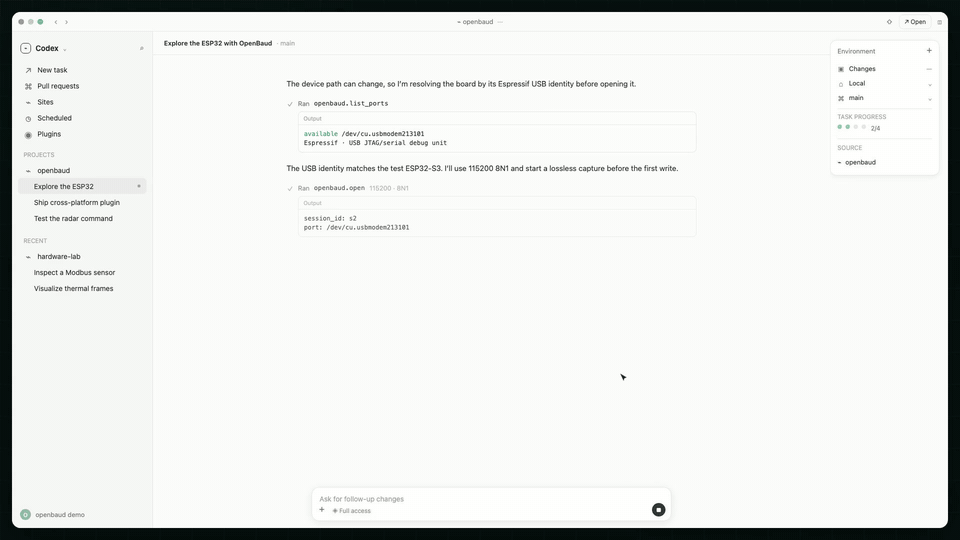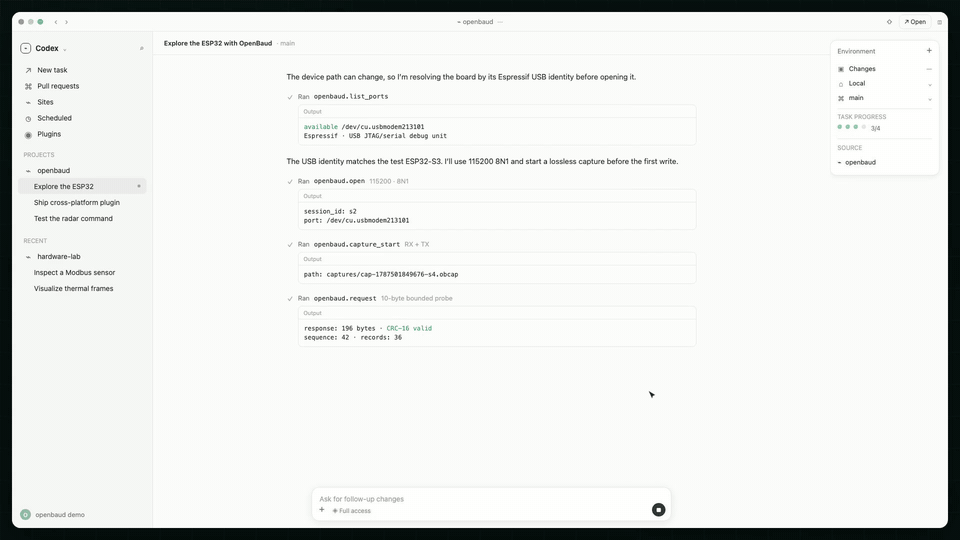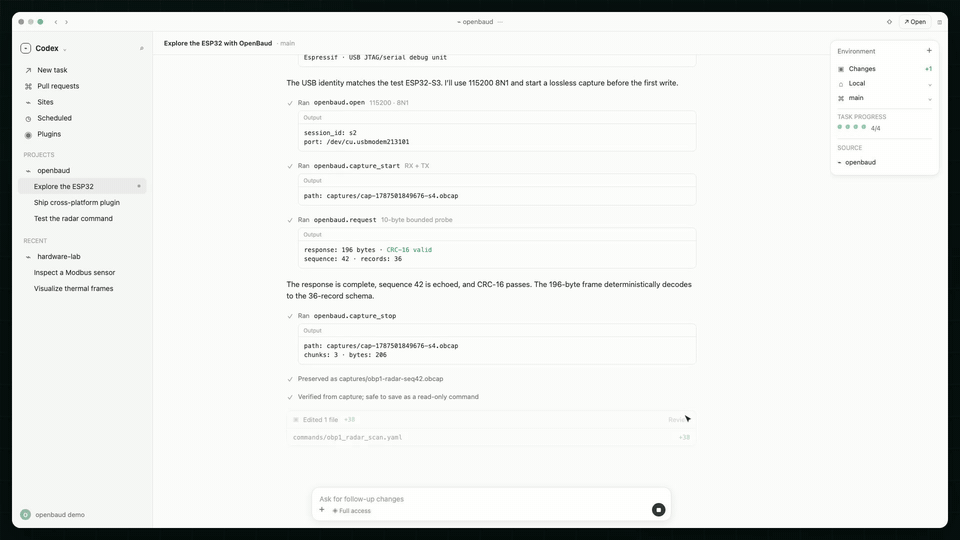
Reviewed Leonezz/openbaud@f3ebd89
App · Integration:
MCP server for Android APK analysis in which a Python FastMCP process talks to the agent over stdio and drives a long-lived local JVM daemon that embeds JADX 1.5.6 as a library, so no JADX GUI is involved and a loaded APK stays warm between sessions.
Reviewed Qtty/jadx-mcp-server@4e6d890
Protocol · Integration:
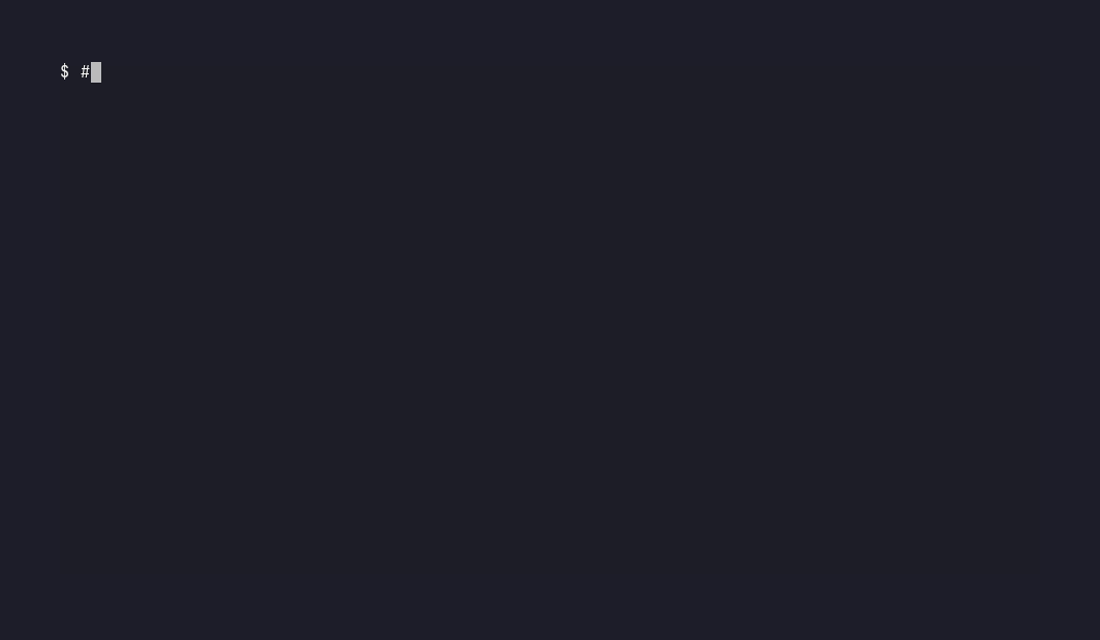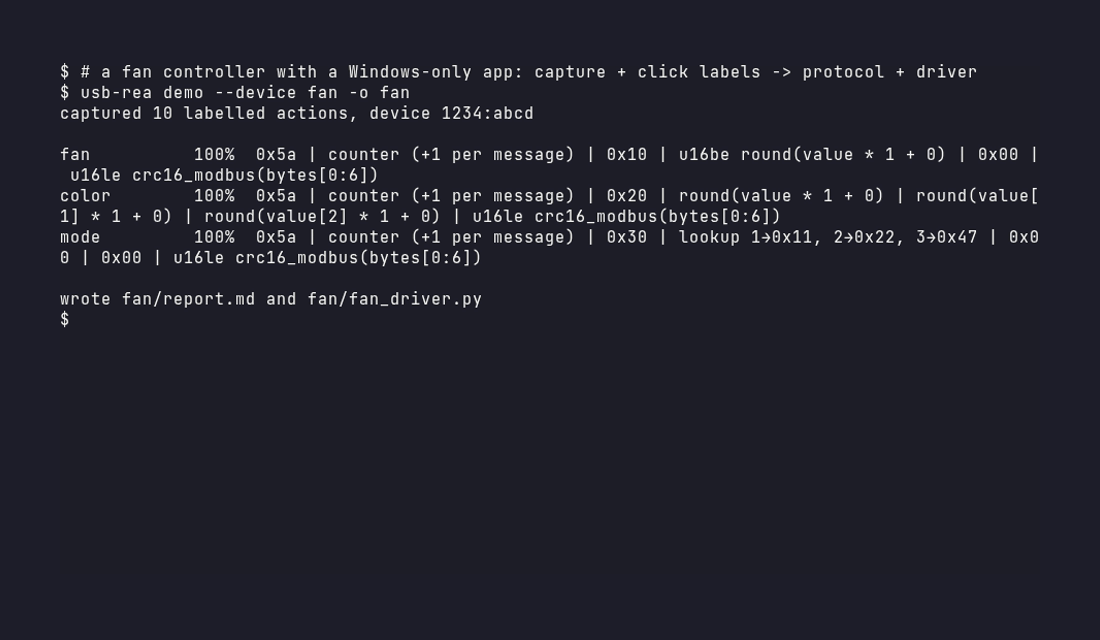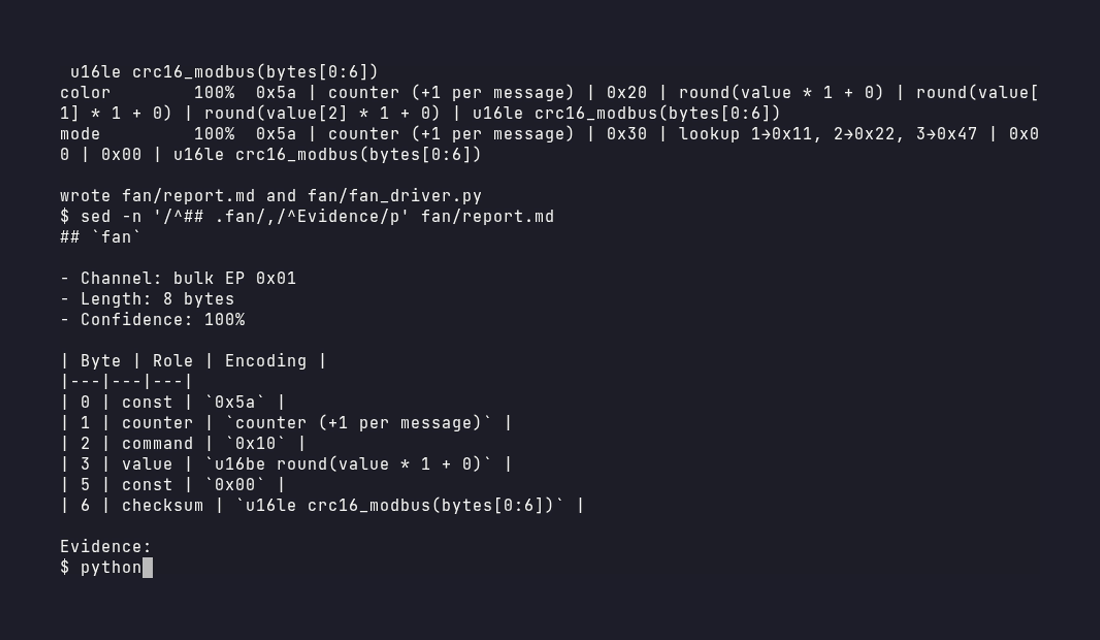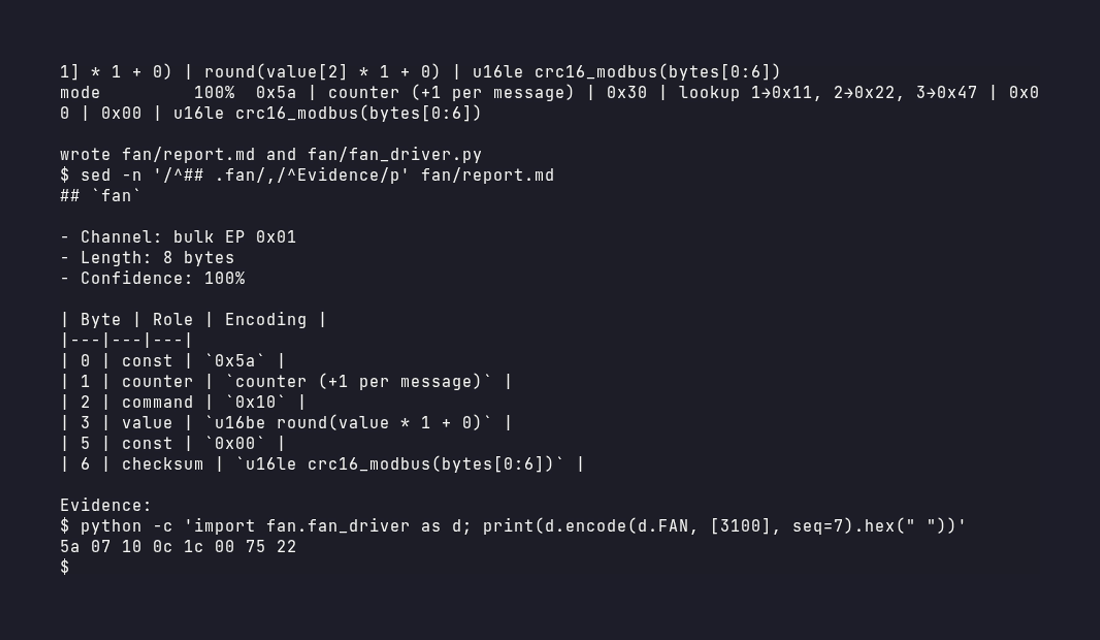
Python CLI and stdio MCP server for inferring the USB protocol of a device whose only control software is a vendor app.
Reviewed emirmrkaljevic/usb-rea@3b77ccb
Binary · Integration:
IDA Pro exporter that turns an analyzed binary into plain files for AI coding tools such as Cursor or Claude Code instead of serving it over MCP.
Reviewed P4nda0s/IDA-NO-MCP@2a48a91
Binary · Integration:
Headless MCP server written in Rust that drives IDA Pro through idalib, so agents such as Claude Code, Codex CLI, Gemini CLI or Cursor can open and analyze binaries without the IDA GUI.
Reviewed blacktop/ida-mcp-rs@7a81b9a
Binary · Integration:
MCP server that lets an agent analyze several IDA Pro databases at once through one endpoint.
Reviewed MeroZemory/ida-multi-mcp@8ff8831
Binary · Integration:
MCP server that connects LLM clients to the x64dbg and x32dbg debuggers through a native plugin and a Python MCP script.
Reviewed Wasdubya/x64dbgMCP@e7474e5
Binary · Integration:
SQL interface to IDA Pro databases that exposes a binary's analysis as more than 30 live virtual tables for agents and scripts.
Reviewed allthingsida/idasql@6212ece
Binary · Integration:
Exoproc exposes Windows x64 process inspection and instrumentation to agents through a CLI and MCP server.
Reviewed w0ldan/exoproc@e1d0710
Firmware · Integration:
OpenOCD SPI Dump Plugin guides an agent through extracting SPI flash or EEPROM contents using a target MCU's SWD/JTAG debug connection.
Binary · Integration:
dos-mcp connects AI agents to DOS programs running in js-dos for interactive reverse engineering.
Reviewed abedegno/dos-mcp@344add4
Binary · Integration:
x64dbg MCP gives agents debugger control over Windows binaries through a native x64dbg plugin and a C# stdio MCP server.
Reviewed HxT9/x64dbg_mcp@6fc0891
App · Integration:
adb-mcp gives agents structured Android Debug Bridge tools for investigating app behavior on a device.
Reviewed FlashZ/adb-mcp@8453309
Website · Integration:
website-to-cli is an agent skill for deriving terminal clients from captured website traffic.
App · Integration:
reverse-workbench-skill is a multi-agent-harness skill bundle that routes investigations to workflows for APKs, native binaries, firmware, frontend JavaScript, and network traffic.
App · Integration:
MindNode MCP Server connects agents to MindNode Next mind maps on macOS.
Reviewed jyuwaaw/mindnode-mcp@634bfe9
Binary · Integration:
OGhidra is an AI integration for analyzing binaries with Ghidra through natural language.
Reviewed llnl/OGhidra@4b91e3f
Binary · Integration:
aiDAPal is an IDA Pro plugin that uses a locally hosted language model trained for Hex-Rays pseudocode to assist with code analysis.
Reviewed atredispartners/aidapal@7cc7c34
Binary · Integration:
An MCP server plugin for x64dbg and x32dbg that lets external applications and AI agents control debugging through HTTP.
Reviewed SetsunaYukiOvO/x64dbg-mcp@56fe235
App · Integration:
JEB-MCP is an MCP server and JEB Pro script that lets MCP clients inspect and rename elements of Android apps in JEB.
Reviewed flankerhqd/jebmcp@e2fdb96
Website · Integration:
re-shell is a Nix flake development environment that provides Claude Code with reverse engineering tools and workflows.
Reviewed schlarpc/re-shell@fd9d858
Binary · Integration:
ghidra-rpc is a CLI integration that lets AI coding assistants use a persistent Ghidra session for binary analysis.
Reviewed cellebrite-labs/ghidra-rpc@fa38662
Binary · Integration:
r0idamcp is a single-file MCP server that connects IDA Pro to an MCP-capable assistant for automated reverse engineering.
Reviewed r0ysue/r0idamcp@4b69484
App · Integration:
SOMCP is an Android MCP server for analyzing and modifying native SO libraries.
Reviewed bilieebiliee1-design/SOMCP@62a7583
Website · Project:
The upstream CLI and MCP server for evidence-based investigations of shipped software and runtime behavior.
Reviewed morluto/rea@808339f
Website · Collection:
A task-oriented reverse-engineering resource list by REA's maintainer, useful for broader tools and foundations.
Website · Collection:
A bilingual collection of REA and other AI-assisted reverse engineering cases, with source links and explicit distinctions between reported and reproduced outcomes.
Game · Collection:
Organizes AI-assisted game decompilation, native ports, static recompilation and tooling around stated acceptance checks, alongside a separate track of practitioner write-ups and discussions.
Reviewed yibie/awesome-rea@6df1bc9
Game · Collection:
A moderated website directory of AI-assisted reverse-engineering projects across games, firmware, file formats, APIs and protocols, apps and legacy software.
Reviewed reversedwithai.com/about
Binary · Collection:
A long-running single-README list of malware analysis tools and resources, grouped into 17 top-level sections covering open-source threat intelligence, detection and classification, online scanners and sandboxes, document and shellcode analysis, deobfuscation, debugging and reverse engineering, network, memory forensics, Windows artifacts, plus books and other references.
Firmware · Collection:
A single-README list of security-research references for IoT, embedded, industrial and automotive systems, organized into sections on hardware attacks, wireless protocols (BLE, Zigbee/Z-Wave, LoRa, Matter/Thread, cellular, NFC/RFID, Wi-Fi, USB), firmware security including extraction, static and dynamic analysis and secure boot, network and web protocols, cloud backends, mobile apps, and industrial and automotive topics.
Protocol · Collection:
A single-README list of CAN bus tools, hardware and resources for automotive and embedded work, grouped into sections for reverse-engineering tools, test equipment and simulators, higher-layer protocols (OBD-II, UDS, ISO-TP, J1939, J2534), general and Linux utilities, CAN database formats (DBC, KCD) with converters, and hardware for ARM, Arduino, ESP32, single-board computers and FPGA cores.
Reviewed iDoka/awesome-canbus@77c5913
Protocol · Collection:
A single-README list that gathers links to CAN message identifier and payload decodings in one place, grouped by vehicle make and model under about 30 car brands and brand groups plus BMW, Ducati and KTM motorcycles.
Game · Collection:
An unofficial, bilingual awesome list of what AI agents have reverse-engineered and rebuilt, tagged by whether each case's own sources show that REA was used.
Reviewed AIshihzong/awesome-reverse-engineer-anything@55f9ff0
Game · Collection:
A website and GitHub list of 81 projects that rebuild existing software or games without the original source: AI-built clean-room apps such as the ArtCraft suite, software rewritten with coding agents, AI-assisted game decompilations, game engine reimplementations, human-led decompilations and ports, clean-room classics such as Wine and ReactOS, and tools for rebuilders.
Reviewed a-barzanti/ai-rebuilds@8092b23
Game · Collection:
A single-README list of about 480 game decompilation, recompilation and disassembly projects, grouped by console from the NES and Game Boy to the Xbox 360, PC and mobile, with a large uncategorised section.
Reviewed CharlotteCross1998/awesome-game-decompilations@31e56f7
Game · Collection:
A generated, rated index of public game reconstruction projects: decompilations, disassemblies, static recompilations, source ports, engine remakes and browser ports.
Game · Collection:
A single-README guide to unofficial PC ports of console games built from decompilations or recompilations and chosen for easy installation by players.
Binary · Collection:
A short, link-only reading list on decompiling machine code, last updated in 2023.
App · Collection:
The source repository of remade.wiki, a community-curated directory of open-source reimplementations of closed-source software, mostly creative, productivity and engineering applications.
Reviewed replicraft/remade@ea8119f
Binary · Collection:
A single-README awesome list, started in January 2017 and maintained under the KaliTut name, of 139 reverse-engineering links in 16 sections: books, courses, practice targets, hex editors, binary-format tools, disassemblers, binary analysis, bytecode analysis, import reconstruction, dynamic analysis, debugging, Mac decryption, document analysis, scripting, Android and YARA.
Reviewed wtsxDev/reverse-engineering@b254985
App · Collection:
An awesome list of Android reverse-engineering training, tools and resources started in 2023 by James Stevenson, with 92 one-line entries, 16 of them starred as great and up to date.
Reviewed user1342/Awesome-Android-Reverse-Engineering@0ade43d
App · Collection:
An awesome list of libraries, scripts, tools, talks and articles built on or about Frida, the dynamic instrumentation toolkit, started by David Weinstein in May 2016.
Reviewed dweinstein/awesome-frida@e20da3b
Binary · Collection:
An awesome list of Ghidra scripts, plugins, extensions, learning materials and related services, kept by the Allsafe GitHub organization since December 2019.
Protocol · Collection:
A table-based reading list of 71 research papers on automatic protocol reverse engineering for network protocols, from the Protocol Informatics project (2004) to NetPlier (2021).
Reviewed techge/PRE-list@9c18f7c
Binary · Collection:
Large reverse-engineering link list, auto-exported in 2019 in English and Chinese, with abridged and full README versions.
App · Collection:
A single-README list of Android and iOS application security resources, about 245 links in all, divided by platform into blogs, papers and how-tos, books, courses, tools, deliberately vulnerable lab apps, talks and miscellany.
Binary · Collection:
A single-README list of resources on executable packing, meaning the bundling, compression, encryption, mutation, protection or virtualization of PE, ELF and other executables, including Android apps, and on detecting and unpacking packed files.
Website · Collection:
A single-README, Chinese-language list of AI-assisted reverse-engineering projects, grouped into JavaScript reversing, binary and native analysis, Android and iOS security, and browser automation and traffic analysis.
Reviewed darbra/awesome-ai-reverse@6459523
Binary · Collection:
A sortable, filterable list of 618 plugins, loaders, processor modules and scripts for Hex-Rays' IDA Pro, published as a GitHub Pages table with a static copy generated into the README.
Reviewed vmallet/ida-plugins@825941f
Binary · Collection:
A single-README list, written in July 2025, of 28 MCP servers for reverse-engineering tools, grouped into disassemblers and decompilers (IDA Pro, Ghidra, Binary Ninja and others), debuggers, static and dynamic analysis, network analysis, Android and security testing, with a one-line note per entry.
Reviewed crowdere/Awesome-RE-MCP@e400b88
Binary · Collection:
A single-README list of 71 open-source reverse-engineering tools with a focus on binary analysis, kept as one alphabetical list from Amoco to X86isa.
Reviewed extremecoders-re/re-list@539b60e
Firmware · Collection:
A public-domain directory, started in June 2026, of hacking projects for Teenage Engineering devices: custom firmware, reverse-engineering notes and protocol documentation, tools, hardware mods, teardown and recovery guides and community hubs for the OP-1, OP-Z, OP-XY, TP-7, SP-1 Stem Player, EP series, Pocket Operators and other gear.
Reviewed bnjreece/awesome-te@02c9fb3
Firmware · Collection:
A single-README awesome list of UEFI and BIOS security material, which its maintainer describes as a personal and not comprehensive collection.
Firmware · Collection:
A single-README reading list of 28 academic security papers on firmware and embedded-system analysis, grouped by year from 2013 to 2021.
Firmware · Collection:
OpenDeviceDB indexes devices with existing firmware or protocol reverse-engineering work and links back to source projects.
Reviewed opendevicedb/opendevicedb@0db6a1f
Binary · Collection:
Malware Analysis & CTI Reports collects ten PDF investigations of malware, security tools and binaries with disputed detections.
Game · Collection:
Eric Oakford's archive collects decompiled scripts for Lucasfilm and Humongous Entertainment SCUMM games.
App · Learning resource:
An Electron practice target, Evidence extractor and MCP probe; offline fixture mode is distinguished from real REA analysis.
Reviewed jinshi666888/rea-playbook@0ad65a8
App · Learning resource:
An unofficial, independently run guide to installing REA and connecting it to coding agents, in 32 pages: install paths for npx, npm and Bun including Windows, MCP setup for Claude Code and Desktop, Codex, Cursor, Windsurf and Gemini CLI, a config generator for 24 clients, Ghidra, IDA and JADX provider setup, and troubleshooting pages that match exact error text to upstream REA issues.
Reviewed reaguide.com
Binary · Learning resource:
Free self-paced security courses with learning paths for reverse engineering, firmware and systems foundations.
Reviewed ost2.fyi/Learning-Paths.html
Binary · Learning resource:
Hands-on reverse-engineering module covering functions, data access, static tools and dynamic tools with hosted exercises.
Binary · Learning resource:
Dennis Yurichev's free book on understanding compiled programs and assembly, available in multiple languages.
Reviewed beginners.re
Binary · Learning resource:
Official practical reference for radare2 analysis, disassembly, scripting, debugging and related plugins.
Reviewed book.rada.re
Game · Learning resource:
A walkthrough from the Snowboard Kids 2 decompilation project on attaching gdb-multiarch to the Ares emulator while the matching build still cannot carry debug information.
Reviewed blog.chrislewis.au/finding-jingle-town-debugging-an-n64-…
App · Learning resource:
JPCERT/CC’s 15 October 2026 blog post on the infrastructure behind a series of unauthorized-access incidents in Japan.
Binary · Learning resource:
A free, English lesson index by mytechnotalent that grows almost daily: 490 numbered lessons, most of which have learners write small programs and then debug and patch ("hack") them, across x86, x64, 32/64-bit ARM, RISC-V and AVR.
Binary · Learning resource:
A free English course by Z0F on reverse engineering 64-bit Windows programs, which its README pitches as taking learners from beginner to intermediate.
App · Learning resource:
OWASP’s open manual for Android and iOS app security testing and reverse engineering, published at mas.owasp.org.
Reviewed OWASP/mastg@02ffd85
Binary · Learning resource:
Community wiki explaining how decompilers work, from disassembly, lifting and control-flow recovery to type recovery, control-flow structuring, quality evaluation and neural decompilation, citing the research behind each technique.
Reviewed mahaloz/decompilation-wiki@0133d71
Binary · Learning resource:
Matthieu Breuil’s Synacktiv article explains tool-calling and code-executing agent designs and describes Frontkick, a CodeAct agent that runs generated Python inside Binary Ninja.
Reviewed synacktiv.com/en/publications/ufc-666-frontkick-vs-…
Binary · Learning resource:
Free English reverse-engineering and malware-analysis modules from Mandiant's FLARE team, published as Google Docs, with lab binaries, IDA databases and scripts kept in this repository.
Reviewed mandiant/flare-learning-hub@ebd4e3a
Protocol · Learning resource:
Notes begun by dekuNukem in 2017 and extended by contributors on how the Joy-Con, Pro Controller and parts of the Switch console and dock work, worked out from teardowns, logic-analyzer captures and packet logs.
Reviewed dekuNukem/Nintendo_Switch_Reverse_Engineering@b354f21
App · Learning resource:
Maddie Stone's free English workshop introducing static reverse engineering of Android apps, published as GitHub Pages.
Reviewed maddiestone/AndroidAppRE@17f9eeb
App · Learning resource:
Ivan Rodriguez's free English course (version 1.1) on reverse engineering iOS applications, aimed at beginners in iOS app security.
Reviewed ivRodriguezCA/RE-iOS-Apps@183873a
Binary · Learning resource:
Zhuo Zhang's small educational decompiler for 32-bit RISC-V (RV32I) ELF files, written in Python to teach how decompilation works rather than to compete with production decompilers.
Reviewed ZhangZhuoSJTU/tiny-dec@4f5f1e0
Binary · Learning resource:
A short reading list, compiled by One Thawt mostly in 2015–2016, of about 58 links to reverse-engineering tools, books, papers, talks and blog posts, kept in a README and a separate malware-analysis page.
Game · Learning resource:
A free, English, in-browser course in matching decompilation maintained by Jack Price-Burns: learners read a function's target assembly, write C, and the original console compiler grades the result byte for byte.