Binary · Tool:
8086 Register Command DebuggerC2
8086 Register Command Debugger is an MS-DOS machine-code inspection tool written in 8086 assembly.
- Binary
Binary · Tool:
8086 Register Command Debugger is an MS-DOS machine-code inspection tool written in 8086 assembly.
App · Tool:
advantage is a Windows research tool for inspecting Lenovo Vantage and add-in RPC commands.
Reviewed rtfmkiesel/advantage@fd75e9c
Binary · Tool:
Valkyrie analyzes suspect binaries through static inspection and Docker-based execution.
Reviewed rifatardarslan/Valkyrie@eab7e5e
Binary · Tool:
PE Disassembler is a WPF application that extracts the .text section of 32-bit Windows PE executables and displays decoded x86 instructions.
Reviewed ddeeduck/Pe-disassembler@089a567
Binary · Tool:
SIC/XE Disassembler and Linking Loader converts SIC/XE object code into assembly listings and reconstructed symbols.
Reviewed MN294/SICXE-Disassembler@60726b6
App · Tool:
Malware Deobfuscator analyzes obfuscated malware scripts and generates code, behavior and indicator reports.
Binary · Tool:
flashkit is a Python toolkit for examining Adobe Flash SWF files and AVM2 bytecode.
Reviewed bitalizer/pyflashkit@e50946b
Binary · Tool:
Kaiju is a Rust reverse-engineering framework with a headless CLI for binary loading and analysis.
Reviewed nightwarelabz/kaiju@86572f2
App · Tool:
sqlce reads SQL Server Compact .sdf database files using a cross-platform C++ parser informed by analysis of decompiled SQL CE components.
Reviewed boykopovar/sqlce@78a3888
App · Tool:
inkterop converts native handwriting files from note apps and e-ink devices through a documented intermediate representation.
Reviewed cable729/inkterop@f16eb8d
Binary · Tool:
wMatcher compares two Java archives to match classes renamed or obfuscated between releases.
Reviewed earthsworth/wMatcher@225940a
Binary · Tool:
tasm-rs implements TVM bytecode assembly and disassembly in Rust, with a tdisasm CLI, instruction tables, Fift parsing and trace and coverage reports.
Reviewed nktkt/tasm-rs@b9ed7d9
Binary · Tool:
Sogen Dart bindings expose Windows and Linux binary emulation through a Dart FFI package and native bridge.
Reviewed Wdestroier/sogen_dart@17a7b46
App · Tool:
cupertino-files is a TypeScript library for reading and writing modern Apple Pages, Numbers, and Keynote documents.
Binary · Tool:
PackerScope scans Windows PE executables for packer signatures and structural indicators, including entropy, sections, imports and entry-point instructions.
Reviewed salmanmallah/packerscope@db2ea6d
Binary · Tool:
imprint analyzes Windows PE files by parsing import, delay-import and export directories without executing the image.
Reviewed hamodywe/imprint@b63df33
Binary · Tool:
kdemulator executes Windows x86-64 kernel-driver binaries outside a live kernel for IOCTL analysis.
Reviewed 000nico/kdemulator@44c0521
Binary · Tool:
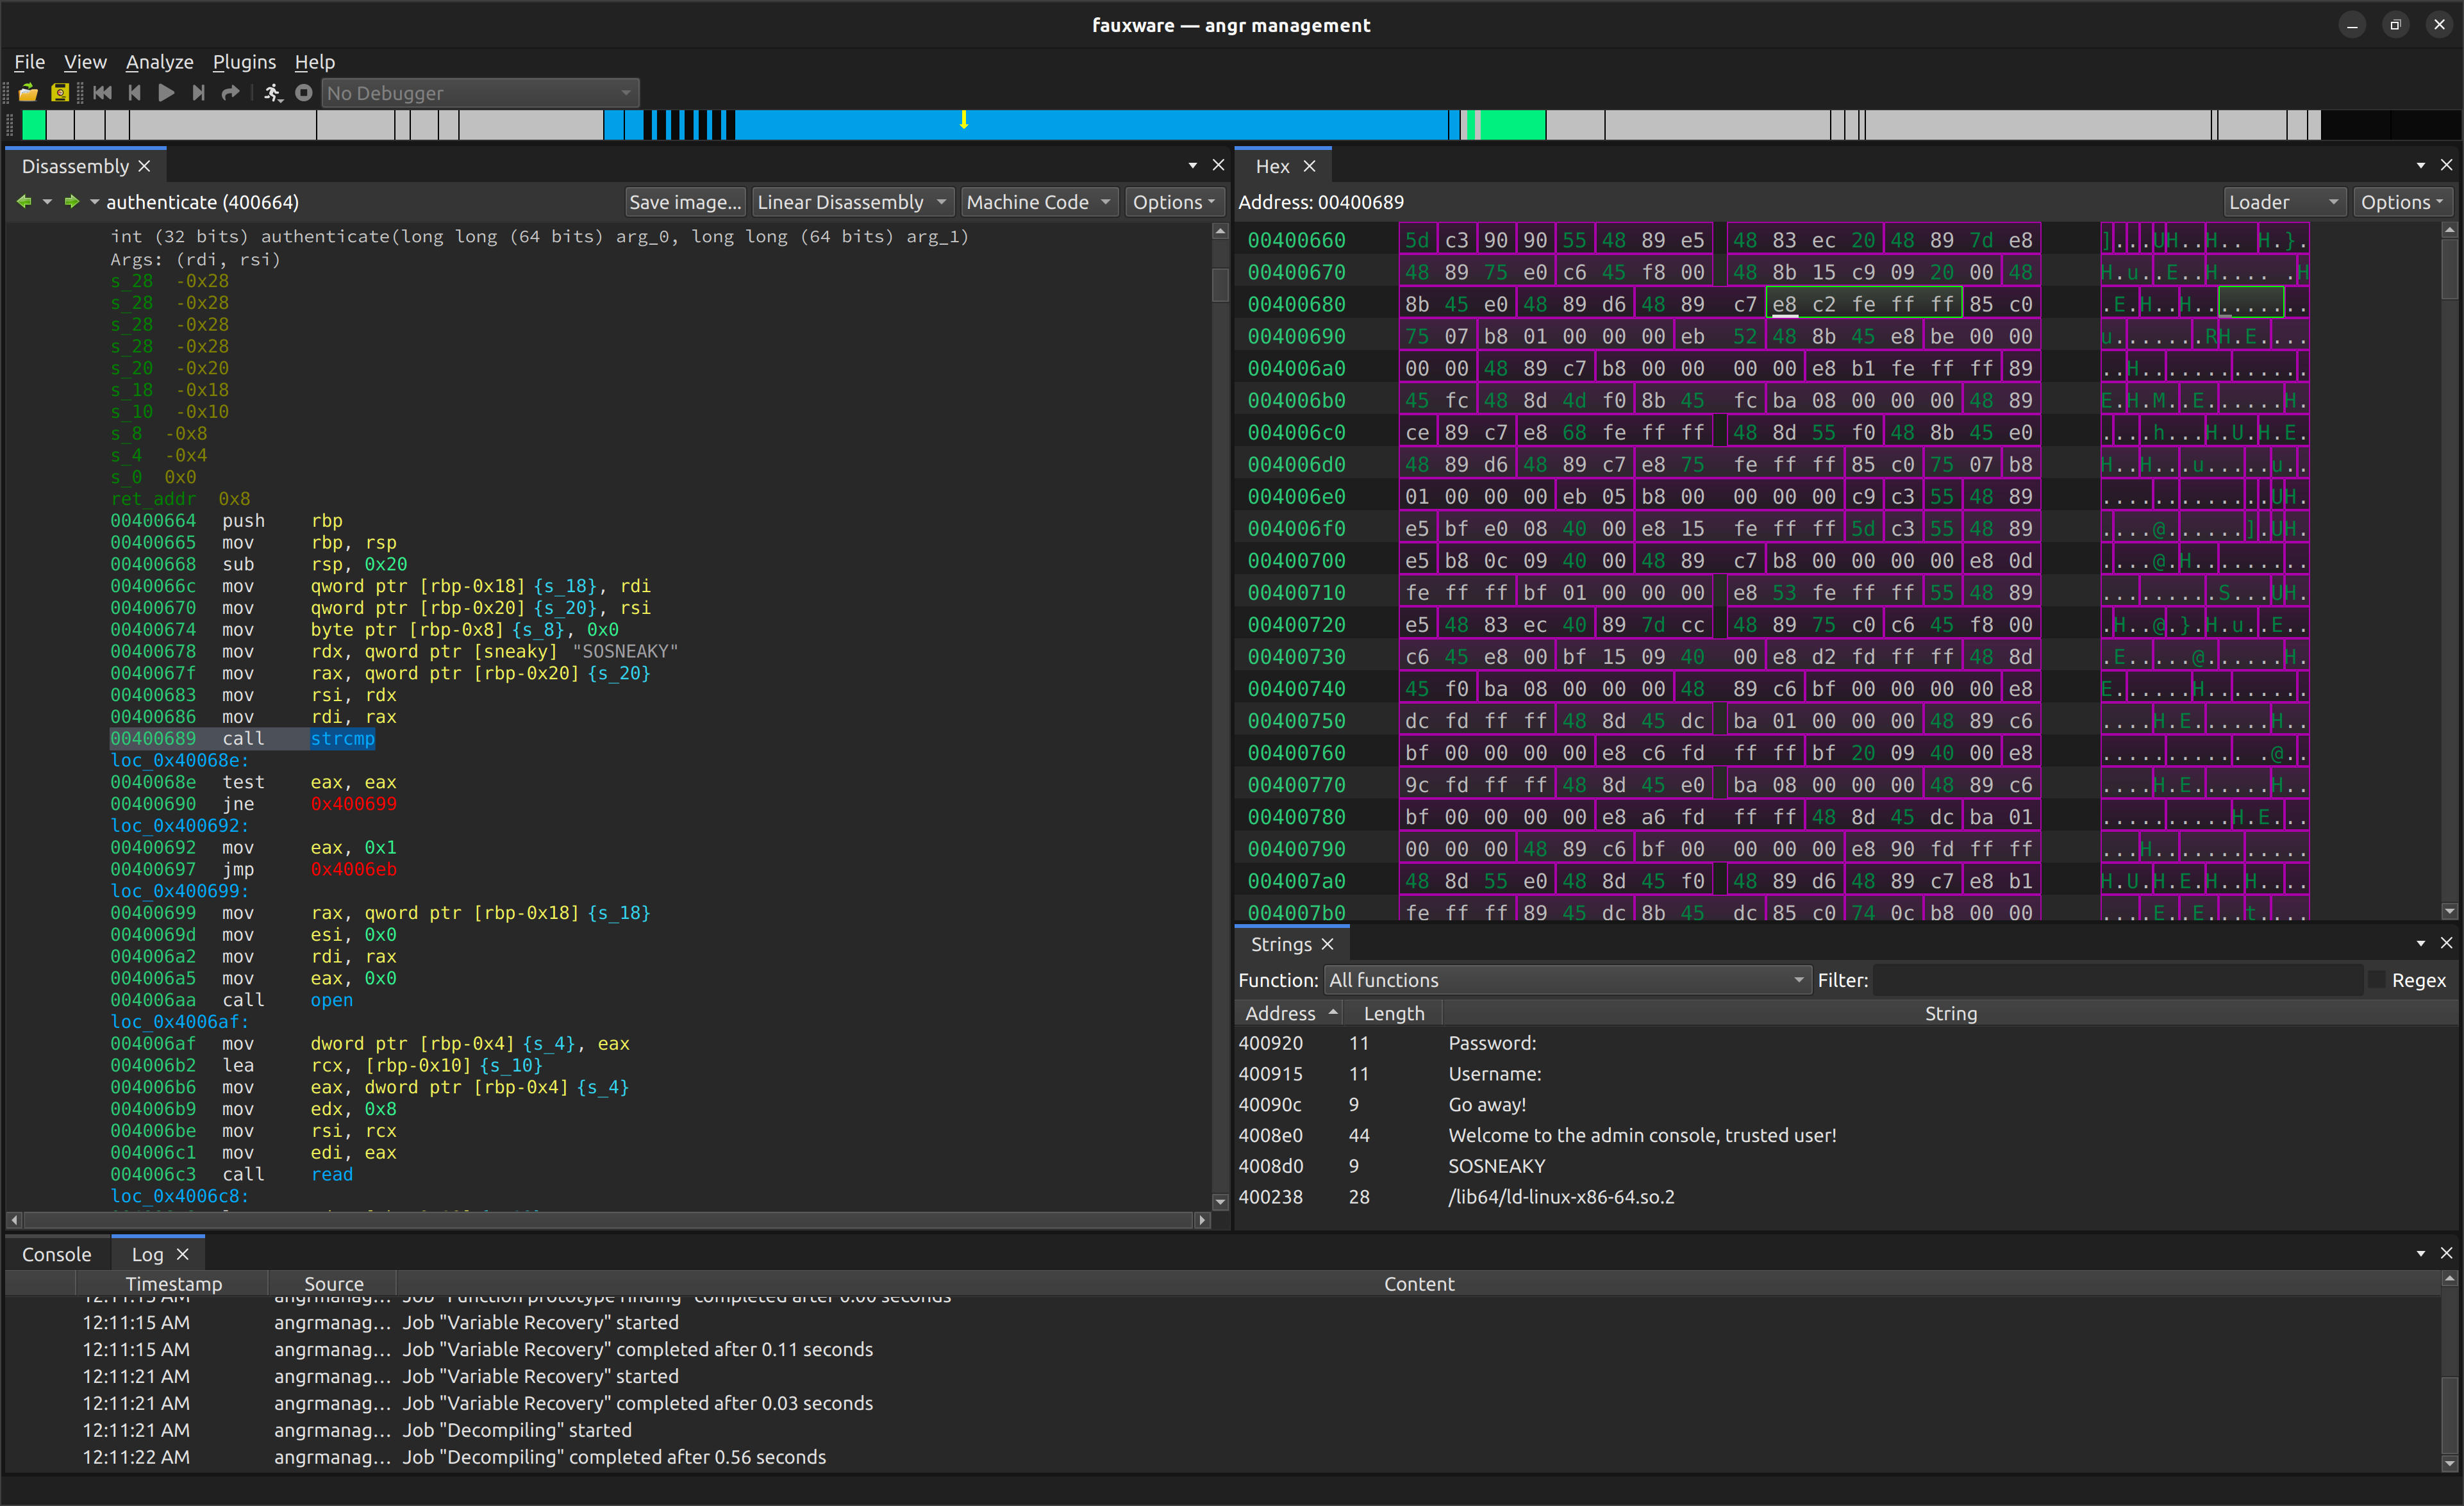
Cross-platform graphical binary analysis tool powered by the angr platform, with disassembly and decompilation views.
Reviewed angr/angr-management@1af4c02
Binary · Tool:
QIRA is a tool for examining program execution traces.
Reviewed geohot/qira@5f34406
Binary · Tool:
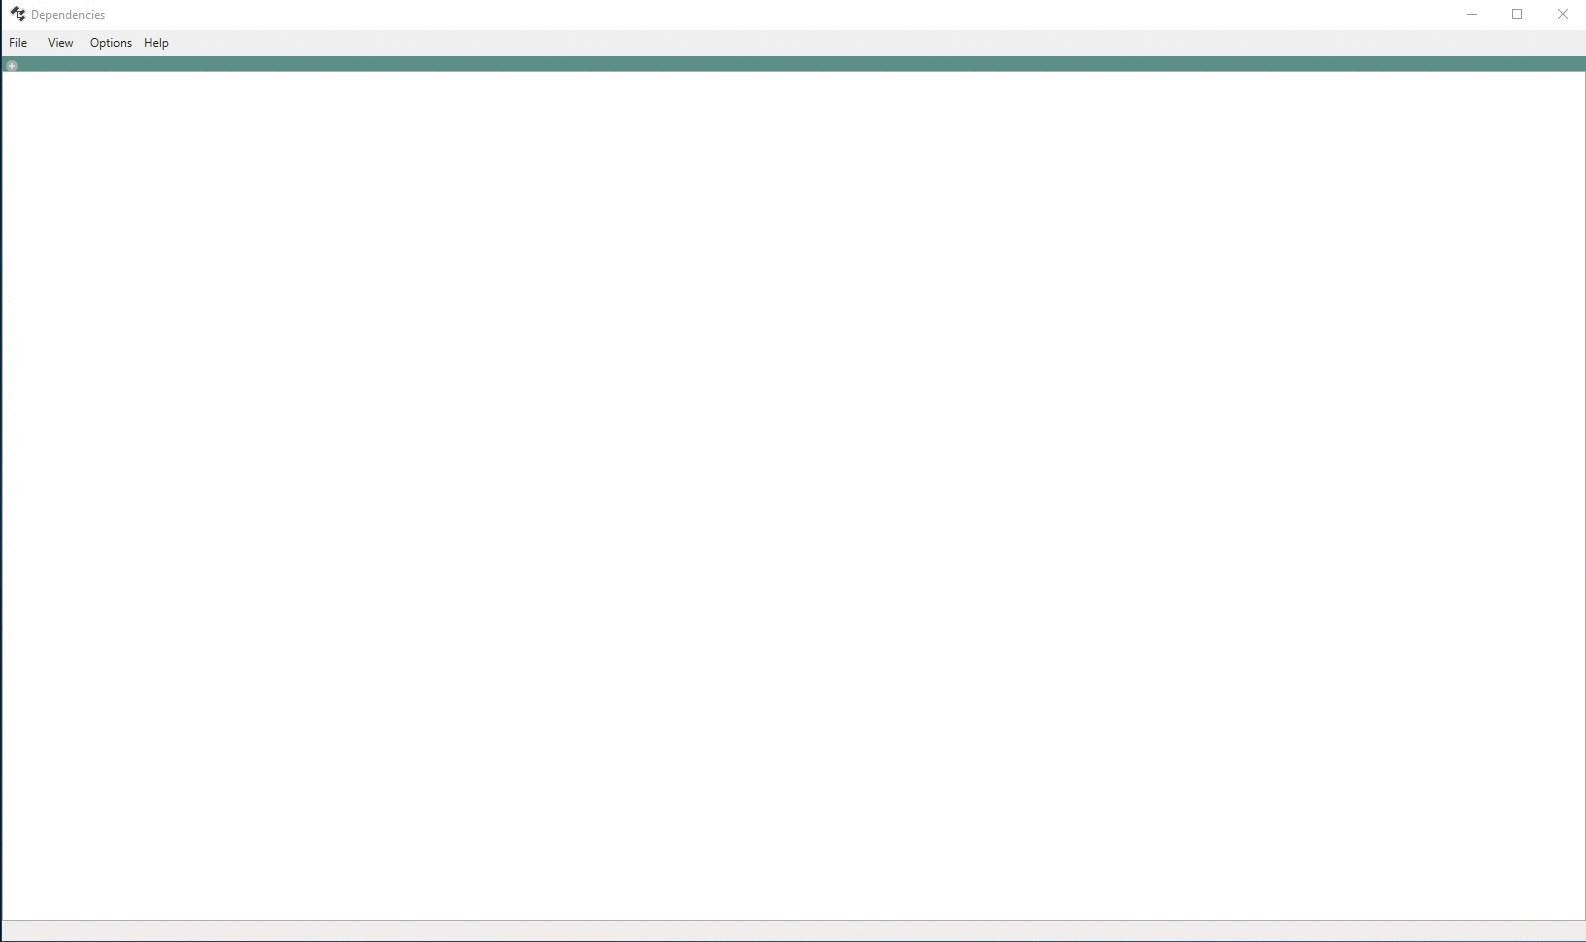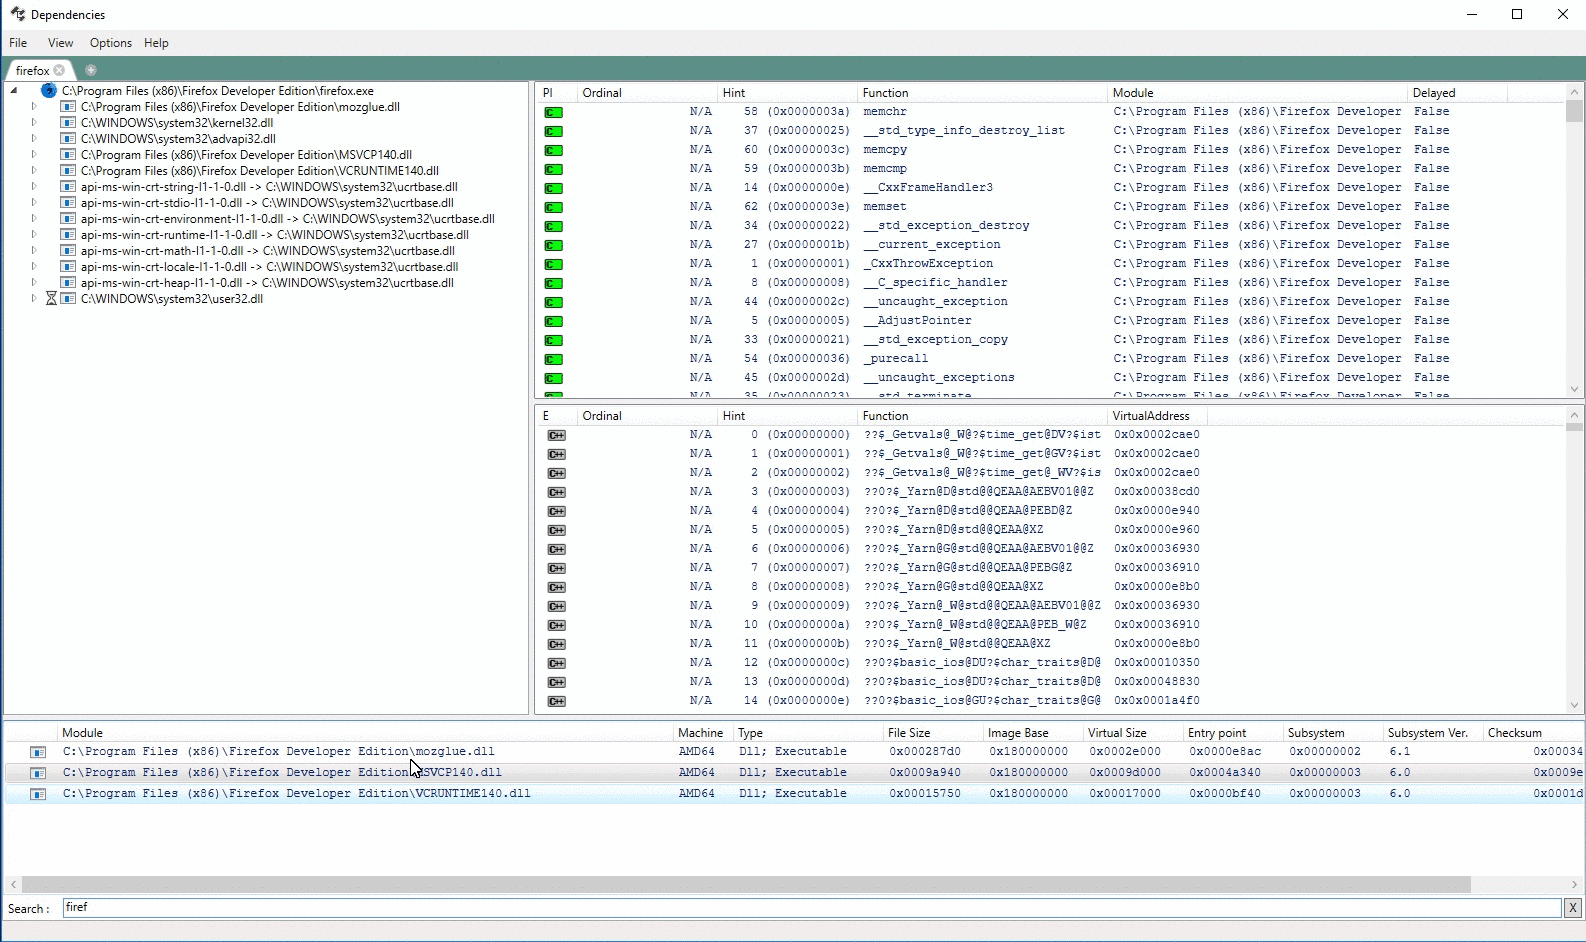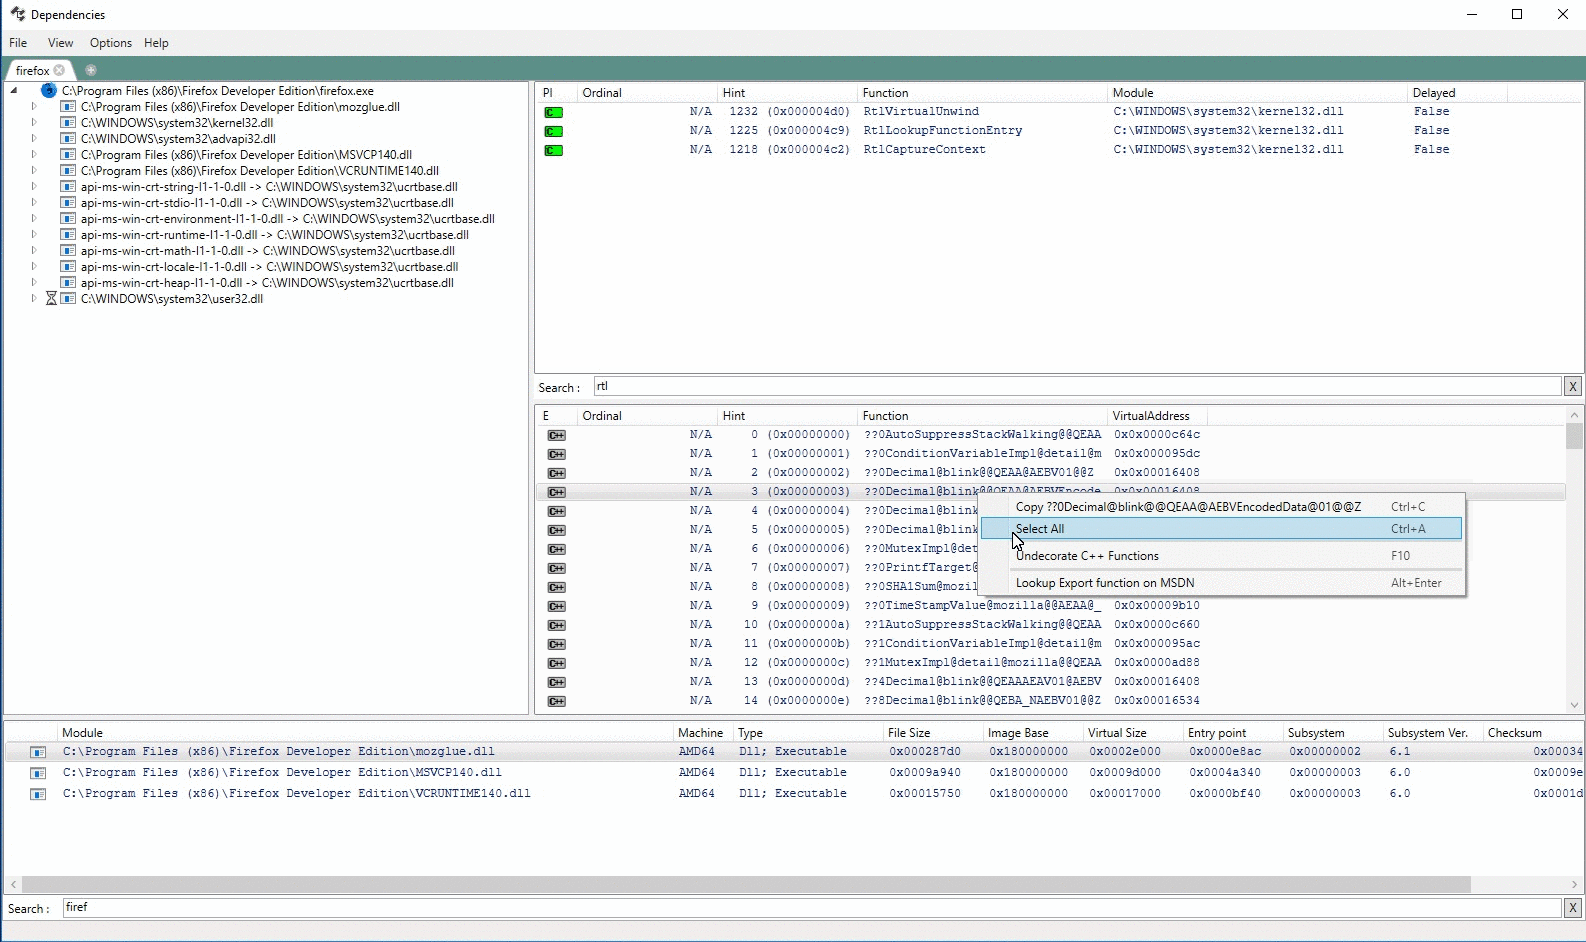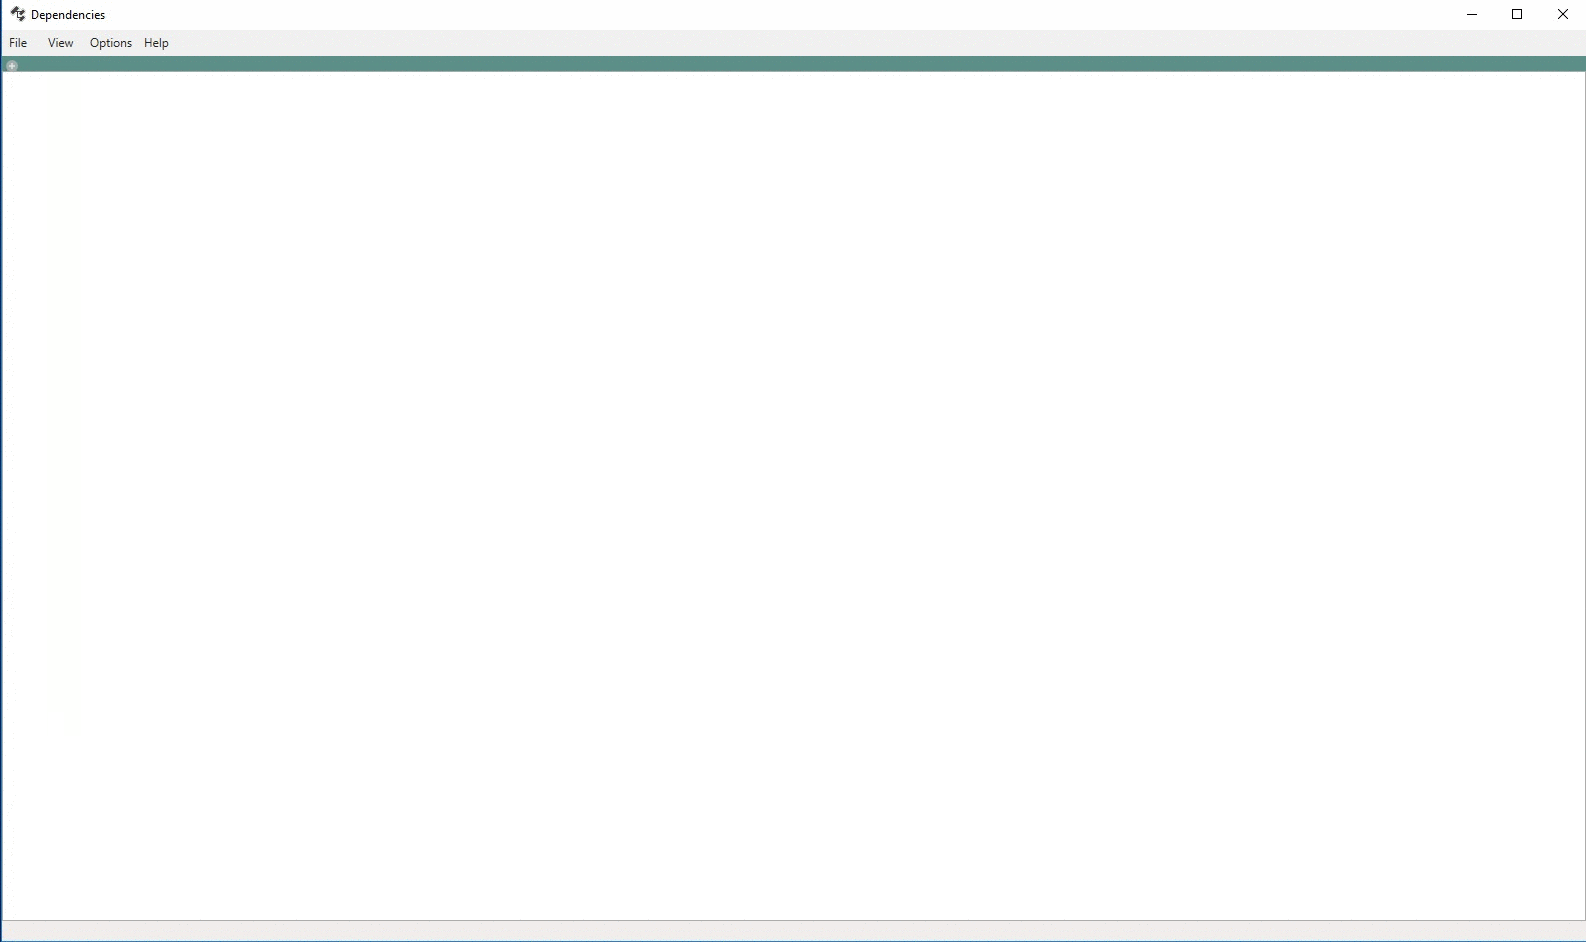
Dependencies is a Windows PE dependency analysis tool with command-line and graphical interfaces.
Reviewed lucasg/Dependencies@1997a40
Binary · Tool:
Hachoir is a Python library for viewing and editing binary streams as trees of fields, down to individual bits.
Reviewed vstinner/hachoir@685b298
Binary · Tool:
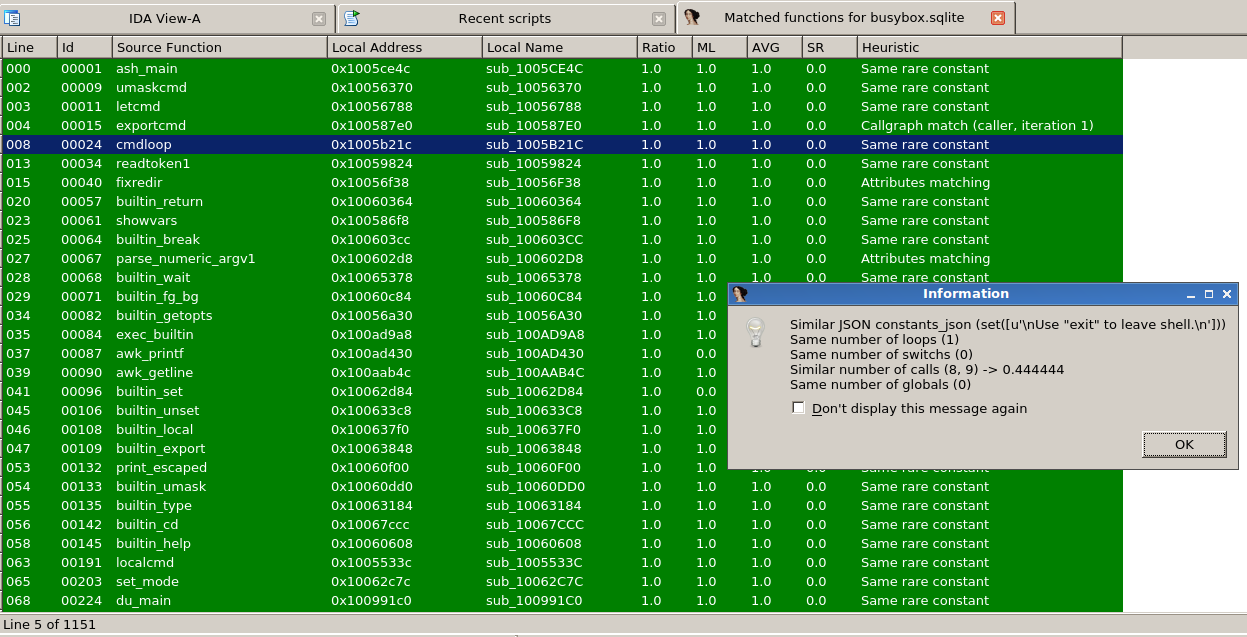
Pigaios is a tool that matches C source code against binaries in IDA.
Reviewed joxeankoret/pigaios@8807972
Binary · Tool:
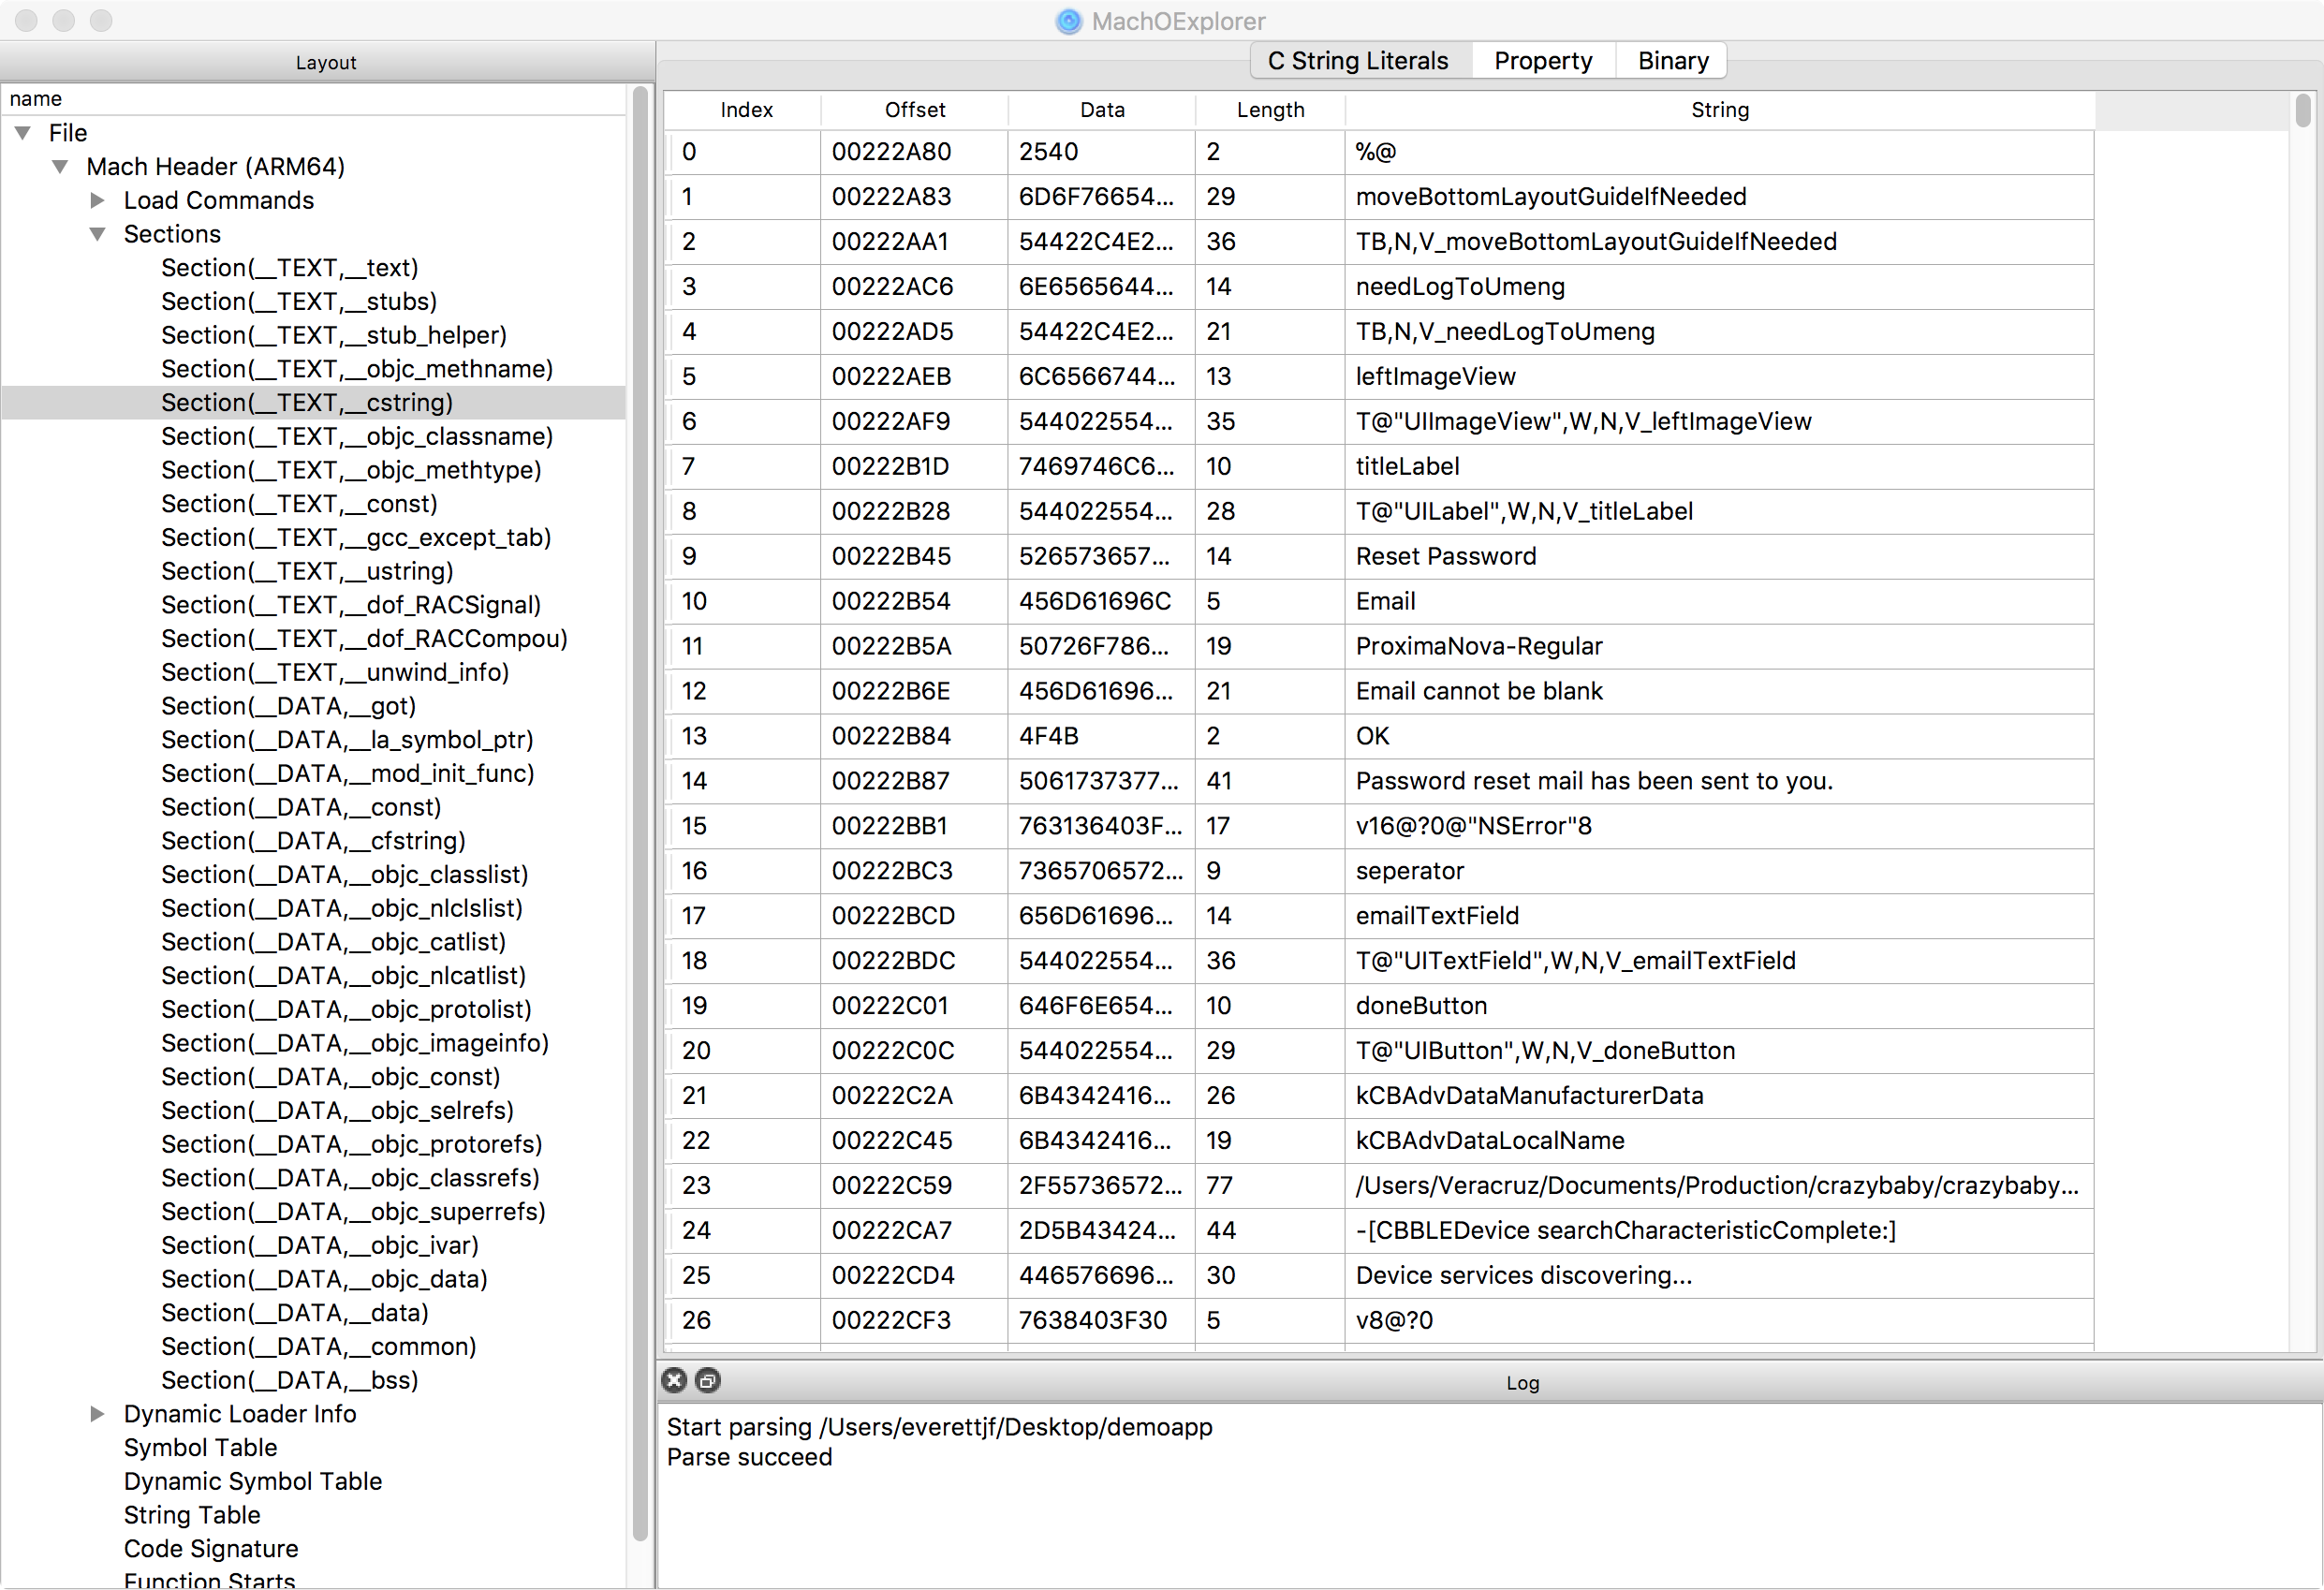
MachOExplorer is a desktop and command-line tool for inspecting Mach-O binaries, Universal binaries, static archives, and dyld shared caches.
Reviewed everettjf/machoexplorer@cd612d7
App · Tool:
FLEX is an in-app tool for exploring and debugging running iOS applications.
Reviewed FLEXTool/FLEX@dac6130
App · Tool:
classdump-dyld is a command-line tool that generates Objective-C headers from Mach-O app binaries, libraries, frameworks, bundles, and images in the dyld shared cache.
Reviewed limneos/classdump-dyld@31b6f9d
Binary · Tool:
Process Dump is a Windows command-line tool that saves code from running processes to disk for malware analysis.
Reviewed glmcdona/Process-Dump@e4373c6
Binary · Tool:
mal_unpack is a Windows dynamic unpacker based on PE-sieve.
Reviewed hasherezade/mal_unpack@cecb9ee
Binary · Tool:
Bloaty is a binary size profiler that attributes file and memory usage to sources such as symbols, compilation units, and sections.
Reviewed google/bloaty@ccb49b0
Binary · Tool:
bingrep is a command-line tool for inspecting and colorizing binary files.
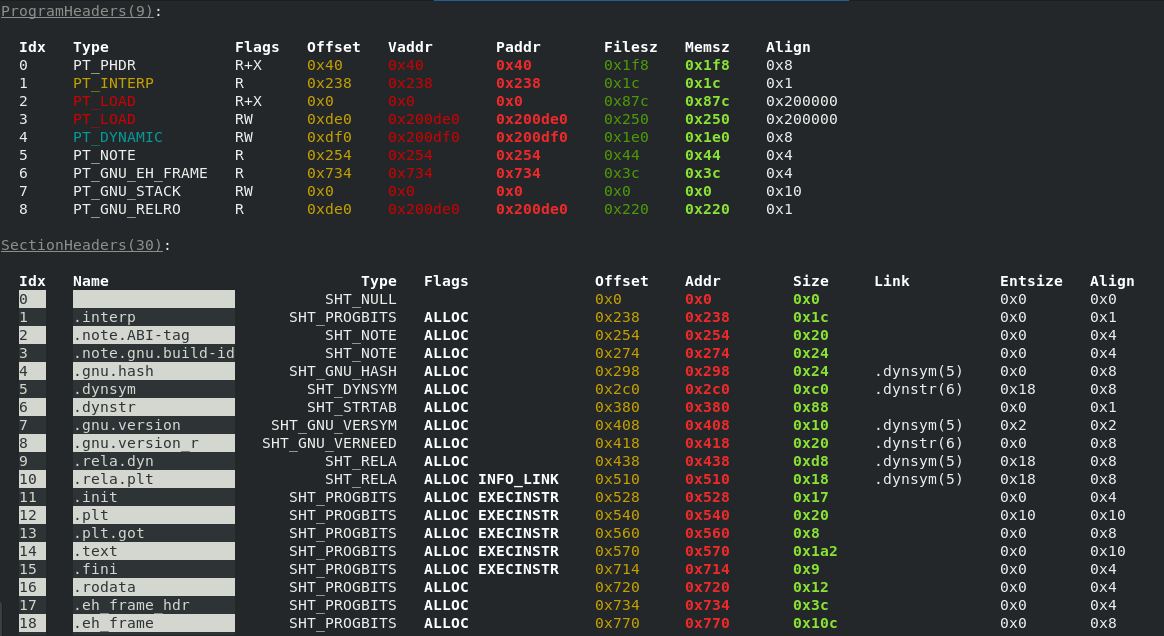
Reviewed m4b/bingrep@99d1054
Binary · Tool:
libPeConv is a Windows library for loading and manipulating PE files.
Reviewed hasherezade/libpeconv@0fc25f6
Binary · Tool:
Viper is a framework for binary analysis and for organizing malware samples, exploit samples, and research scripts.
Reviewed viper-framework/viper@fdd7855
Binary · Tool:
Cuckoo3 is a malware analysis tool that tests suspicious files and links in sandboxed platform emulators.
Reviewed cert-ee/cuckoo3@86be764
Binary · Tool:
Cuckoo Sandbox is an automated malware analysis system that executes suspicious files in an isolated environment and reports their behavior.
Reviewed cuckoosandbox/cuckoo@50452a3
Binary · Tool:
fq is a command-line tool and query language for inspecting and decoding binary formats.
Reviewed wader/fq@3f518c8
Binary · Tool:
Unpacks Inno Setup installers on non-Windows systems without running them.
Reviewed dscharrer/innoextract@6e9e34e
Binary · Tool:
Metasm is a Ruby suite for assembling, disassembling, debugging, and modifying executable binaries.
Reviewed jjyg/metasm@a70271c
App · Tool:
Pure Python 3 library and command-line tool for communicating with iPhones, iPads and other iOS devices from Windows, Linux or macOS, implementing usbmux, lockdown and its services, DTX-based developer (DVT) services and the RemoteXPC tunnels that iOS 17+ uses for developer access.
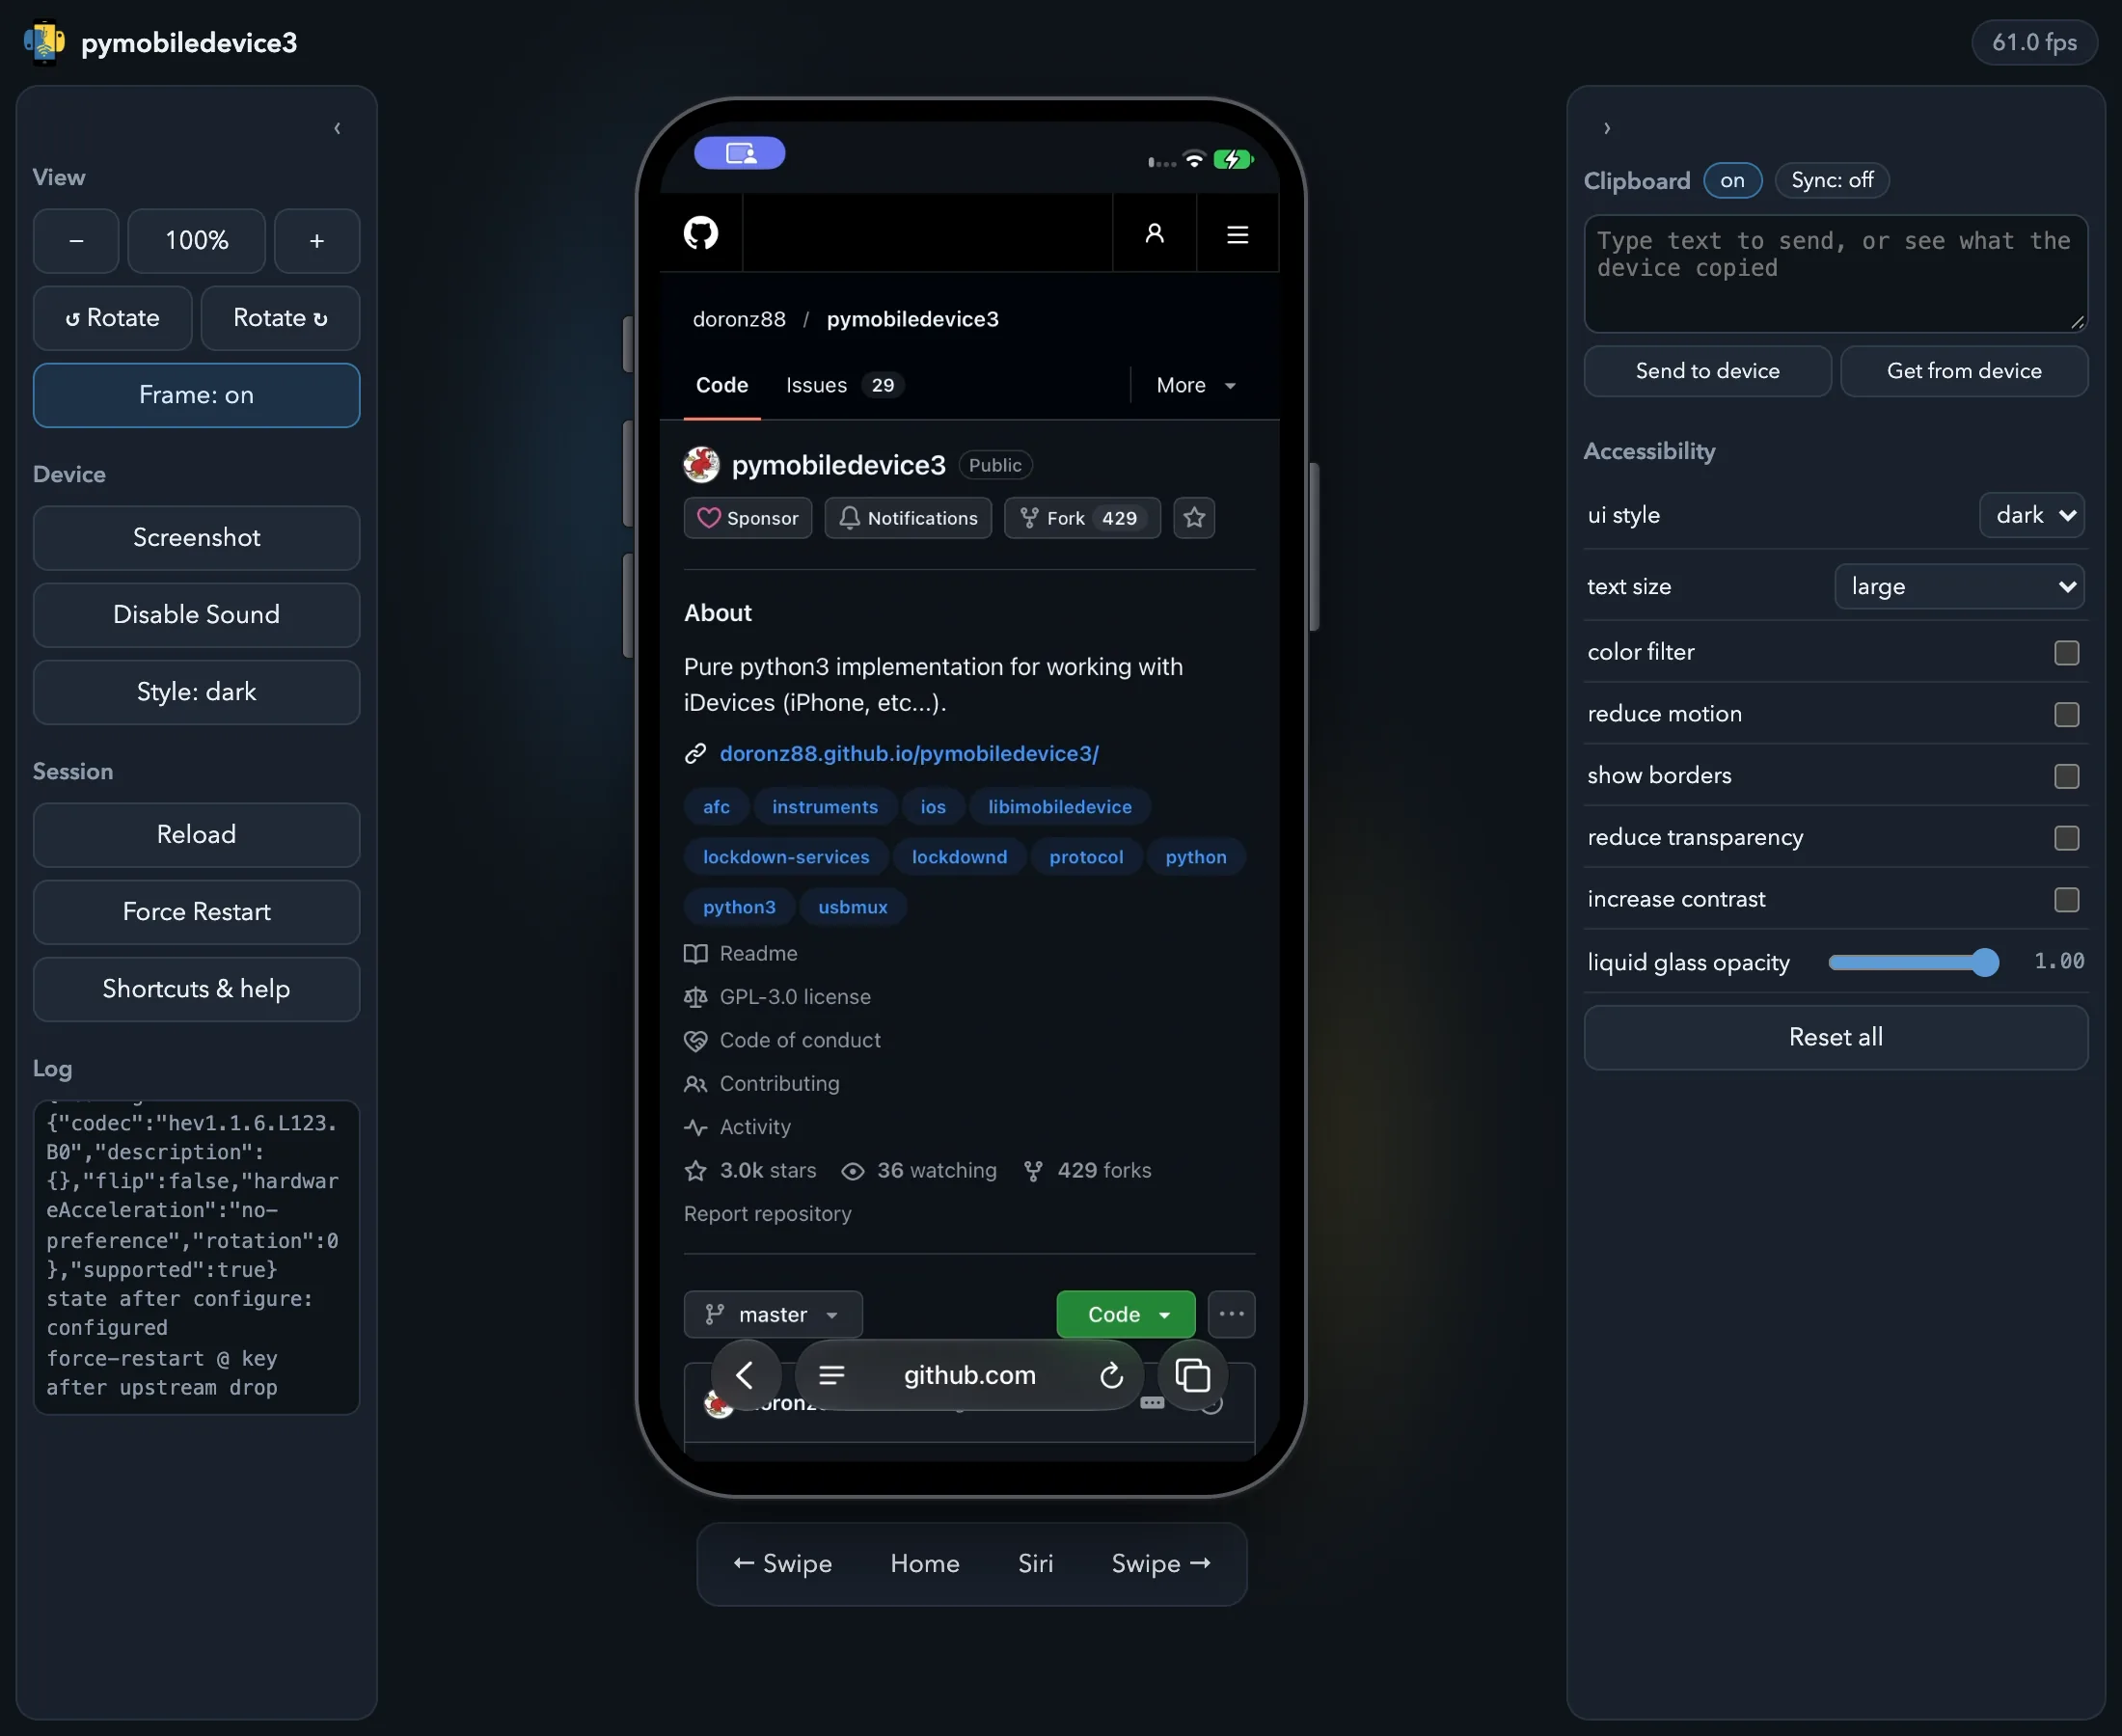
Reviewed doronz88/pymobiledevice3@9ea9491
Binary · Tool:
Python library that emulates user-mode code from minidumps of 64-bit and 32-bit Windows processes with Unicorn.
Reviewed mrexodia/dumpulator@18a64d7
Binary · Tool:
Archived Trail of Bits executable lifter that translates 32- and 64-bit Linux ELF and Windows PE binaries into LLVM bitcode for analysis or recompilation.
Reviewed lifting-bits/mcsema@2636805
Binary · Tool:
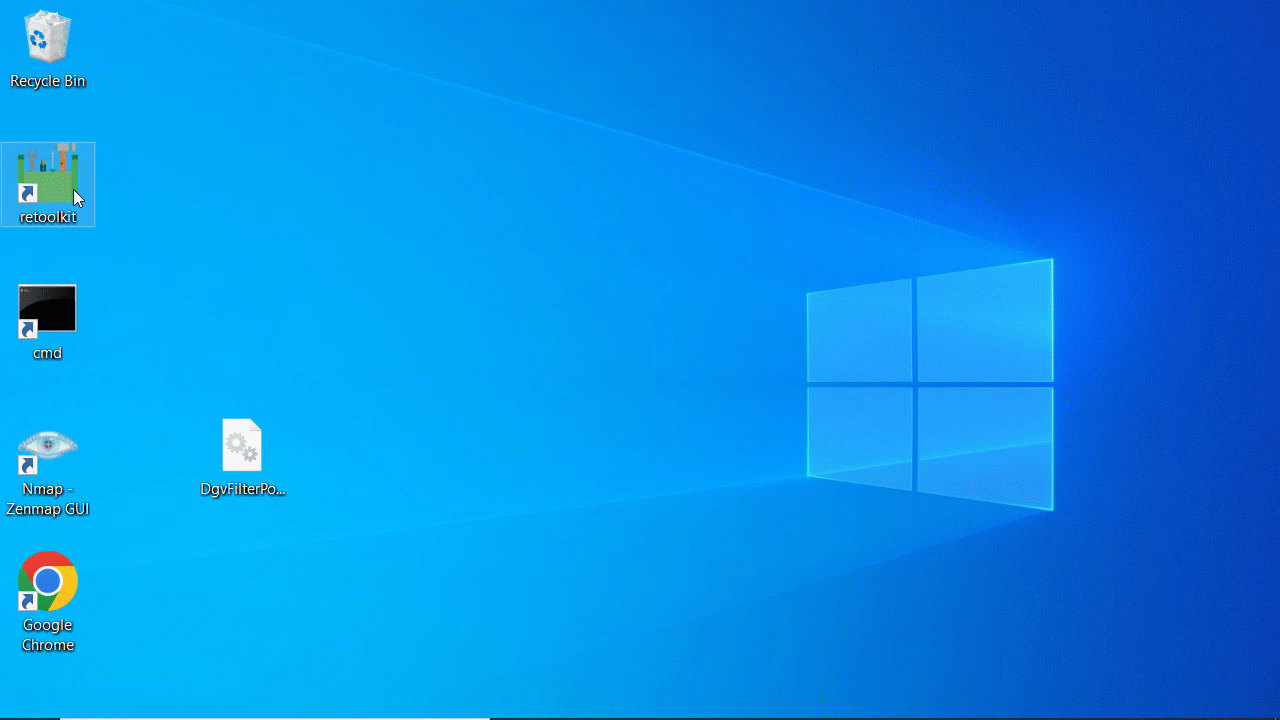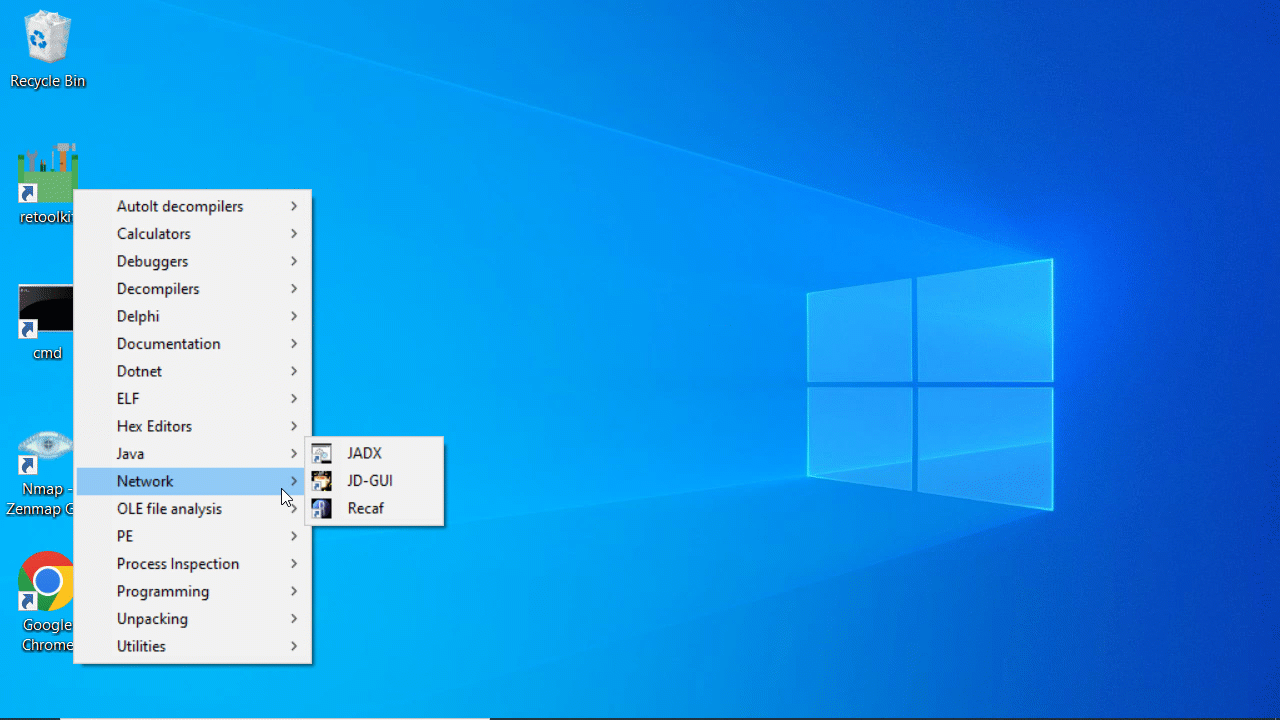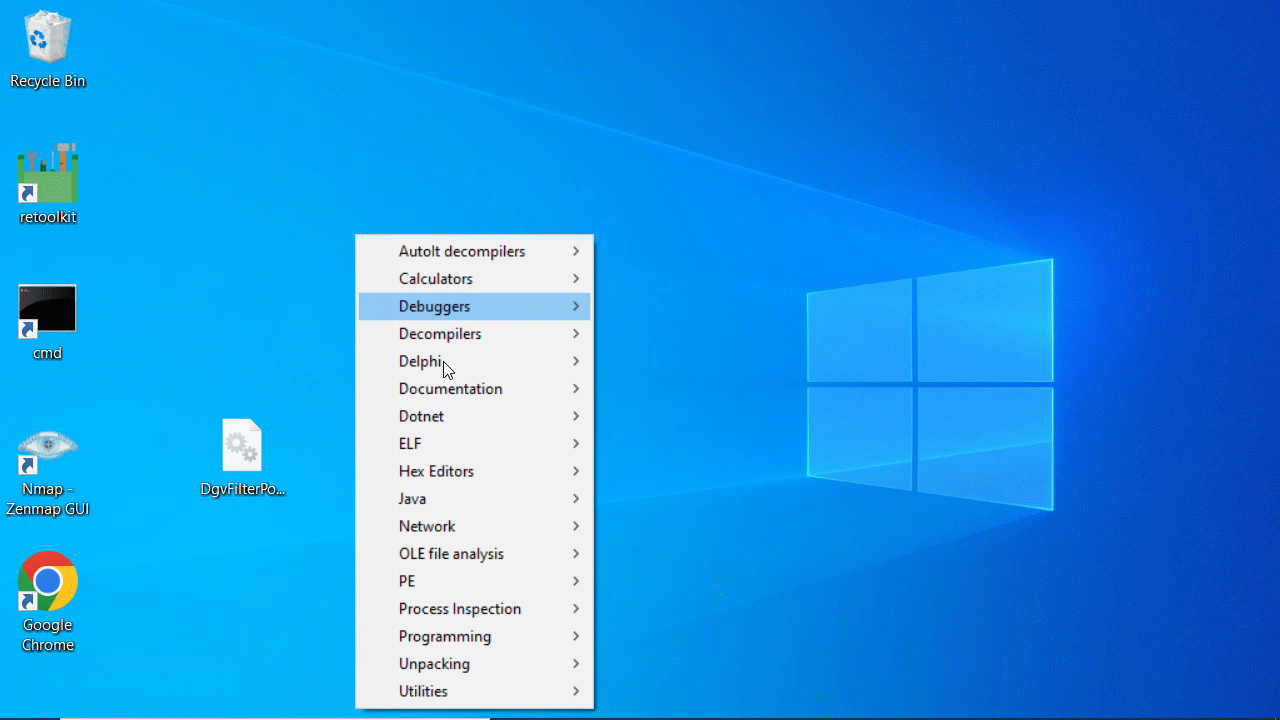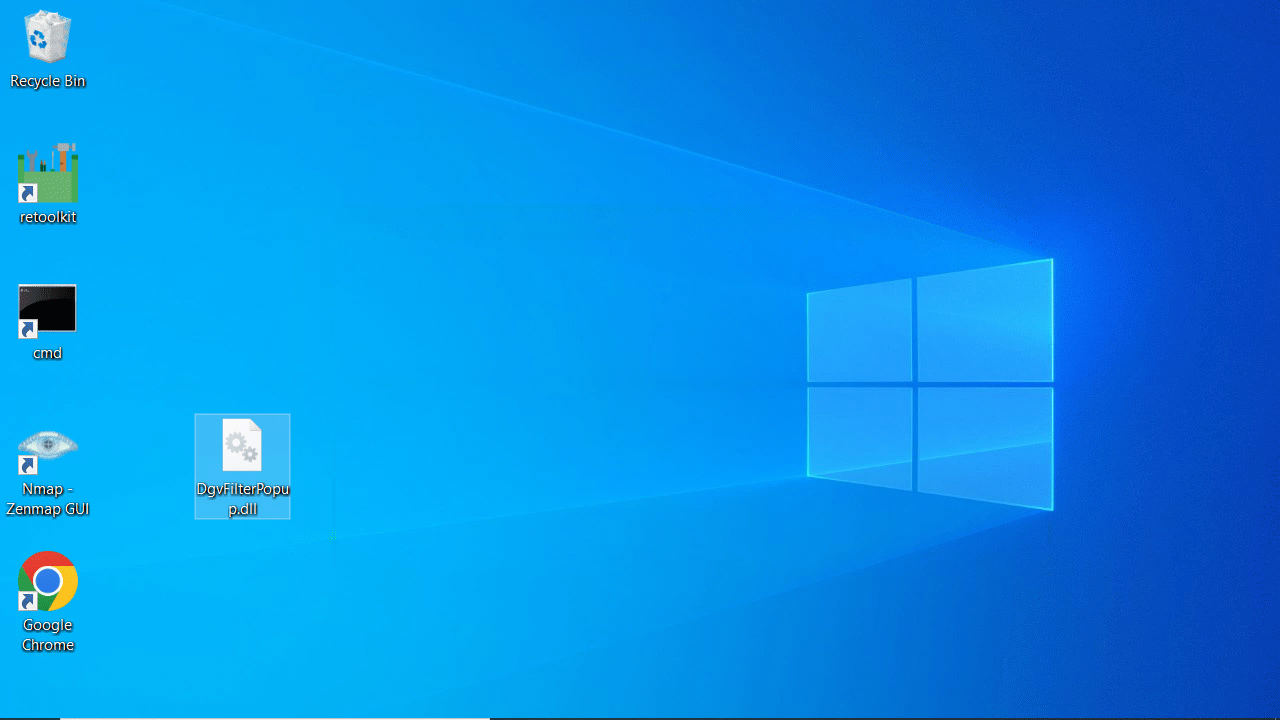
Windows setup program, built with Inno Setup, that installs a ready-made x86/x64 reverse-engineering and malware-analysis toolkit as selectable components: debuggers, decompilers, hex editors, PE, ELF, .NET, Java, Go, Delphi and AutoIt analyzers, and process-inspection, unpacking, network, OLE/PDF and signature tools.
Reviewed mentebinaria/retoolkit@8a5d119
Binary · Tool:
A refactored, updated fork of Boris Batteux's D-810 IDA Pro plugin that deobfuscates code at decompilation time by rewriting Hex-Rays microcode.
Reviewed w00tzenheimer/d810-ng@2e59ab4
Binary · Tool:
Trail of Bits machine-code lifter built on Remill that aims to produce high-quality LLVM bitcode, close to what Clang would emit for a semantically equivalent C function, for Rellic to decompile further into C.
Reviewed lifting-bits/anvill@9948d26
Binary · Tool:
A Python plugin for IDA Pro from Google's FLARE team that adds a custom navigation interface.
Reviewed mandiant/xrefer@1aeda16
App · Tool:
Python wrapper around a prebuilt copy of Derek Selander's dsdump, an improved nm and Objective-C and Swift class-dump for Mach-O binaries, that writes each dumped protocol, class, category and Swift type to its own .h or .swift file instead of a single console stream.
Reviewed paradiseduo/dsdump@16b15c6
Binary · Tool:
Instrument running application binaries to diagnose invalid memory access, uninitialized reads, use-after-free and leaks.
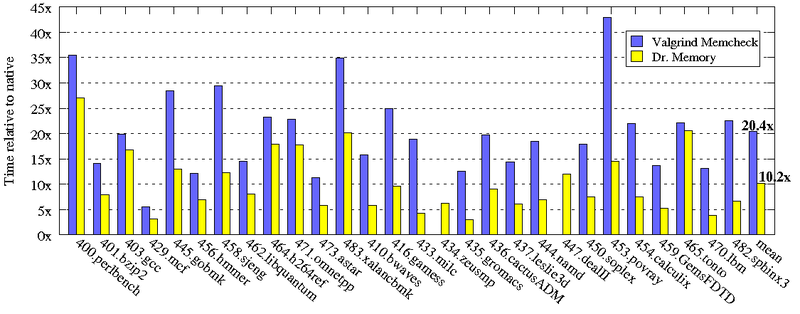
Reviewed DynamoRIO/drmemory@3d2b5f9
Binary · Tool:
Encode and decode x86 instructions through Intel’s library and example analysis utilities.
Reviewed intelxed/xed@0bcb623
Binary · Tool:
Assemble instruction text into machine code through a common API covering x86, Arm, MIPS and other architectures.
Reviewed keystone-engine/keystone@0d9567f
Binary · Tool:
Monitor Windows API calls by embedding instrumentation into a program’s execution path.
Reviewed microsoft/Detours@1dbd4ea
Binary · Tool:
Record and replay whole-system execution for repeated inspection, plugin analysis and dynamic taint tracking.
Reviewed panda-re/panda@3650211
Binary · Tool:
Inspect PE headers, sections, resources and malformed values through a Python API with limited in-place editing.
Reviewed erocarrera/pefile@274e0b8
Binary · Tool:
Trace how parser functions consume input bytes by rebuilding programs with LLVM data-flow instrumentation and inspecting the resulting trace.
Reviewed trailofbits/polytracker@ae7b5f1
Binary · Tool:
Parse ELF executables and DWARF debugging information from Python for scripted binary inspection.
Reviewed eliben/pyelftools@beedcc4
Binary · Tool:
Turn mangled Rust symbols into readable names for symbol inspection and binary-analysis tooling.
Reviewed rust-lang/rustc-demangle@7778bc9
Binary · Tool:
Inspect and rebuild x86/x64 PE import tables and repair process dumps during executable analysis.
Reviewed NtQuery/Scylla@e87fd57
Binary · Tool:
Embed a Windows debugging engine with breakpoint, exception, process-dump and import-reconstruction support.
Reviewed x64dbg/TitanEngine@947ad61
Binary · Tool:
Inspect operating-system memory samples to recover processes, modules and other runtime artifacts through forensic plugins.
Binary · Tool:
FoxDec is a research decompiler for formally checked lifting of x86-64 binaries to recompilable NASM.
Reviewed ssrg-vt/FoxDec@d9206ef
Binary · Tool:
Dragodis is a Python framework for writing disassembler scripts that run on more than one disassembler.
Binary · Tool:
MBBSDASM is a C# disassembler for 16-bit New Executable (NE) EXE and DLL files, written with .NET Core.
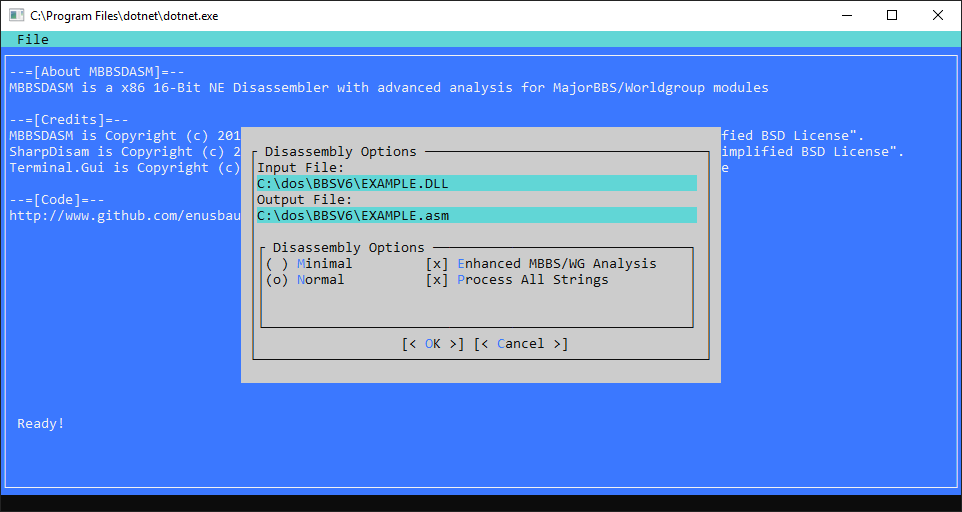
Reviewed mbbsemu/MBBSDASM@52dc12a
Binary · Tool:
blc, the Binary Lifting Contraption, is an IDA Pro plugin that integrates Ghidra's decompiler and shows a source view for platforms supported by both IDA and Ghidra.
Reviewed cseagle/blc@ac38069
Binary · Tool:
IDA BPF Processor is a Python processor and loader for classic BPF bytecode in IDA.
Reviewed bnbdr/ida-bpf-processor@d1ced37
Binary · Tool:
Disassembler library for x86 and x86-64.
Reviewed vmt/udis86@56ff6c8
Binary · Tool:
Quick Assembler is a Windows application for editing x86 and x64 assembly, assembling it with NASM or Keystone in 16-bit, 32-bit, or 64-bit mode, and running it in the Unicorn emulator with breakpoints, registers, and memory views.
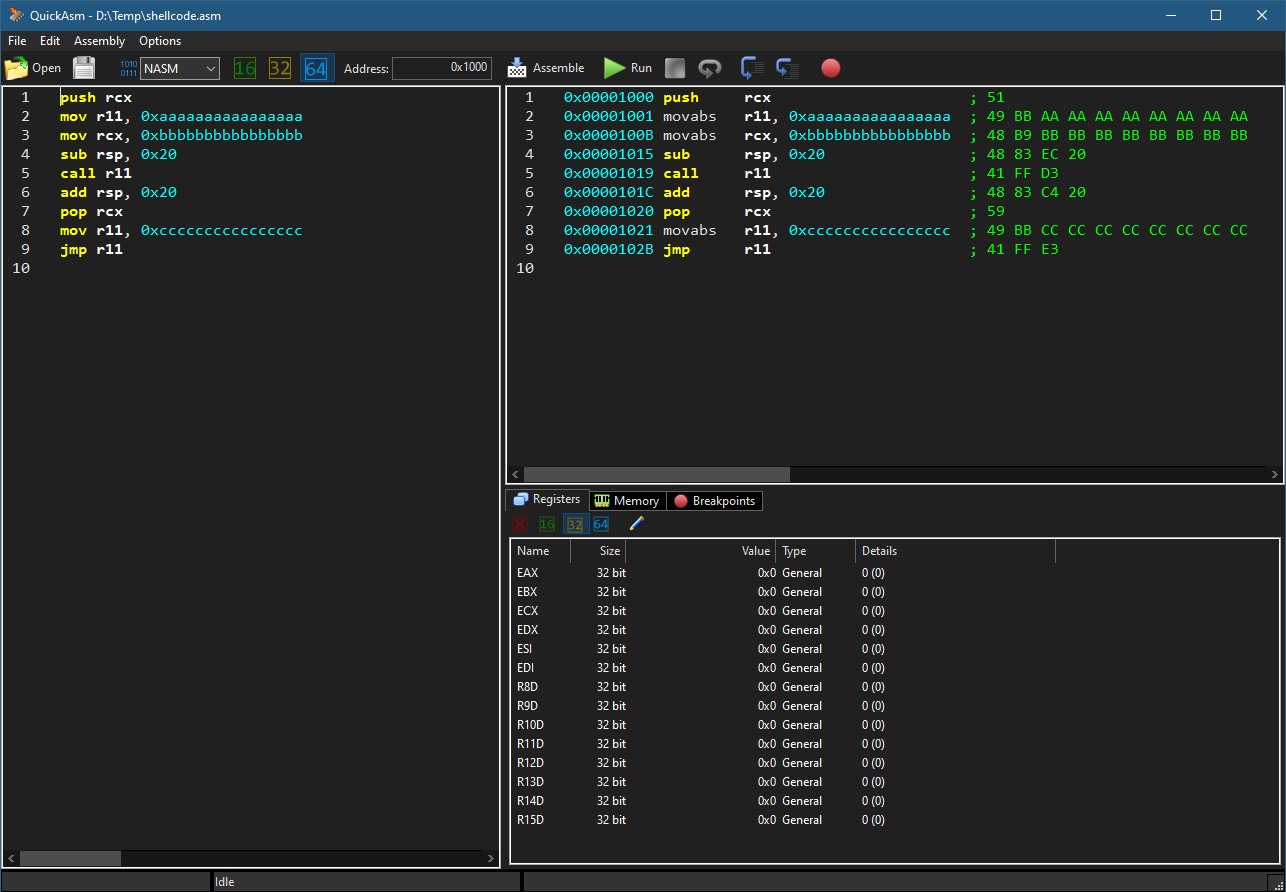
Reviewed zodiacon/QuickAsm@27955fc
Binary · Tool:
HLSL Decompiler translates DXBC for shader model 5.x or lower, DXIL for shader model 6.x, and SPIR-V into HLSL.
Reviewed YYadorigi/HLSL-Decompiler@5a80336
Binary · Tool:
Windows x64 WinDbg extension that resolves a function by name or address, reconstructs a control-flow view, and asks an LLM from the extension to produce pseudocode.
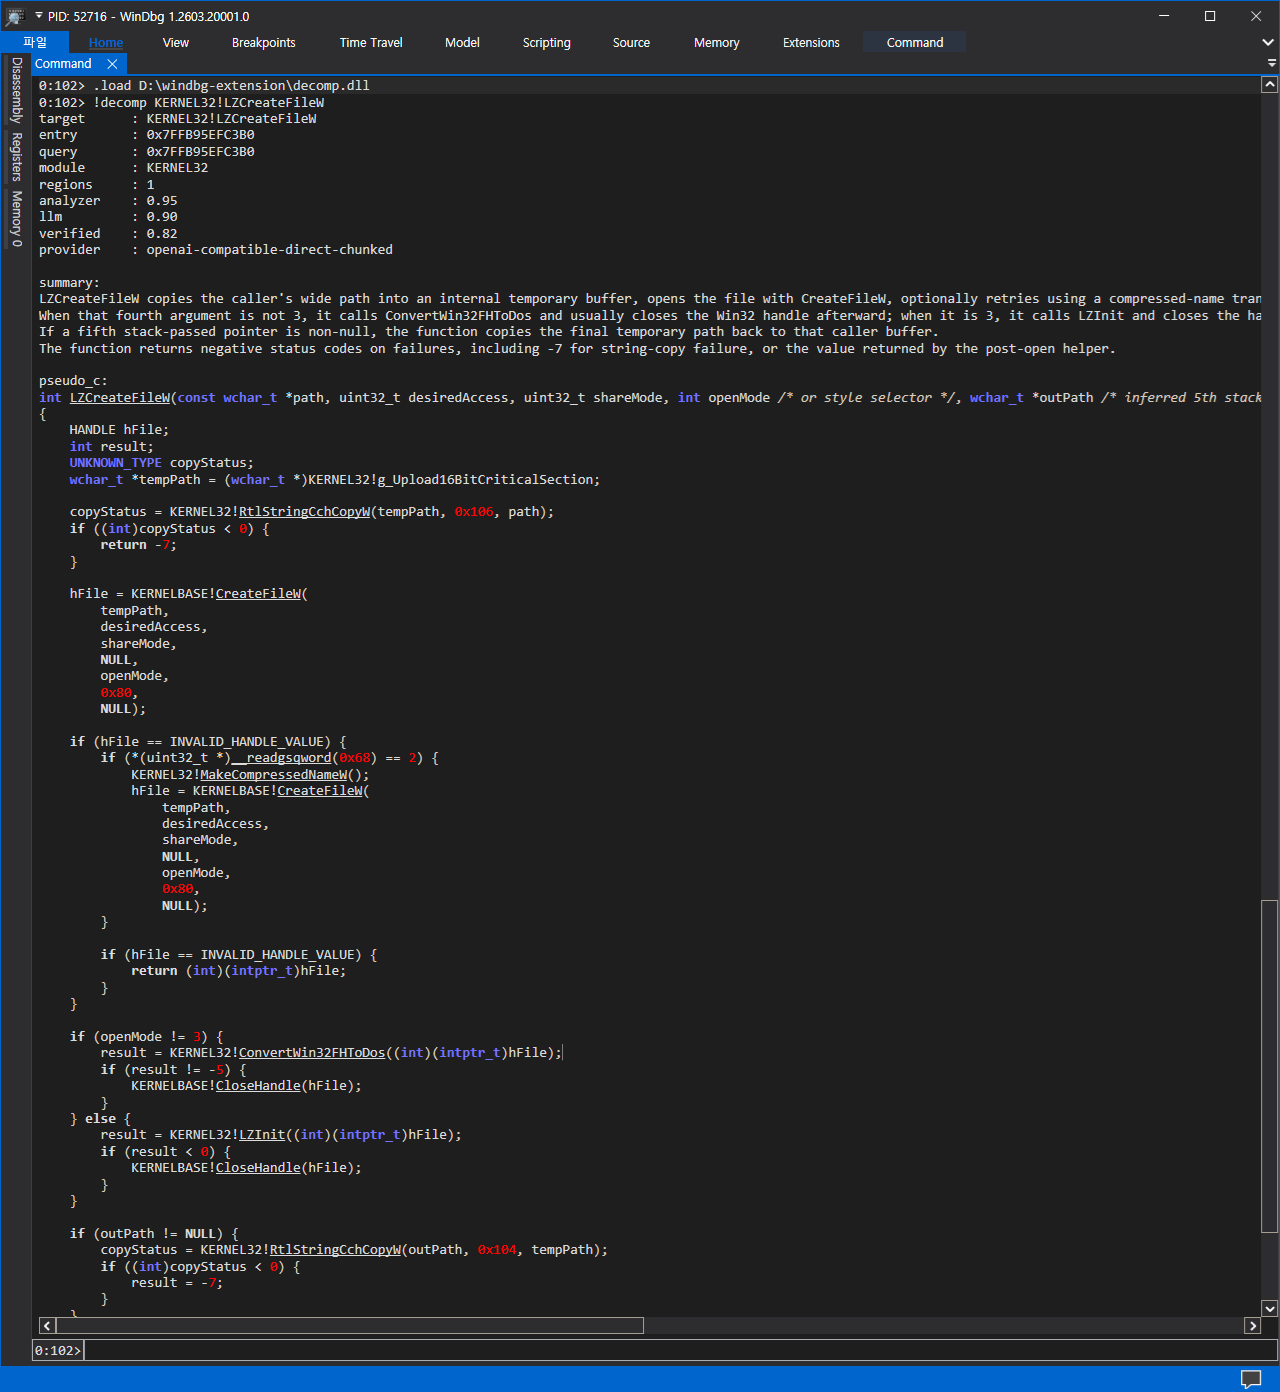
Binary · Tool:
Pseudo C Dump is a Binary Ninja plugin that writes the decompiler's Pseudo C for a binary into a chosen folder, so the output can be opened in an IDE or passed to a later static-analysis tool.
Reviewed AsherDLL/PCDump-bn@67aec1f
Binary · Tool:
Ruri.ShaderDecompiler is a shader decompiler library that turns compiled shader binaries into HLSL and rebuilds links between symbols and bytecode.
Binary · Tool:
libghidra is a typed API for Ghidra program databases, callable from C++, Python, or Rust.
Reviewed 0xeb/libghidra@d4c399b
Binary · Tool:
ghidrasql is a SQL interface for Ghidra program databases.
Reviewed 0xeb/ghidrasql@8c525e3
Binary · Tool:
Pyre runs Ghidra's C++ decompiler in the browser.
Reviewed ant4g0nist/pyre@835d7dd
Binary · Tool:
gapstone is a Go binding for the Capstone disassembly library.
Reviewed bnagy/gapstone@ede92aa
Binary · Tool:
scared is a side-channel analysis framework maintained by eShard.
Reviewed eshard/scared@a1bb2f8
Binary · Tool:
IDAPyHelper is an IDAPython script that lists names available to IDAPython so they can be sorted, searched, and filtered.
Reviewed patois/IDAPyHelper@2a13c48
Binary · Tool:
vscode-decompiler is a Visual Studio Code extension that decompiles binaries through Ghidra or an experimental Windows-only IDA Pro path, plus Java jars and classes, Android APKs, Python .pyc and .pyo files, and Ethereum smart contracts.
Reviewed tintinweb/vscode-decompiler@fb499bd
Binary · Tool:
Capstone.js is a JavaScript and WebAssembly port of the Capstone disassembler, built with Emscripten.
Reviewed AlexAltea/capstone.js@75da2ab
Binary · Tool:
idp_hexagon is an IDA Pro processor module for Qualcomm Hexagon, also called QDSP6.
Reviewed n-o-o-n/idp_hexagon@197cf95
Binary · Tool:
ida-pro-loadmap is an IDA Pro plugin that loads VC, Borland, Dede, GCC, and IDA .map symbol files into an IDA database.
Reviewed mefistotelis/ida-pro-loadmap@8433b8e
Binary · Tool:
Mach-O-Scope 0.2 browses the disassembly of Mach-O bundles such as OS X applications and plugins.
Reviewed smorr/Mach-O-Scope@c29a5db
Binary · Tool:
dayu is a parser and a rudimentary decompiler for the Ark Bytecode .abc files used on OpenHarmony and HarmonyOS.
Reviewed hx1997/dayu@da59296
Binary · Tool:
gdbida pairs an IDA Pro plugin with a GDB Python client so an interactive GDB session can be followed in IDA.
Reviewed Comsecuris/gdbida@c317816
Binary · Tool:
reccmp is a toolchain for decompilation projects that compares a recompilation with the original binary.
Reviewed isledecomp/reccmp@b0bf3d3
Binary · Tool:
decompiler is a Python decompiler with IDA and Capstone backends.
Reviewed EiNSTeiN-/decompiler@f7923b5
Binary · Tool:
unluac-rs is a Rust decompiler for Lua bytecode.
Reviewed x3zvawq/unluac-rs@3186d2e
Binary · Tool:
aevt_decompile annotates a disassembled run-only AppleScript.
Reviewed SentineLabs/aevt_decompile@d48c1ec
Game · Tool:
GBARecomp is a beta static-recompilation framework for the Game Boy Advance.
Reviewed mstan/gbarecomp@351572f
Binary · Tool:
Zomboid Decompiler is a decompiler for Project Zomboid, powered by Vineflower.
Binary · Tool:
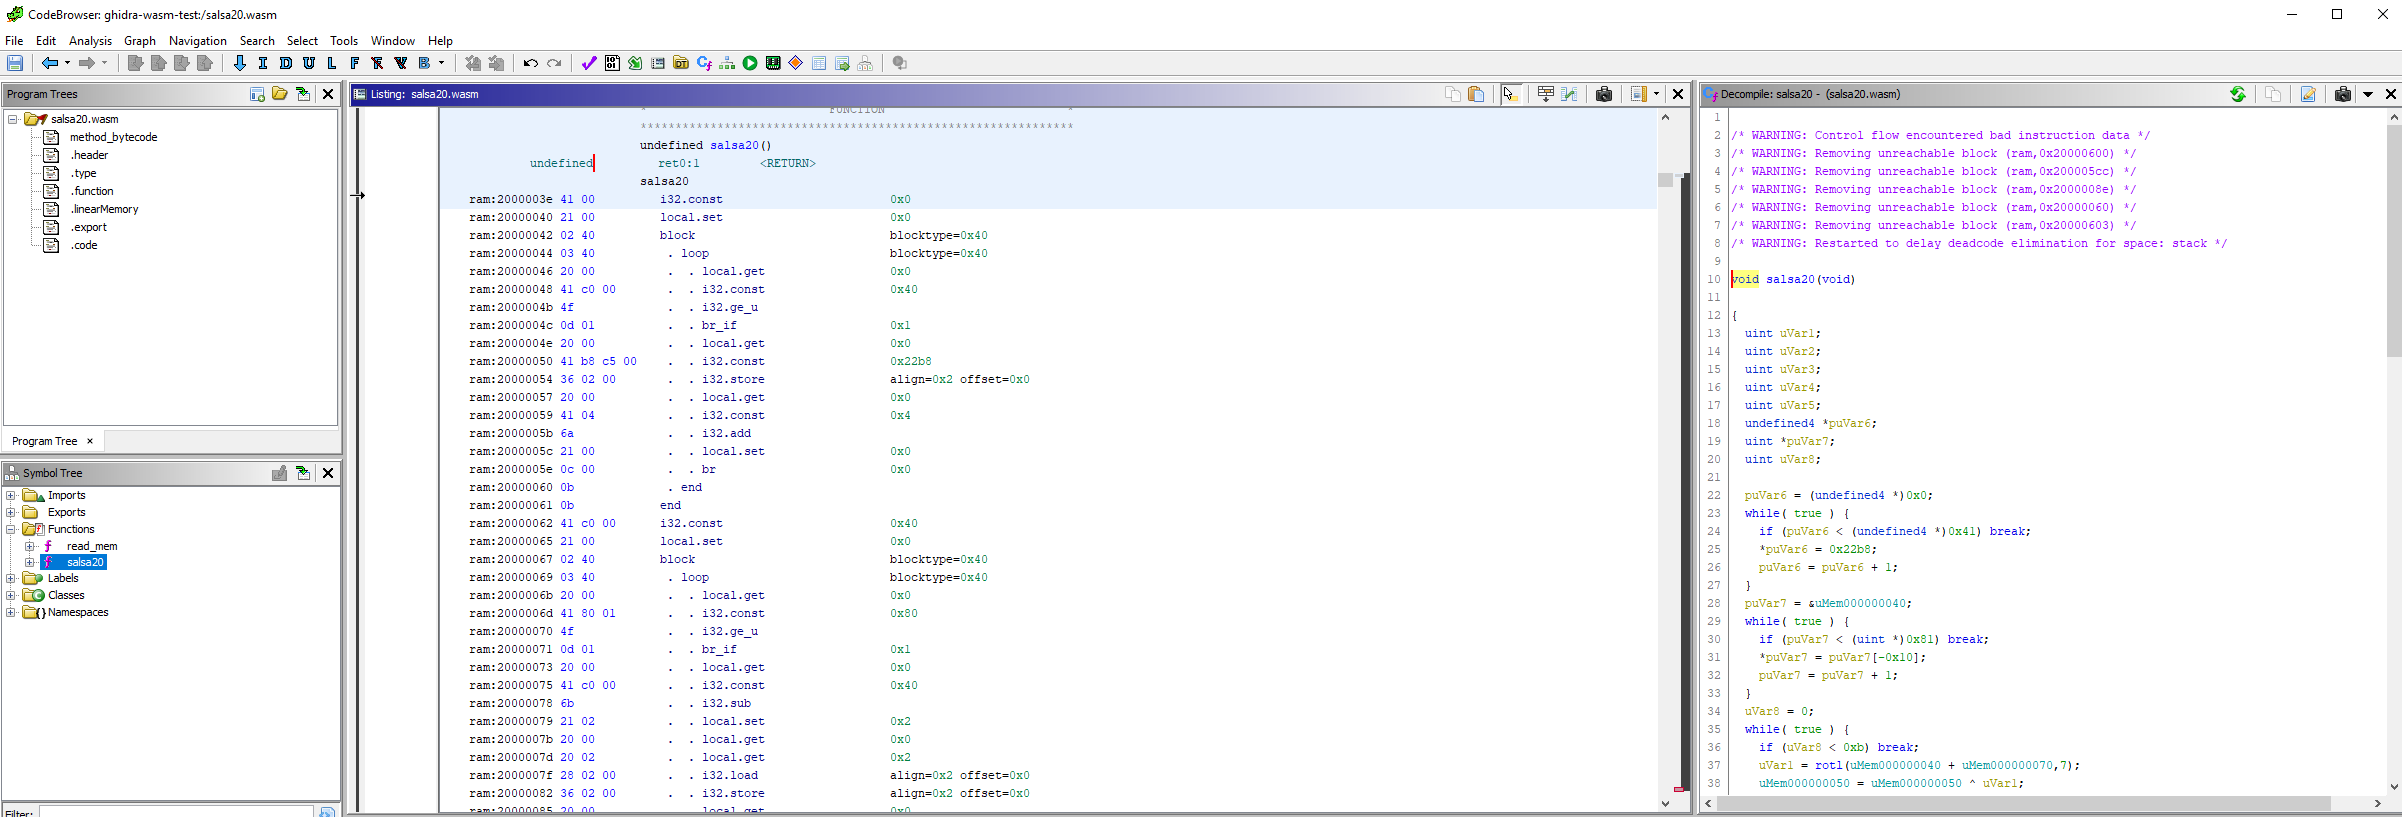
Ghidra Wasm Plugin loads WebAssembly modules into Ghidra for disassembly and decompilation.
Binary · Tool:
dx-shader-decompiler decompiles DirectX 9 pixel and vertex shaders, shader model 3.0.
Game · Tool:
agsutils unpacks, disassembles, modifies, and repacks Adventure Game Studio games.
Reviewed rofl0r/agsutils@48dc22e
Binary · Tool:
ExtractMachO is an IDA plugin that extracts Mach-O binaries found in a disassembly.
Reviewed gdbinit/ExtractMachO@0ee718a
Firmware · Tool:
waterbear is an assembler and disassembler for Dreamcast VMU programs, available as a Rust library and command-line program.
Reviewed wtetzner/waterbear@9d7a253
Binary · Tool:
WPP Remover is an IDA Pro plugin that removes Windows software-trace calls from Hex-Rays pseudocode.
Reviewed L4ys/IDA-WPP-Remover@386fb45
Firmware · Tool:
ds_disassembly_tools is a set of scripts for the initial setup of a Nintendo DS disassembly.
Reviewed pret/ds_disassembly_tools@8cd986c
Game · Tool:
PSRetrox is a C++ application for reverse engineering PlayStation 2 games from extracted ISO files.
Reviewed cualquiercosa327/psretrox@a7bd938
Binary · Tool:
IDR Pascal is a Pascal translation of the Interactive Delphi Reconstructor.
Reviewed tmcdos/IDR@805f601
Binary · Tool:
YaraVM is an IDA Pro loader and processor module for compiled YARA rules.
Reviewed milankovo/YaraVM@3b4e357
Game · Tool:
DecompPipeline turns a game's machine code into C one function at a time and builds that C into a native port.
Reviewed GeneralAtrox/DecompPipeline@7623853
Binary · Tool:
GameMaker 8.1 Decompiler is the 2011 source of a decompiler for GameMaker 8.1 and 8.0 executables.
Reviewed WastedMeerkat/gm81decompiler@80040ac
Binary · Tool:
libdecomp decompiles multi-architecture machine code into source.
Reviewed dmaivel/libdecomp@c711508
Game · Tool:
This toolkit translates a PSP relocatable executable into C, links it with a native runtime, and builds a Windows executable.