Star on GitHubStar2.4k stars

Curated reverse engineering resources

5,191

Filters

Kind
Category
Show all 24

Showing 3,601–3,700 of 5,191

Evidence class
  • C0full software reconstruction
  • C1partial scope or analysis entry
  • C2code & docs, no demo or download
  • C3notes only
  • ?Source unavailable or unreadable at review time
How classes are assigned
  • Native binaries

    502
  • Binary · Tool:

    QuokkaC1

    Quarkslab’s binary exporter, inspired by BinExport, saves a disassembler’s analysis to a protobuf .quokka file so functions, basic blocks, data, cross-references, segments and optionally decompiled code can be used later without the disassembler.
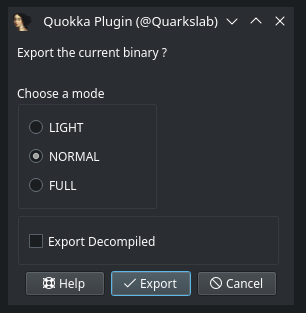
    Demo screenshot from the project's public documentation
    • Binary

    Reviewed quarkslab/quokka@5afe14b
  • Binary · Tool:

    knifeC1

    Static reverse-engineering toolkit in Rust, installed as the knife command, that parses PE, ELF, Mach-O and WebAssembly files without running them.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed bl4ckr0ss3/knife@f260b87

  • Binary · Tool:

    BARFC2

    Python binary analysis framework that loads ELF and PE programs, disassembles 32- and 64-bit x86 and 32-bit ARM code with Capstone and translates it into the REIL intermediate language, so its analyses do not depend on the source architecture.

    • Binary

    Reviewed programa-stic/barf-project@9547ef8

  • Game · Tool:

    rabbitizerC2

    MIPS instruction decoder written in C that never allocates on the heap, with Python, C++ and Rust bindings in the same repository and the stated aim of producing matching assembly.

    • Game
    • Binary

    Reviewed Decompollaborate/rabbitizer@724a49a

  • Binary · Tool:

    ghidrecompC2

    Python command-line decompiler that drives Ghidra through pyghidra to decompile every function of a binary into separate C files, or into one C file and header with Ghidra's C++ exporter, keeping the Ghidra project so later runs can reuse the analysis.

    • Binary

    Reviewed clearbluejar/ghidrecomp@7a82556

  • Binary · Tool:

    VivisectC2

    Pure-Python reverse-engineering framework that combines the vivisect static analyzer, the vtrace debugging library and the vdb debugger.

    • Binary
    • Firmware

    Reviewed vivisect/vivisect@66c93f0

  • Binary · Tool:

    r2pipeC2

    radare2's official scripting interface, with implementations for more than two dozen languages in one repository.

    • Binary

    Reviewed radareorg/radare2-r2pipe@c355810

  • Binary · Tool:

    GREASEC2

    Galois's command-line tool, Ghidra plug-in and Haskell library for checking properties of binaries with under-constrained symbolic execution.

    • Binary

    Reviewed GaloisInc/grease@b94e1e0

  • Binary · Tool:

    PLASMAC2

    Interactive terminal disassembler, formerly named Reverse, for x86 and x86-64 with partial ARM and MIPS/MIPS64 support, reading ELF, PE and raw binaries.

    • Binary

    Reviewed plasma-disassembler/plasma@ec7df9b

  • App · Tool:

    mobdevimC2

    Derek Selander's macOS command-line utility for inspecting and controlling iOS devices connected over USB or Wi-Fi through Apple's private MobileDevice framework.

    • App

    Reviewed DerekSelander/mobdevim@68cddb3

  • Binary · Tool:

    XPEViewerC1

    Qt-based PE file viewer and editor for Windows, Linux and macOS by horsicq, the author of the catalog's Detect It Easy.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed horsicq/XPEViewer@828a0fb

  • App · Tool:

    FermionC1

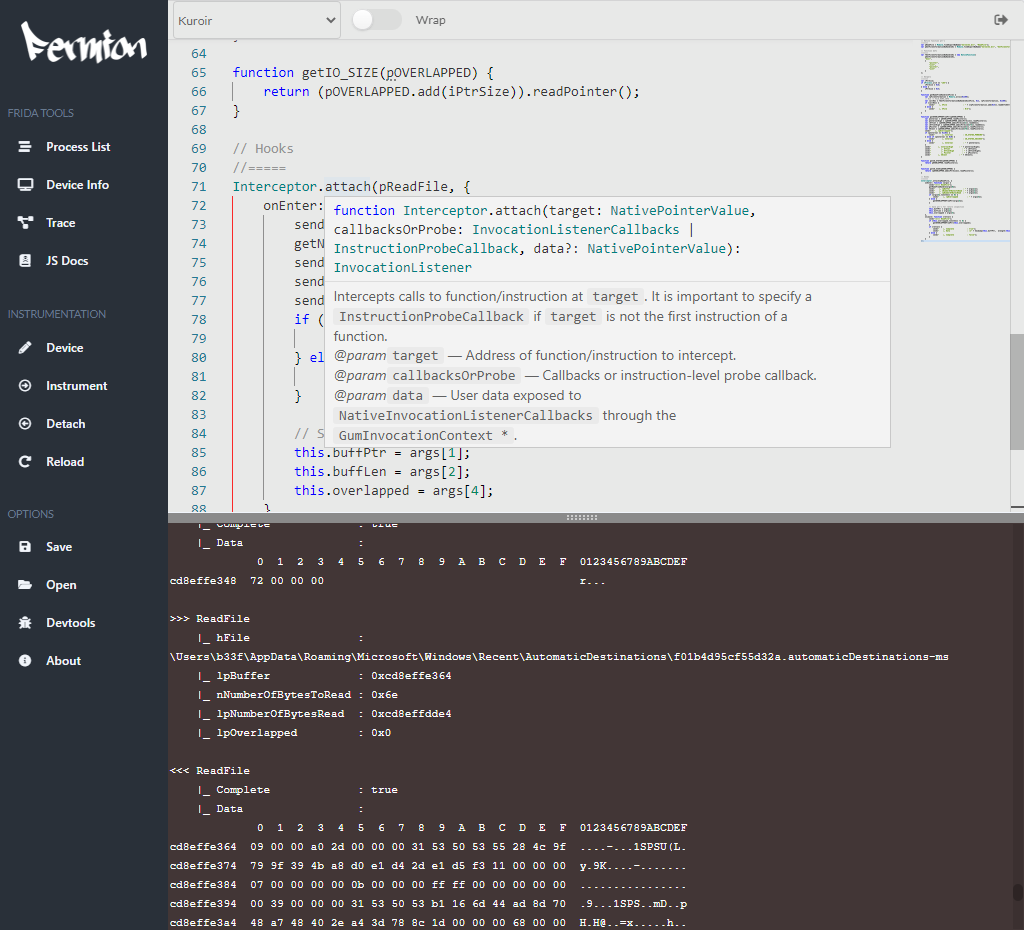
    Ruben Boonen's Electron desktop application that wraps frida-node and the Monaco editor into one window for writing, injecting and refining Frida scripts.

    Demo screenshot from the project's public documentation
    • App
    • Binary

    Reviewed FuzzySecurity/Fermion@79b2643

  • Binary · Tool:

    GhidrathonC1

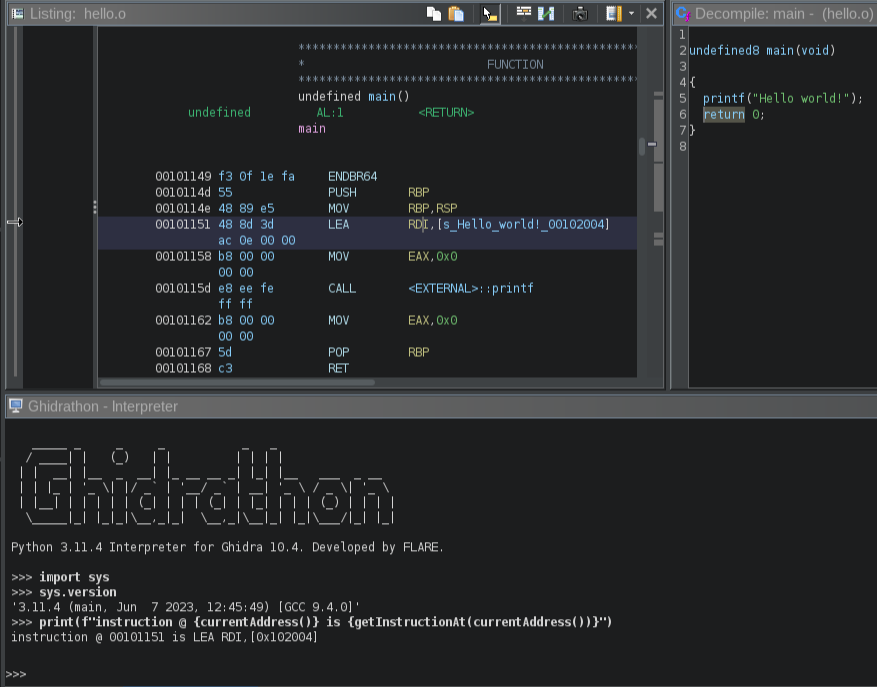
    Mandiant FLARE's Ghidra extension that embeds the user's local CPython 3 interpreter in Ghidra through Jep, as an alternative to Ghidra's Jython-based Python 2.7 scripting.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed mandiant/Ghidrathon@56866ad

  • Binary · Tool:

    diStorm3C2

    Lightweight x86/AMD64 disassembler library in C that the README describes as a decomposer: besides formatted text, distorm_decompose returns a binary structure per instruction with its opcode, operands, prefixes, flow-control class and optionally affected CPU flags.

    • Binary

    Reviewed gdabah/distorm@7a02caa

  • App · Tool:

    ProbeDroidC2

    Dynamic Java-method instrumentation kit for Android 5.0 that lets analysts write their own tracing and profiling tools for apps whose source code they do not have.

    • App

    Reviewed ZSShen/ProbeDroid@a6dc602

  • App · Tool:

    FridumpC2

    Small Python command-line tool that attaches to a running process through Frida and writes its accessible memory ranges to files, run from a Windows, Linux or macOS host against iOS, Android or Windows applications.

    • App
    • Binary

    Reviewed Nightbringer21/fridump@3e64ee0

  • Binary · Tool:

    RedressC2

    Command-line tool, built on the GoRE library, that recovers metadata from stripped binaries produced by the Go compiler.

    • Binary

    Reviewed goretk/redress@fe38d96

  • Firmware · Tool:

    ghidra-nanomipsC2

    Ghidra processor module that adds nanoMIPS disassembly and decompilation through a SLEIGH specification of the little-endian 32-bit nanoMIPS instruction set, including its multithreading instructions.

    • Firmware
    • Binary

    Reviewed nccgroup/ghidra-nanomips@62ebe71

  • Binary · Tool:

    SMDAC2

    Python recursive disassembler library built on Capstone that recovers control-flow graphs from PE, ELF and Mach-O files, .NET assemblies, raw DEX files and memory dumps with a known base address, through x86/x64, AArch64, 32-bit ARM/Thumb, CIL and Dalvik backends.

    • Binary

    Reviewed danielplohmann/smda@04652e6

  • Binary · Tool:

    frida-trace (NowSecure library)C2

    JavaScript library for Frida agents that traces native functions from a declarative description: each function is listed with its return type and input and output arguments, including pointers, UTF-8 and UTF-16 strings and byte arrays whose length is bound to another argument or the return value, with conditions such as reading an output pointer only when the call succeeds.

    • Binary
    • App

    Reviewed nowsecure/frida-trace@9b92c17

  • App · Tool:

    ktoolC1

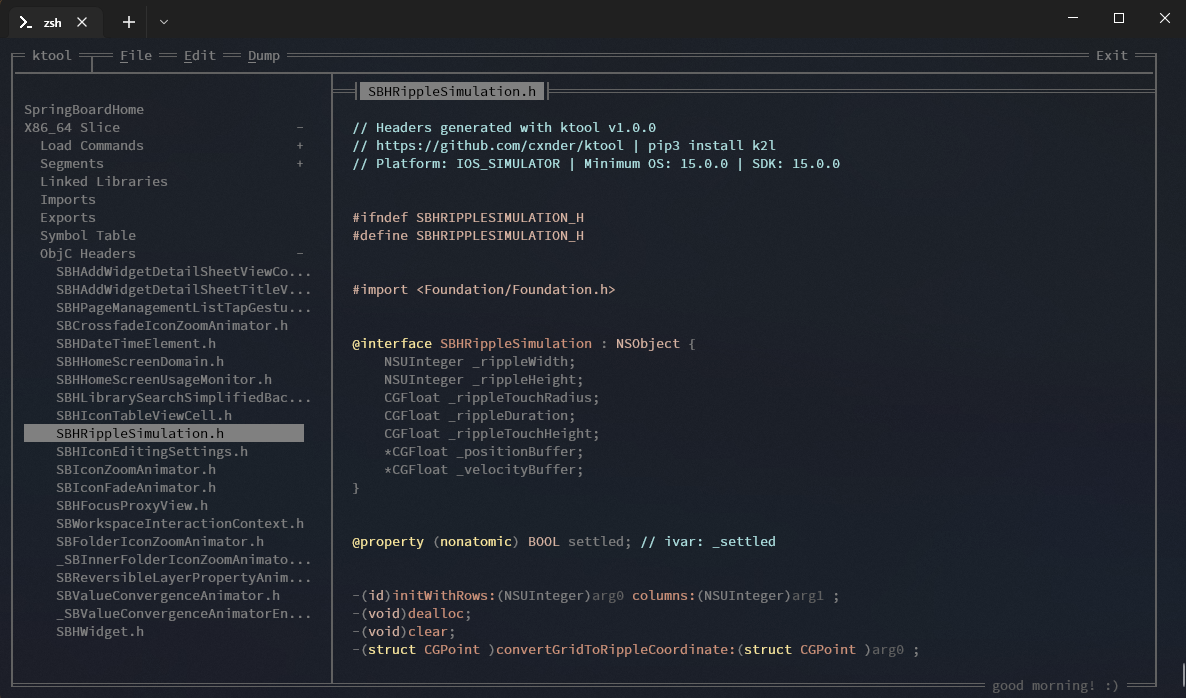
    Pure-Python toolkit for static Mach-O and Objective-C analysis, used as the ktool command line, a terminal browser (ktool open) or a library, with no compiled dependencies.

    Demo screenshot from the project's public documentation
    • App
    • Binary

    Reviewed 0cyn/ktool@faed829

  • App · Tool:

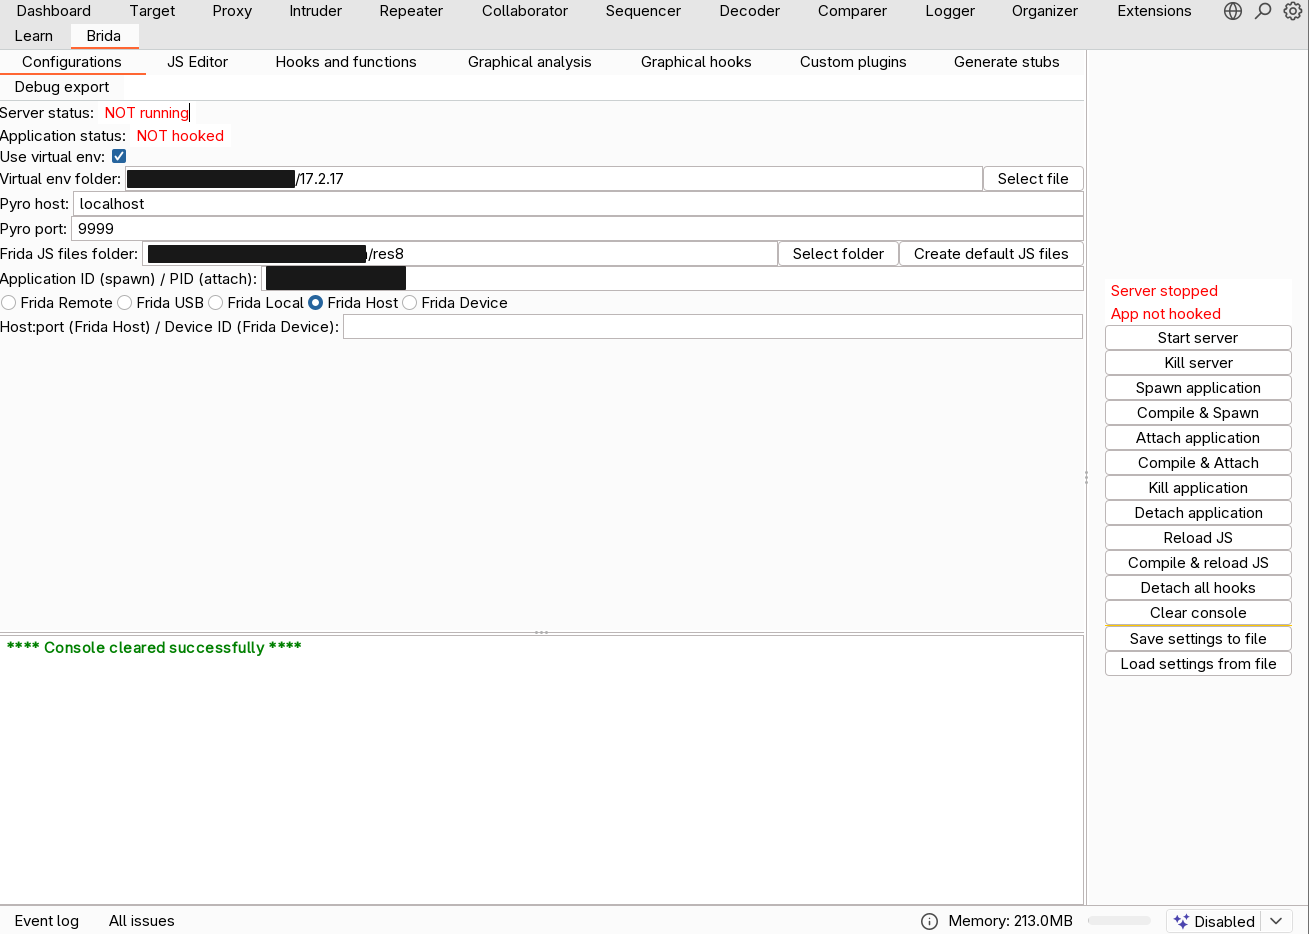
    BridaC1

    Burp Suite extension by Federico Dotta and Piergiovanni Cipolloni that bridges Burp and Frida, so an analyst can run an app's own functions on the HTTP messages it exchanges with its backend instead of reimplementing its encryption, encoding or signing.

    Demo screenshot from the project's public documentation
    • App
    • Protocol

    Reviewed federicodotta/Brida@f335034

  • Binary · Tool:

    Qu1cksc0peC2

    All-in-one malware triage tool that statically analyses Windows PE, Linux ELF (including Go binaries), macOS Mach-O and Android APK, JAR and DEX files as well as Office and PDF documents, scripts, shortcuts, archives, e-mails and PCAPs, reporting imports and API categories, sections, strings and IOCs, packers, embedded executables, Android permission risk, YARA matches and, for Windows and Linux, MITRE ATT&CK mappings.

    • Binary
    • App

    Reviewed CYB3RMX/Qu1cksc0pe@180d44f

  • App · Tool:

    AppMonC1

    Frida-based framework by Nishant Das Patnaik, shown at Black Hat Arsenal 2016, for watching the system API calls that native macOS, iOS and Android apps make.

    Demo screenshot from the project's public documentation
    • App

    Reviewed dpnishant/appmon@f753c4d

  • Binary · Tool:

    YagiC1

    Airbus CERT plugin that embeds Ghidra's native decompiler in IDA Pro and IDA Free: pressing F3 on a function shows Ghidra's C output inside IDA, and edits made there, covering global symbols such as function prototypes and the names and types of stack and register variables, are saved to the IDA database.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed airbus-cert/Yagi@6fc4787

  • Binary · Tool:

    CyberChefC2

    GCHQ's browser-based workbench for decoding, decrypting, decompressing, parsing and carving data by chaining operations into a recipe, with all processing done client-side.

    • Binary
    • Protocol

    Reviewed gchq/CyberChef@d4d96c6

  • Binary · Tool:

    YARAC2

    VirusTotal's pattern-matching tool for identifying and classifying files such as malware samples with rules that combine text, hex and regular-expression strings with a Boolean condition.

    • Binary

    Reviewed VirusTotal/yara@6d47342

  • Game · Tool:

    Cheat EngineC2

    Memory scanner, debugger, disassembler and assembler for inspecting and changing running games and other applications; its README calls it a development environment focused on modding games and applications for personal use.

    • Game
    • Binary

    Reviewed cheat-engine/cheat-engine@ec45d5f

  • Binary · Tool:

    NoribenC2

    Python script that drives Sysinternals Process Monitor to record what a program does while it runs, filters out routine system activity and writes a text report of the processes it created and its file, registry and network activity.

    • Binary

    Reviewed Rurik/Noriben@4c84a98

  • Binary · Tool:

    QEMUC2

    Machine and user-space emulator that runs code built for one CPU architecture on another through its TCG dynamic translator.

    • Binary
    • Firmware

    Reviewed qemu-project/qemu@f71afb4

  • Binary · Tool:

    Hex FiendC1

    Open-source macOS hex editor that inspects and edits binary files of any size without loading them into memory.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed HexFiend/HexFiend@32cb2ef

  • Binary · Tool:

    ScyllaHideC2

    User-mode (ring 3) anti-anti-debug library for 32- and 64-bit Windows programs that hooks system functions so the program being debugged cannot detect the debugger.

    • Binary

    Reviewed x64dbg/ScyllaHide@baa5c8e

  • Binary · Tool:

    YARA-XC2

    VirusTotal's Rust rewrite of YARA for identifying and classifying files with pattern-matching rules.

    • Binary

    Reviewed VirusTotal/yara-x@1bda5fc

  • Binary · Tool:

    ReClass.NETC1

    Memory structure editor for reconstructing the classes and data structures of a running x86 or x64 process, a .NET port of ReClass with many additions.

    Demo available · no screenshot
    • Binary
    • Game

    Reviewed ReClassNET/ReClass.NET@a02fcb9

  • Binary · Tool:

    KeypatchC2

    IDA Pro plugin built on the Keystone assembler engine that patches a binary from typed assembly, fills an address range with instructions or raw bytes and searches the loaded binary for assembly instructions.

    • Binary

    Reviewed keystone-engine/keypatch@e7ecb93

  • Binary · Tool:

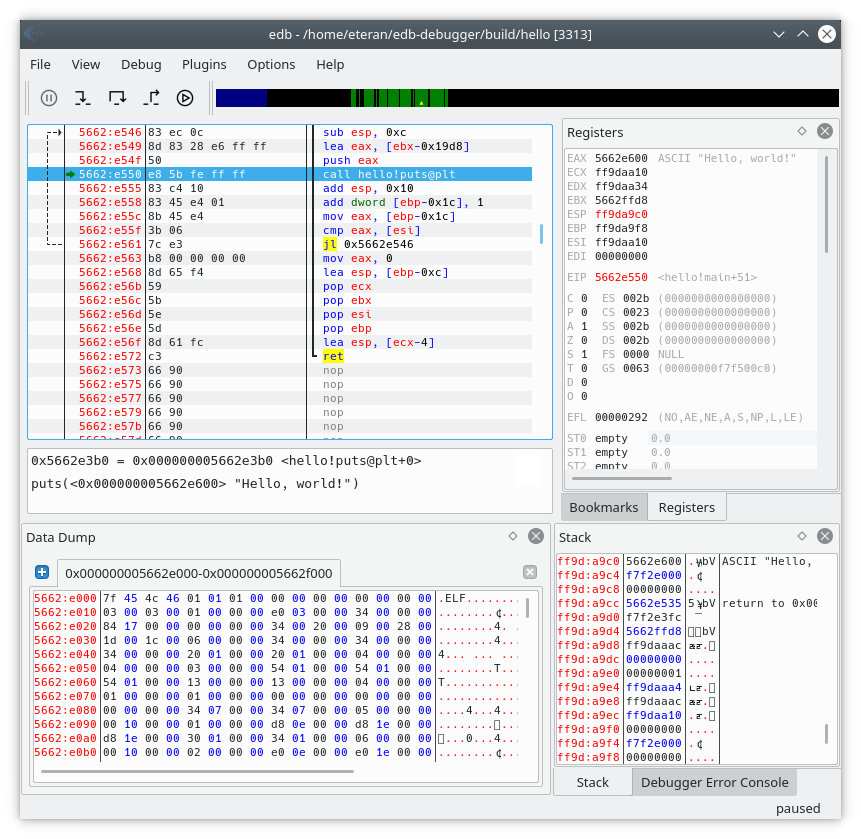
    edb-debuggerC1

    Qt-based graphical debugger for AArch32, x86 and x86-64 programs, inspired by OllyDbg, with Linux as its only officially supported platform.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed eteran/edb-debugger@b8640eb

  • Binary · Tool:

    BinNaviC2

    Google's open-sourced binary analysis IDE for inspecting, navigating, editing and annotating the control-flow graphs and call graphs of disassembled code.

    • Binary

    Reviewed google/binnavi@4cfdd91

  • Binary · Tool:

    flare-emuC2

    Mandiant FLARE Python library that pairs IDA Pro, Rizin or Radare2 with the Unicorn emulator so analysts can script emulation of the binary they are analyzing, for 32- and 64-bit x86, ARM and ARM64.

    • Binary

    Reviewed mandiant/flare-emu@6688c32

  • Binary · Tool:

    IDA ProC2

    Hex-Rays' commercial interactive disassembler, decompiler and debugger, which turns compiled code for more than 70 processor families into annotated, cross-referenced assembly and decompiled pseudocode.

    • Binary
    • App
    • Firmware
    • +1

    Reviewed hex-rays.com/ida-pro

  • Binary · Tool:

    Binary NinjaC3

    Vector 35's commercial interactive disassembler, decompiler and debugger, whose decompiler is built on the BNIL family of intermediate languages and shows either C or BNIL for every officially supported architecture.

    • Binary
    • Firmware

    Reviewed binary.ninja

  • Binary · Tool:

    Hopper DisassemblerC3

    Cryptic Apps' commercial disassembler, decompiler and debugger for macOS and Linux, which reads Mach-O (macOS and iOS), PE and ELF executables built for 32- and 64-bit Intel, ARMv6, ARMv7, ARM64 and PowerPC processors.

    • Binary
    • App

    Reviewed hopperapp.com

  • Binary · Tool:

    010 EditorC3

    SweetScape Software's commercial hex and text editor whose Binary Templates, C/C++-like struct definitions with control flow and functions, parse binary files into hierarchical, editable structures.

    • Binary

    Reviewed sweetscape.com/010editor

  • Binary · Tool:

    pestudioC3

    Winitor's Windows tool for initial malware assessment, which statically inspects Windows executable files and reports key indicators such as hard-coded URLs and IP addresses, flagged imports, resources and overlay data.

    • Binary

    Reviewed winitor.com

  • Binary · Tool:

    OllyDbgC3

    32-bit assembler-level analyzing debugger for Windows that emphasizes binary code analysis for programs without source; its site says development is frozen, and the newest version it lists is 2.01 of 27 September 2013.

    • Binary

    Reviewed ollydbg.de/viewer.htm

  • Binary · Tool:

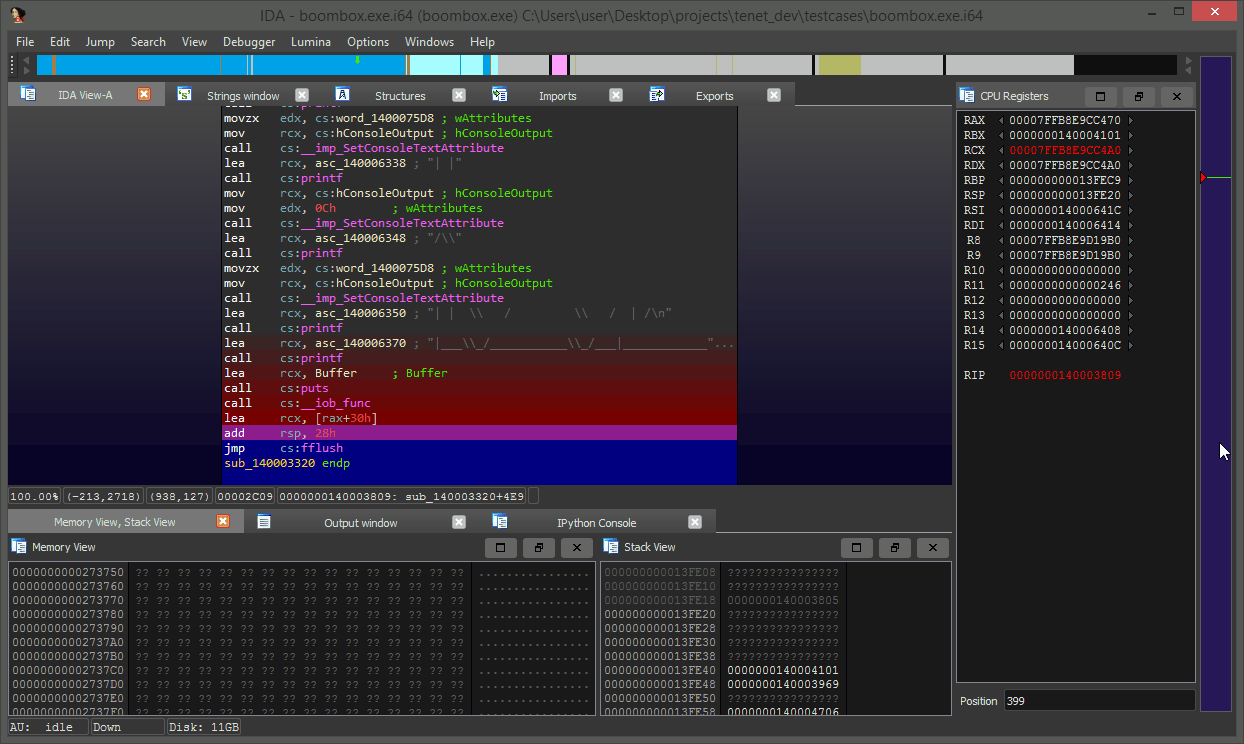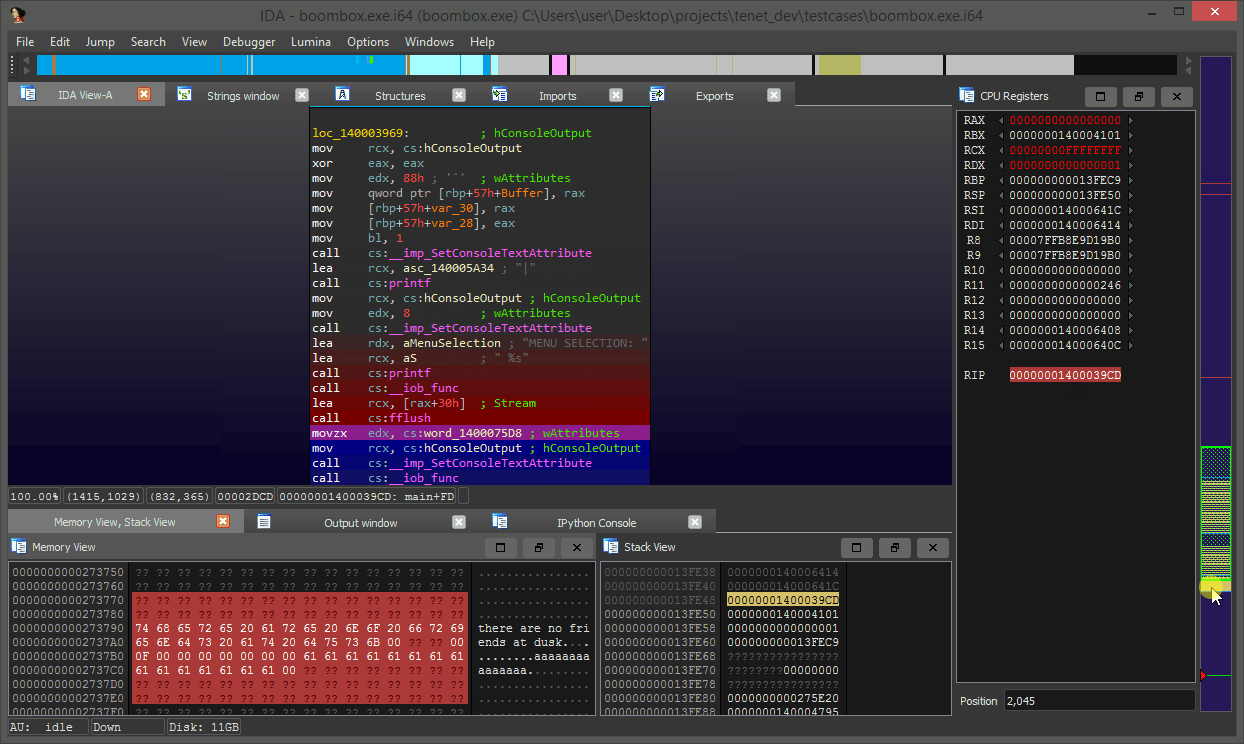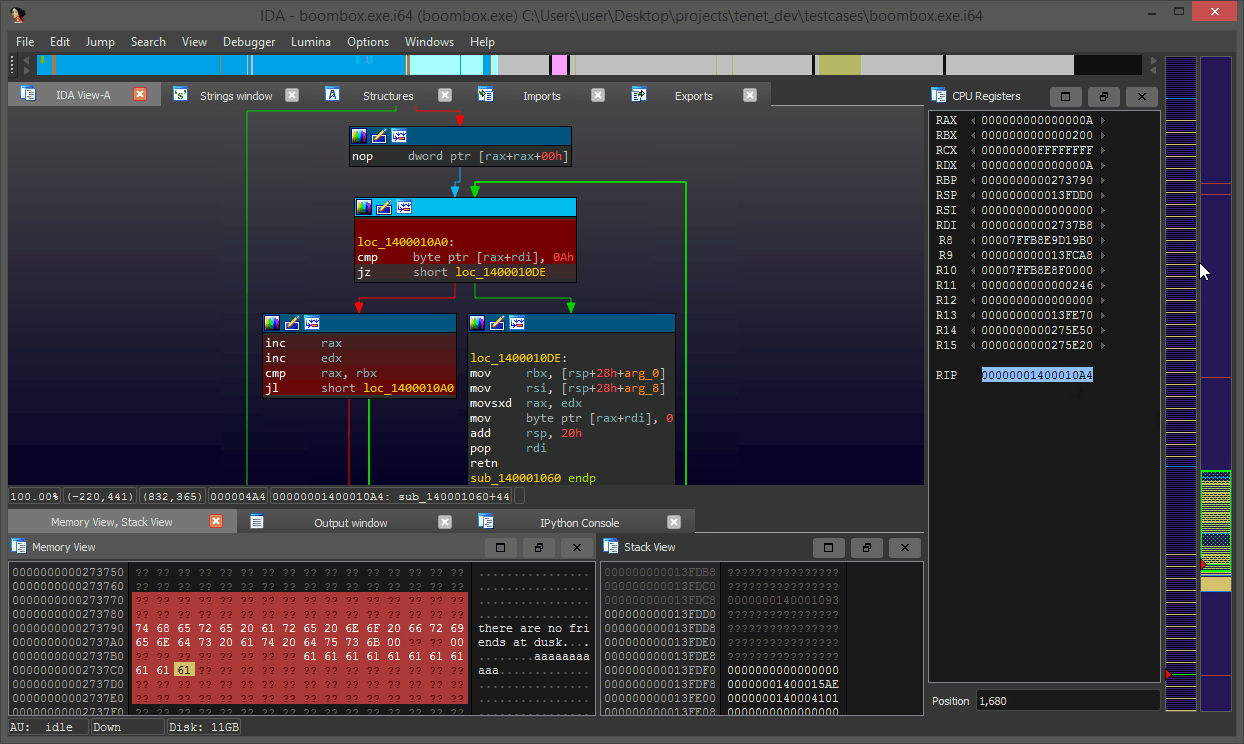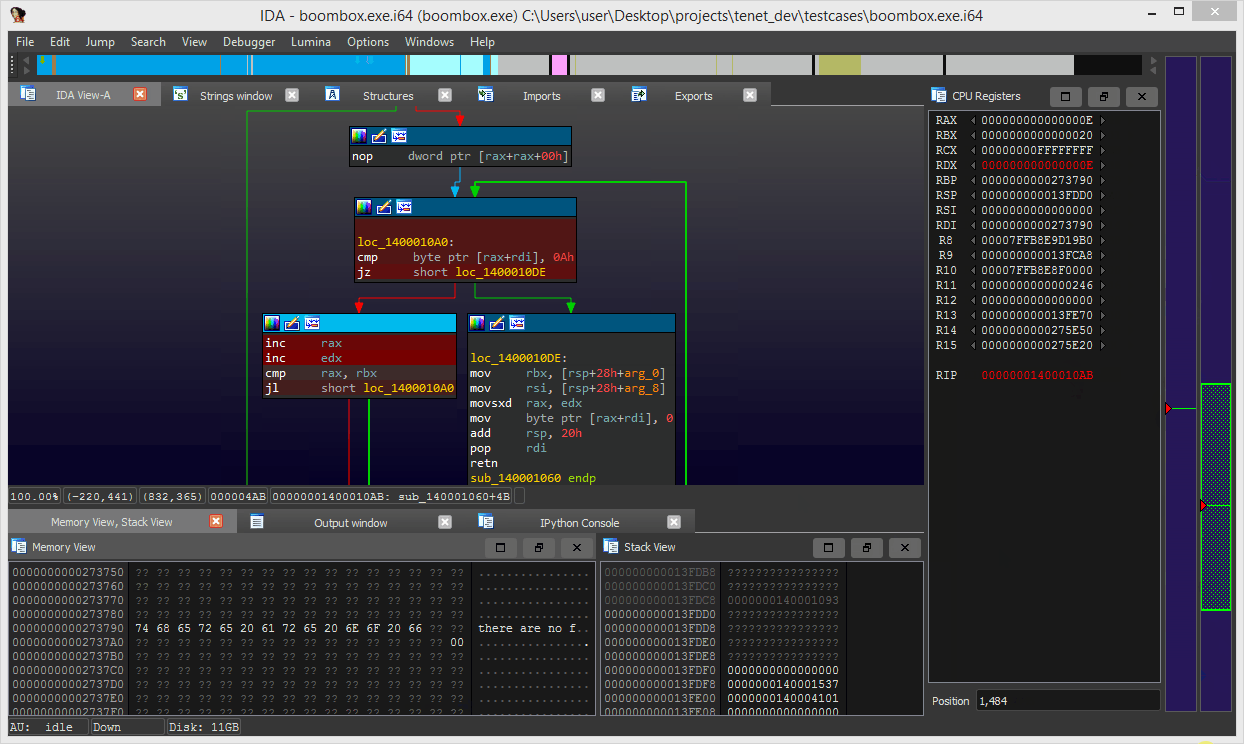
    TenetC1

    IDA Pro plugin for exploring execution traces of a binary: it loads an externally recorded trace and lets the analyst step forwards and backwards through time while the disassembly shows the execution flow in both directions.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed gaasedelen/tenet@62c0bec

  • Binary · Tool:

    findcrypt-yaraC2

    IDA Pro plugin that scans the loaded database with YARA rules for cryptographic constants and similar signatures, lists the matches in a results window and names each matching address after its rule.

    • Binary

    Reviewed polymorf/findcrypt-yara@044644b

  • Binary · Tool:

    deREferencingC2

    IDA Pro plugin that adds register and stack views to the debugger in which pointers are dereferenced and colored, similar to the context displays of GDB plugins such as PEDA, GEF and pwndbg.

    • Binary

    Reviewed danigargu/deREferencing@797a615

  • Binary · Tool:

    HexRays ToolboxC2

    IDAPython scripts that find code patterns in Hex-Rays decompiler output, independent of the binary's processor architecture, by running user-written lambda queries over the decompiled ctree.

    • Binary

    Reviewed patois/HexraysToolbox@d04869a

  • Binary · Tool:

    VirtuailorC2

    IDAPython tool that reconstructs C++ virtual tables in IDA Pro for 32- and 64-bit Intel and AArch64 code by observing indirect calls while the program runs under IDA's debugger.

    • Binary
    • Firmware

    Reviewed 0xgalz/Virtuailor@f5e20a0

  • Binary · Tool:

    xAnalyzerC2

    x64dbg plugin that annotates the static code of the debugged x86 or x64 executable with function-call, argument and loop analysis.

    • Binary

    Reviewed ThunderCls/xAnalyzer@09b7742

  • Binary · Tool:

    VoltronC2

    Extensible Python debugger UI toolkit that attaches utility views to LLDB, GDB, VDB and WinDbg/CDB sessions.

    • Binary

    Reviewed snare/voltron@be9e54b

  • Binary · Tool:

    RemillC2

    Static binary translation library that lifts AArch64, SPARC32, SPARC64, x86 and amd64 machine code, including AVX and AVX512, into LLVM bitcode, with AArch32 support underway.

    • Binary

    Reviewed lifting-bits/remill@56918a8

  • Binary · Tool:

    iaitoC1

    Official Qt-based graphical interface for the radare2 reverse-engineering framework, aiming for parity with radare2's commands, features and keybindings so that existing r2 plugins and scripts keep working.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed radareorg/iaito@a043f93

  • Binary · Tool:

    GDB dashboardC2

    Standalone .gdbinit file written with GDB's Python API that shows a modular status interface each time the debugged program stops, reducing the commands needed to inspect its state.

    • Binary

    Reviewed cyrus-and/gdb-dashboard@7b9b126

  • Binary · Tool:

    REHexC1

    Cross-platform hex editor for reverse engineering that handles files over 1 TB.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed solemnwarning/rehex@1e4fcd4

  • Binary · Tool:

    DobbyC2

    Lightweight, modular hook framework for Windows, macOS, iOS, Android and Linux on x86, x86-64, ARM and ARM64.

    • Binary

    Reviewed jmpews/Dobby@5dfc854

  • Binary · Tool:

    PE TreeC2

    Python module that shows Portable Executable files in a tree view using pefile and PyQt5, as a standalone application and as a plugin for IDA Pro, Ghidra, Volatility, Rekall and minidump.

    • Binary

    Reviewed blackberry/pe_tree@2be607f

  • Binary · Tool:

    RpcViewC2

    Open-source Windows tool that explores and decompiles the RPC functionality present on a Microsoft system.

    • Binary

    Reviewed silverf0x/RpcView@14d5e1a

  • Binary · Tool:

    amocoC2

    Python package for symbolic analysis of binaries.

    • Binary

    Reviewed bdcht/amoco@3e36c52

  • Binary · Tool:

    gdbguiC2

    Browser-based frontend to the GNU debugger, gdb.

    • Binary

    Reviewed cs01/gdbgui@773b916

  • Binary · Tool:

    PorosityC2

    Decompiler that turns Ethereum Virtual Machine bytecode into readable Solidity-syntax contracts, supported on Linux and macOS.

    • Binary

    Reviewed msuiche/porosity@b407155

  • Binary · Tool:

    XoriC2

    Automation-ready disassembly and static analysis library for shellcode and PE binaries that outputs disassembly, functions and imports as JSON.

    • Binary

    Reviewed endgameinc/xori@d58a742

  • Binary · Tool:

    binglideC2

    Visual reverse-engineering tool that gives a quick overview of the data types present in a file.

    • Binary

    Reviewed wapiflapi/binglide@60168d8

  • Binary · Tool:

    ERESIC2

    Reverse Engineering Software Interface built around ELFsh, an interactive and scriptable shell for reading and modifying ELF objects, and e2dbg, an embedded ELF debugger.

    • Binary

    Reviewed thorkill/eresi@4769c17

  • Binary · Tool:

    pixdC2

    Terminal tool that visualises binary data like a hexdump, but draws each octet as a coloured square from a palette.

    • Binary

    Reviewed FireyFly/pixd@f49add4

  • Binary · Tool:

    Universal Extractor 2C2

    Unofficial, extended continuation of Universal Extractor that unpacks files from standard archives, application installers, disk images and game archives.

    • Binary
    • Game

    Reviewed Bioruebe/UniExtract2@9719ac9

  • Binary · Tool:

    ElleKitC2

    Function hooking toolkit for arm64 XNU devices: a C function hooker that patches memory pages directly, an Objective-C function hooker, an arm64 assembler, JIT inline assembly for Swift and a reimplementation of the Substrate and libhooker APIs.

    • Binary

    Reviewed tealbathingsuit/ellekit@1017a0d

  • Binary · Tool:

    ProcDump for Linux and macOSC1

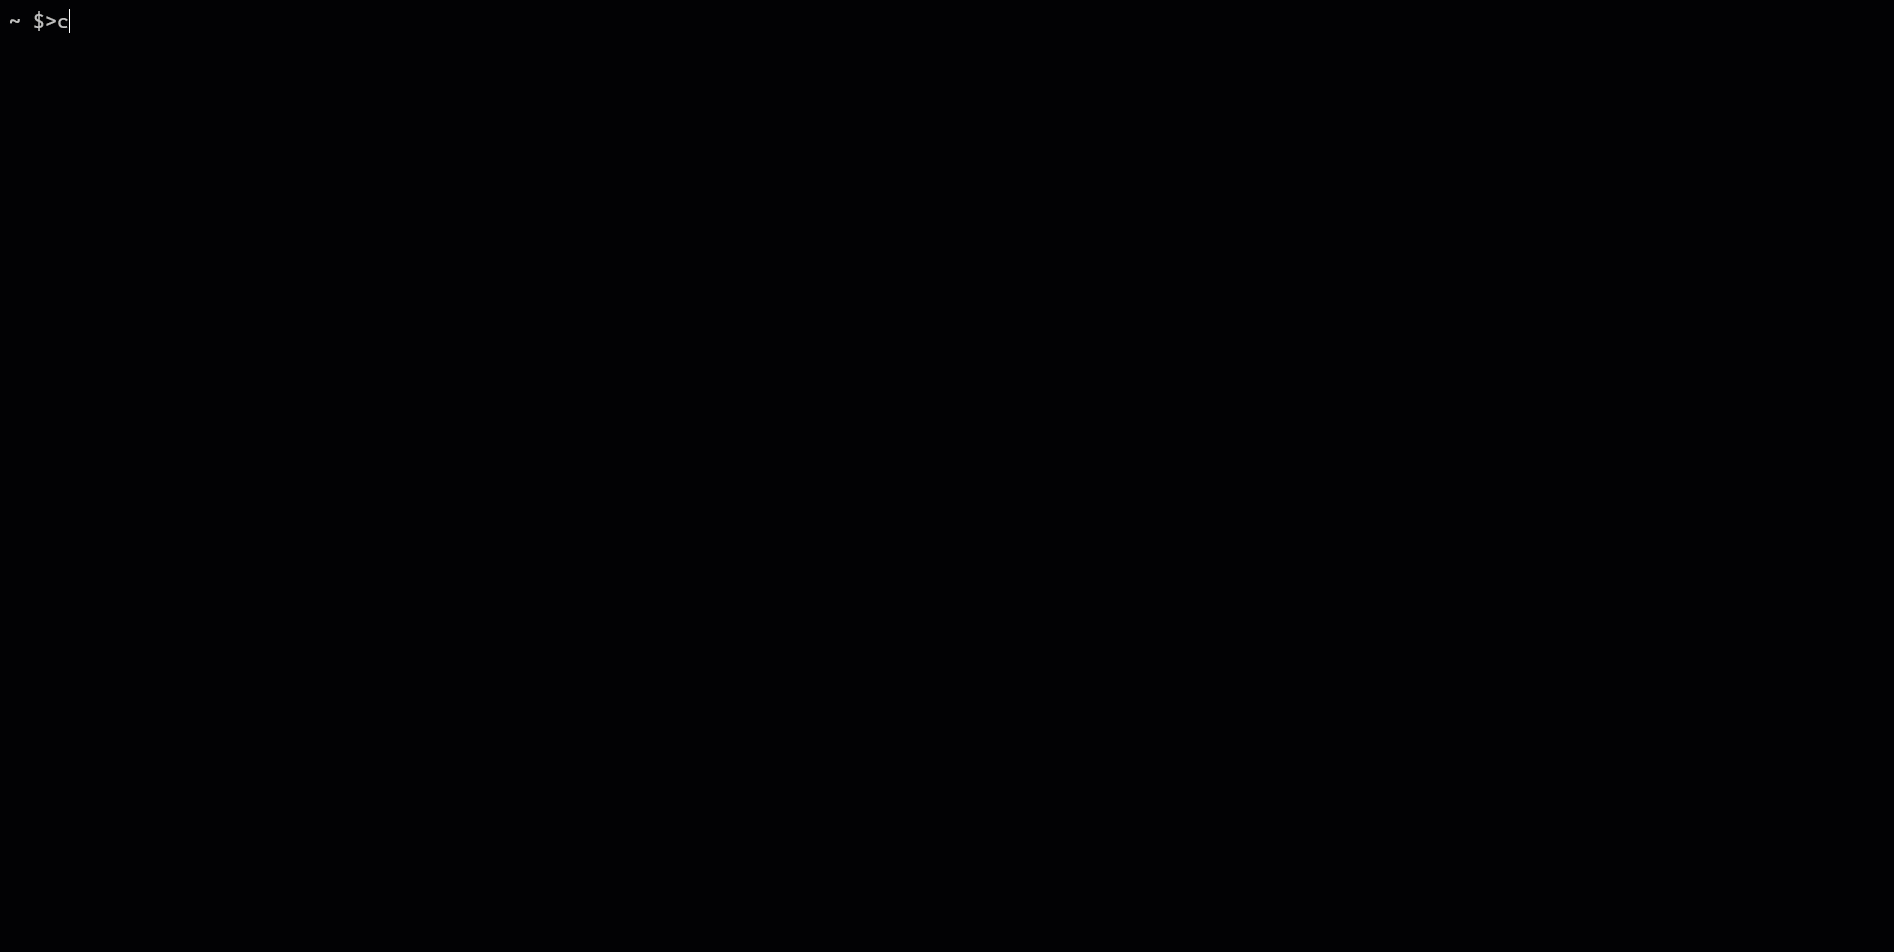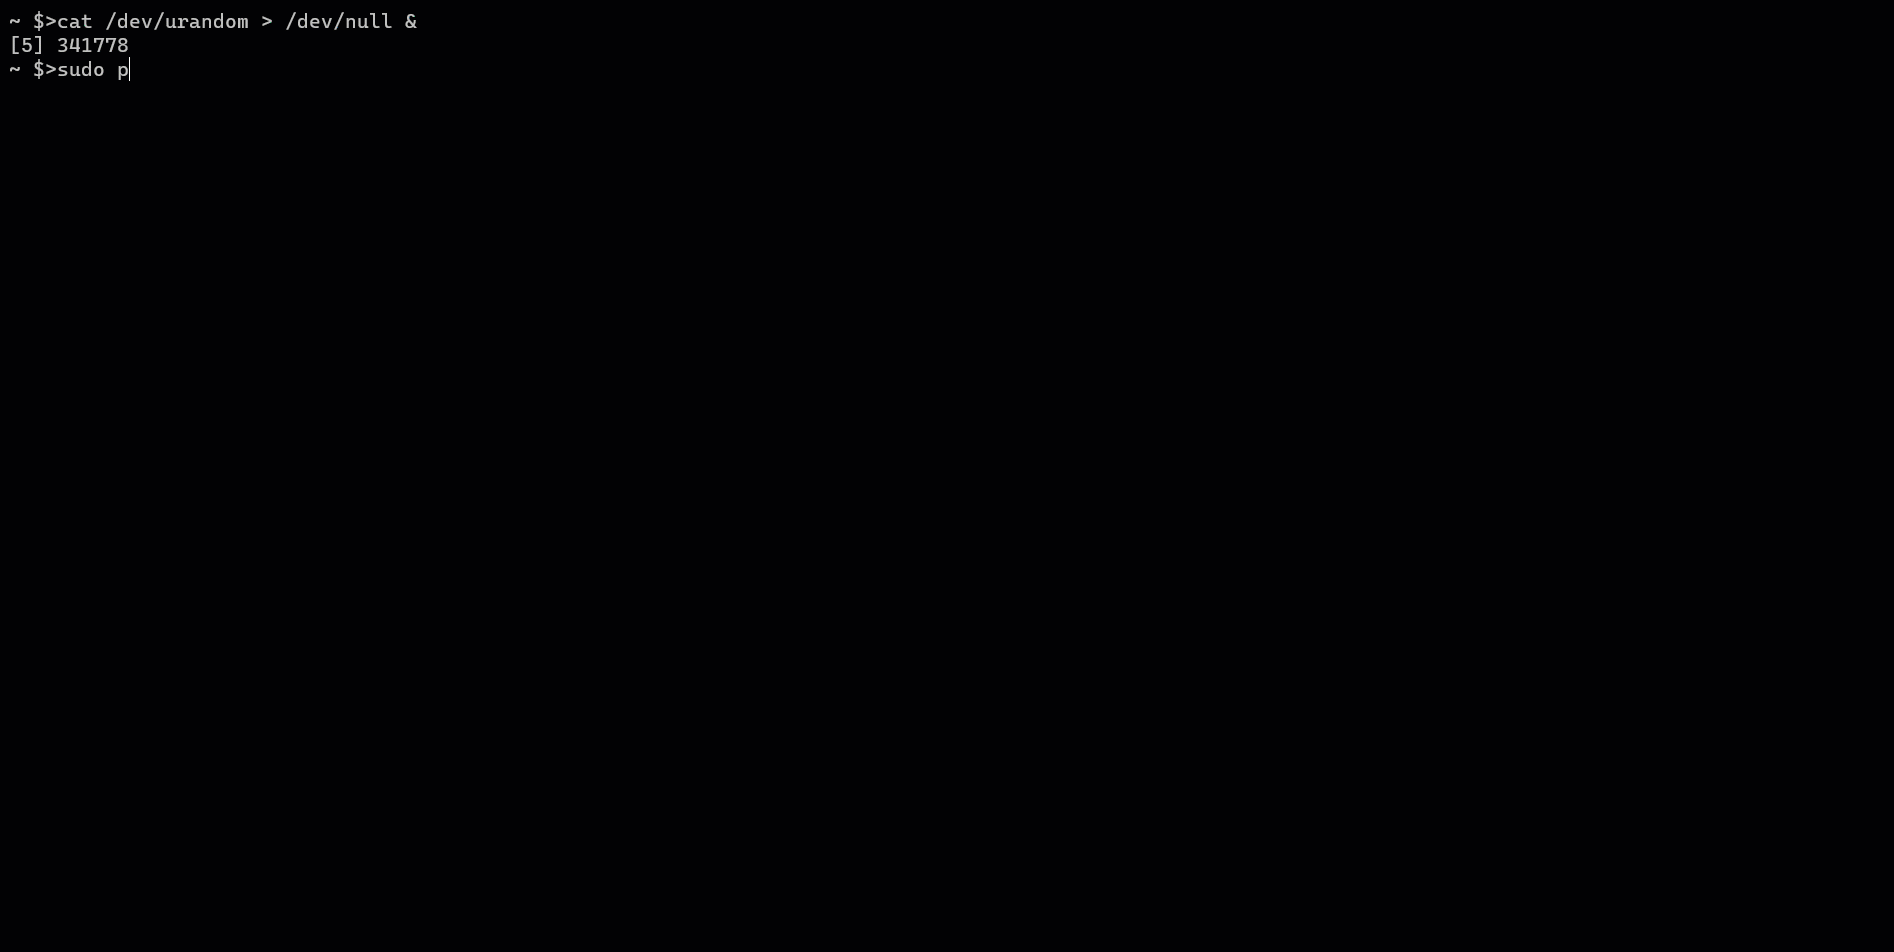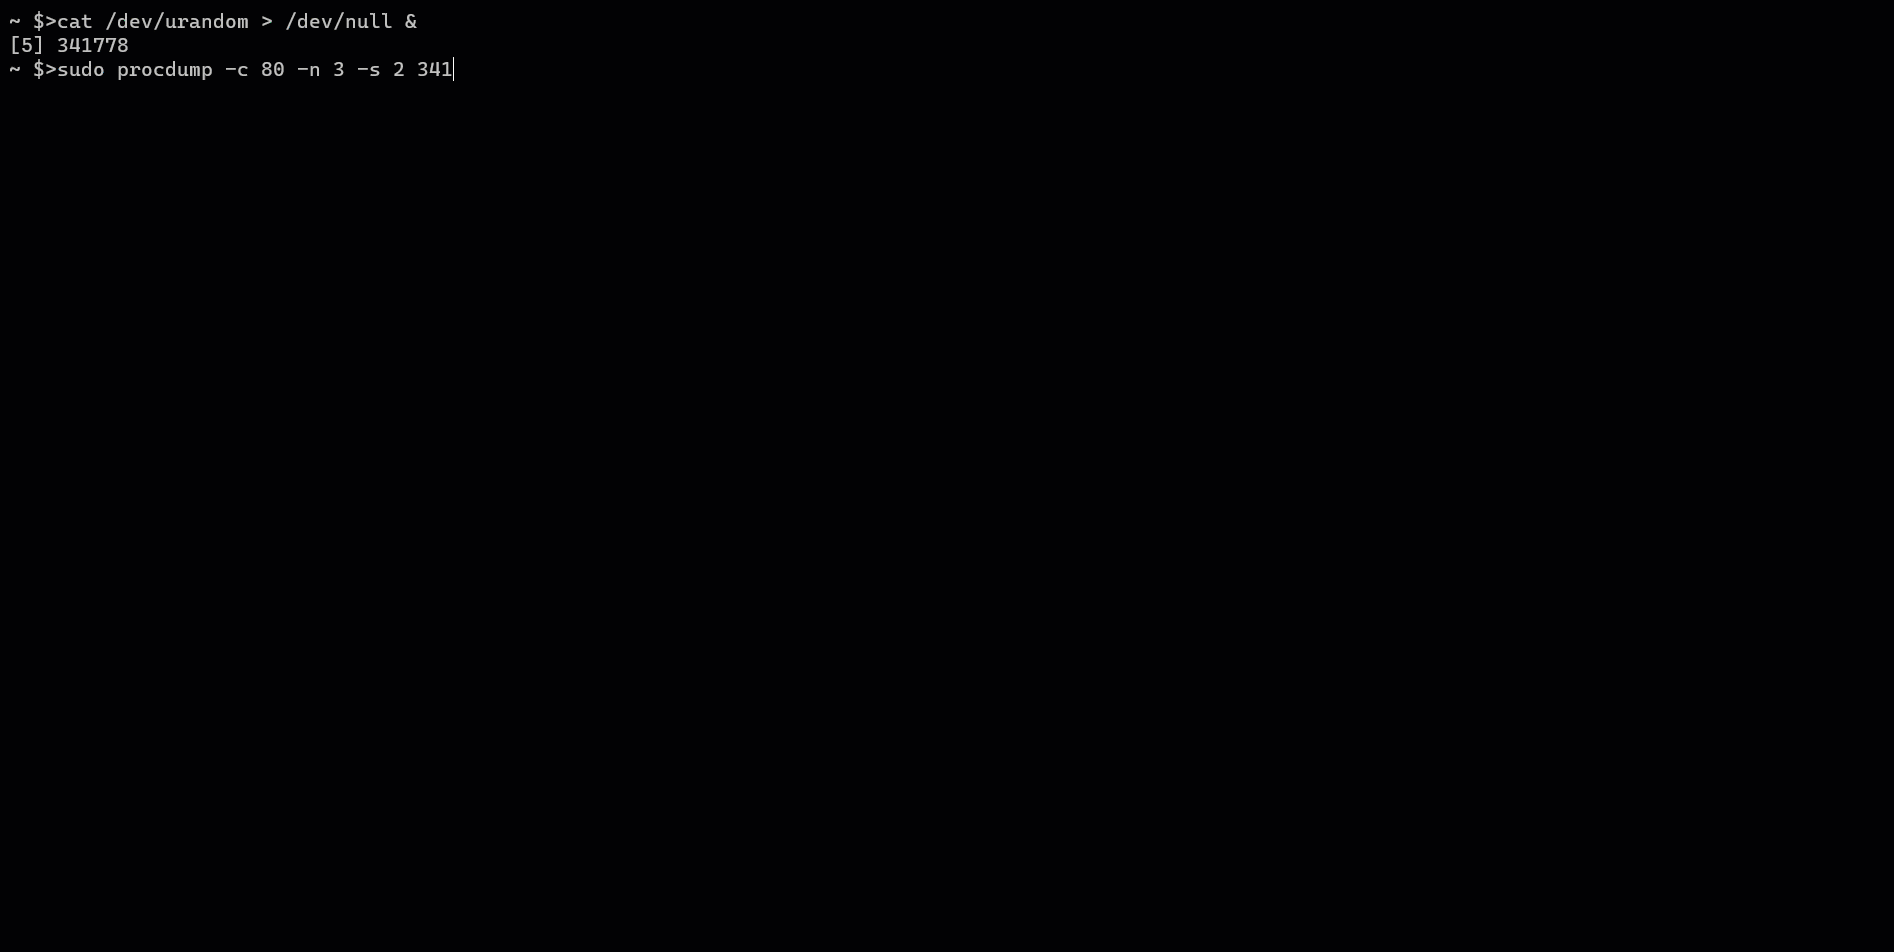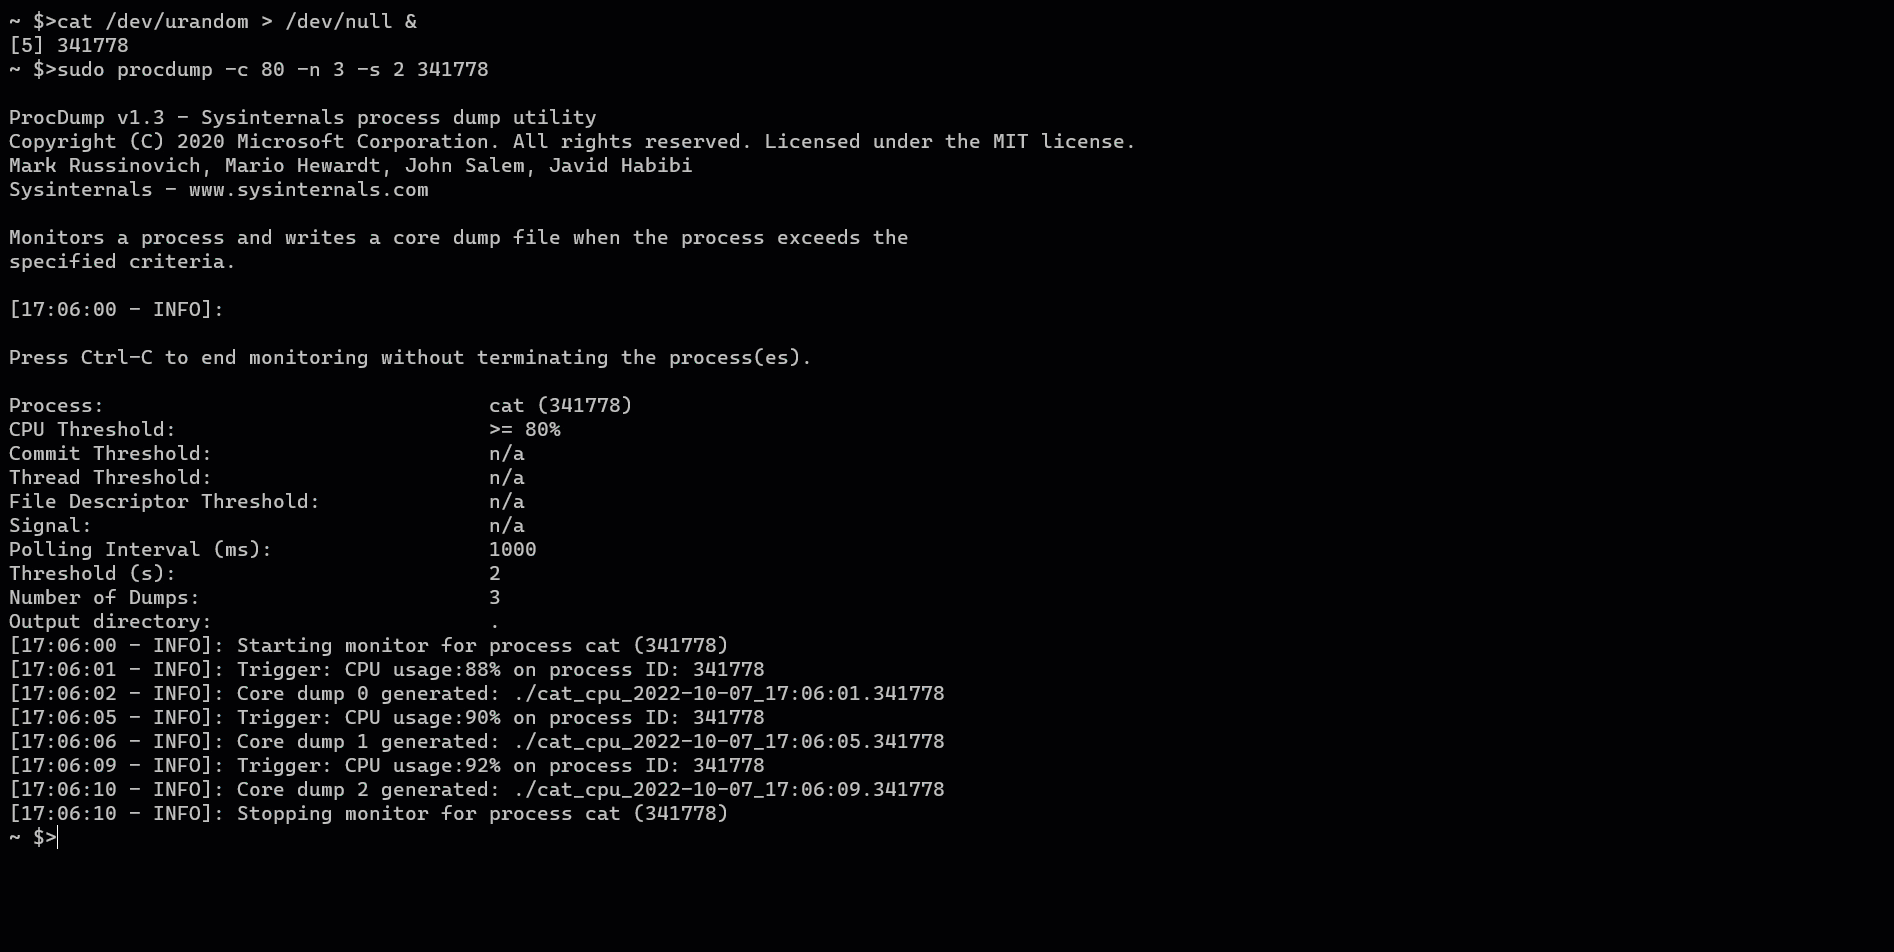
    Linux and macOS reimagining of the Sysinternals ProcDump tool that writes process dumps in response to performance, runtime, signal and resource-tracking triggers, including native dumps through a Rust ELF writer and managed dumps through .NET diagnostics IPC.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed microsoft/ProcDump-Linux@2f83148

  • App · Tool:

    fishhookC2

    Small library that dynamically rebinds symbols in Mach-O binaries running on iOS, on device and in the simulator, by updating the lazy and non-lazy symbol pointers that dyld uses.

    • App

    Reviewed meta/fishhook@aadc161

  • Binary · Tool:

    pcode2codeC2

    VBA p-code decompiler based on pcodedmp, written for Office documents whose macro source has been stomped to leave only bytecode.

    • Binary

    Reviewed Big5-sec/pcode2code@65ae983

  • Binary · Tool:

    rust-deobfC1

    rust-deobf analyzes compiled, mainly Rust, ELF, PE and Mach-O binaries to recover hidden strings and related artifacts.

    Demo screenshot from the project's public documentation
    • Binary

    Reviewed VAHPEM/rust-deobf@04a9c4a

  • Binary · Tool:

    CFG VisualizerC2

    CFG Visualizer extracts function control-flow graphs from ELF, PE and Mach-O binaries with radare2 and presents them in an interactive 3D browser view.

    • Binary

    Reviewed zhameersheraz/cfg-visualizer@76a84f0

  • Binary · Tool:

    Cpp2CSC2

    Cpp2CS recovers managed methods from Android ARM64 Unity IL2CPP ELF binaries and matching metadata, emitting CIL assemblies, C# source and per-method diagnostics.

    • Binary

    Reviewed MetaMikuAI/Cpp2CS@c1acd6b

  • Binary · Tool:

    cocos2d-dumperC2

    cocos2d-dumper extracts defined function symbols from ELF shared libraries and demangles C++ names with GNU binutils.

    • Binary

    Reviewed d1xus/cocos2d-dumper@c53f57c

  • Binary · Tool:

    BinScanC2

    BinScan scans files in bulk and emits per-file JSON containing format identification, structural metadata, hashes and entropy.

    • Binary

    Reviewed Mraxzist/BinScan@7bd7e78

  • Binary · Tool:

    m68kdasmC2

    m68kdasm disassembles Motorola 68000-family machine code in Go and returns assembly with structured instruction metadata.

    • Binary

    Reviewed jenska/m68kdasm@a4de220

  • Binary · Tool:

    rust-sig-genC2

    rust-sig-gen generates IDA FLAIR library signatures from compiled Rust crates for executable analysis.

    • Binary

    Reviewed st0de/rust-sig-gen@8890d96

  • Binary · Tool:

    pdbinspectorC1

    pdbinspector analyzes Microsoft PDB files to list structures, classes, enums, functions, public symbols and exports.

    Demo available · no screenshot
    • Binary

    Reviewed nikaiw/pdbinspector@c02a188

↑↓ move↵ open⌘↵ new tab