Binary · Tool:
B2R2C2
Binary analysis framework written in F# for .NET by KAIST's SoftSec Lab.
- Binary
Reviewed B2R2-org/B2R2@37de7a7
Binary · Tool:
Binary analysis framework written in F# for .NET by KAIST's SoftSec Lab.
Reviewed B2R2-org/B2R2@37de7a7
Binary · Tool:
Rizin plugin that embeds Ghidra's C++ decompiler and Sleigh disassembler, so no Java Ghidra installation is needed.
Reviewed rizinorg/rz-ghidra@0f4e062
Binary · Tool:
Research decompiler from Fraunhofer FKIE, developed with Singapore's DSO National Laboratories between 2019 and 2021, that runs as a Binary Ninja plugin and starts from Binary Ninja's Medium Level IL.
Reviewed fkie-cad/dewolf@3c389e1
Binary · Tool:
Decompiler-to-debugger bridge that serves function names, global variables, stack and register variable names and decompiled code from IDA Pro, Binary Ninja, Ghidra or angr-management to GDB over an XML-RPC connection.
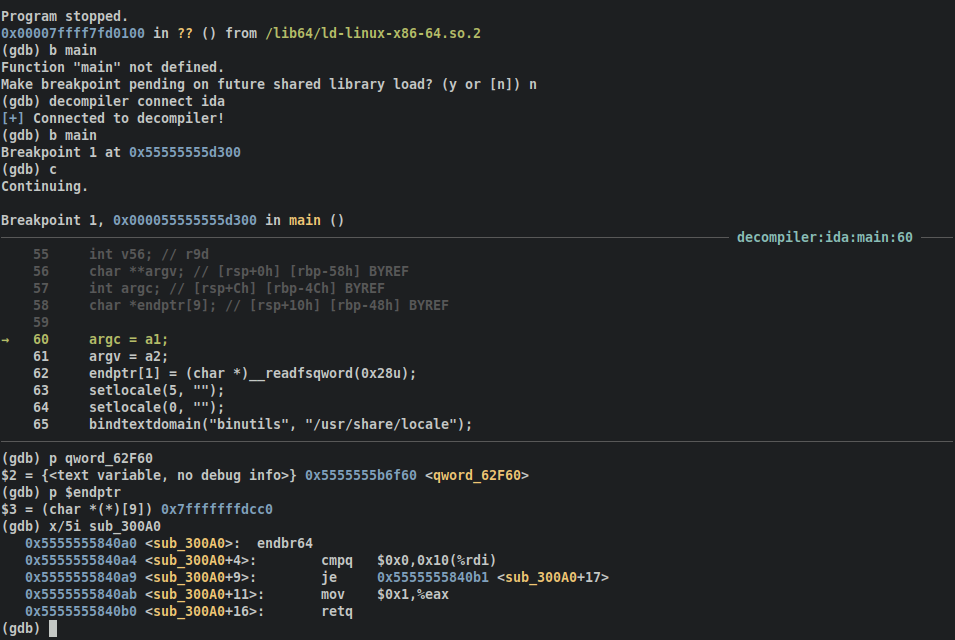
Reviewed mahaloz/decomp2dbg@416dce4
Binary · Tool:
Static binary rewriter for x86-64 Linux ELF executables and shared objects that inserts instrumentation without control-flow recovery and writes a drop-in replacement binary, following the PLDI 2020 paper Binary Rewriting without Control Flow Recovery.
Reviewed GJDuck/e9patch@682ab1f
Binary · Tool:
Trail of Bits implementation of the pattern-independent structuring algorithm from the No More Gotos paper, turning LLVM bitcode into goto-free C as a small, hackable decompiler back end that interoperates with LLVM and Remill.
Reviewed lifting-bits/rellic@370abaa
Binary · Tool:
Ghidra extension that delinks a selected part of a program back into a relocatable object file.
Binary · Tool:
The exporter component of BinDiff: plugins for IDA Pro and Binary Ninja and an extension for Ghidra that write an analyzed disassembly to the Protocol Buffer format BinDiff requires.
Reviewed google/binexport@1fc1d73
Binary · Tool:
Source-code-assisted IDA Python plugin from Check Point Research that finds and matches open-source libraries compiled into large binaries and firmware.
Reviewed CheckPointSW/Karta@7a3d0d3
Binary · Tool:
C++20 core of the VTIL (Virtual-machine Translation Intermediate Language) project, an intermediate language and optimizing compiler that the README describes as built for binary de-obfuscation and de-virtualization.
Reviewed vtil-project/VTIL-Core@9ebee8e
App · Tool:
Unofficial Visual Studio Code extension for Frida work.
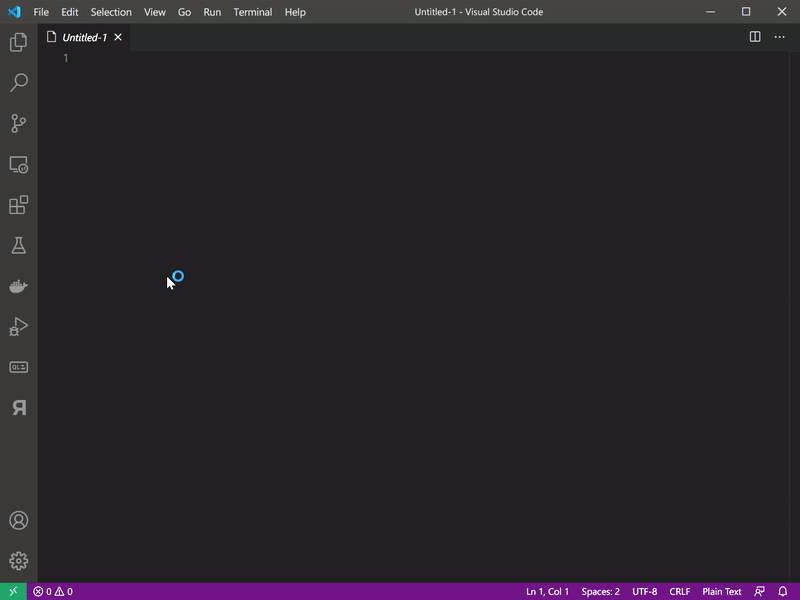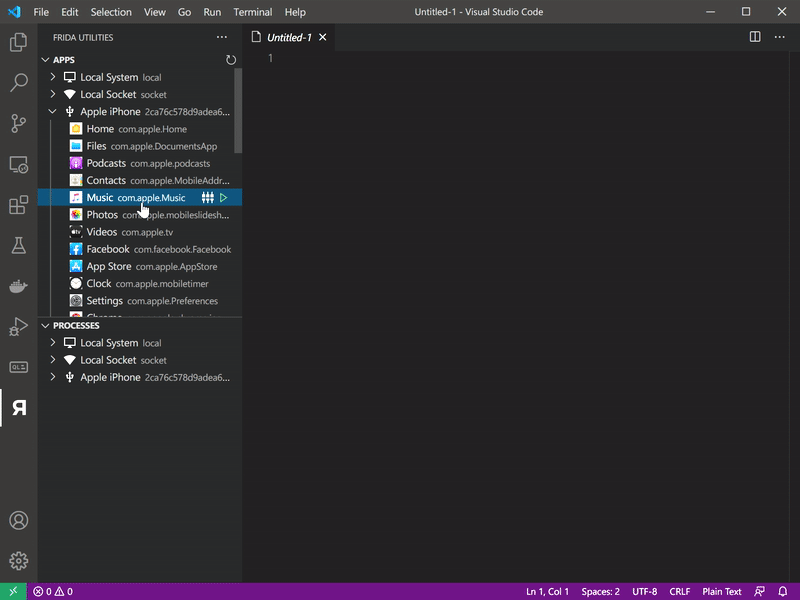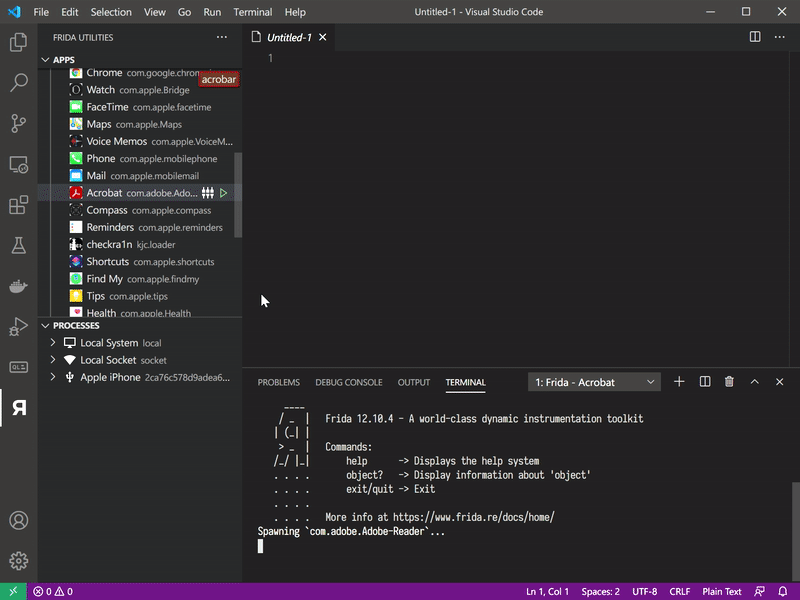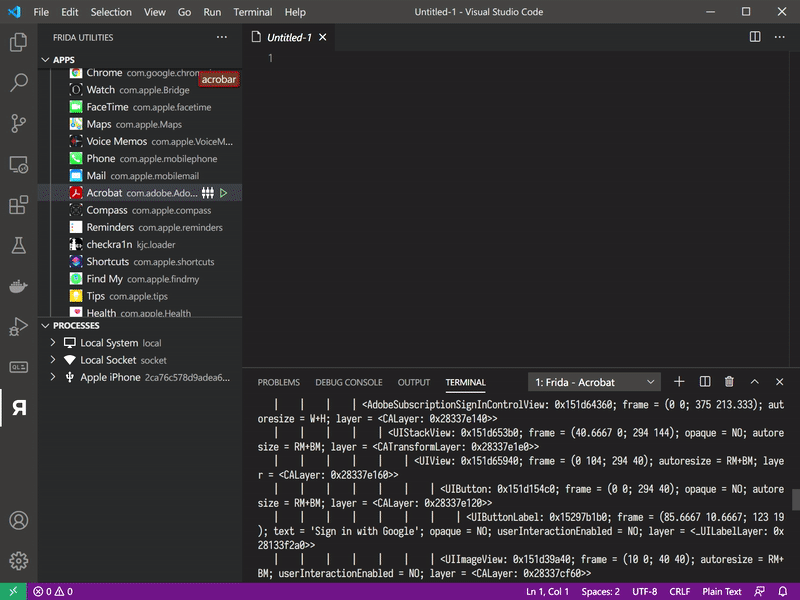
Reviewed ChiChou/vscode-frida@271aa36
Binary · Tool:
Command-line binary diffing engine that drives Ghidra headlessly through pyghidra: it imports and analyzes an old and a new binary, then reports added, deleted and modified functions, with patch diffing as its main use.
Reviewed clearbluejar/ghidriff@4f5d895
Binary · Tool:
GrammaTech's Datalog disassembler, which turns ELF and PE binaries for x86-32, x86-64, ARM32, ARM64 and MIPS32 into the GTIRB intermediate representation.
Reviewed GrammaTech/ddisasm@1d17f29
Binary · Tool:
Linux front end for the GNU Debugger (GDB), focused on games but usable for other reverse engineering; the name stands for “PINCE is not Cheat Engine”.
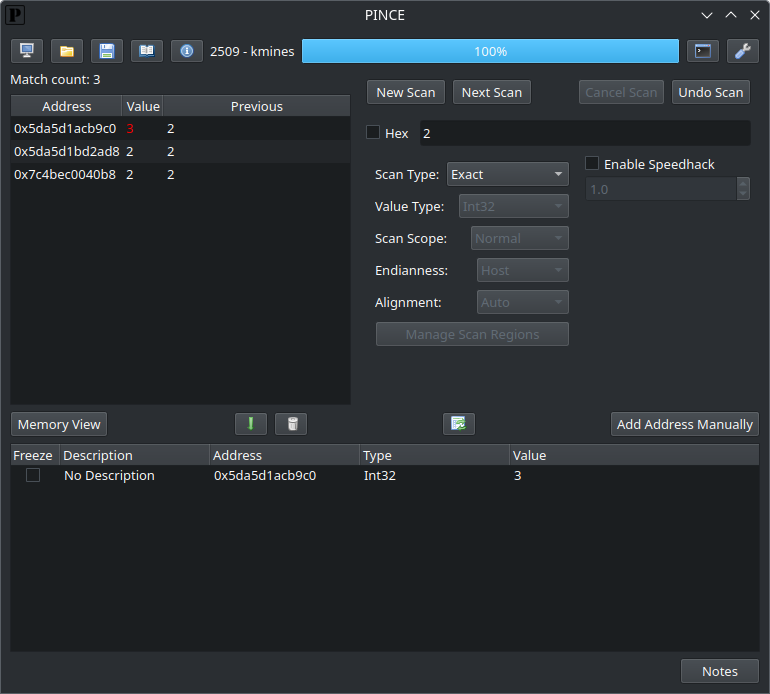
Reviewed korcankaraokcu/PINCE@9357ba3
Binary · Tool:
Cross-version decompiler that translates Python bytecode back into equivalent Python source, accepting bytecode from Python 1.0 through 3.8 as well as some PyPy bytecode and Dropbox's Python 2.5.
Reviewed rocky/python-uncompyle6@91298ba
Binary · Tool:
Reverse-Engineering Tools SYNChronization: plugins that keep IDA, Ghidra or Binary Ninja graph and decompiler views following a live WinDbg, GDB, LLDB, OllyDbg 1.10/2 or x64dbg session, rebasing addresses on the fly so ASLR does not break the mapping.
Reviewed bootleg/ret-sync@60e7b0f
Binary · Tool:
Single-file Python script that extracts the contents of executables built with PyInstaller, including Linux ELF builds without other tools.
Binary · Tool:
OCaml binary analysis platform from Carnegie Mellon University.
Reviewed BinaryAnalysisPlatform/bap@034bbd0
Binary · Tool:
General-purpose decompiler that loads executables or raw images, scans their machine code into a machine-independent register transfer language, groups it into procedures and decompiles them into high-level C code.
Reviewed uxmal/reko@63c497a
Binary · Tool:
Binary instrumentation, analysis and modification libraries from the Paradyn project.
Reviewed dyninst/dyninst@0c08389
Binary · Tool:
Rust crate for zero-copy, endian-aware parsing of ELF32/64, 32/64-bit Mach-O and multi-architecture fat containers, PE32/PE32+, COFF objects, Terse Executable (TE) images and Unix/BSD archives; Object::parse picks the format from its magic bytes.
Reviewed m4b/goblin@24a6260
Binary · Tool:
Mandiant FLARE string extractor for malware analysis that is used like strings.exe but also recovers obfuscated strings.
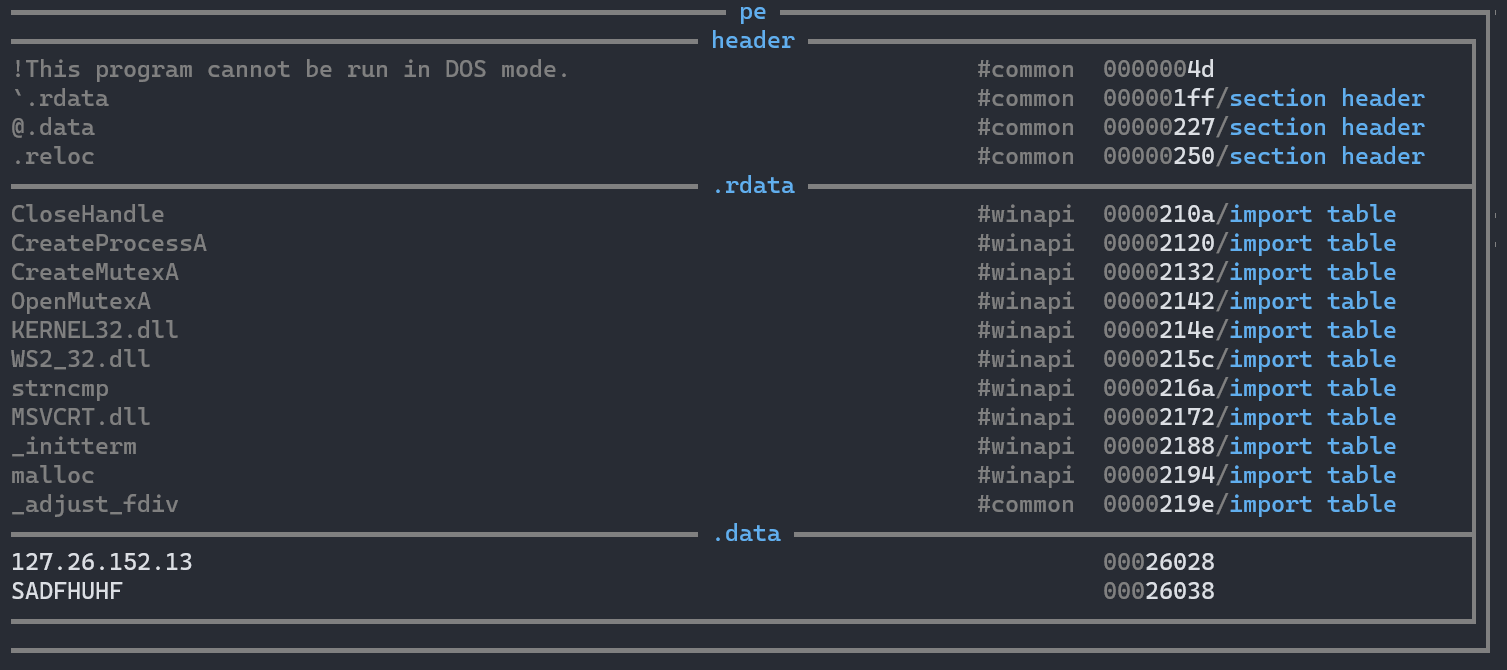
Reviewed mandiant/flare-floss@e100790
Binary · Tool:
Lightweight C11 x86/x86-64 disassembler and code-generation library.
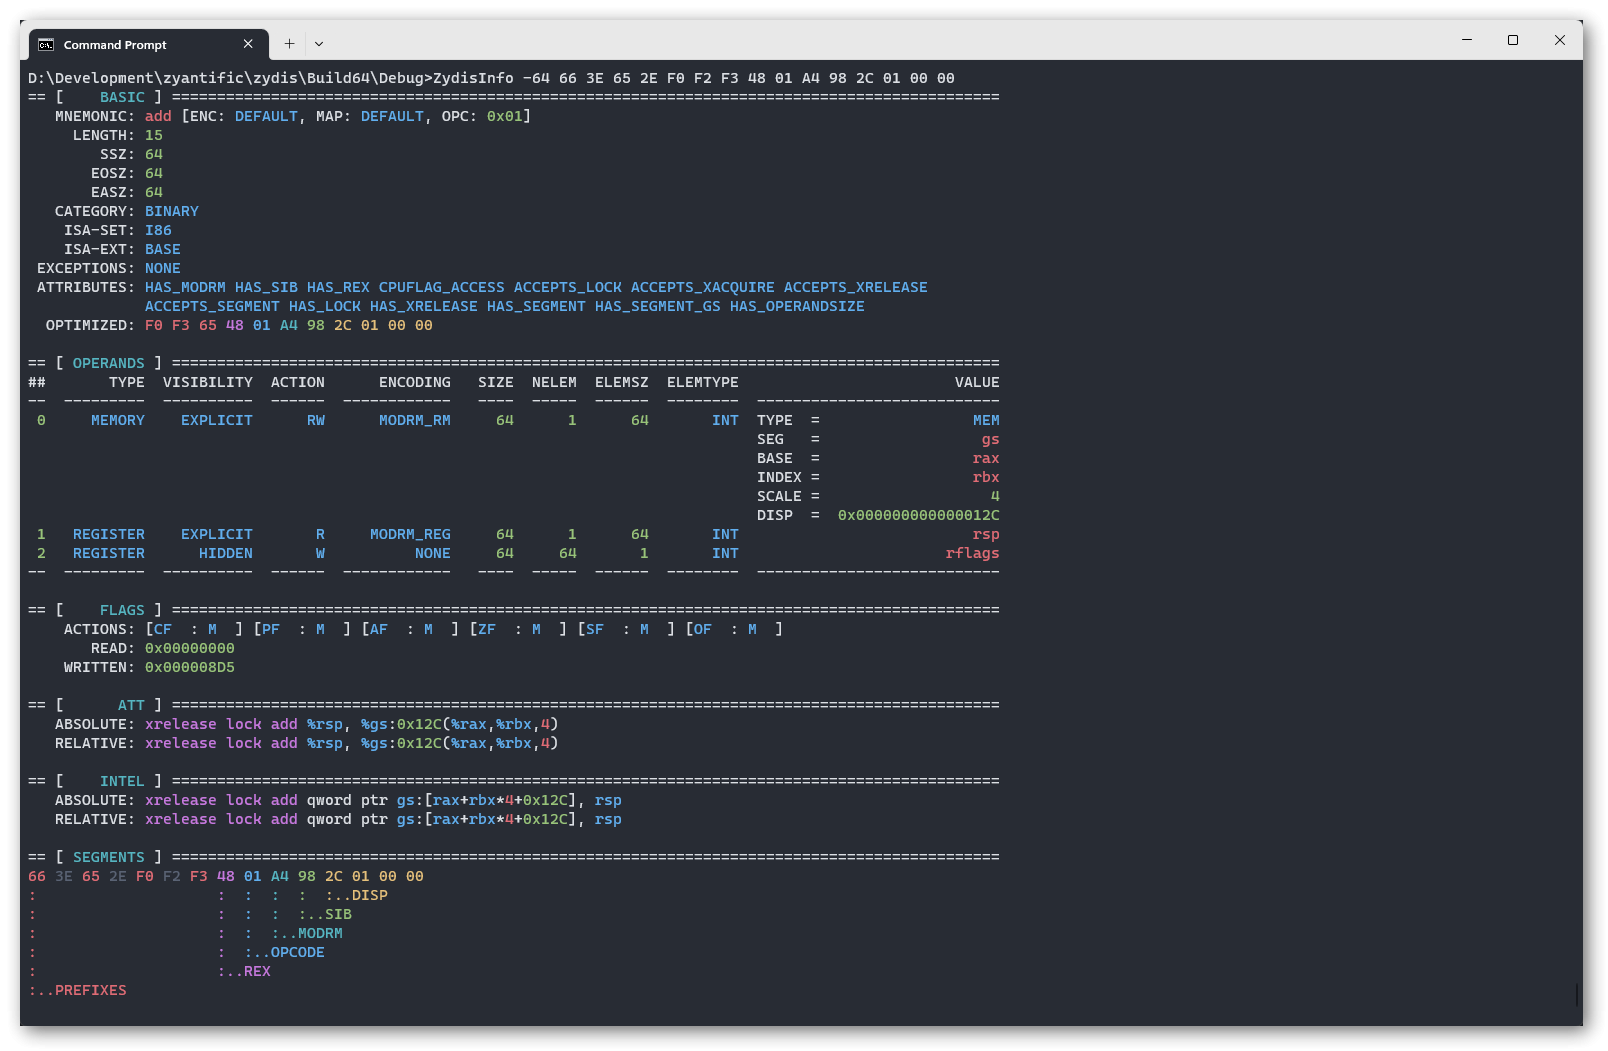
Reviewed zyantific/zydis@a95bb71
Binary · Tool:
Quarkslab's modular dynamic binary instrumentation (DBI) framework, which JIT-recompiles a program's basic blocks inside its own process so that an instrumentation tool can register callbacks before or after instructions, on memory reads and writes, and on VM events.
Reviewed QBDI/QBDI@3318580
Binary · Tool:
Terminal user interface for inspecting ELF binaries.
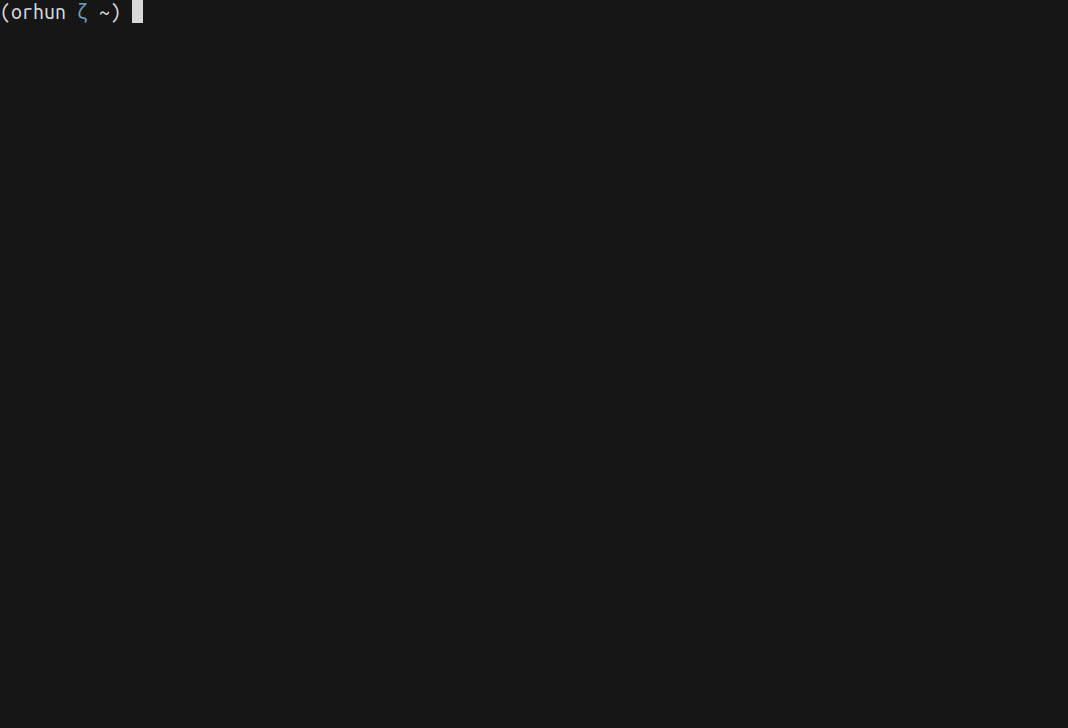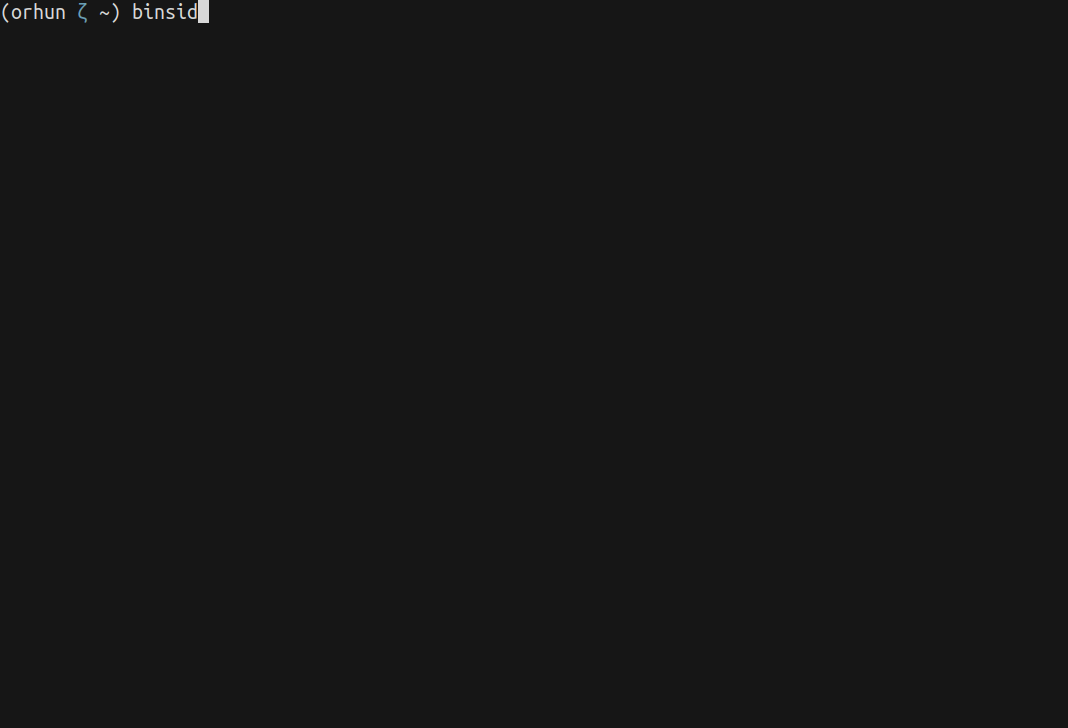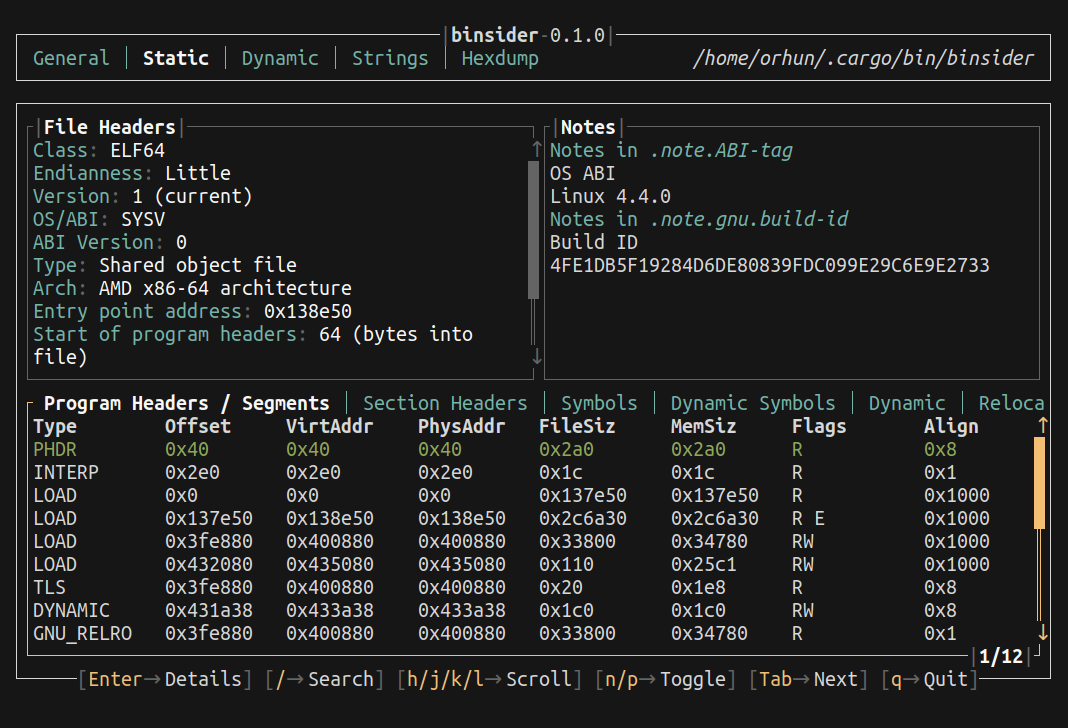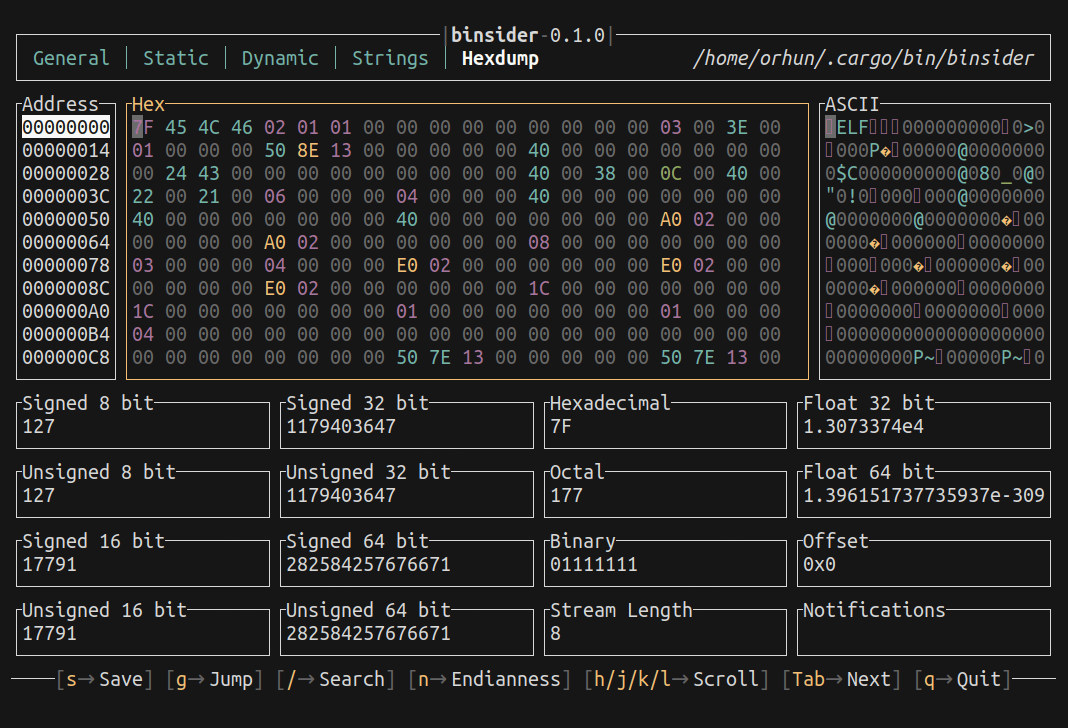
Reviewed orhun/binsider@7f0633d
Binary · Tool:
x86 instruction library for 16-, 32- and 64-bit code that decodes, formats, assembles and encodes instructions, with masm, nasm, GNU AT&T and Intel XED output syntaxes.
Reviewed icedland/iced@8cfc5f5
Binary · Tool:
IDA plugin published by Kaspersky that extends the Hex-Rays decompiler with tools its author collected for reverse-engineering work, including malware analysis.
Reviewed KasperskyLab/hrtng@2c7b78e
Binary · Tool:
Static binary code analysis toolkit designed for reverse engineers.
Reviewed airbus-seclab/bincat@5d0ee3b
Binary · Tool:
Single-file Python extension, gef.py, that adds dynamic-analysis commands to GDB.
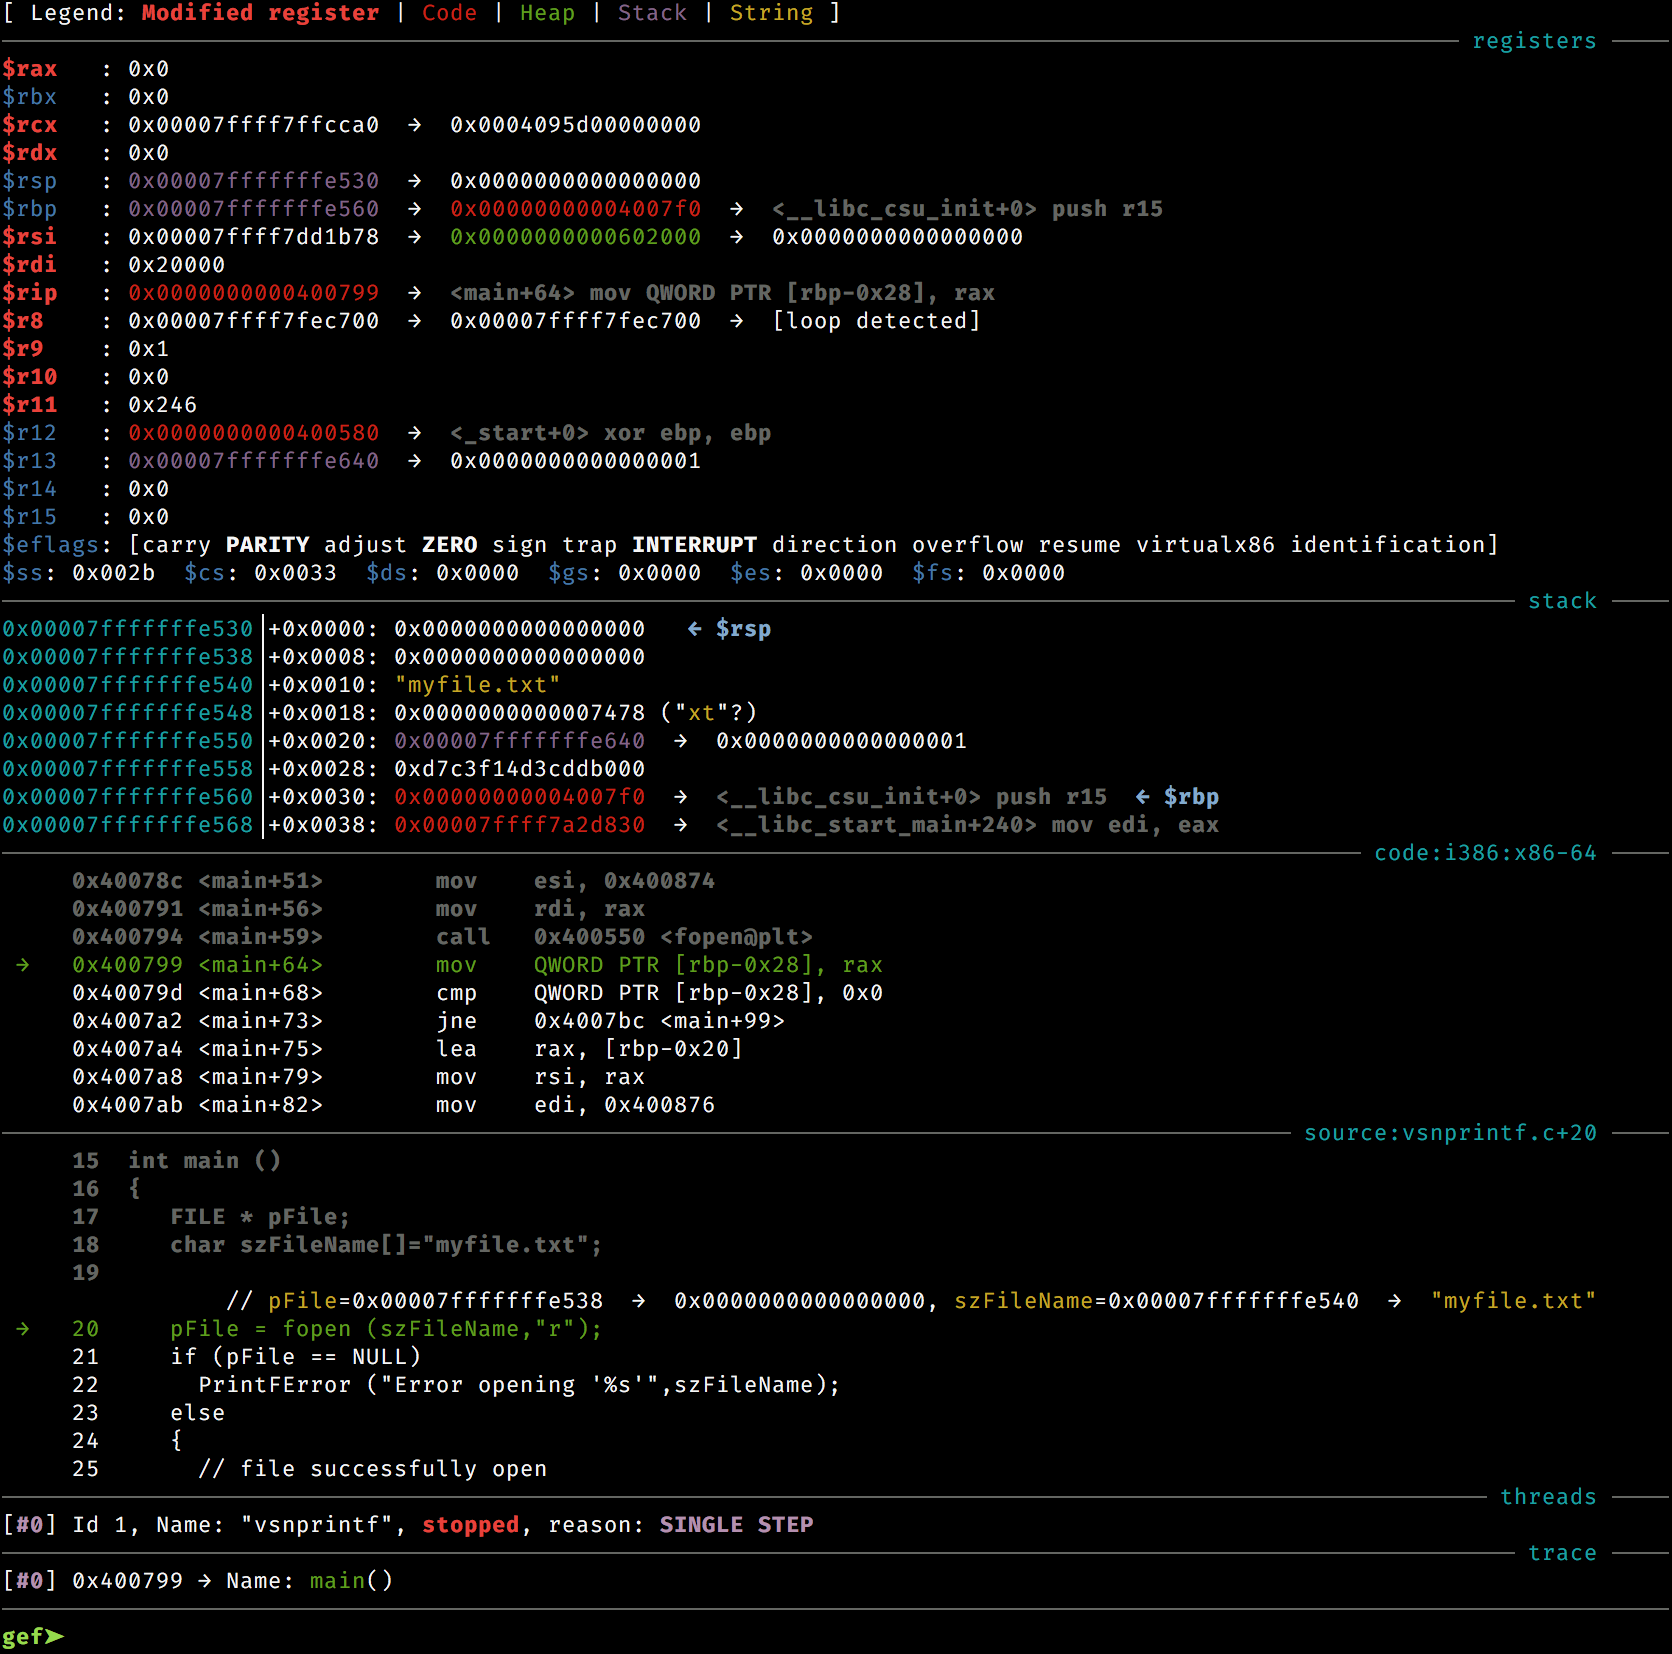
Reviewed hugsy/gef@49c07dc
Binary · Tool:
C++ library with Python bindings for dynamic binary analysis of x86, x86-64, ARM32, AArch64 and RISC-V 32/64 code.
Reviewed JonathanSalwan/Triton@bc84cf7
Binary · Tool:
Research decompiler for CPython bytecode from Python 3.6 onward that pairs per-version transformer models with control-flow reconstruction.
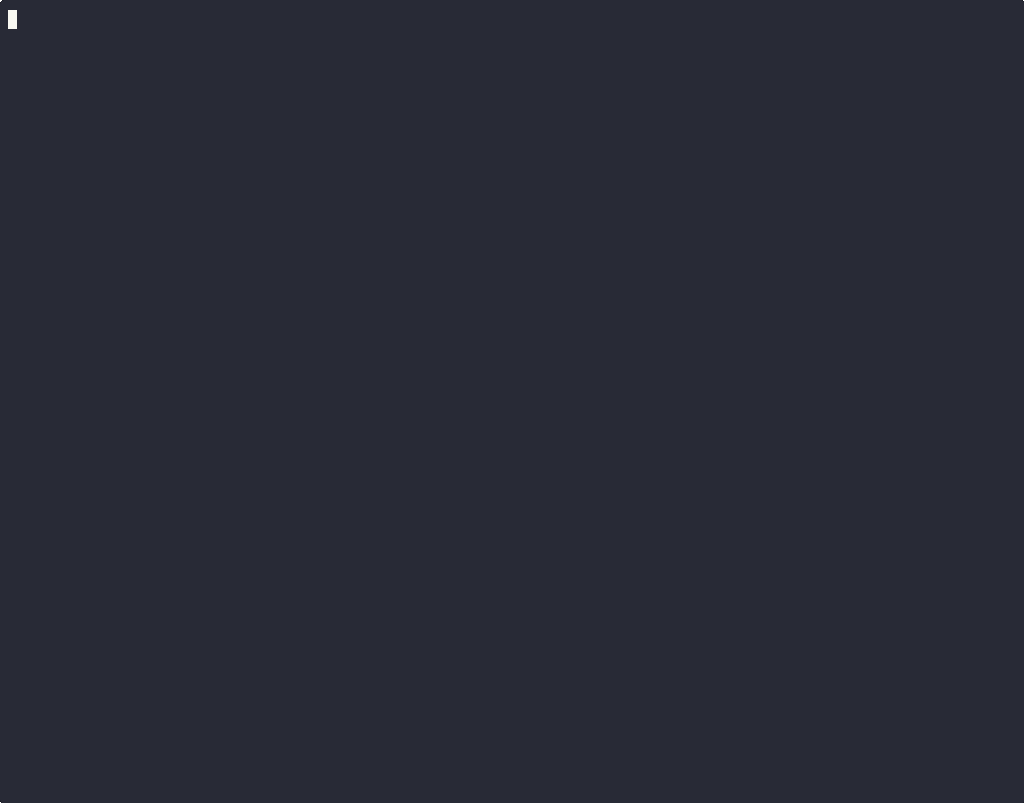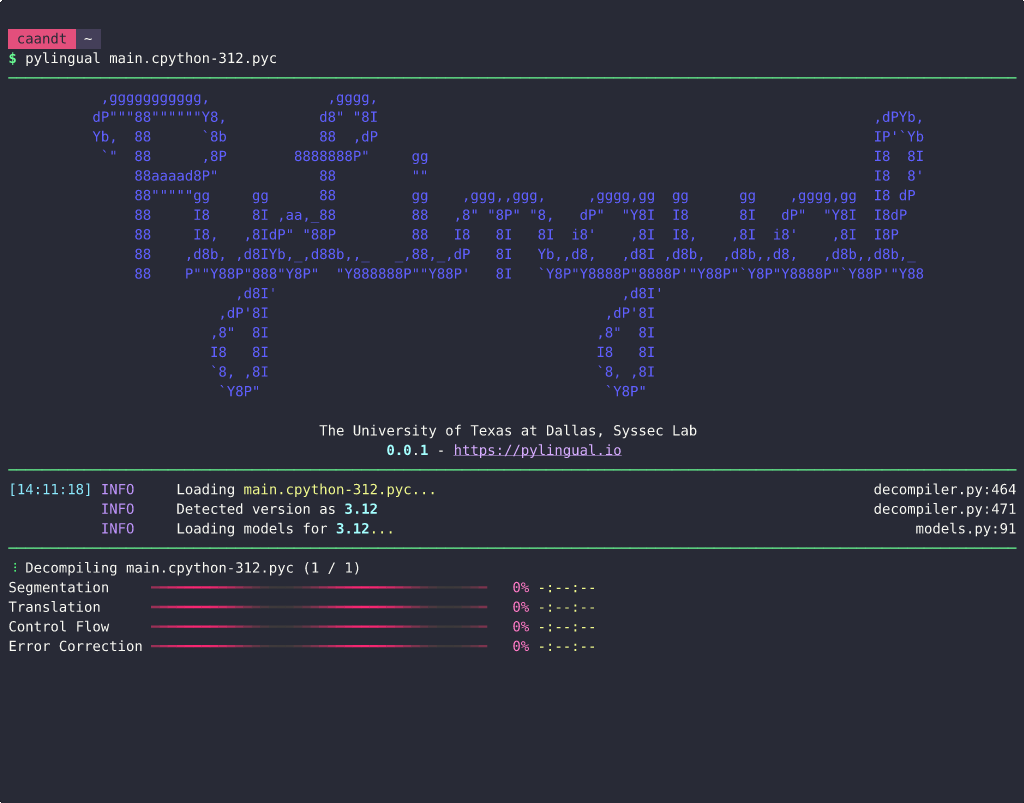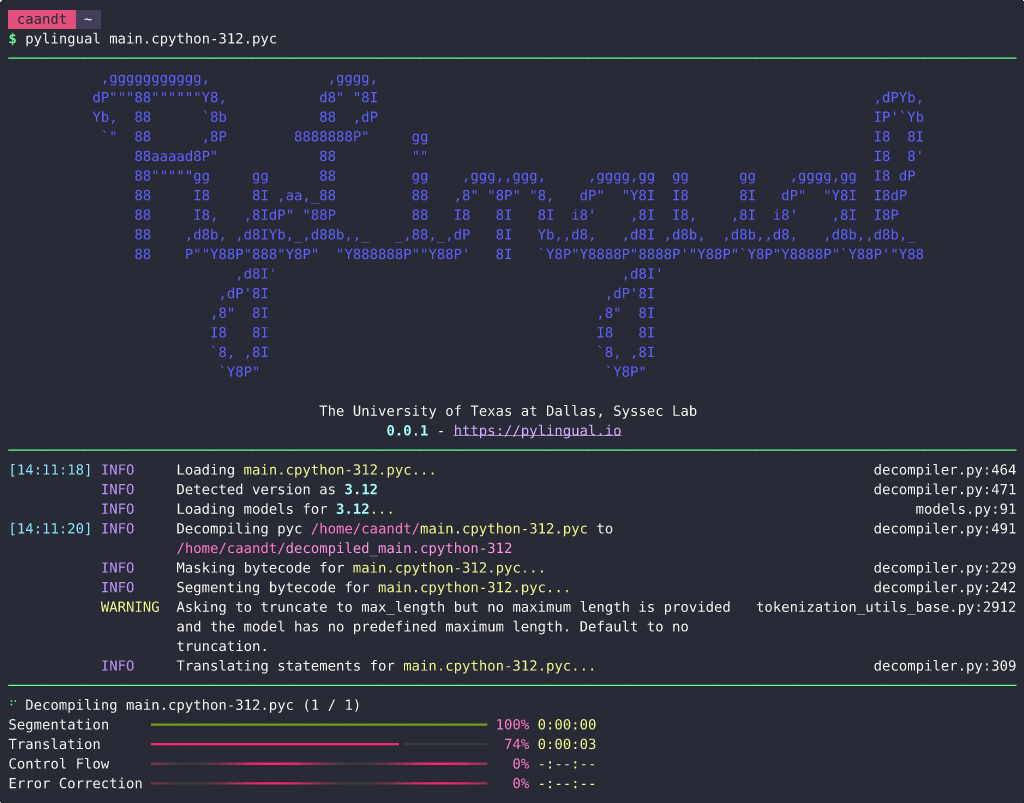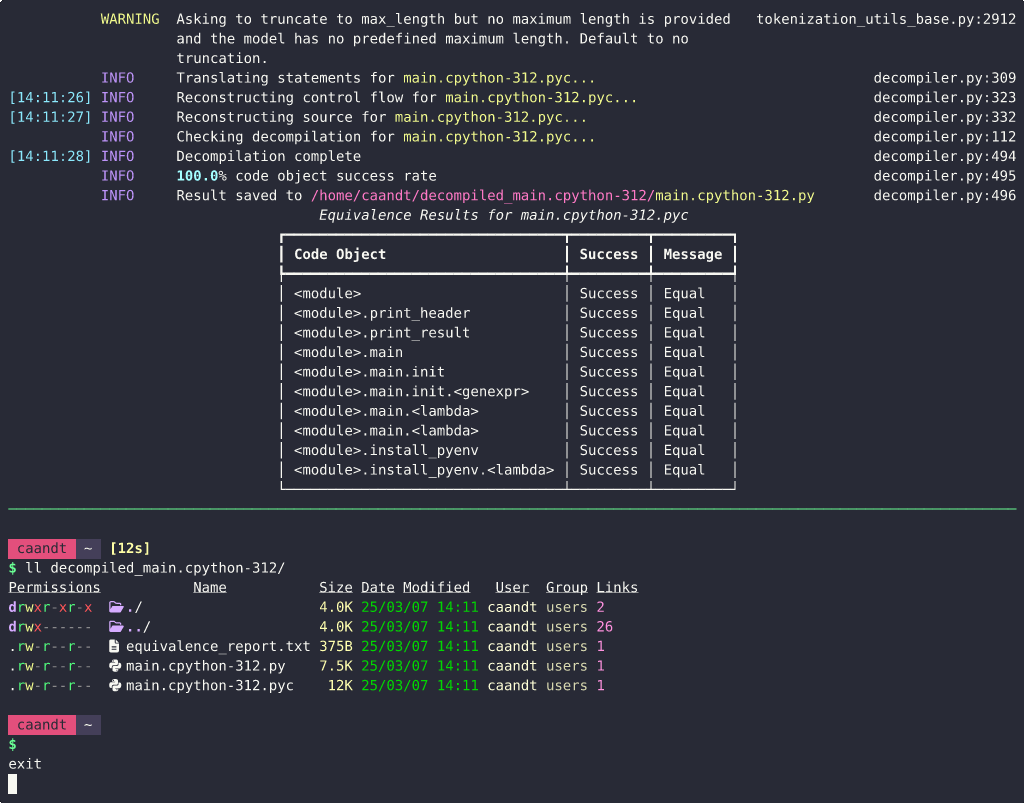
Reviewed syssec-utd/pylingual@509ea92
Binary · Tool:
Python reverse-engineering framework for analyzing, modifying and generating binary programs.
Reviewed cea-sec/miasm@3671fc2
Binary · Tool:
Hypervisor-assisted Windows debugger that virtualizes the running system with Intel VT-x and Extended Page Tables to debug kernel and user mode, either locally as a tracing and introspection tool or from a host attached over a serial connection to a guest virtual machine.
Reviewed HyperDbg/HyperDbg@ff3ba35
Binary · Tool:
Agent-first decompiler written in Rust that began as a port of Ghidra’s C++ decompiler and SLEIGH compiler, and has since diverged with option-gated features, some ported from angr.
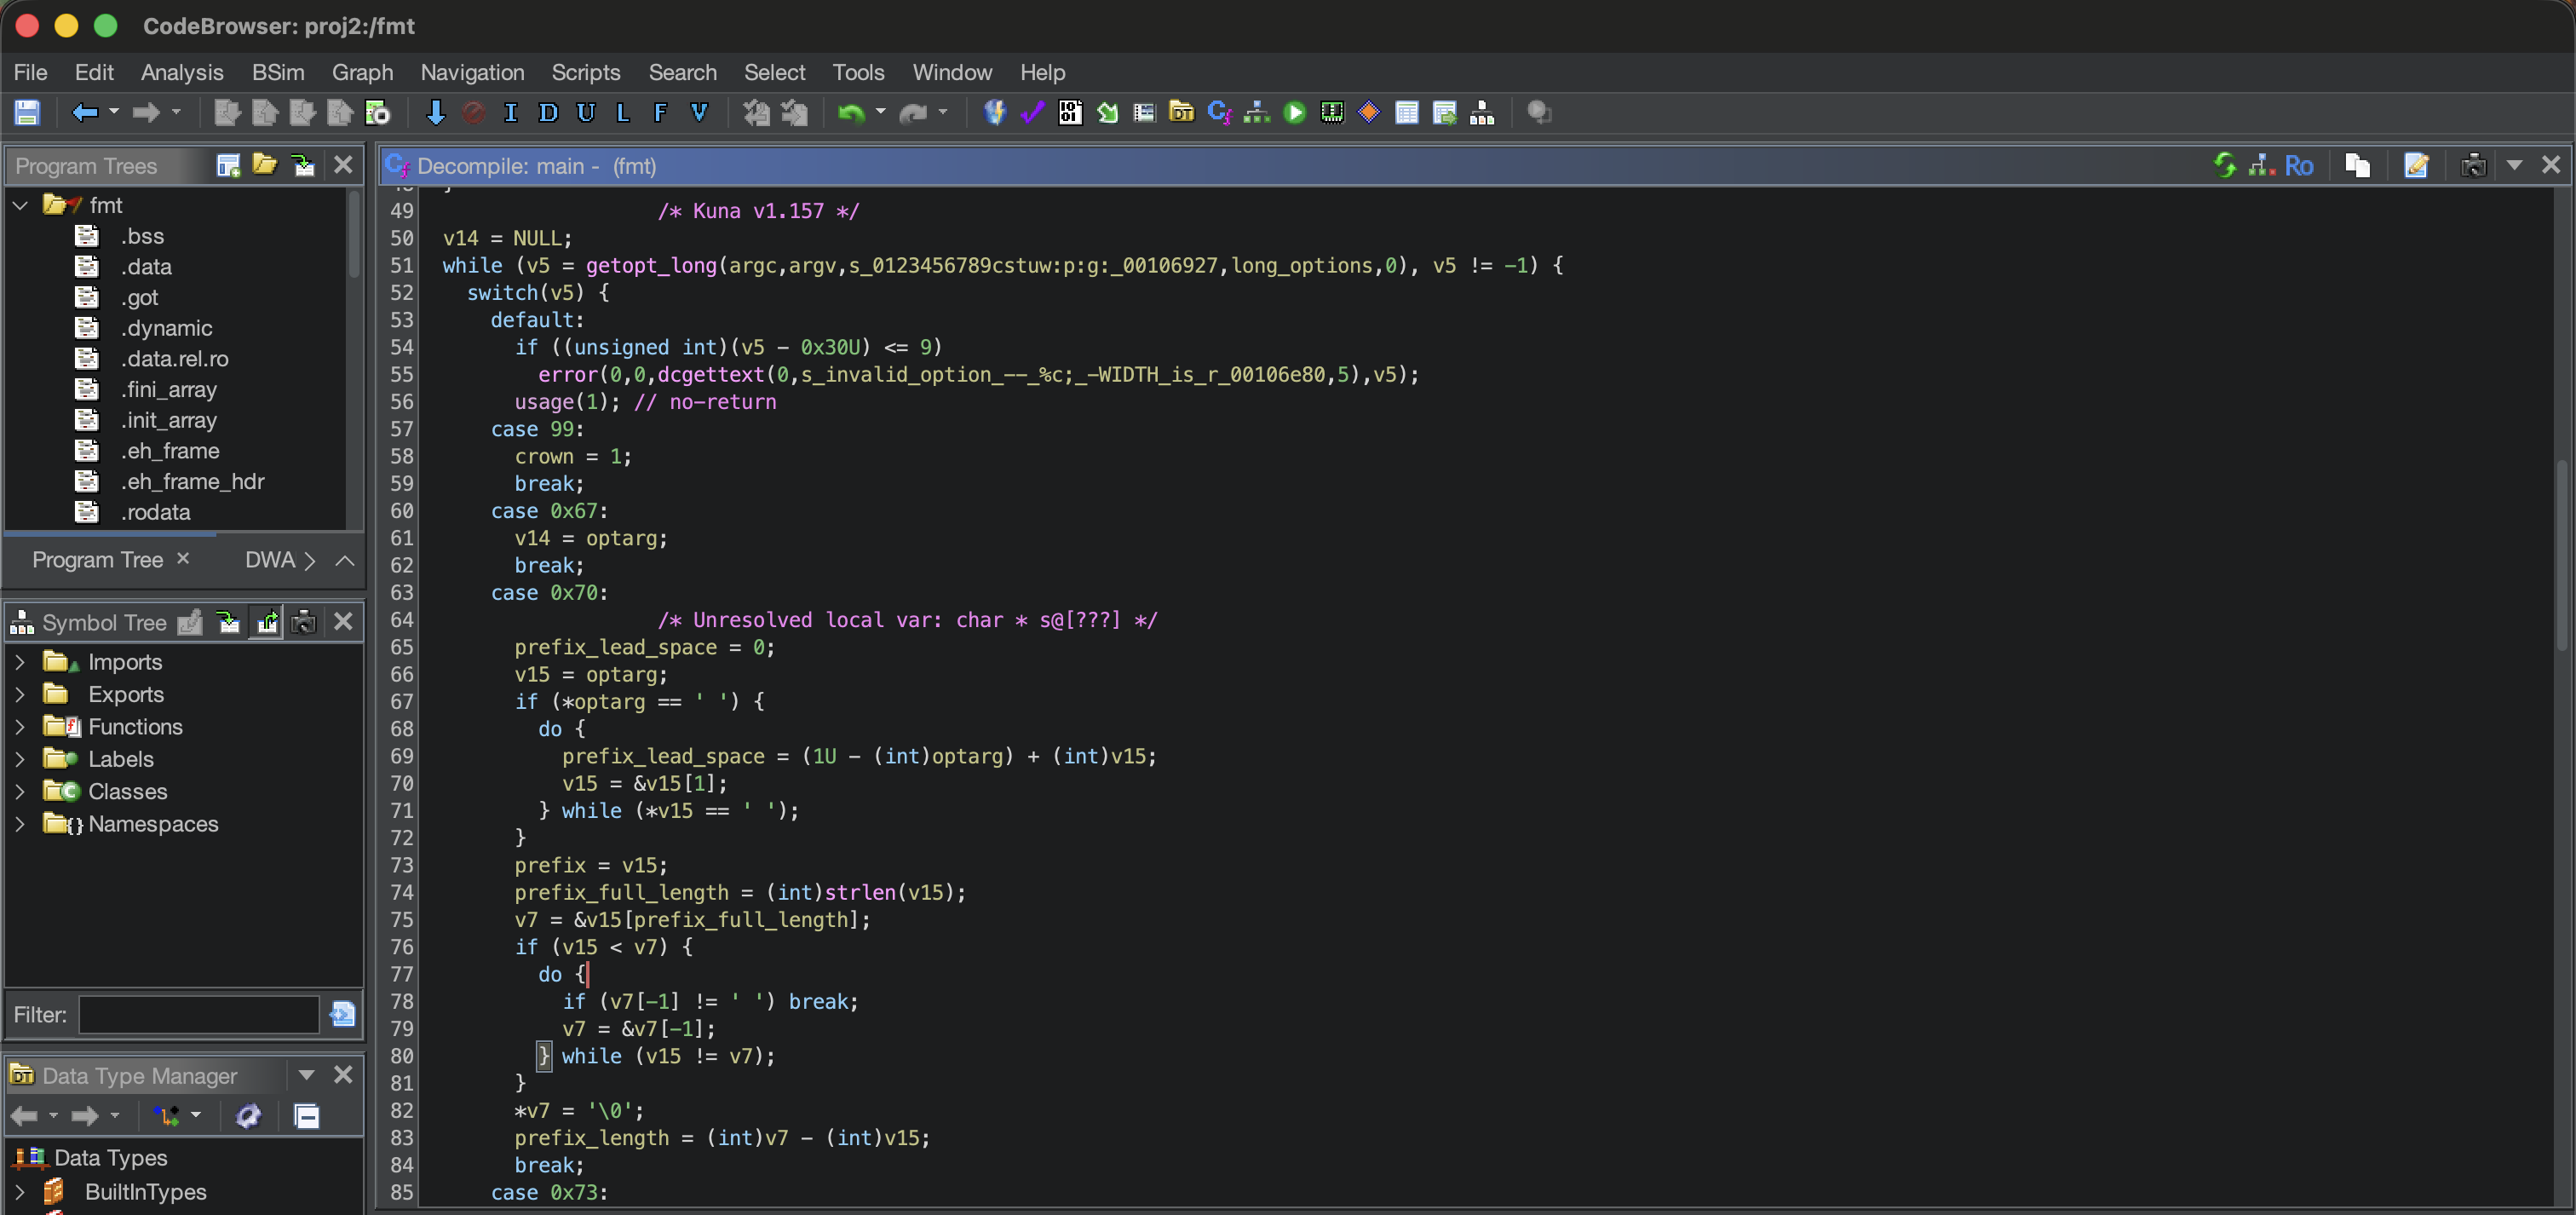
Reviewed Noelo-Lab/kuna@d1f98e5
Binary · Tool:
Vector 35’s public C++, Python and Rust APIs for Binary Ninja, with their documentation, examples and the open-source plugins built on them.
Reviewed Vector35/binaryninja-api@14d46ea
Binary · Tool:
Mandiant FLARE tool that reports what an executable can do by matching a YAML rule set against features extracted from PE, ELF and .NET files or 32/64-bit shellcode, such as API calls, imports, strings and constants.
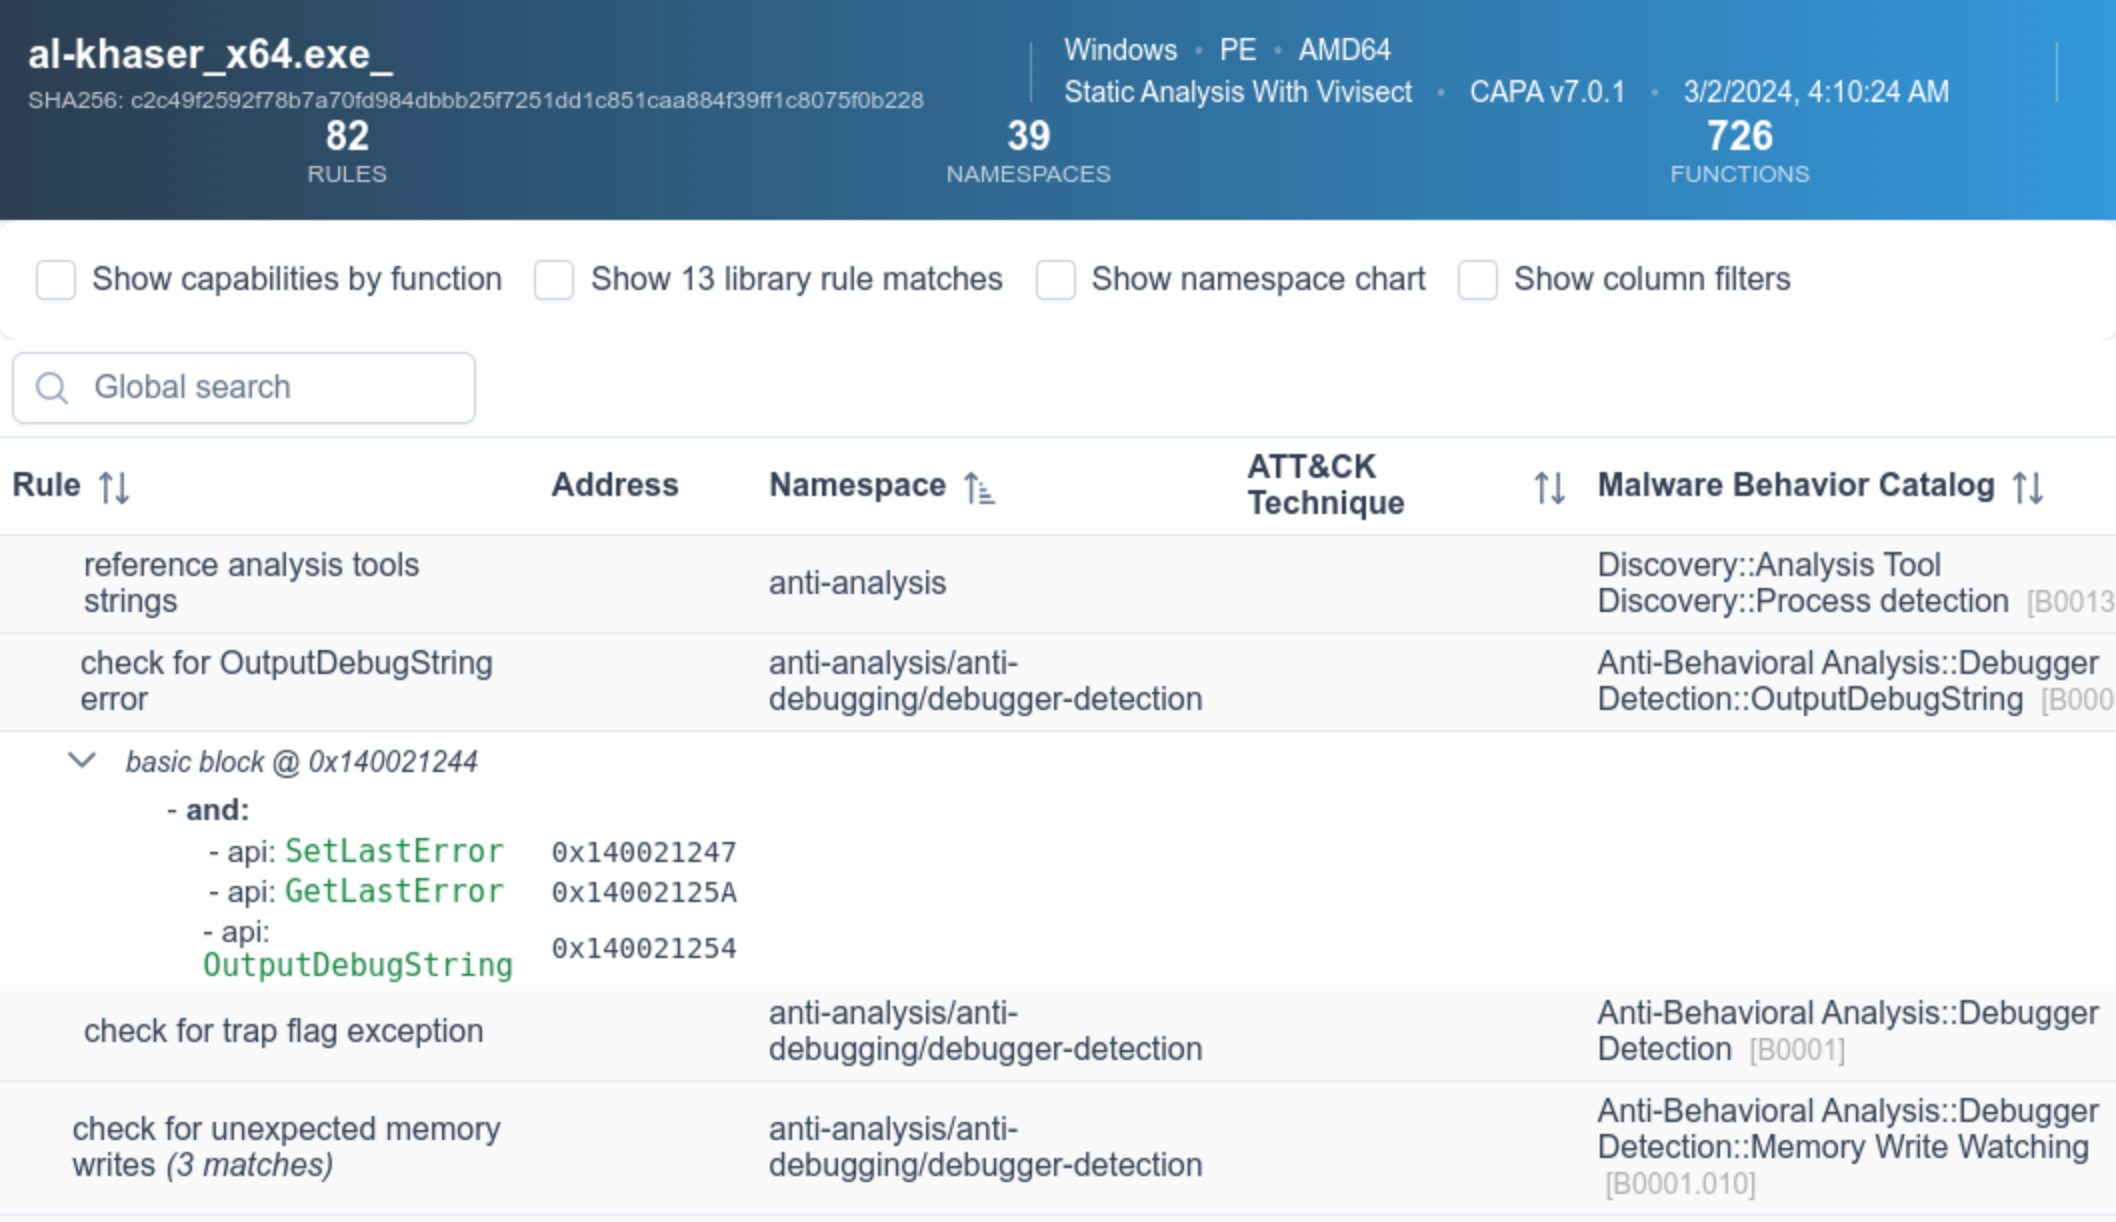
Reviewed mandiant/capa@7a235c4
Binary · Tool:
Avast's retargetable machine-code decompiler built on LLVM.
Reviewed avast/retdec@9450585
Binary · Tool:
Cross-platform interactive disassembler whose version 4 is a plain-C rewrite: a C17 engine library, the Qt6 GUI kept in this repository, and loader, processor and analyzer plugins loaded as shared libraries.
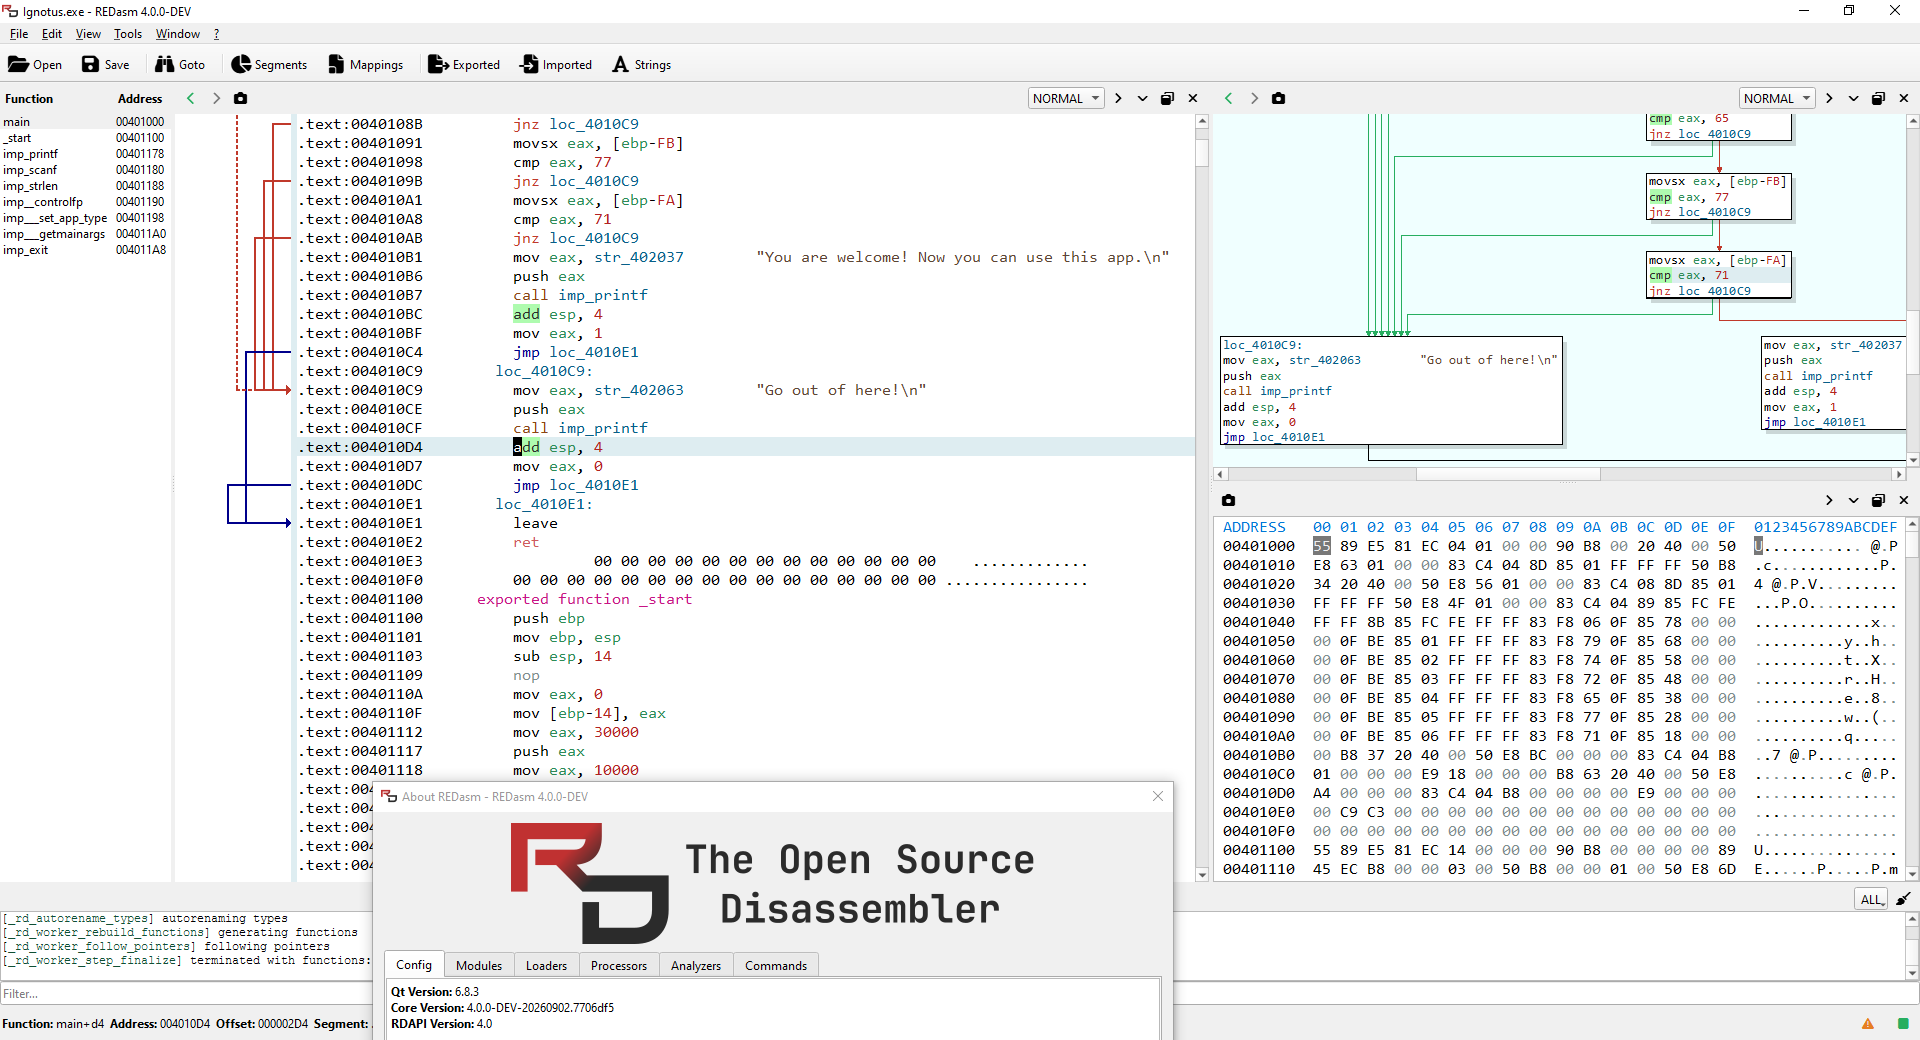
Reviewed redasm-dev/redasm@509b765
Binary · Tool:
Code-coverage explorer plugin for IDA Pro and Binary Ninja that loads execution traces of native programs and paints the executed code across the disassembler's views, without needing symbols or source.
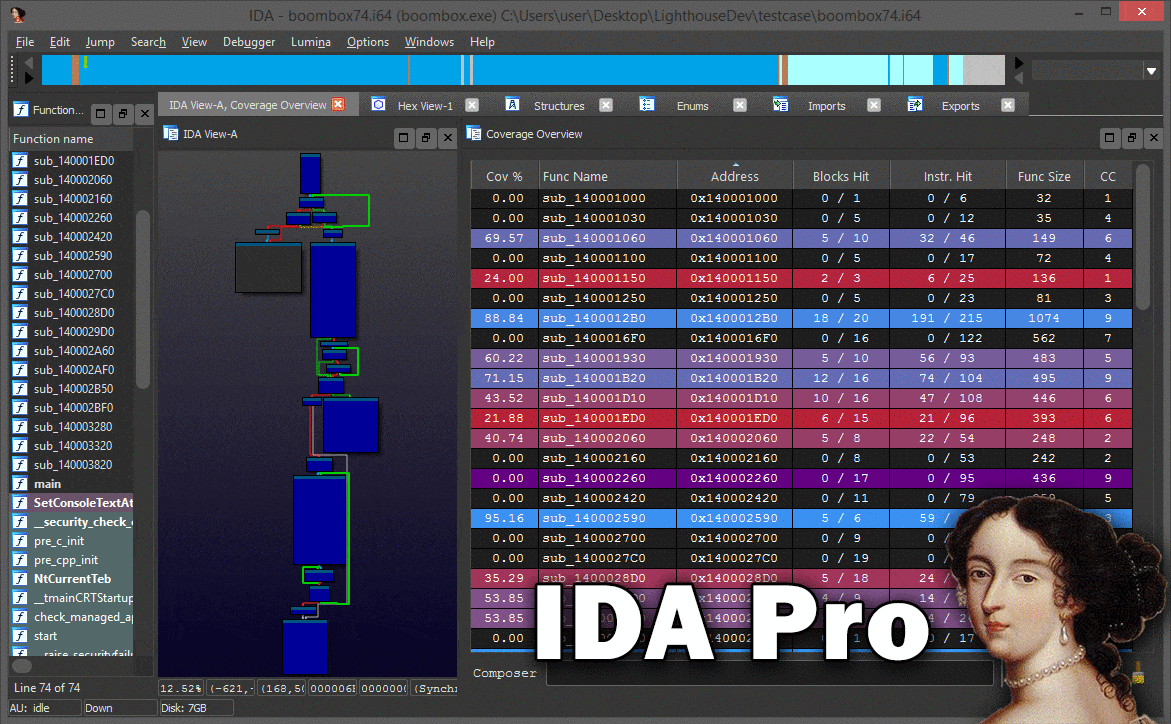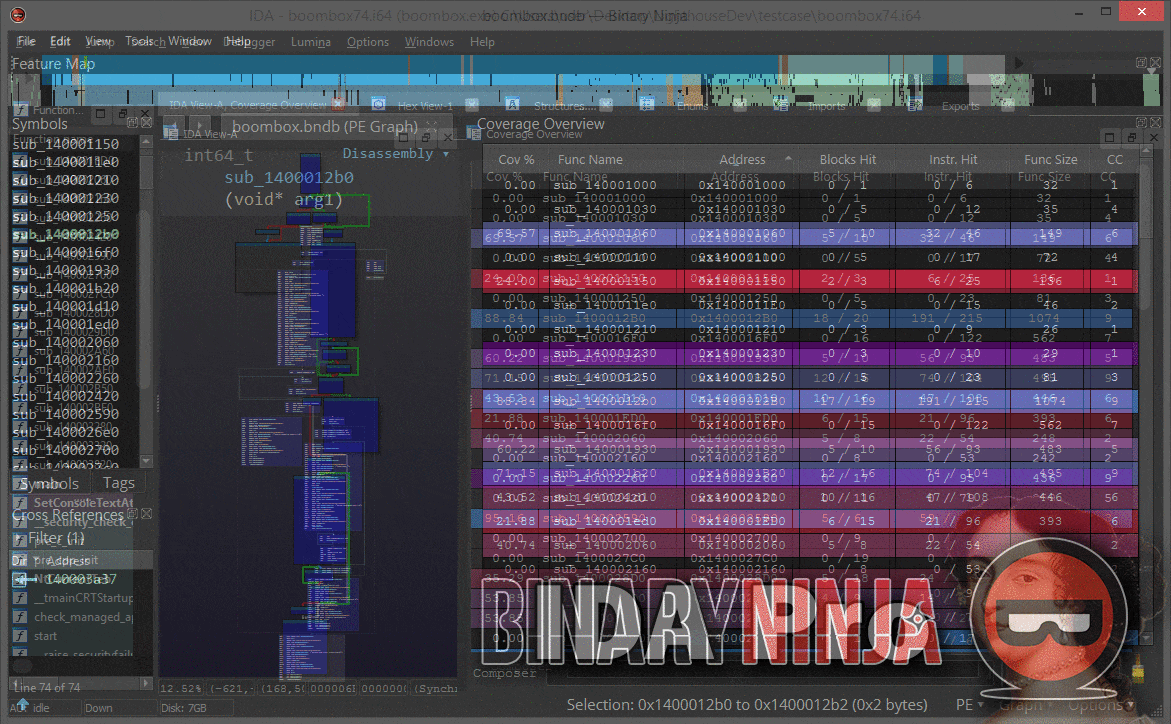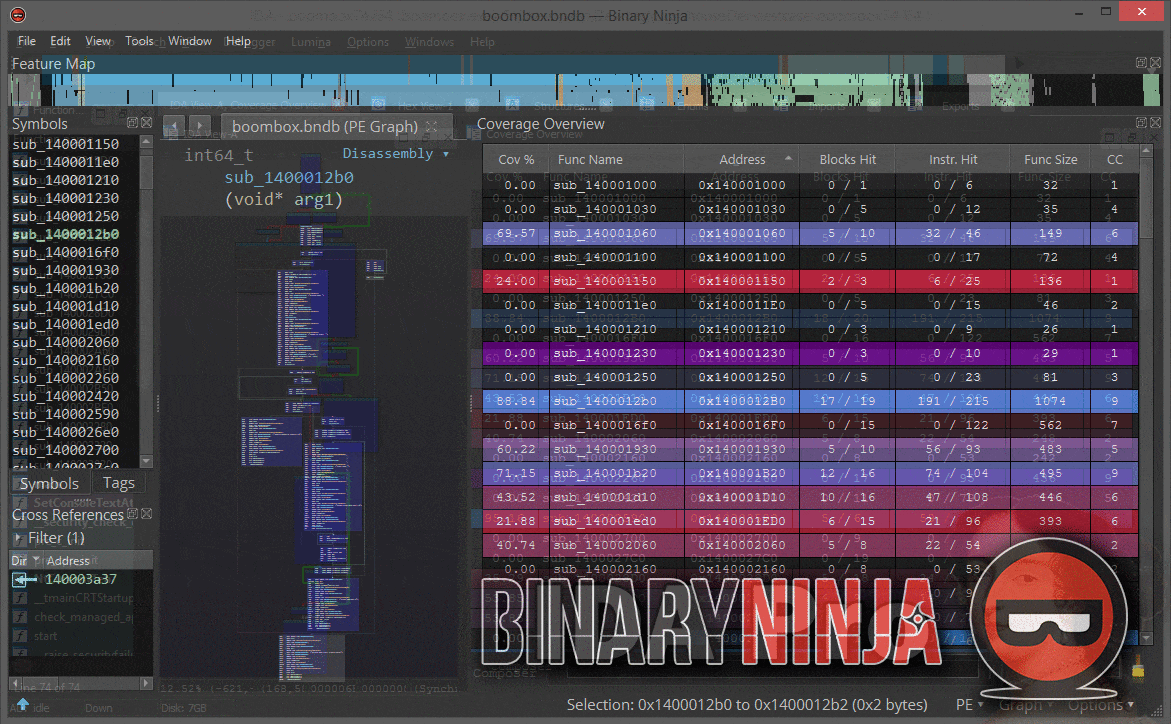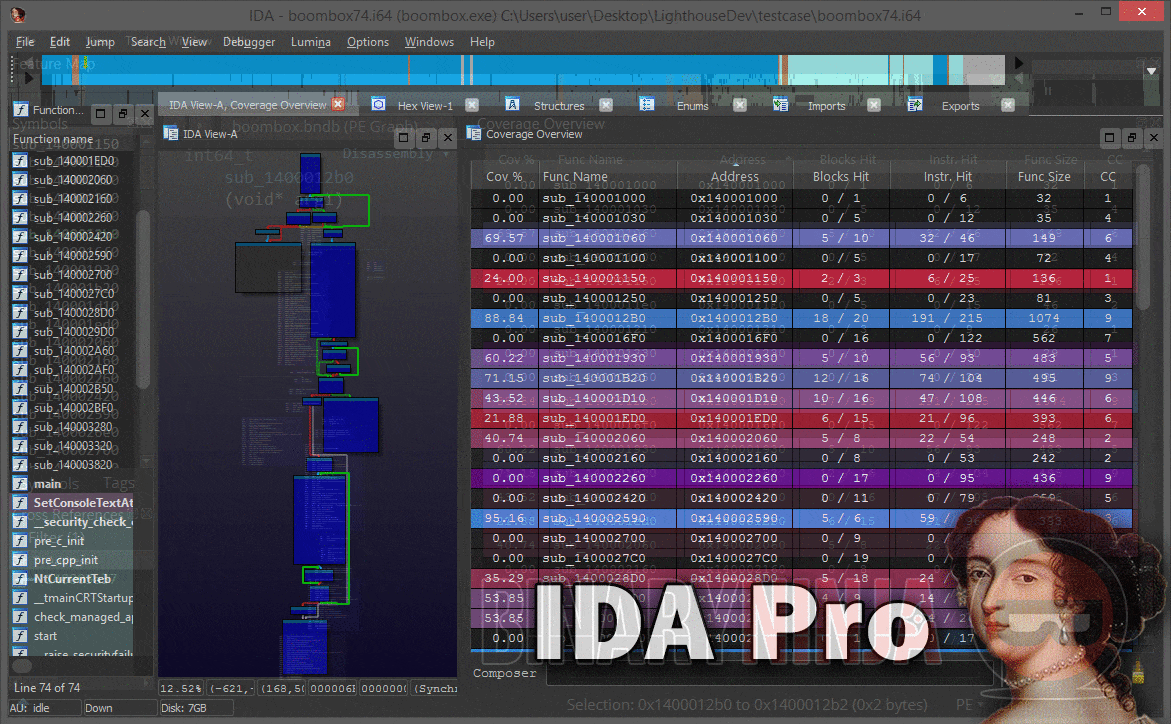
Reviewed gaasedelen/lighthouse@562595b
Binary · Tool:
Static vulnerability scanner from Tencent Keen Lab that runs as a Ghidra extension or headless script and applies abstract interpretation to Ghidra's P-code rather than to assembly, covering x86, x64, ARMv7 and AArch64 binaries.
Binary · Tool:
Open-source Community Edition of Binarly REsearch's VulHunt engine for hunting vulnerabilities in POSIX binaries and UEFI firmware on x86 and ARM.
Reviewed vulhunt-re/vulhunt@b2fa617
Binary · Tool:
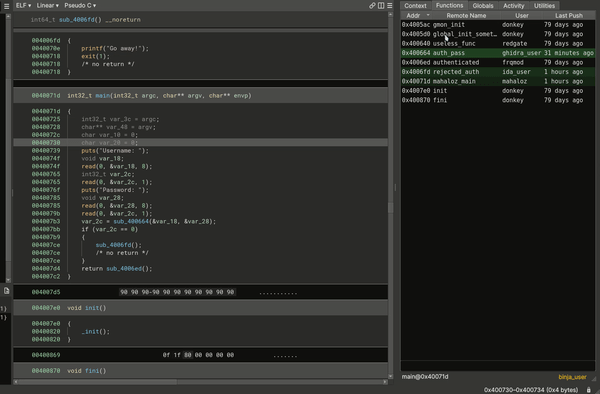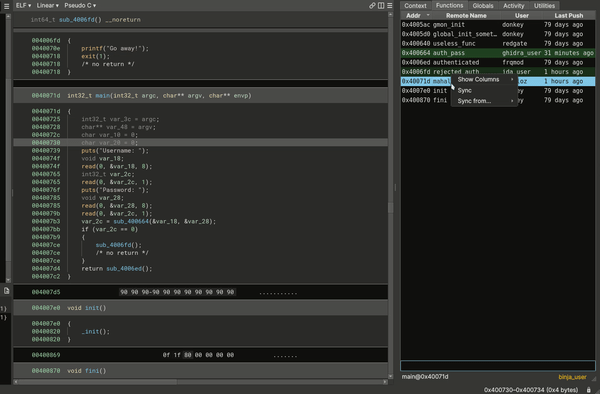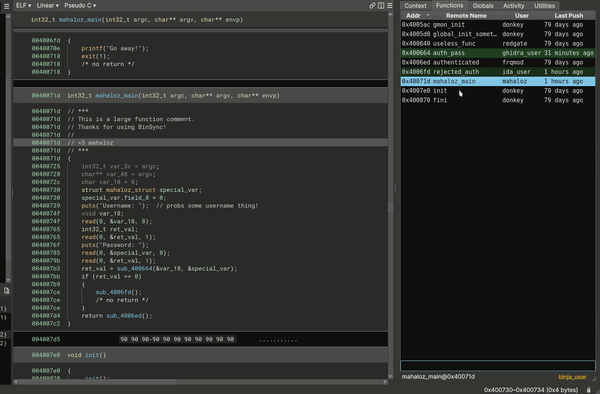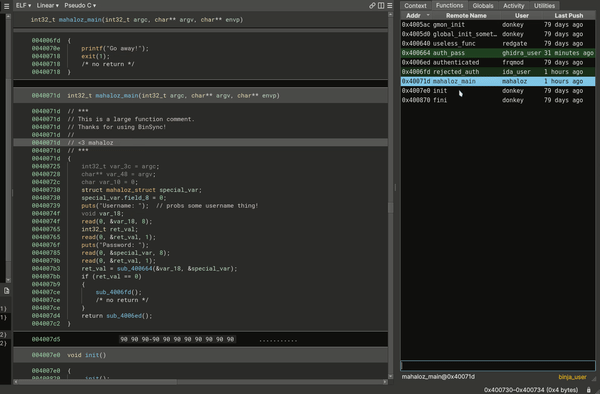
Decompiler plugin for collaborative reverse engineering that records each analyst's work in a shared Git repository, one branch per user, so teammates can pull, push or auto-push changes across IDA Pro, Binary Ninja, Ghidra and angr-management.
Reviewed binsync/binsync@07a2ce8
App · Tool:
Command-line utility that reads the Objective-C runtime metadata in Mach-O executables, frameworks and bundles and prints it as ordinary Objective-C declarations for the classes, categories and protocols it finds, the same information otool -ov shows in a more compact form.
Reviewed nygard/class-dump@2c82b4f
Binary · Tool:
IDA Pro plugin by Markus Gaasedelen for studying how the Hex-Rays decompiler transforms its microcode intermediate language.
Reviewed gaasedelen/lucid@9f2480d
Binary · Tool:
Decompiler plugin for radare2 that turns the disassembly of an analyzed function into pseudo-C through the pdd command.
Reviewed wargio/r2dec-js@32ada0d
App · Tool:
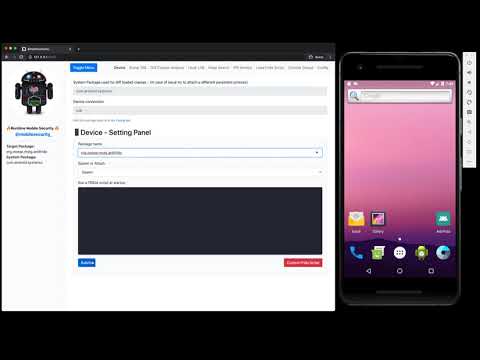
Frida-based web interface for observing Android and iOS apps at run time on a test device.
Binary · Tool:
Carnegie Mellon SEI's framework of automated static analysis tools for binary programs, built on LLNL's ROSE compiler infrastructure for disassembly, control-flow analysis and instruction semantics.
Reviewed cmu-sei/pharos@782492f
Binary · Tool:
Rust toolkit by Jonathan Becker for analyzing EVM smart-contract bytecode, particularly of contracts without verified source.
Reviewed Jon-Becker/heimdall-rs@9de15de
Binary · Tool:
Qt GUI to view and edit Windows Portable Executable files, meant as a fast first look for malware analysts and robust against malformed PE32 and PE64 files.
Reviewed hasherezade/pe-bear@b90f1d7
Binary · Tool:
Windows process scanner by hasherezade that finds and dumps implants in one running process: replaced or injected PE modules, shellcode, inline and IAT hooks and other in-memory patches, with the README naming Process Hollowing, Process Doppelgänging and reflective DLL injection among the techniques it detects.
Reviewed hasherezade/pe-sieve@98788a6
Binary · Tool:
Python package by Philippe Lagadec for analyzing Microsoft OLE2 (Compound File Binary) files such as Office 97–2003 documents, MSI files and Outlook messages, as well as RTF and OpenXML documents, mainly for malware analysis, forensics and debugging.
Reviewed decalage2/oletools@ec10260
App · Tool:
Based on iOSOpenDev, MonkeyDev adds a MonkeyApp project template to Xcode for instrumenting iOS apps the developer is authorized to analyze.
Reviewed AloneMonkey/MonkeyDev@f906af1
Binary · Tool:
Windows command-line memory scanner by hasherezade that runs the PE-sieve engine across many processes, or the whole system, instead of a single PID.
Reviewed hasherezade/hollows_hunter@831561c
App · Tool:
macOS command-line tool that writes a stripped iOS app's Mach-O executable back out with a rebuilt symbol table, so a debugger such as lldb can break on and display Objective-C method names.
Reviewed tobefuturer/restore-symbol@83ccb90
Binary · Tool:
Mandiant FLARE's dynamic network analysis tool for malware analysts, a successor to the original Fakenet.
Reviewed mandiant/flare-fakenet-ng@7c8e006
Binary · Tool:
Static code analysis platform that parses source code, JVM bytecode and executables into code property graphs held in a graph database and queried with a Scala-based language from an interactive shell or server mode.
Reviewed joernio/joern@7f886b3
Binary · Tool:
Mandiant's Windows malware emulation framework, which runs PE executables, DLLs, kernel drivers and raw x86/amd64 shellcode on the Unicorn CPU emulator inside a modeled Windows runtime instead of a full VM.
Reviewed mandiant/speakeasy@aa9f226
Binary · Tool:
Single-file IDA plugin of convenience actions first written for CTF work.
Reviewed L4ys/LazyIDA@0ecdf8d
Binary · Tool:
Intel Pin tool by hasherezade that traces a 32- or 64-bit program while it runs on Windows or Linux, logging API calls (with arguments and return values for watched functions), chosen local and statically linked functions, inline system calls, RDTSC, CPUID and INT instructions, and transitions between sections of the traced module, which helps find the original entry point of a packed module.
Reviewed hasherezade/tiny_tracer@99618fc
Binary · Tool:
IDA Pro plugin, described by its repository as the winner of the 2016 IDA plugin contest, that brings the Triton framework's taint analysis and symbolic execution into IDA's debugger for x86 and x64 programs.
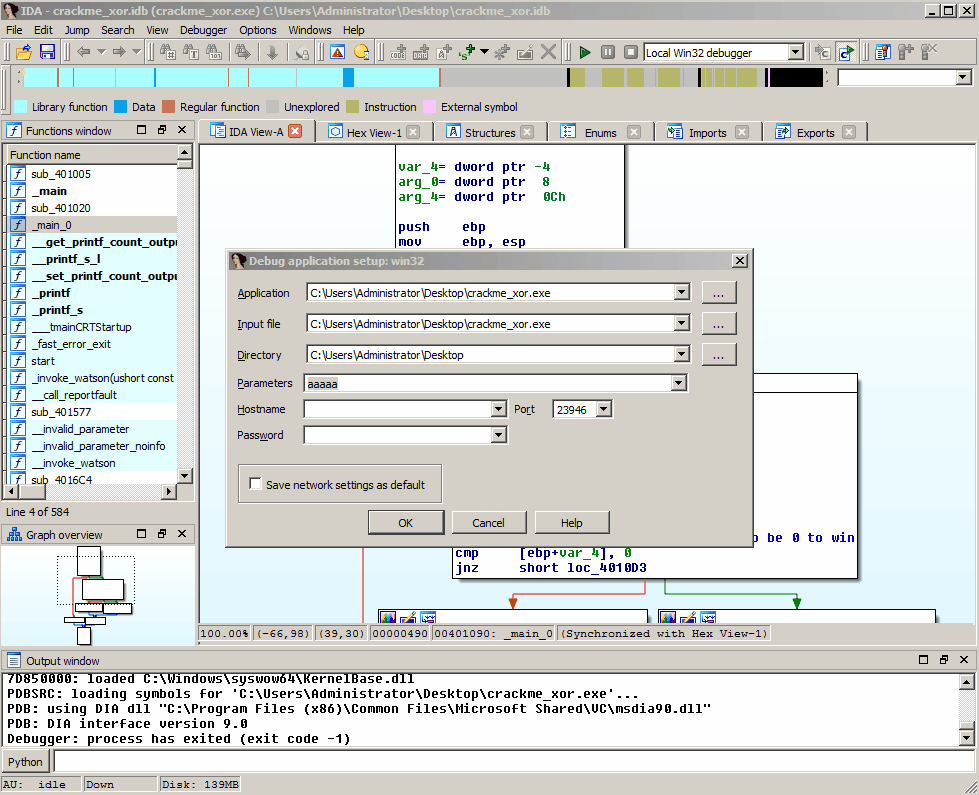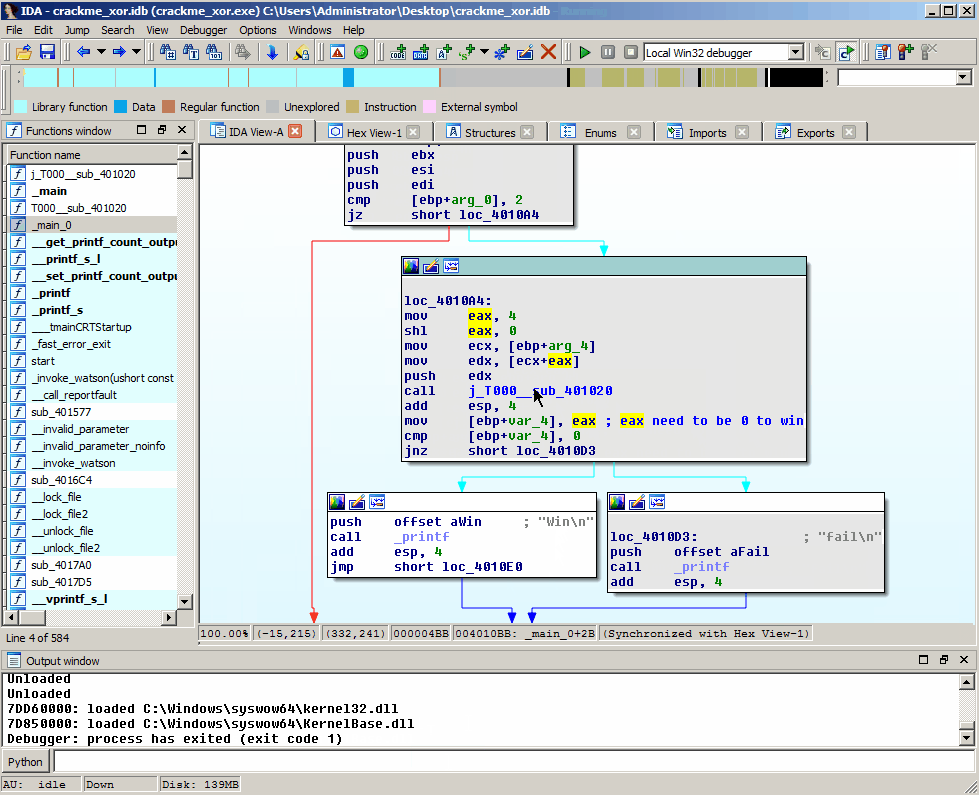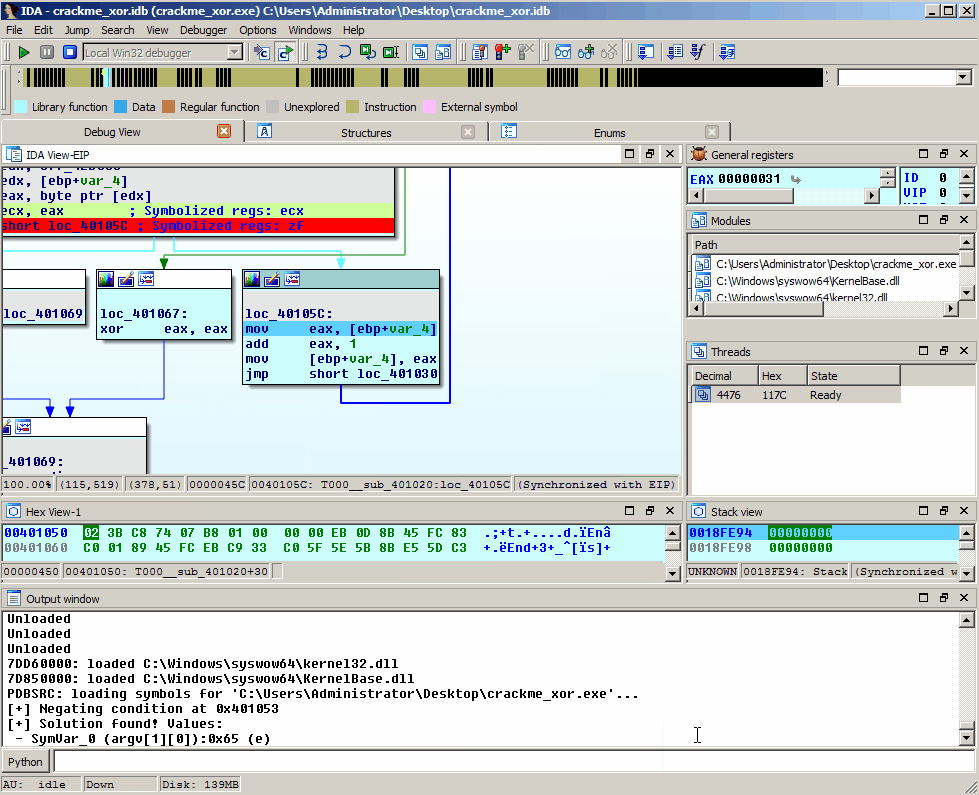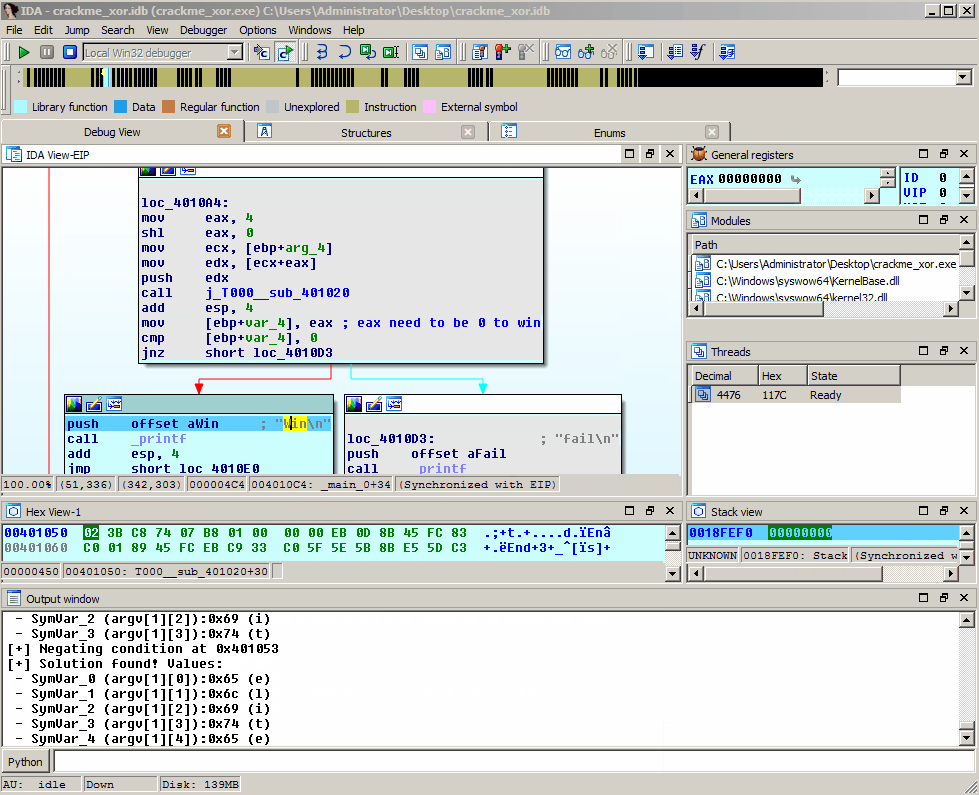
Reviewed illera88/Ponce@6858676
Binary · Tool:
CERT Polska’s automated black-box malware analysis system built on the DRAKVUF engine, which observes a Windows guest from the Xen hypervisor through virtual machine introspection rather than an agent installed in the guest.
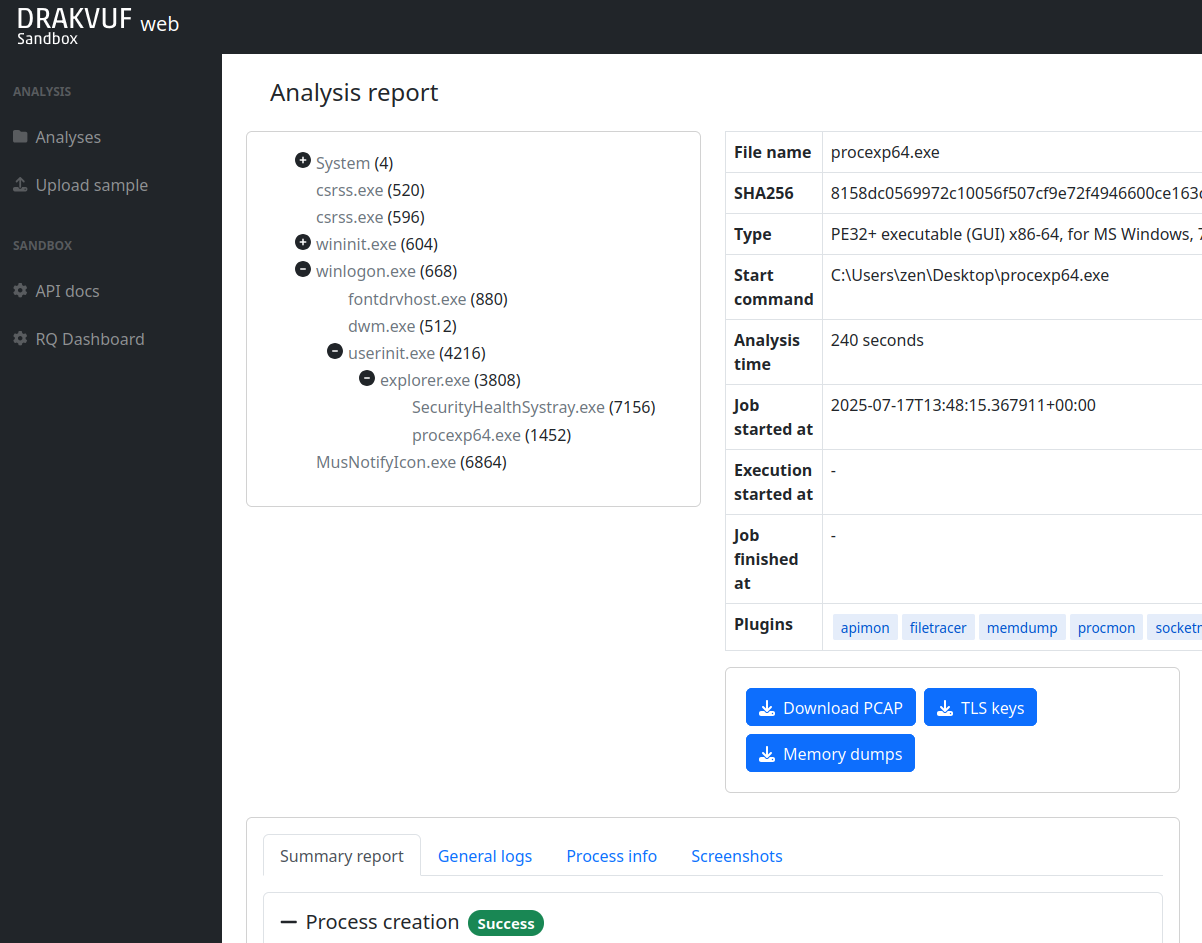
Reviewed CERT-Polska/drakvuf-sandbox@7c328ab
Binary · Tool:
IDAPython plugin for IDA Pro's Hex-Rays decompiler that helps rebuild structures and classes from pseudocode.
Reviewed igogo-x86/HexRaysPyTools@b8ebf75
Binary · Tool:
Malware sandbox derived from Cuckoo v1 that runs samples in isolated Windows guests and records API-hook behavior, created and modified files, network traffic as PCAP, screenshots and memory dumps.
Reviewed kevoreilly/CAPEv2@38c34af
Game · Tool:
Lua bytecode decompiler that turns compiled chunks back into Lua source, with a disassembly mode, selection of single nested functions by number and a guesser for local variable declarations that can be overridden by hand.
Reviewed viruscamp/luadec@895d923
App · Tool:
Frida-powered command-line tool that observes XPC messages exchanged between processes on iOS and macOS in both directions, for understanding how Apple-platform apps and services talk over XPC.
Reviewed ab-rizk/xpcspy@07c5a5b
Binary · Tool:
Python deobfuscation and analysis toolkit with a PySide6 GUI and a CLI mode, aimed at analysts examining obfuscated or packed Python programs.
Reviewed Fadi002/de4py@0f66191
App · Tool:
PyQt5 debugger built on Frida that attaches to or spawns processes on Android and iOS devices, the local machine or a remote Frida server.
Reviewed iGio90/Dwarf@fd859ae
Binary · Tool:
Bitdefender’s dependency-free C decoder for x86/x64 instructions, reporting explicit and implicit operands with their access modes, CPUID feature flags, flag accesses and valid modes, and printing Intel/MASM-style text.
Reviewed bitdefender/bddisasm@f0c0e90
Binary · Tool:
Reworking of uncompyle6 by the same author that translates Python 3.7 and 3.8 bytecode, including some PyPy 3.7 and 3.8 bytecode, back into equivalent Python source; older bytecode stays with uncompyle6.
Reviewed rocky/python-decompile3@0b97289
Binary · Tool:
Tamas K Lengyel's virtualization-based, agentless black-box binary analysis system: running on the Xen hypervisor through LibVMI, it traces execution in Windows and Linux guests, from kernel functions to user-mode code, without installing software inside the analyzed virtual machine.
Reviewed tklengyel/drakvuf@b2f64d8
Binary · Tool:
VBA parser and emulation engine, created by Philippe Lagadec and developed since 2017 mainly by Kirk Sayre and other contributors, for analyzing and deobfuscating malicious macros in Microsoft Office files such as Word, Excel, PowerPoint and Publisher documents, as well as VBScript files and HTA files carrying VBScript.
Reviewed decalage2/ViperMonkey@73547ce
Firmware · Tool:
Injectable real-mode x86 debugger for legacy BIOS code, boot code and DOS programs on real hardware or in a virtual machine.
Reviewed Theldus/bread@700807e
Binary · Tool:
Function-level lifter that symbolically lifts one x86-64 function from a Windows PE binary into LLVM IR, then iterates LLVM and custom passes to a fixpoint so obfuscated or virtualized code reduces to simpler control flow and semantics for analysis.
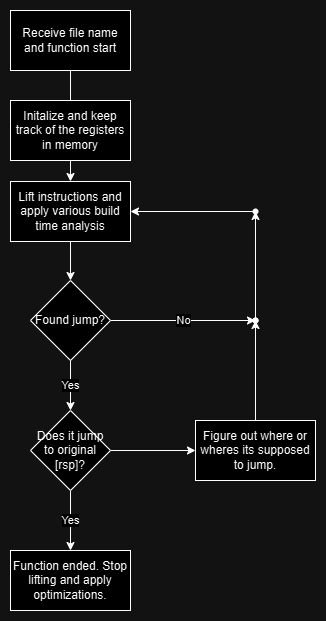
Reviewed NaC-L/Mergen@1998057
Binary · Tool:
Command-line toolkit, formerly named pev, for analyzing 32- and 64-bit Windows PE files.
Reviewed mentebinaria/readpe@967ab57
Website · Tool:
Node.js sandbox for semi-automatic analysis of JavaScript malware: it runs a sample in Node's vm module against emulated Windows Script Host and ActiveX objects such as WScript.Shell, MSXML2.XMLHTTP, ADODB.Stream, Scripting.FileSystemObject and WMI, plus a partial browser context with selectable browser profiles.
Reviewed HynekPetrak/malware-jail@ec370f1
App · Tool:
macOS command-line XPC sniffer, inspired by xpcspy, that injects a Frida agent into an attached or newly spawned process and logs the XPC messages it sends and receives, labelled with the libxpc function, connection name, peer PID and process name.
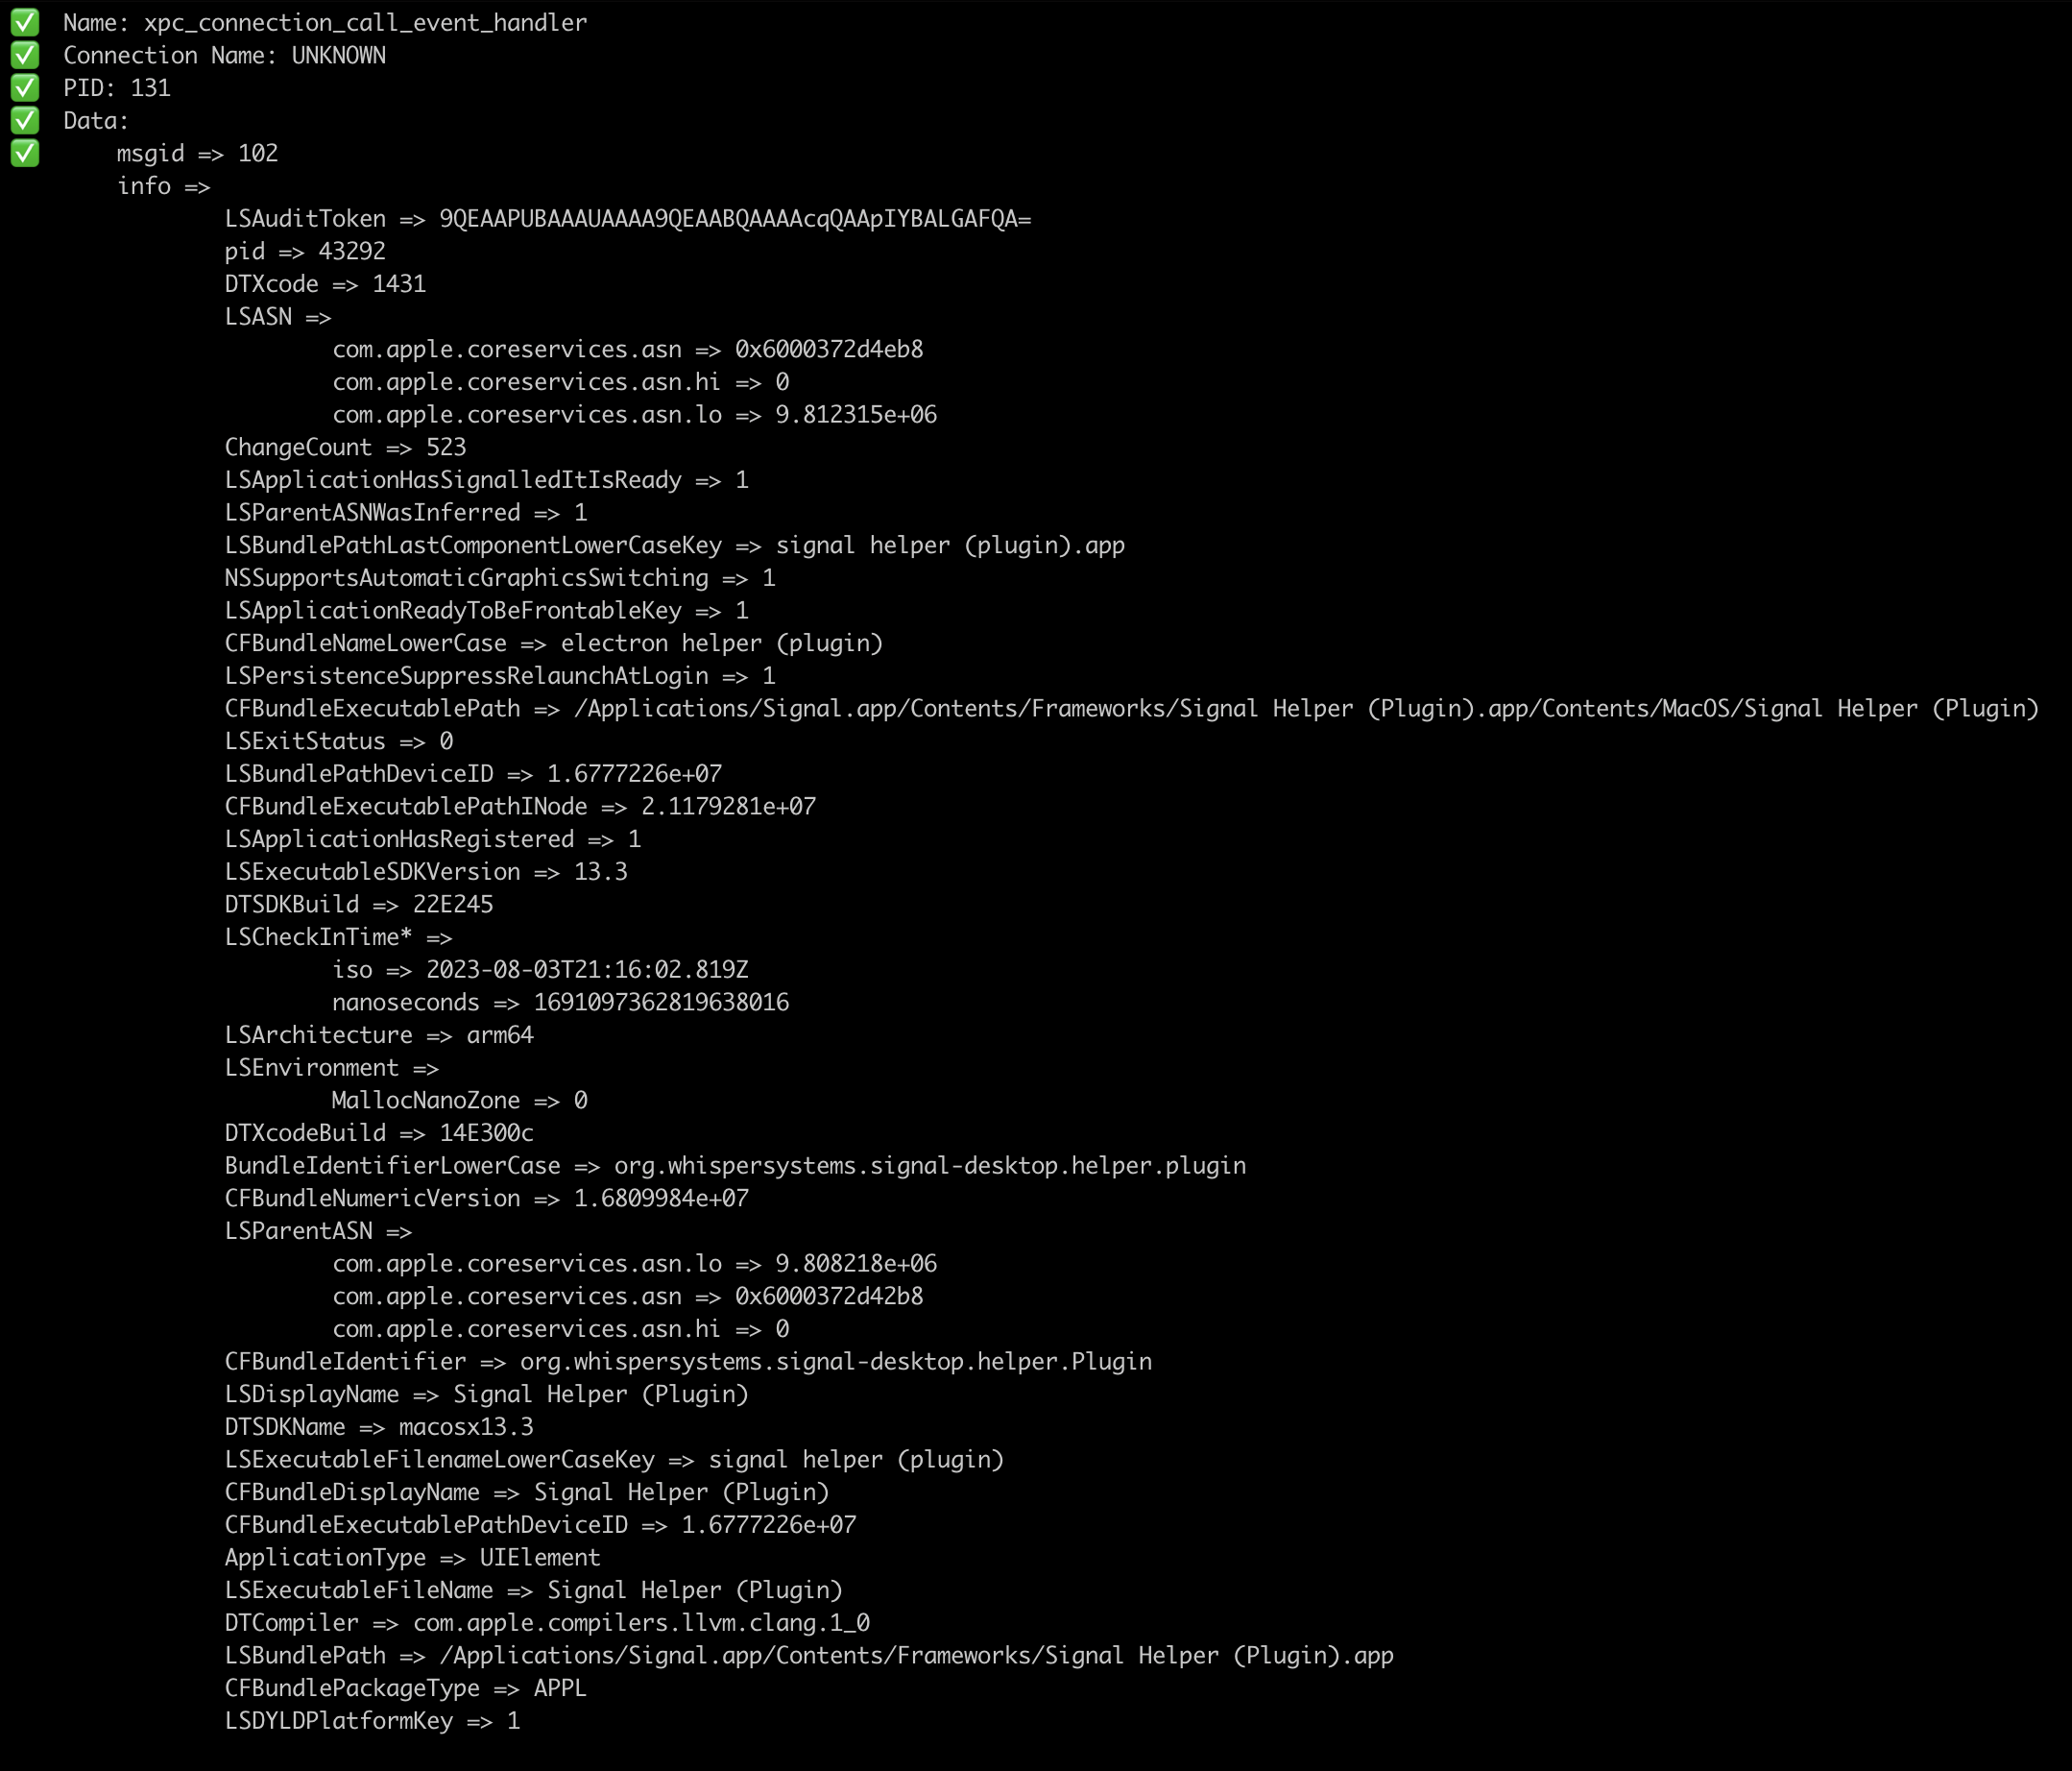
Reviewed ReverseApple/gxpc@4fad36d
Binary · Tool:
Trail of Bits' now-archived symbolic execution tool for Linux ELF binaries on x86, x86-64, AArch64 and ARMv7, Ethereum smart contracts as EVM bytecode, and WebAssembly modules.
Reviewed trailofbits/manticore@cdf6c4b
Binary · Tool:
Thomas Roth's (Ghidra Ninja) collection of Ghidra Python scripts, which appear under a Ghidra Ninja category in the Script Manager.
Reviewed ghidraninja/ghidra_scripts@99f2a86
Binary · Tool:
Ghidra script that ports Ilfak Guilfanov's FindCrypt plugin for IDA, searching a program's memory or the current selection for constants of cryptographic and compression algorithms.
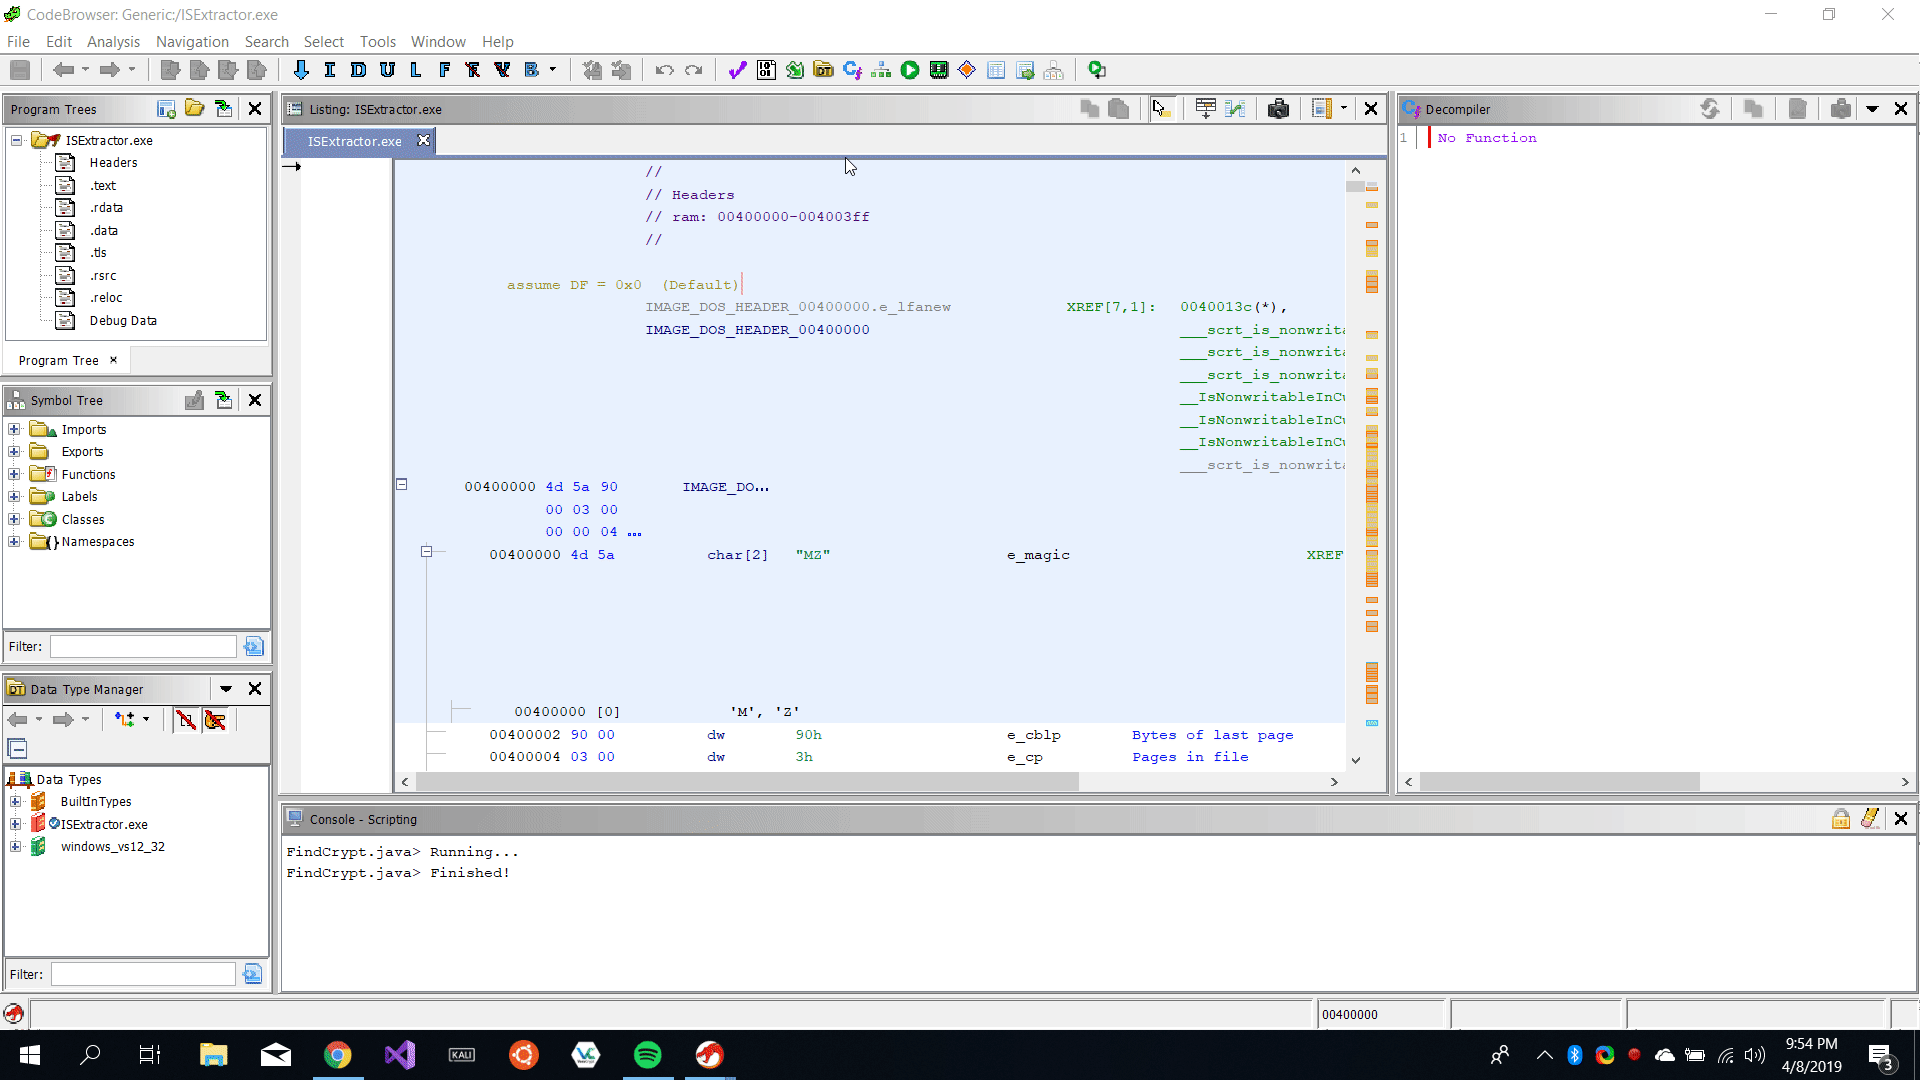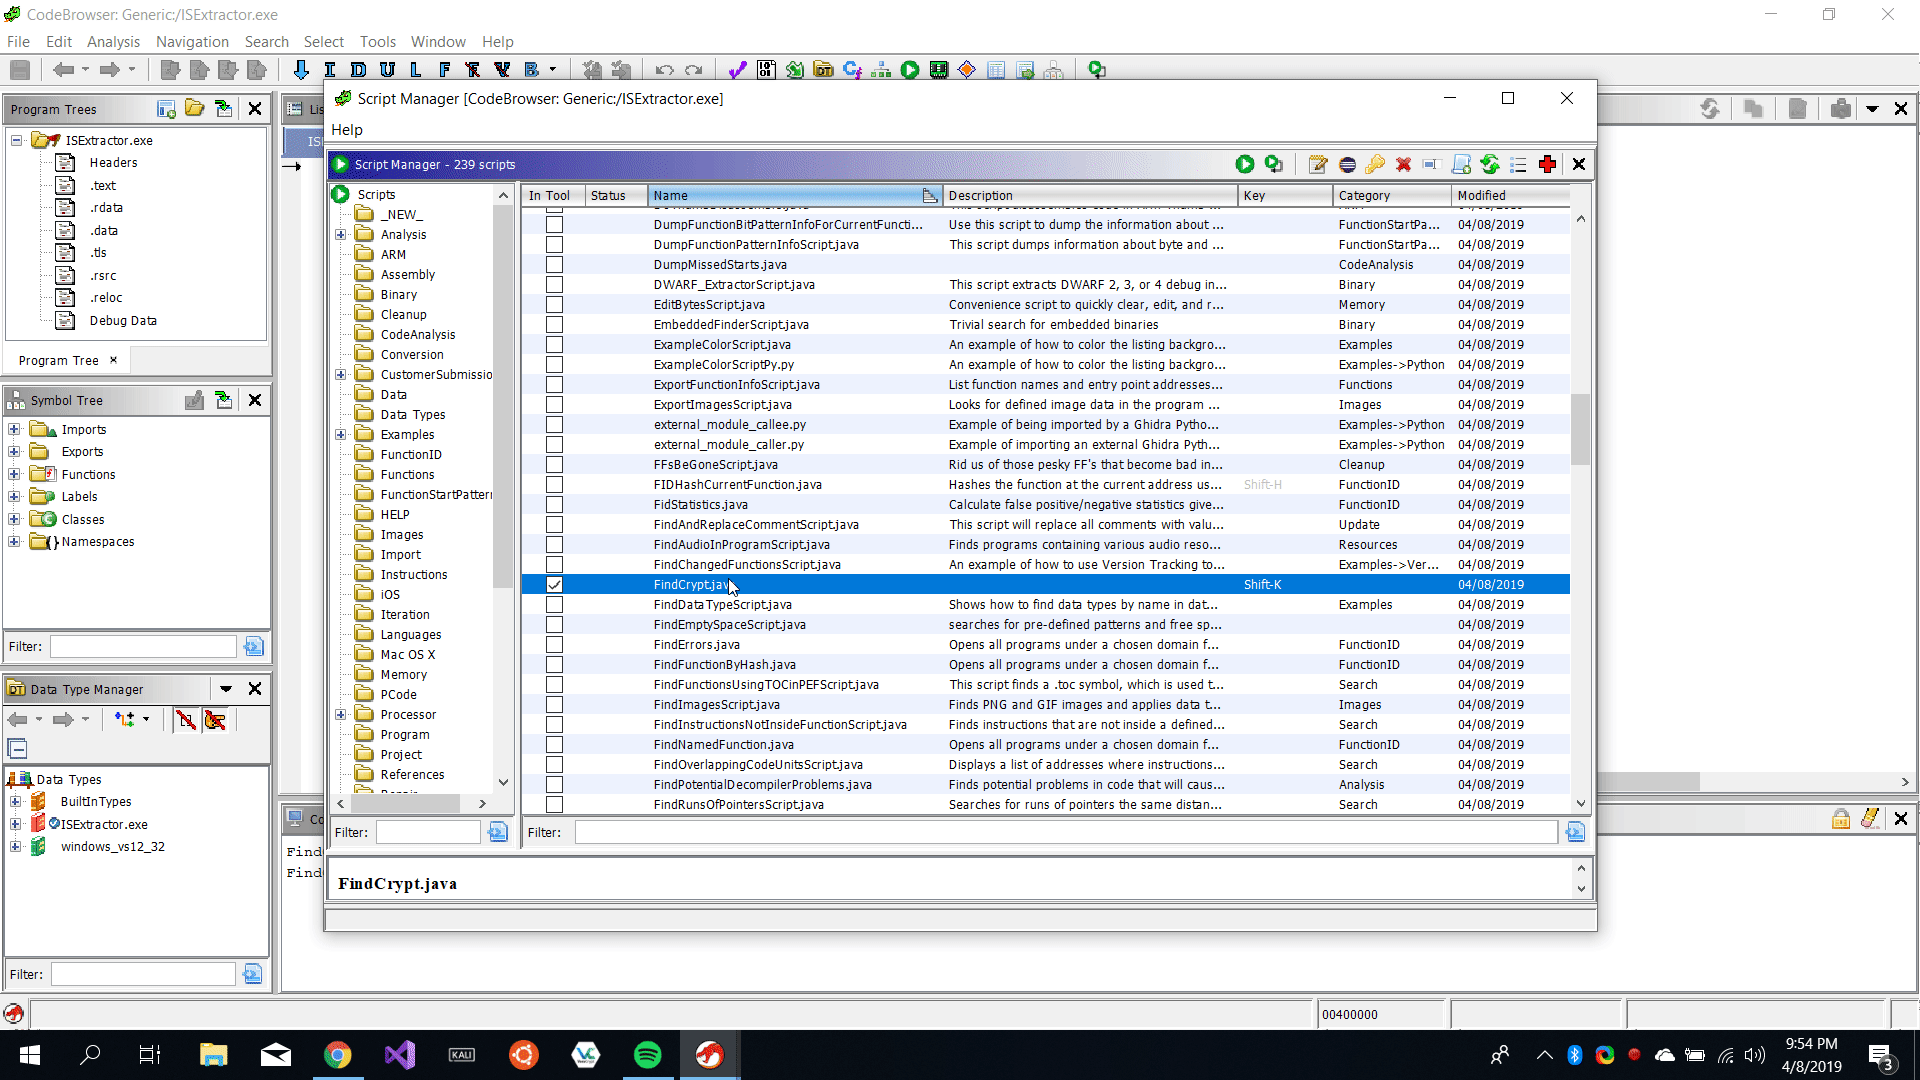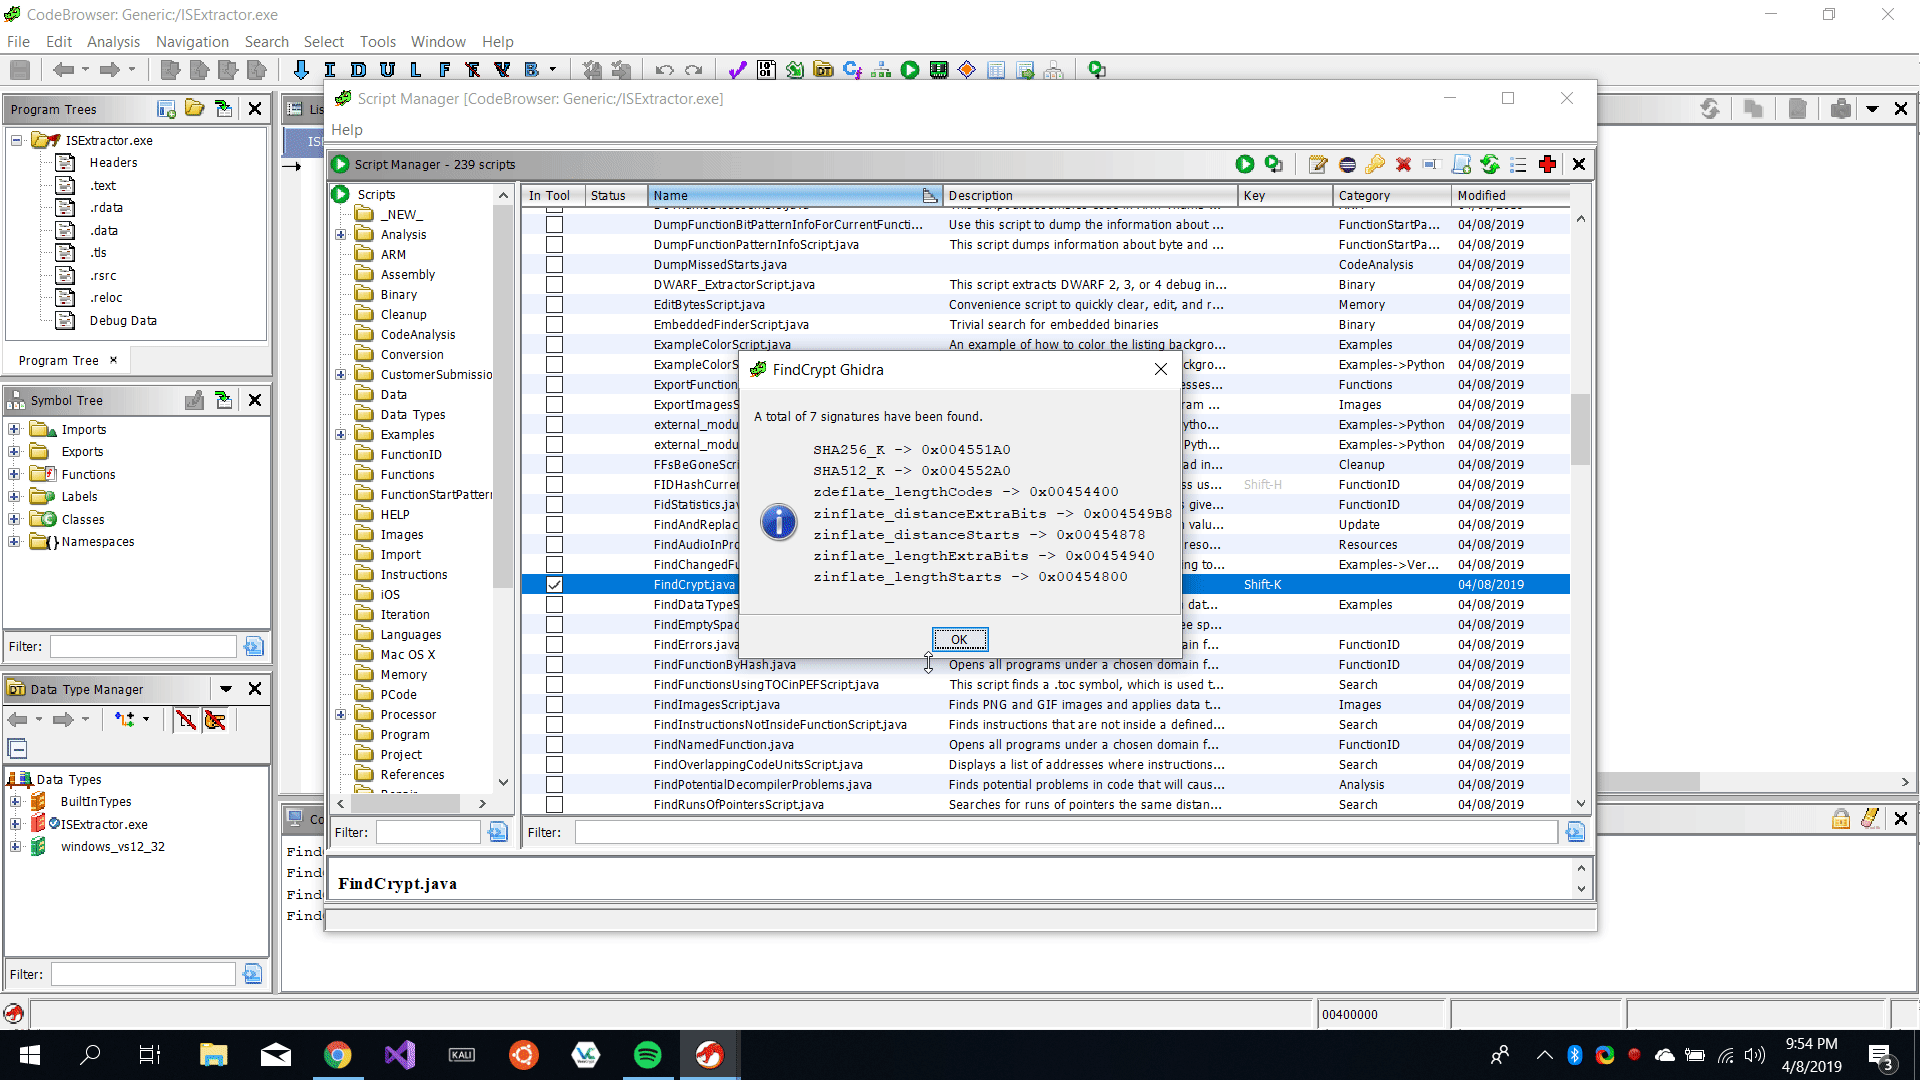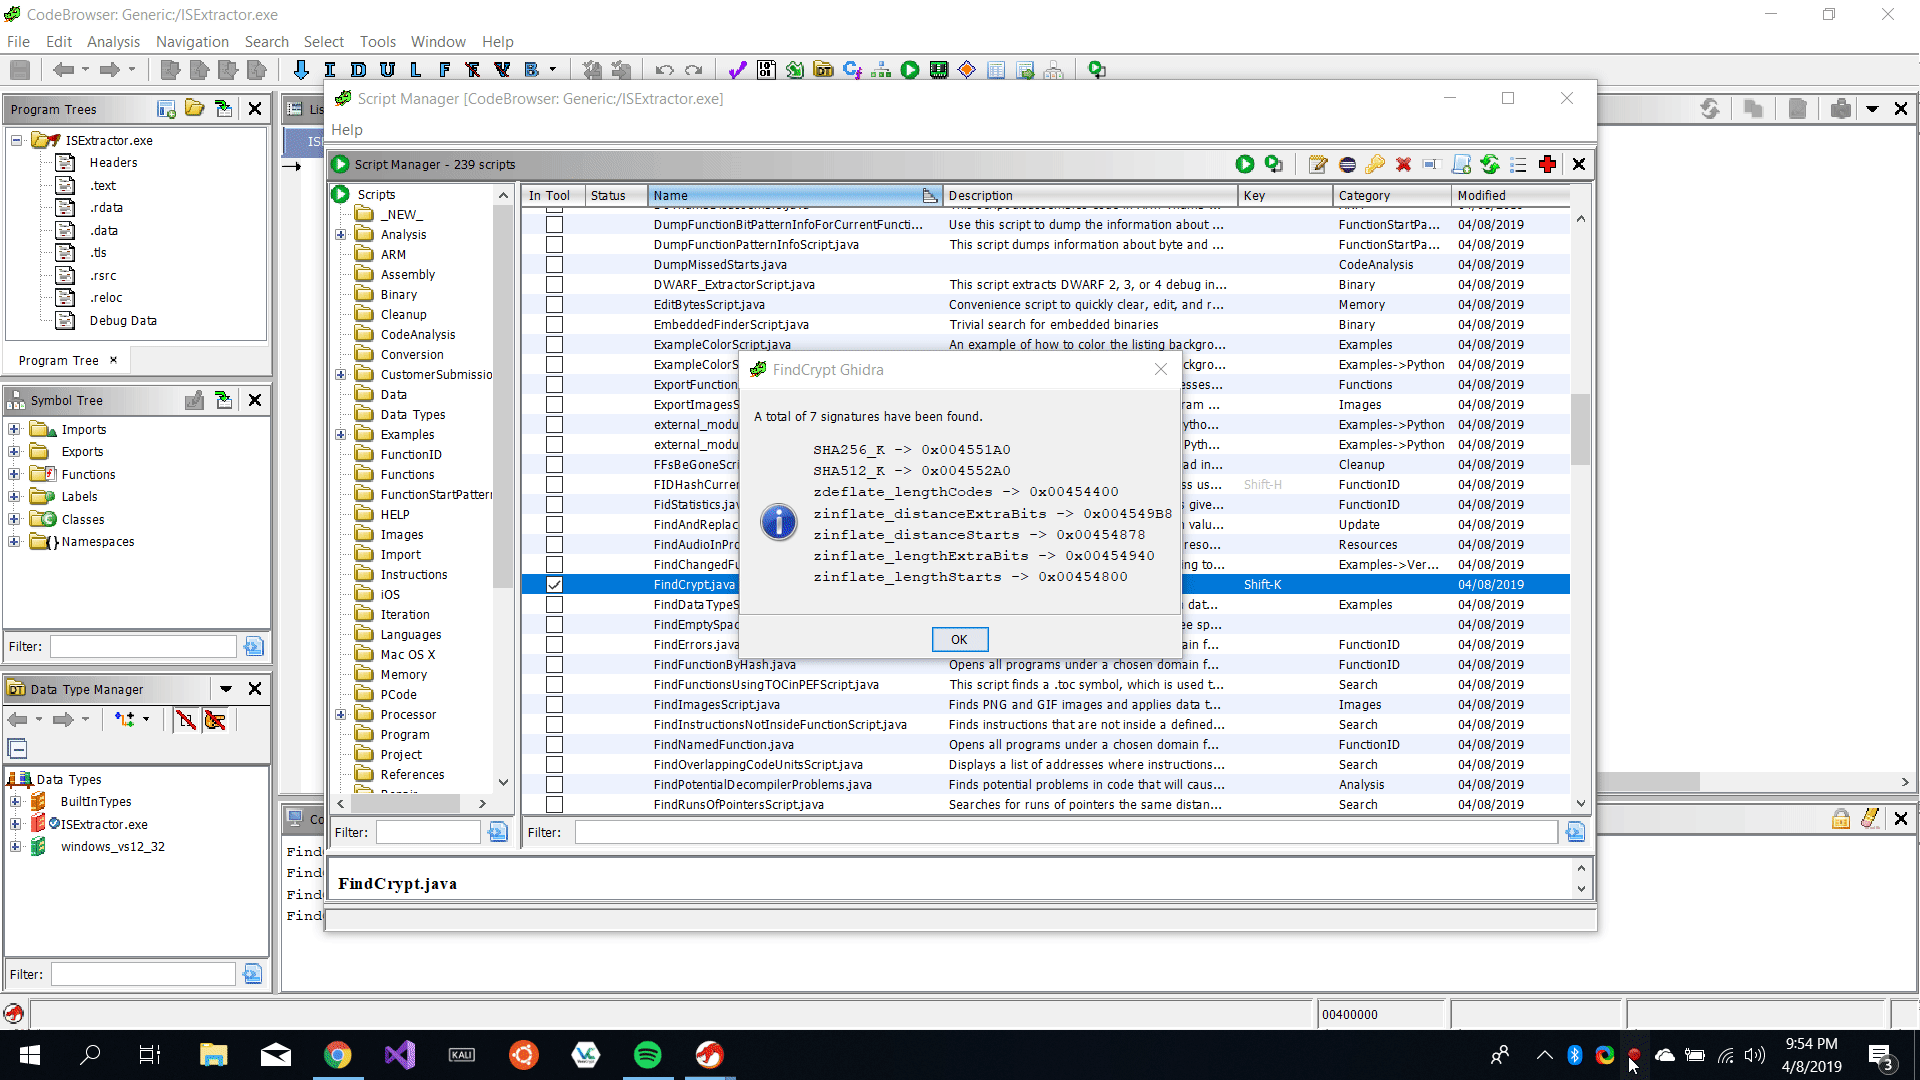
Reviewed d3v1l401/FindCrypt-Ghidra@71660fd
Binary · Tool:
Large collection of composable Python command-line units for transforming binary data: encodings, compression, encryption, archive and executable-format extraction, carving and pattern search.
Reviewed binref/refinery@13d8c68
Binary · Tool:
Ghidra extension that runs angr symbolic execution from a CodeBrowser panel.
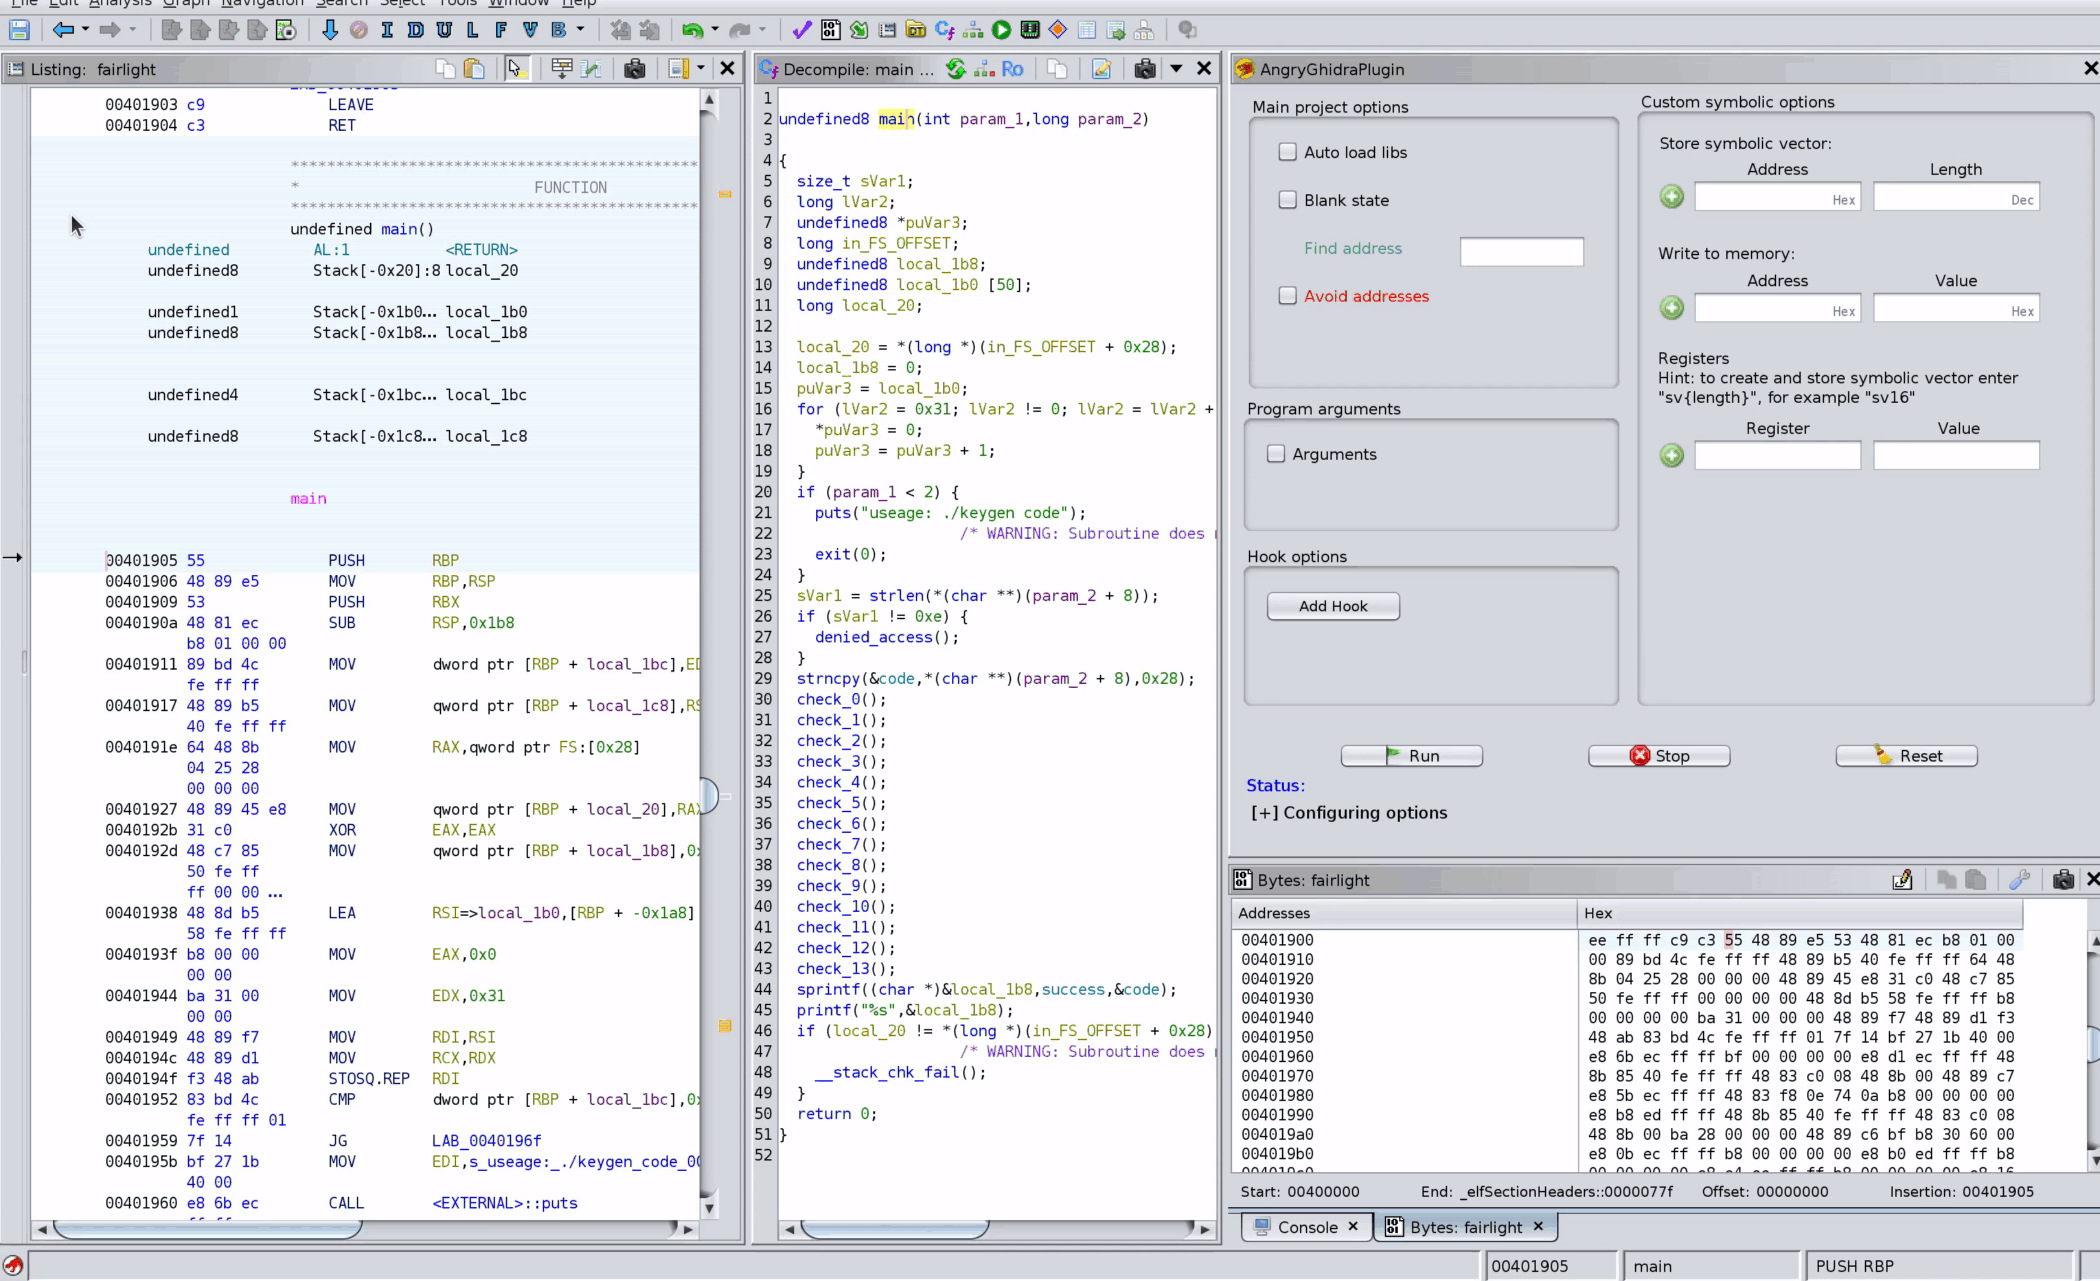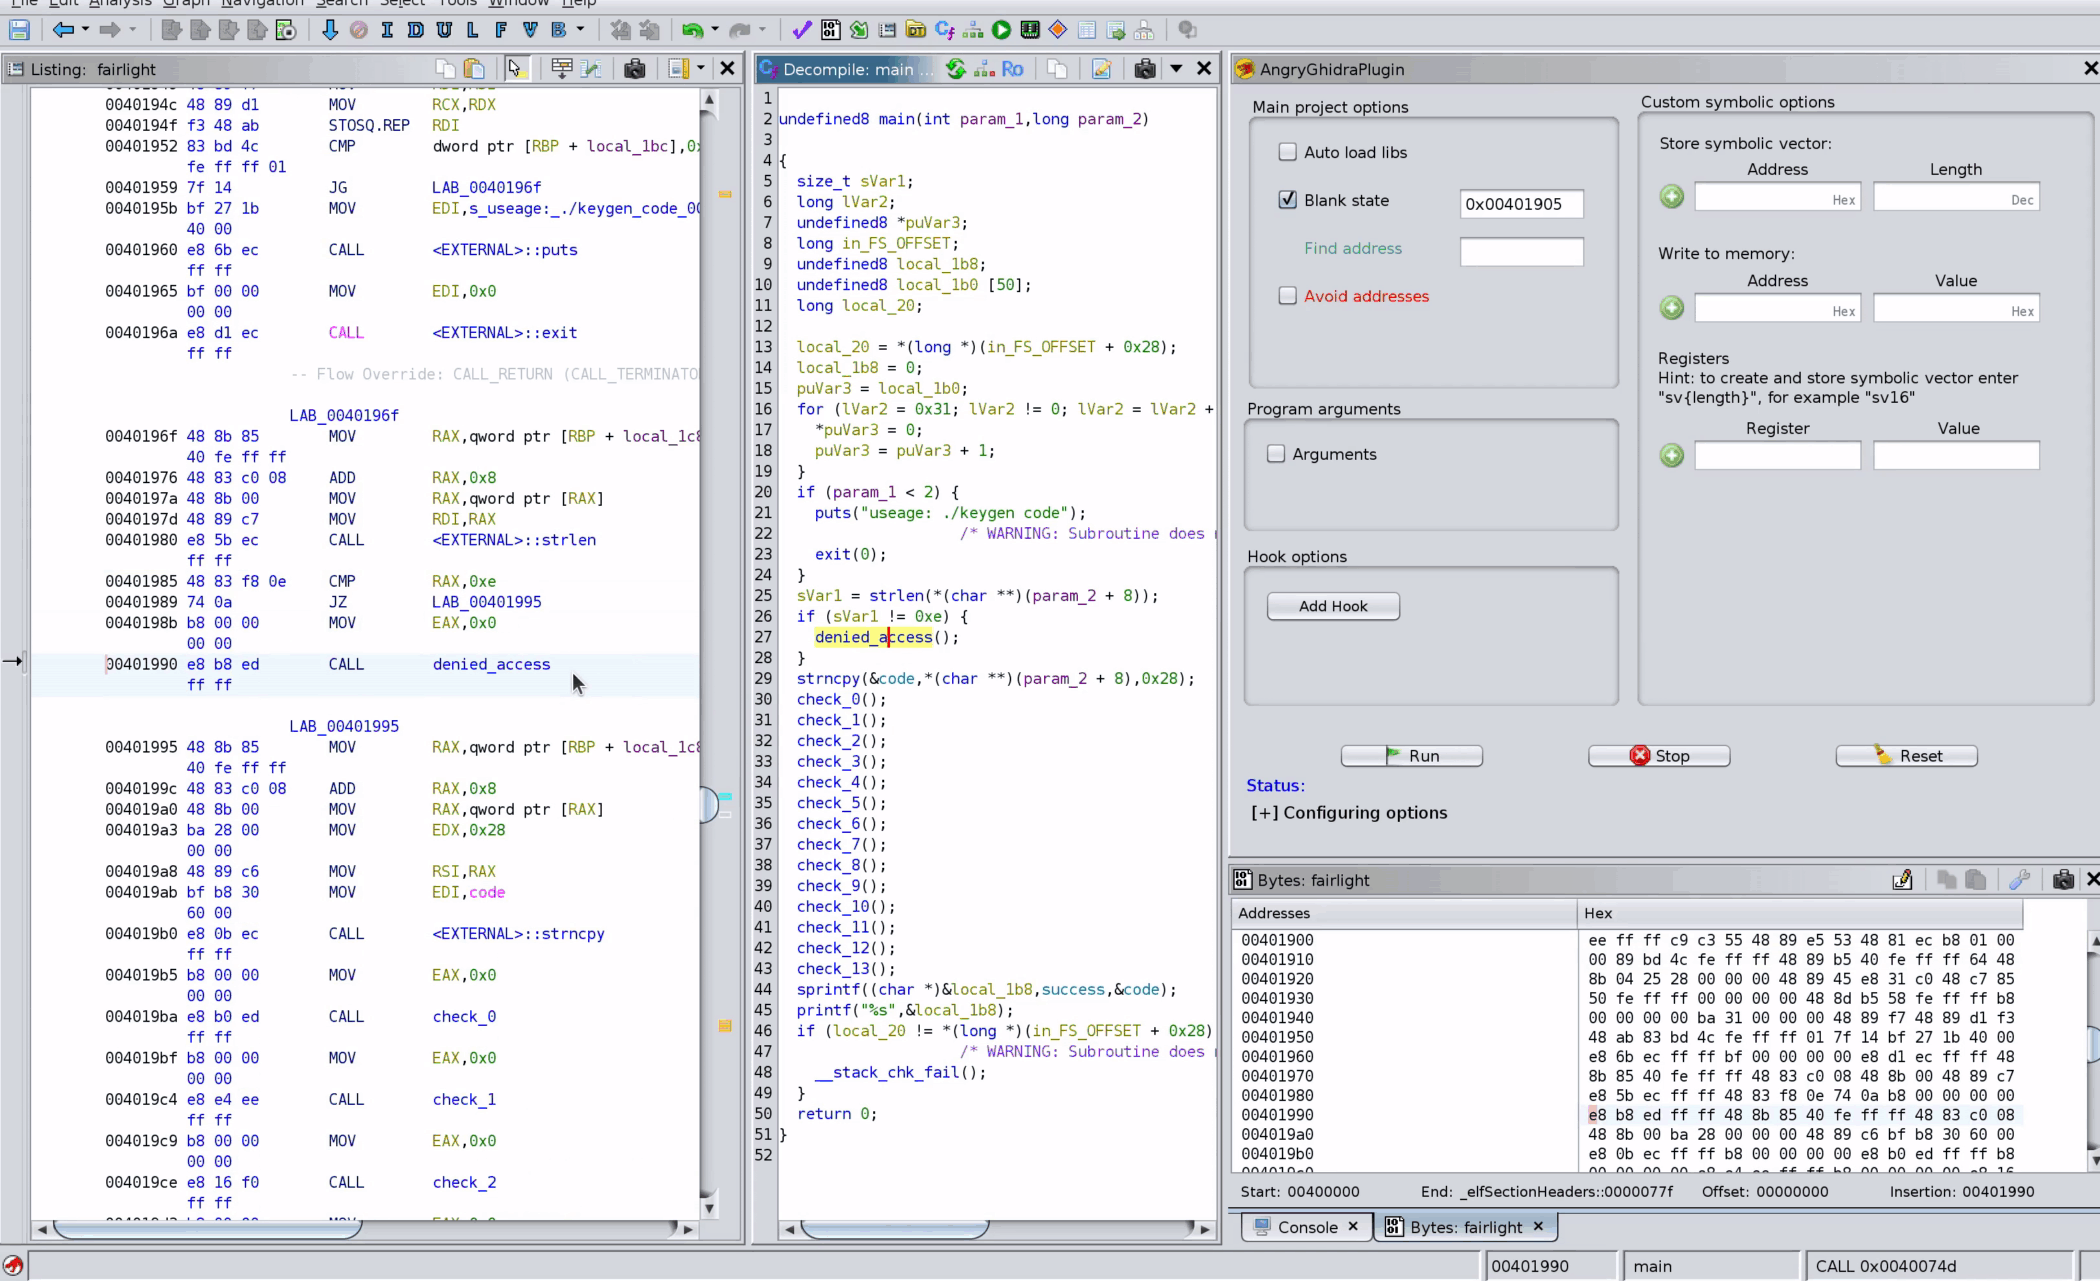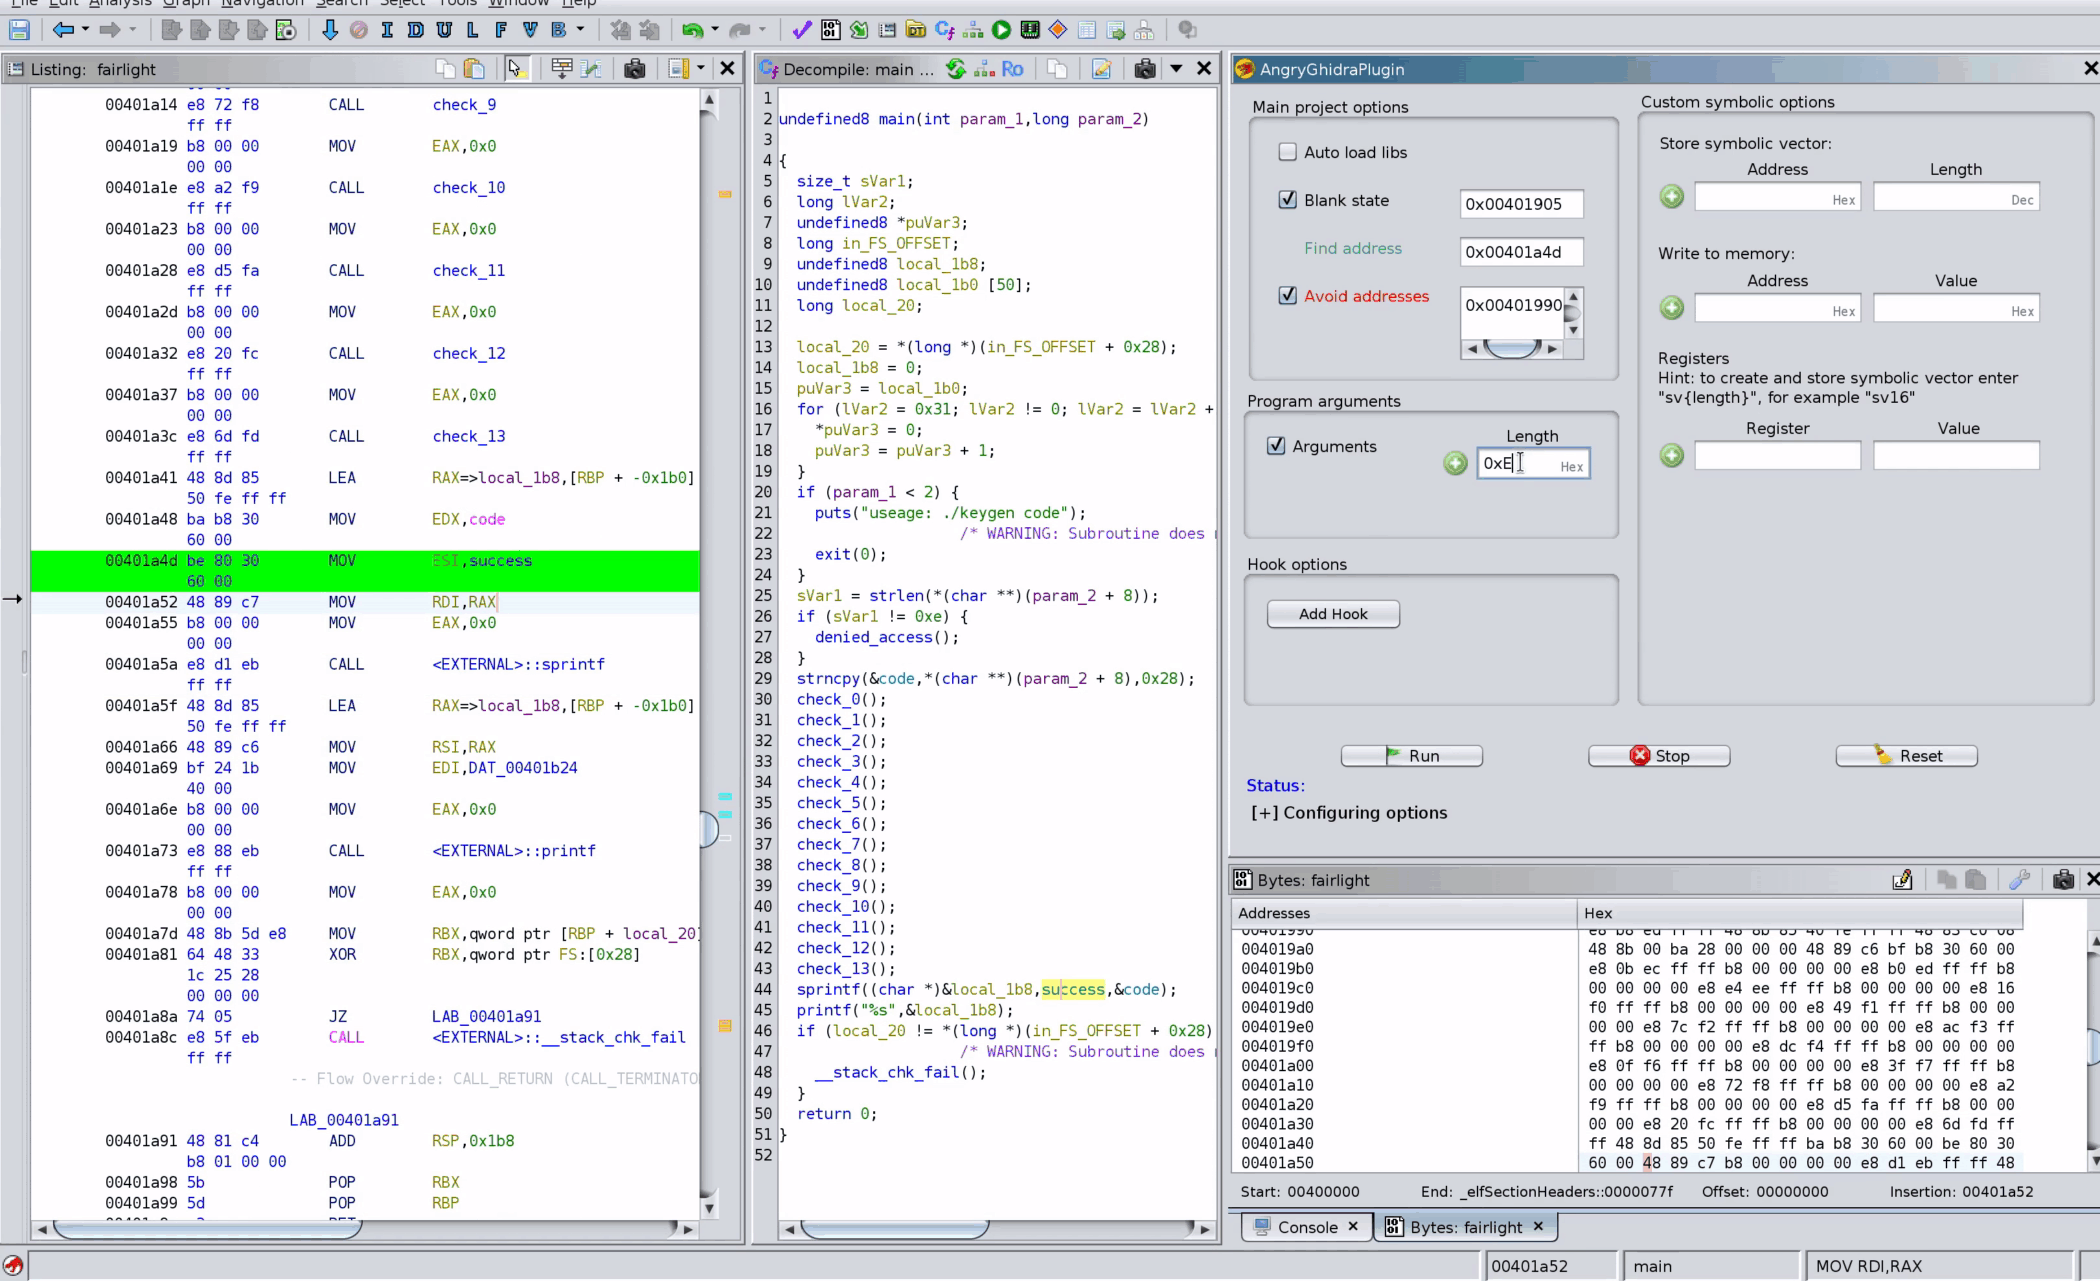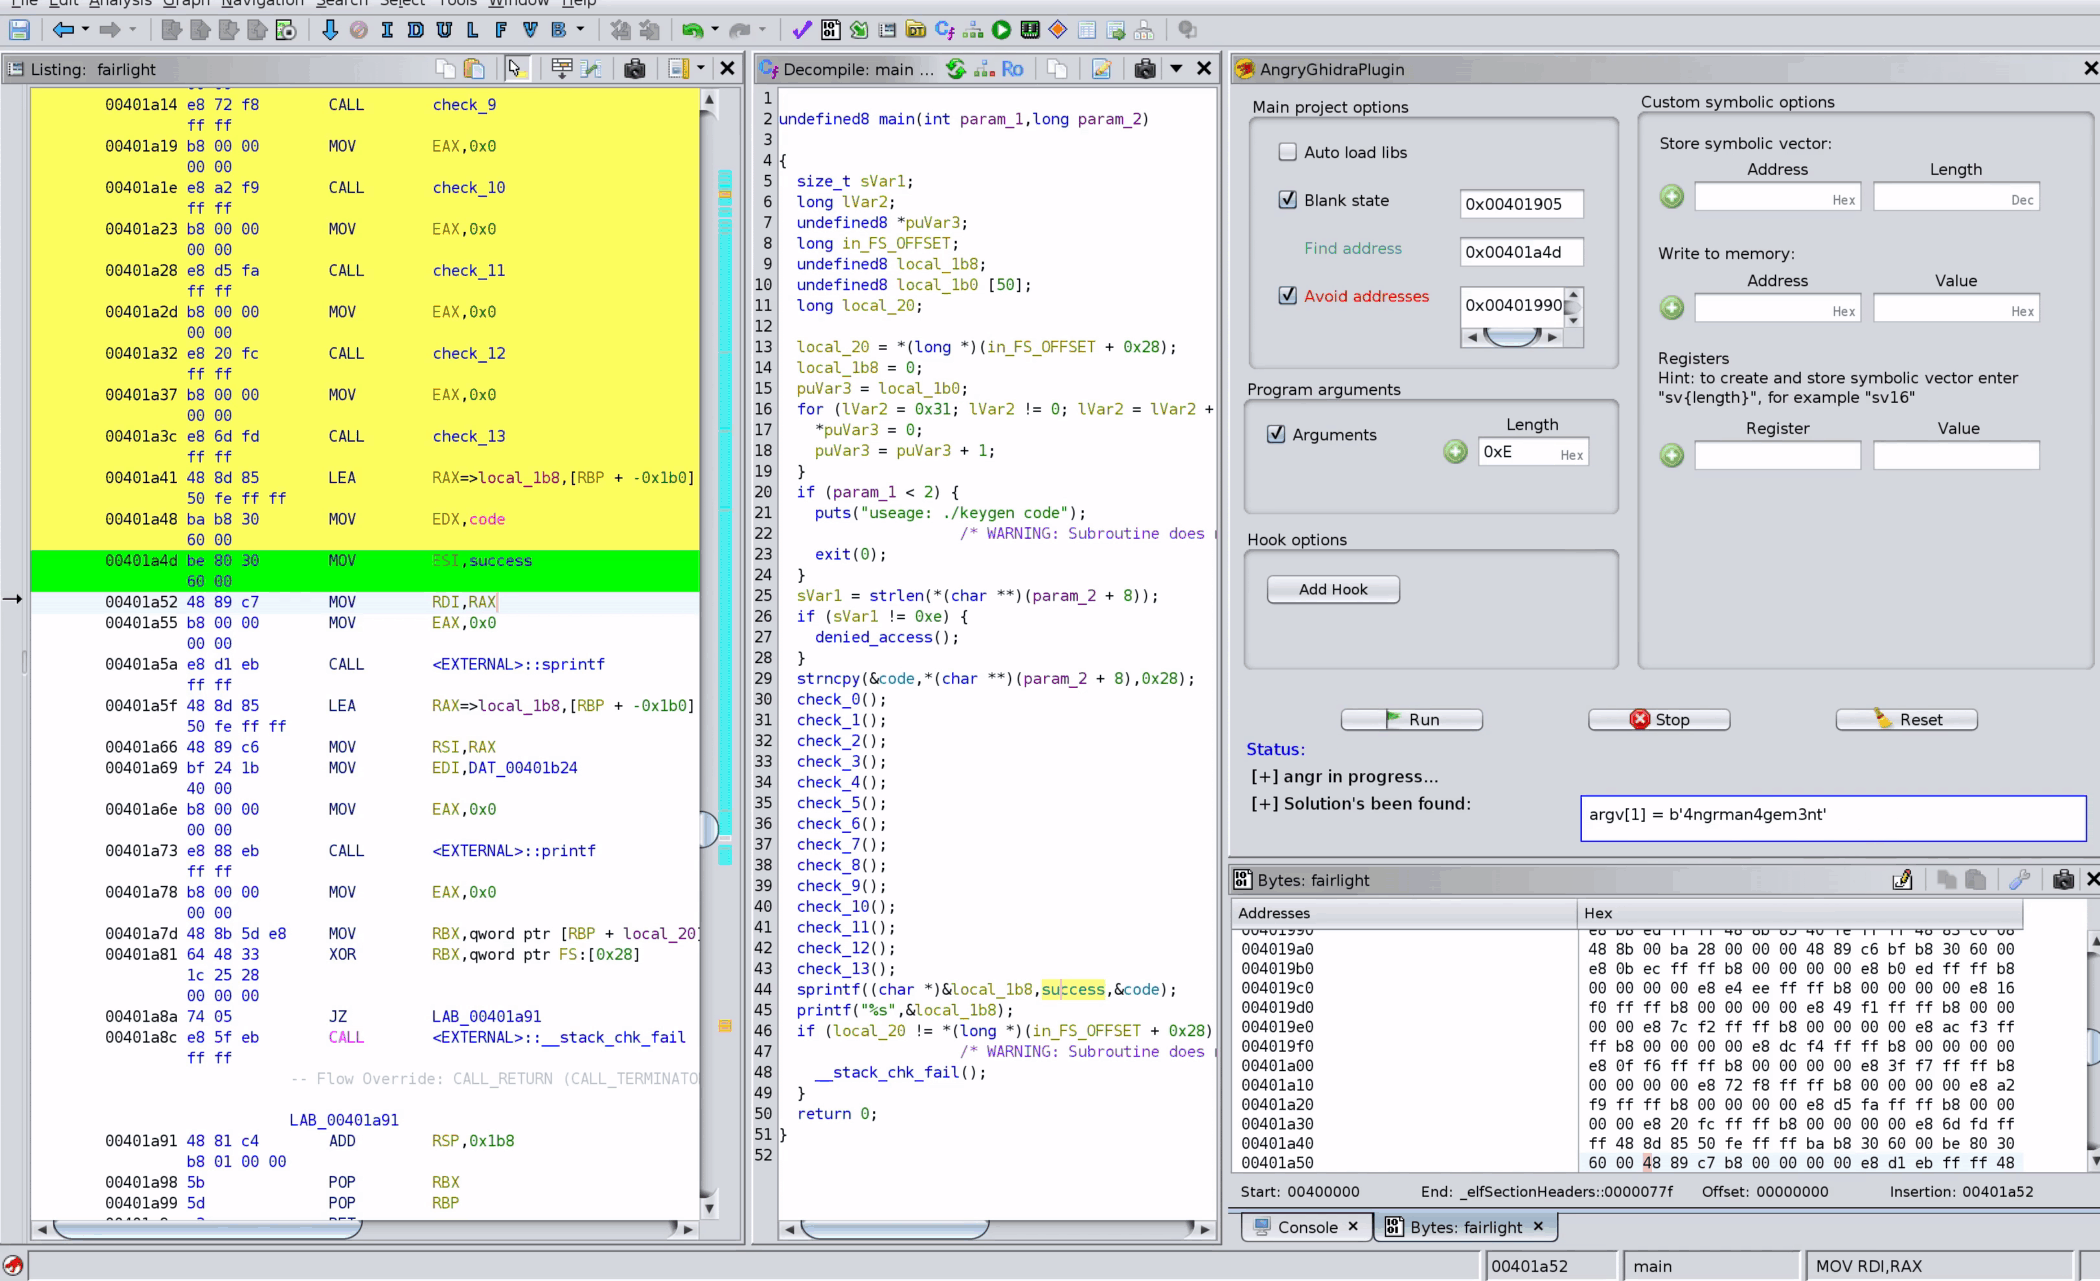
Reviewed Nalen98/AngryGhidra@0e6dc9c
Binary · Tool:
Frida-based fuzzing suite for closed-source programs, listed here for its in-process instrumentation and coverage layer.
Reviewed ttdennis/fpicker@04f4b06
Binary · Tool:
HexHive's static binary rewriter for x64 and aarch64 Linux ELF binaries, which turns a binary into symbolized, reassemblable assembly so instrumentation can be inserted without source code and without heuristics.
Reviewed HexHive/retrowrite@3b1e366
App · Tool:
Frida library, taken from the Dexcalibur project, that uses Frida’s Stalker to trace a process’s system calls and print strace-like lines with the calling thread, module and offset, decoded flag values and file paths resolved from descriptors.
Reviewed FrenchYeti/interruptor@6faa9f6
App · Tool:
macOS application and command-line tool that reads a dyld_shared_cache file from macOS or iOS, shows its header, mappings and image list, and copies one library or every library out to a directory.
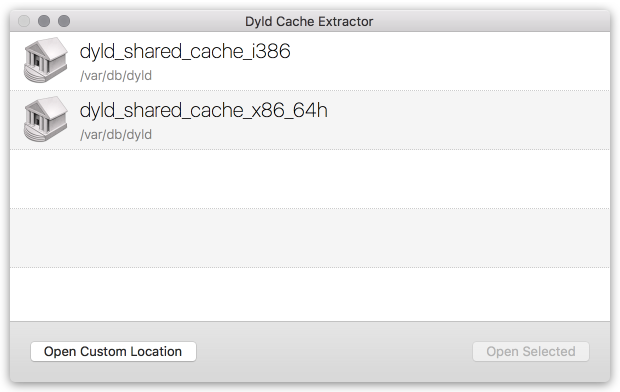
Reviewed macmade/dyld_cache_extract@b29fbb9
Binary · Tool:
Archived collection of IDAPython plugins and scripts from Mandiant's FLARE team for malware and native-code analysis in IDA Pro.
Reviewed mandiant/flare-ida@fc667de
Binary · Tool:
Binary trait-lexer framework that extracts instructions, basic blocks and functions from executables and emits searchable JSON traits for similarity, hunting and signature work.
Reviewed c3rb3ru5d3d53c/binlex@f02f270
Binary · Tool:
IDA Pro Python plugin for triaging Windows kernel drivers, building on NCC Group's original DriverBuddy.
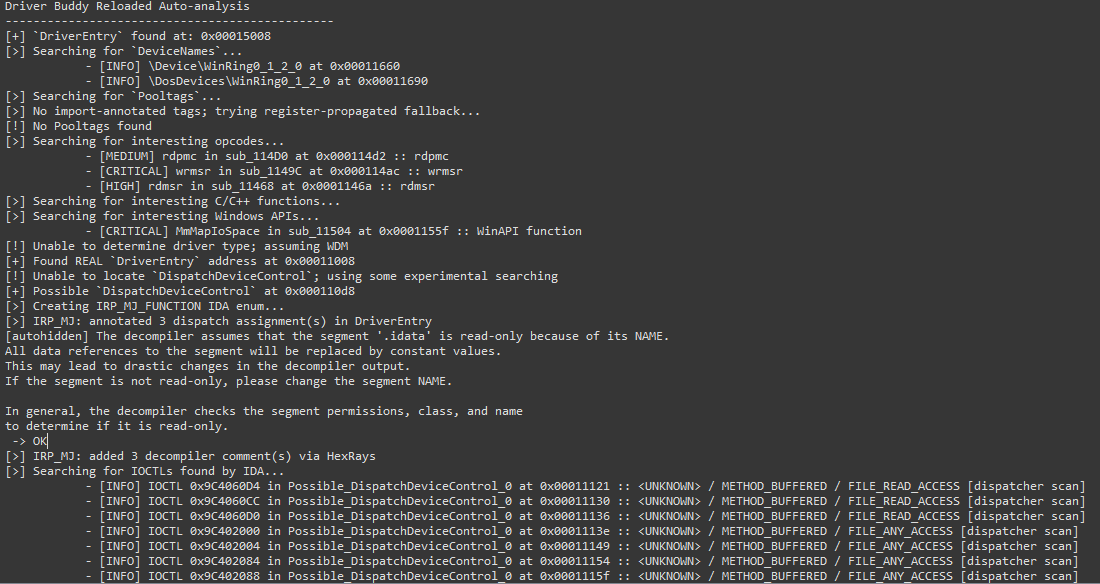
Reviewed VoidSec/DriverBuddyReloaded@72bf7c8
Binary · Tool:
Python framework, mainly used as an IDA plugin, that turns the manual steps of locating symbols, such as finding a string, following its cross-reference and taking the function start, into reusable signatures.
Reviewed doronz88/fa@b584a37
Binary · Tool:
Fork of PyInstaller Extractor (pyinstxtractor) by the same author that extracts the bundled CArchive files and PYZ modules from Linux ELF and Windows PE executables built with PyInstaller, writing .pyc files with repaired headers for a separate bytecode decompiler.
Binary · Tool:
Trail of Bits' C++23 simplifier for Mixed Boolean-Arithmetic (MBA) expressions, an obfuscation technique that rewrites simple computations as interleaved arithmetic, bitwise and shift operations.
Reviewed trailofbits/CoBRA@af44b8a
Binary · Tool:
Python command-line deobfuscator for the control-flow flattening applied by Obfuscator-LLVM (OLLVM).
Reviewed cdong1012/ollvm-unflattener@d006201
Binary · Tool:
Ghidra extension whose Golang Analyzer reads the runtime header and module data in Go binaries built with go1.6 through go1.27 to identify the Go version, rename functions, correct their arguments, comment source files and line numbers, add Go types to the Data Type Manager and label Go strings.
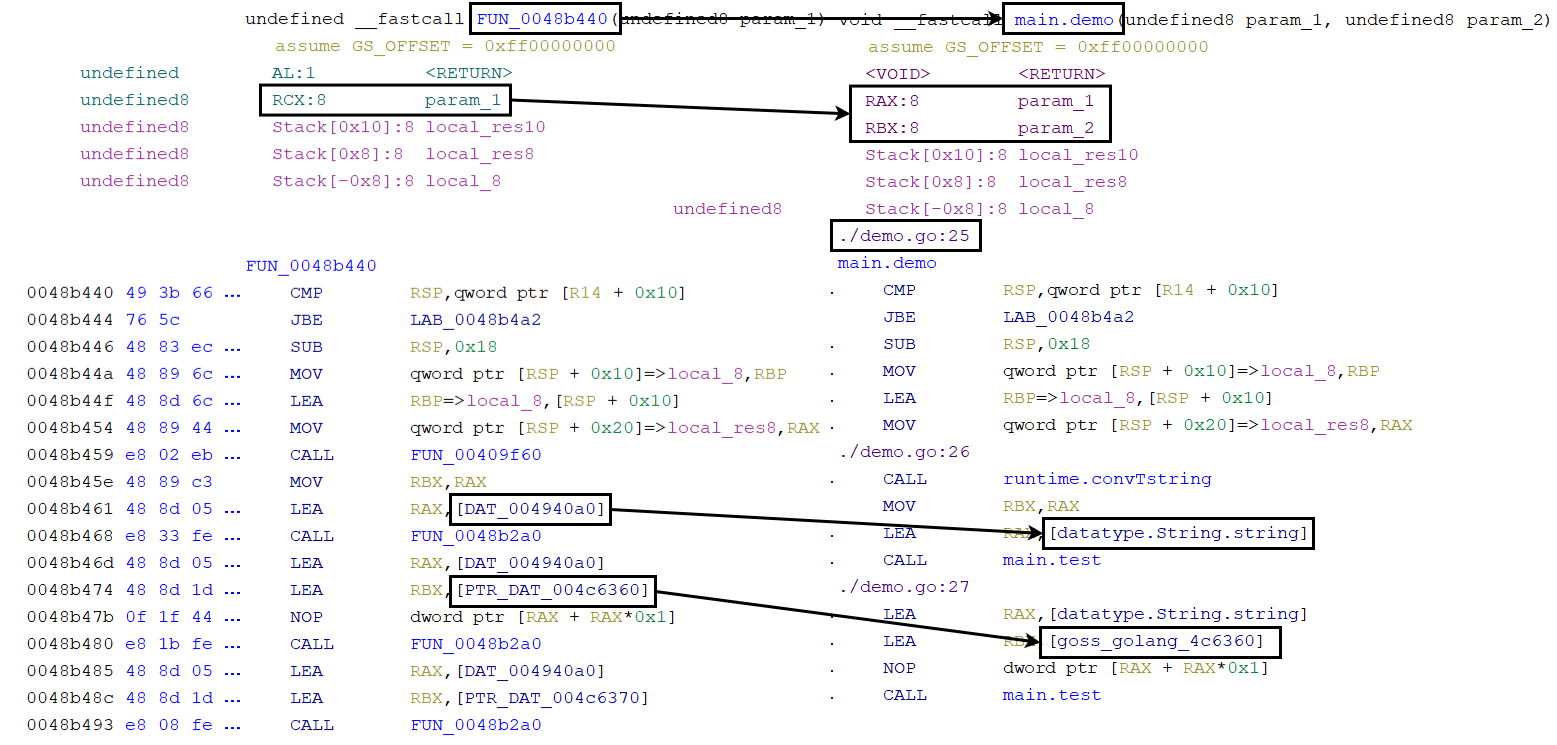
Reviewed mooncat-greenpy/Ghidra_GolangAnalyzerExtension@c0d1540
App · Tool:
IDA Pro plugin that cleans up Hex-Rays pseudocode and adds navigation helpers for iOS user-mode binaries and the kernelcache, enabling its components according to the loaded file.
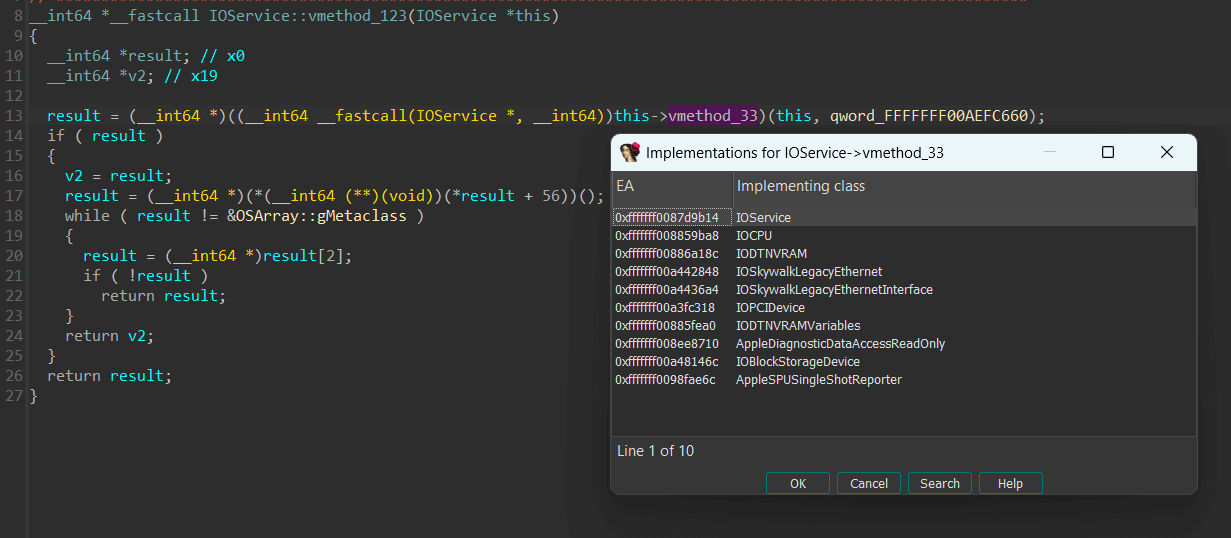
Reviewed yoavst/ida-ios-helper@65c7b03
Binary · Tool:
Dynamic binary modification framework from the University of Manchester that runs unmodified Linux user-space programs on 32-bit Arm (A32/T32), AArch64 and RV64GC RISC-V, translating their code into a code cache as it executes.
Reviewed beehive-lab/mambo@dcdf19a
Binary · Tool:
IDA Pro plugin that scans Microsoft Visual C++ binaries for virtual function tables (vftables) through their C++ run-time type information (RTTI), names, labels and comments the vftables it finds, defines the RTTI data structures and identifies single, multiple and virtual inheritance in each class hierarchy.
Binary · Tool:
Server platform from McGill University's Data Mining and Security Lab that indexes collections of disassembled binaries into shared repositories and searches them for cloned assembly functions.
Reviewed McGill-DMaS/Kam1n0-Community@1c3c309
App · Tool:
Toolkit for analyzing iOS apps and arm64 Mach-O binaries, built on Capstone, Unicorn and Keystone.
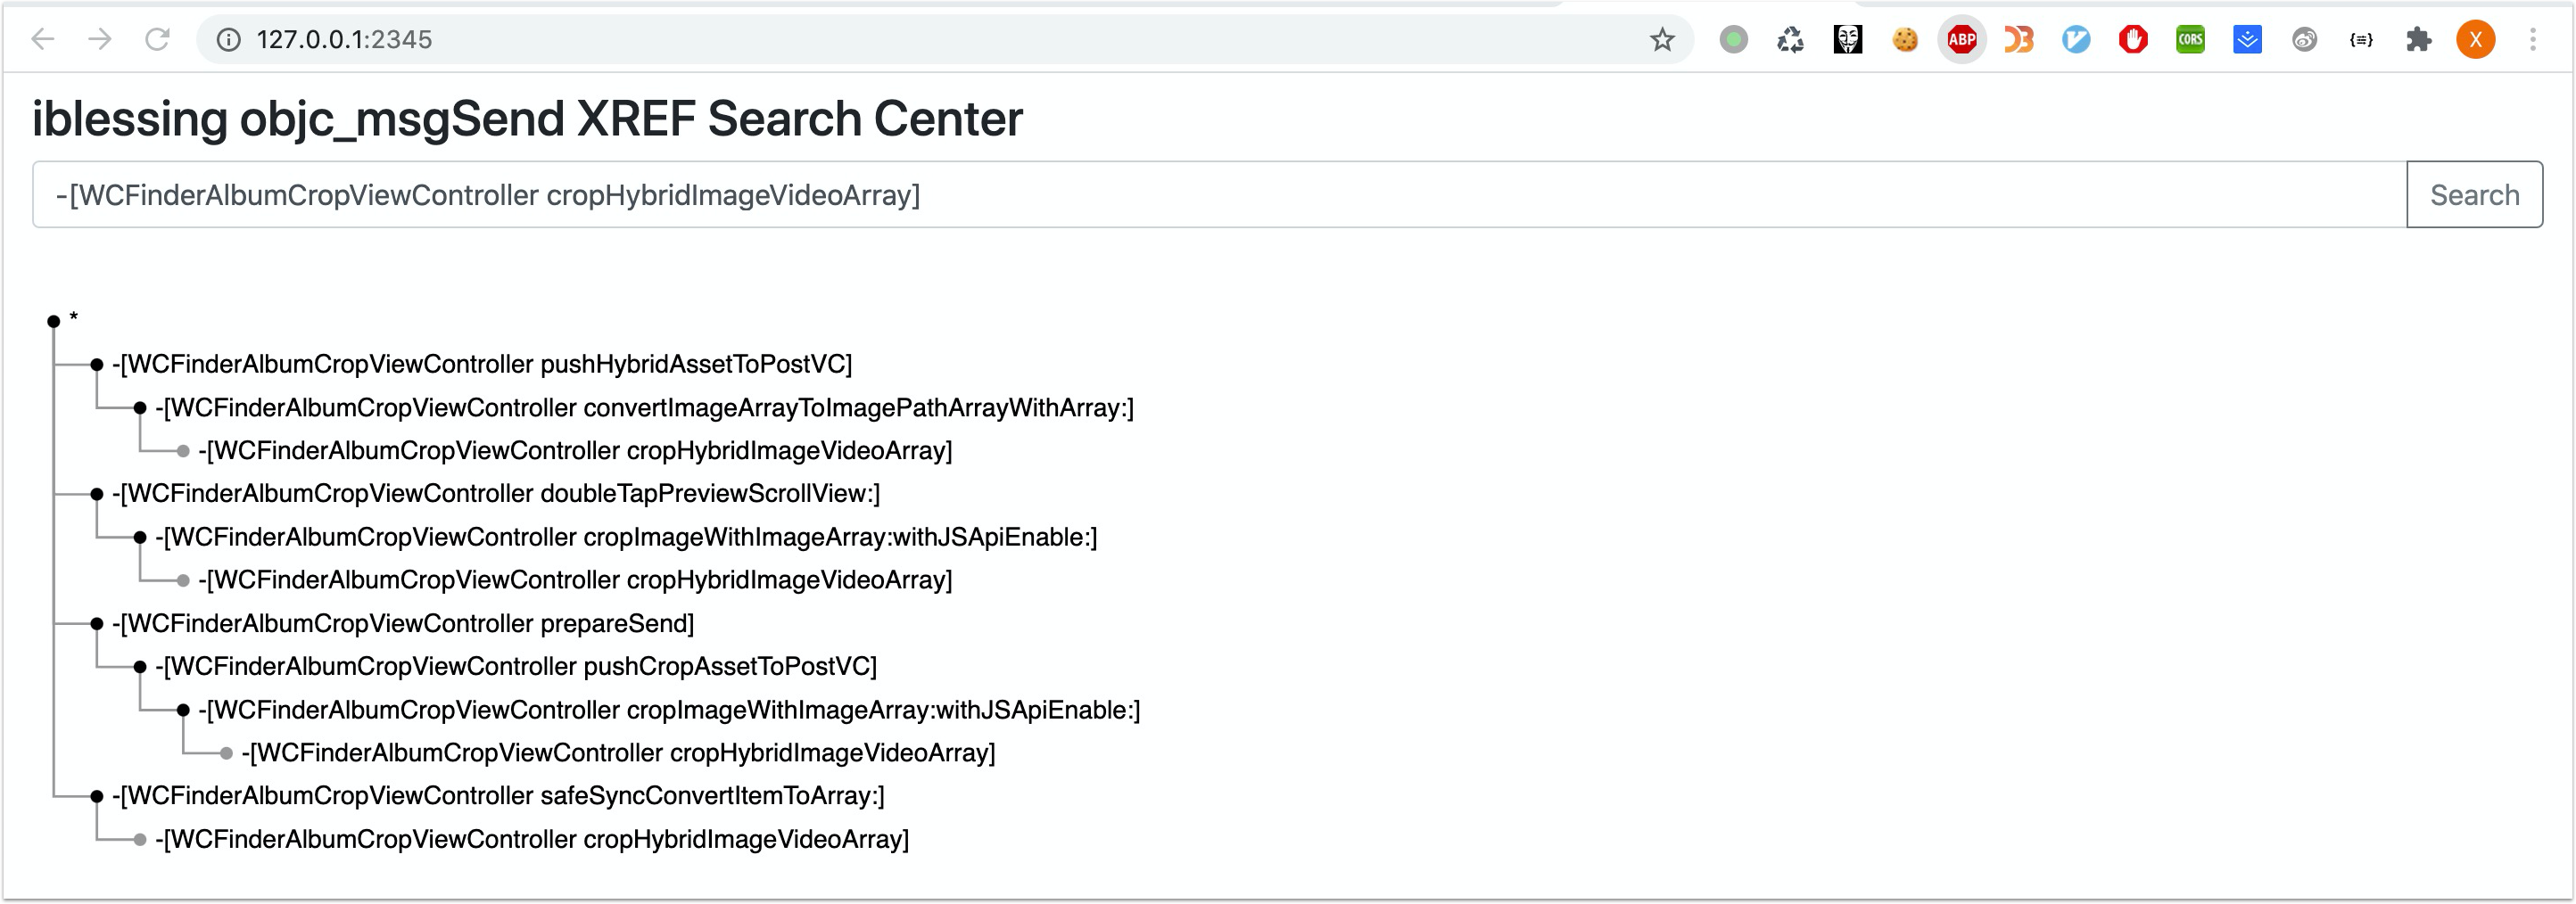
Reviewed Soulghost/iblessing@ff14351
Binary · Tool:
Research tool from Denuvo that simplifies linear mixed Boolean-arithmetic (MBA) expressions, which combine bitwise and integer operations and are used in code obfuscation.
Binary · Tool:
GrammaTech's intermediate representation for passing disassembly, analysis and rewriting results between binary tools, modeled on the role LLVM-IR plays for compilers.
Reviewed GrammaTech/gtirb@98fecec